

hexvero
 maximilianfeix/hexvero
The first look at a binary or app bundle: static, execution-free analysis with evidence. CLI, 15-tool MCP server and local web UI, Node only.
ai-securityandroid-securitybinary-analysis+9
3
maximilianfeix/hexveroThe first look at a binary or app bundle: static, execution-free analysis with evidence. CLI, 15-tool MCP server and local web UI, Node only.
 abraxas/mysql-mysqlbinlog-raw-path
MySQL Community Server 26.7.0 - High - mysqlbinlog --raw Rotate path leftover - client file write
 gmh5225/ghidra_svr_bridge
Binary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 romain-deperne/cve-2026-33980
KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
 redyank/cve-2026-33154
Proof-of-concept exploit for CVE-2026-33154, demonstrating remote code execution via SSTI in Dynaconf's Jinja resolver, with analysis and mitigation…
 fevar54/cve-2026-72530-trueconf-sandbox-escape-
Este repositorio contiene una demostración educativa de la mitigación y detección para **CVE-2026-72530**, una vulnerabilidad crítica de **Code…
 hiteshgorana/susvibes-jupyter-server-cve-2026-35397
Benchmark task for reimplementing a masked path-resolution fix in Jupyter Server, with functional and hidden security tests to evaluate…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.
 eset/wslink-vm-analyzer
WslinkVMAnalyzer is a tool to facilitate analysis of code protected by a virtual machine featured in Wslink malware

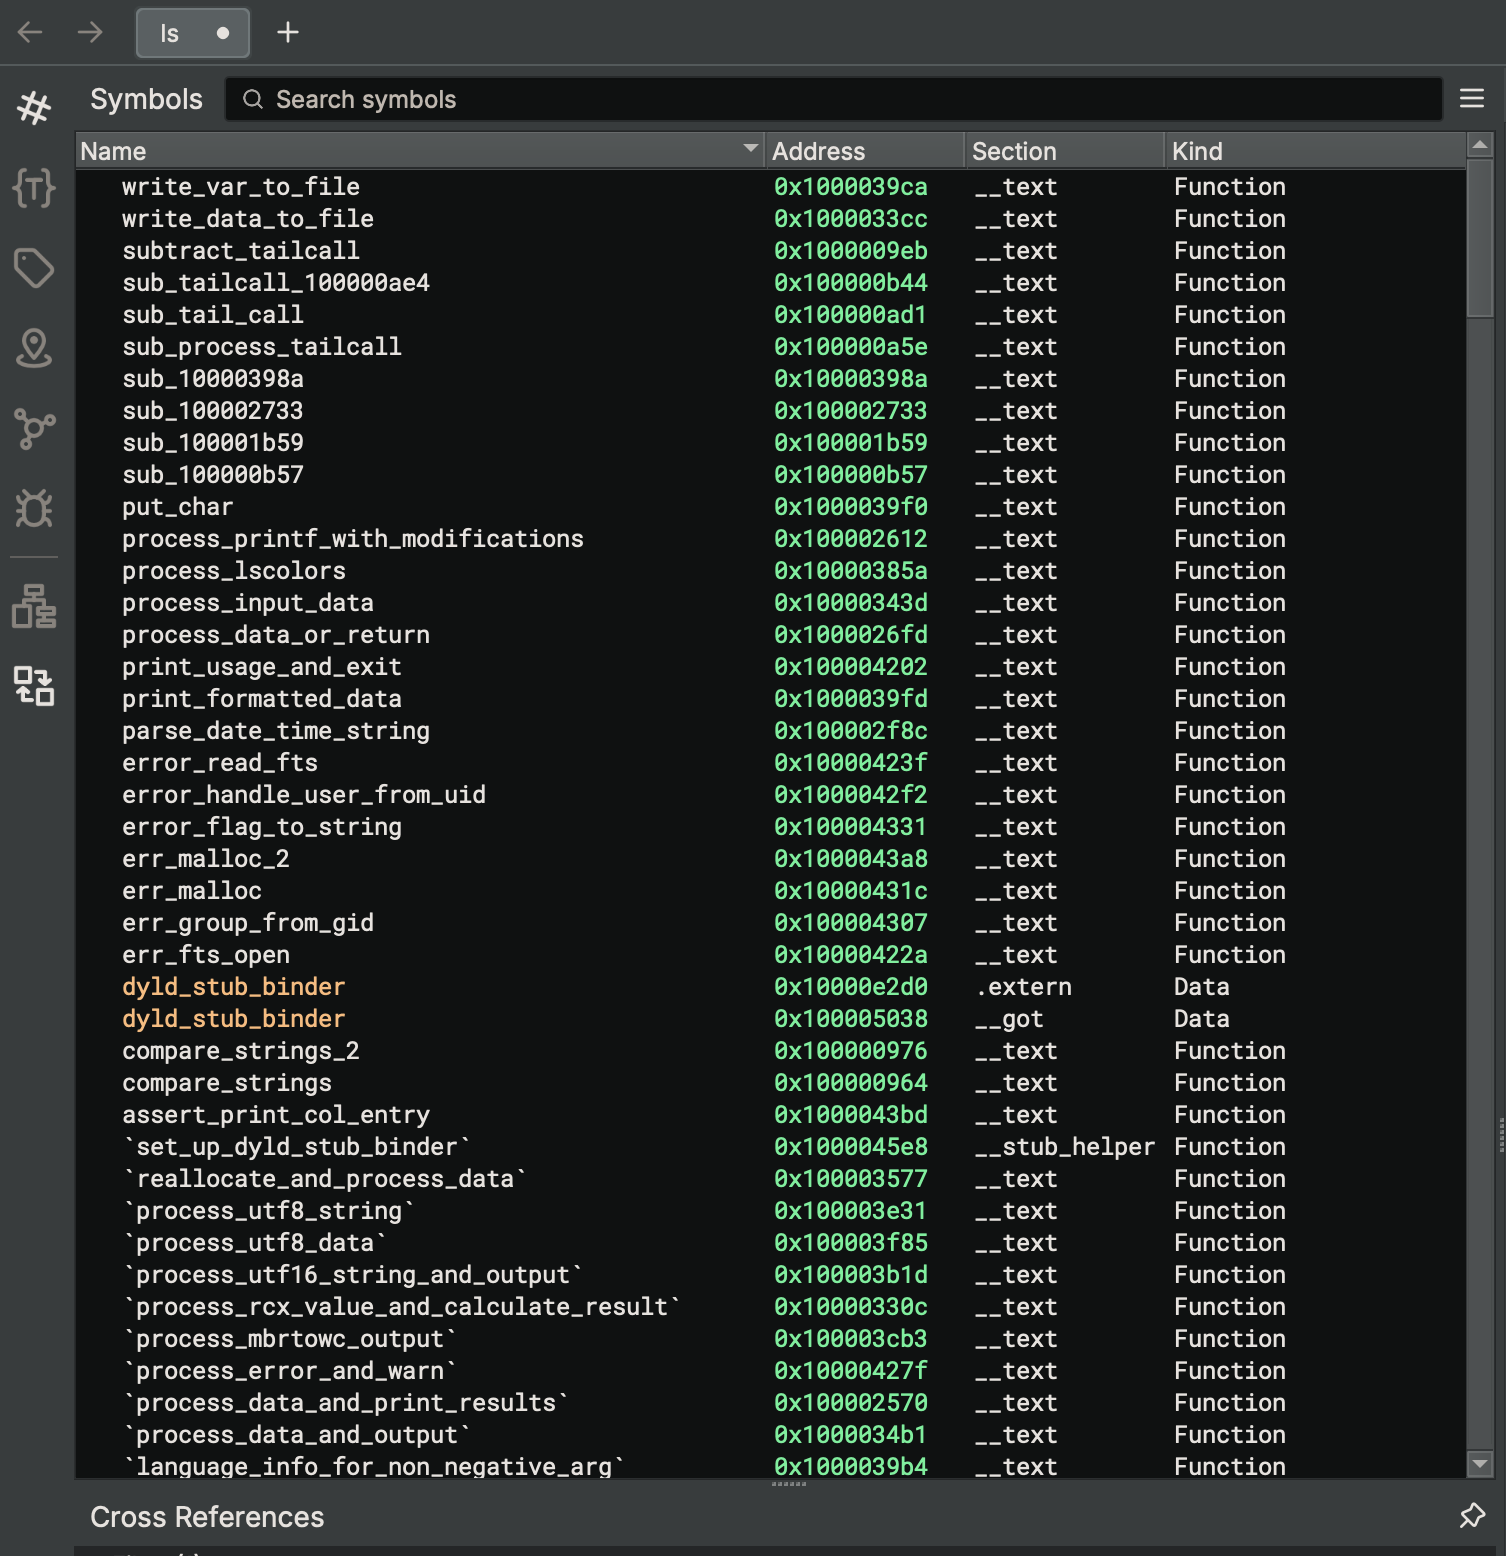 ahaggard2013/binaryninja-ollama
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…
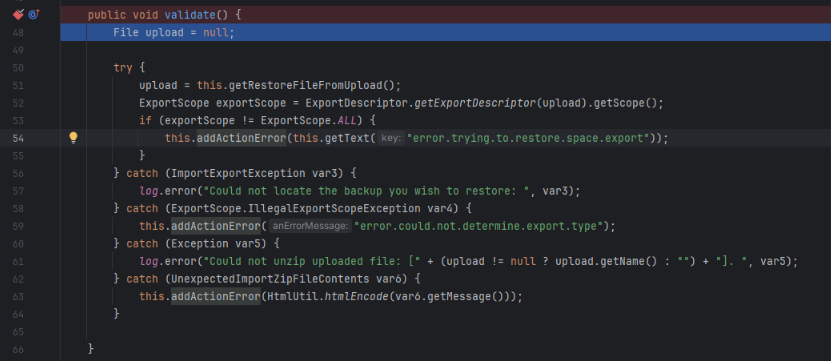 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…
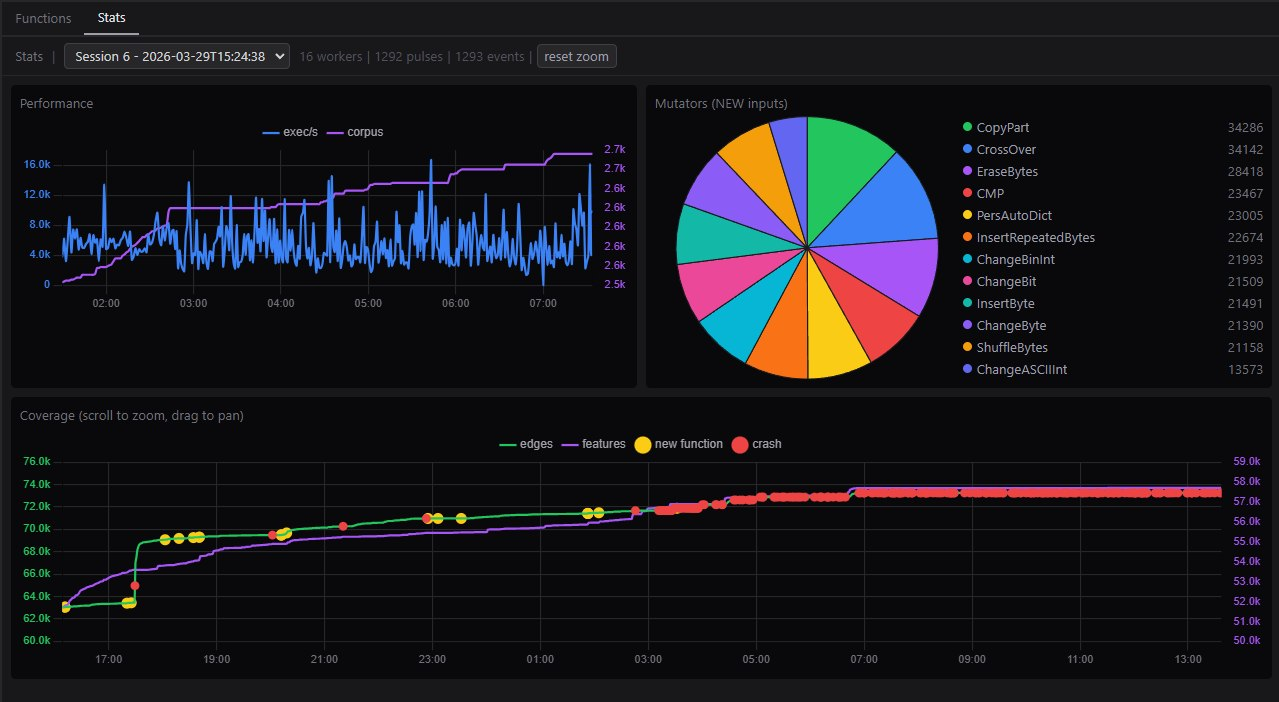 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…