

security-harness
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
ai-securitycode-analysisdevsecops+9
22
dmdhrumilmistry/security-harnessMulti-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
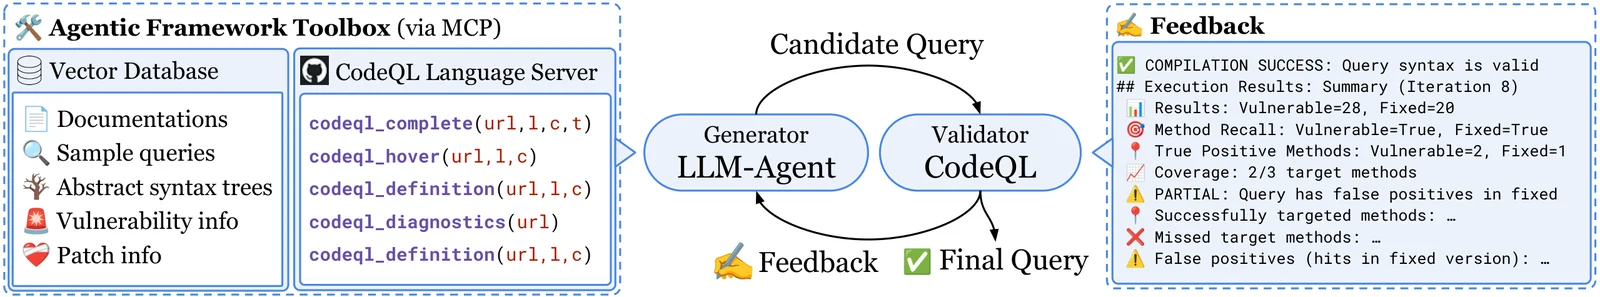 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 sivaadityacoder/cve-2026-22038
Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
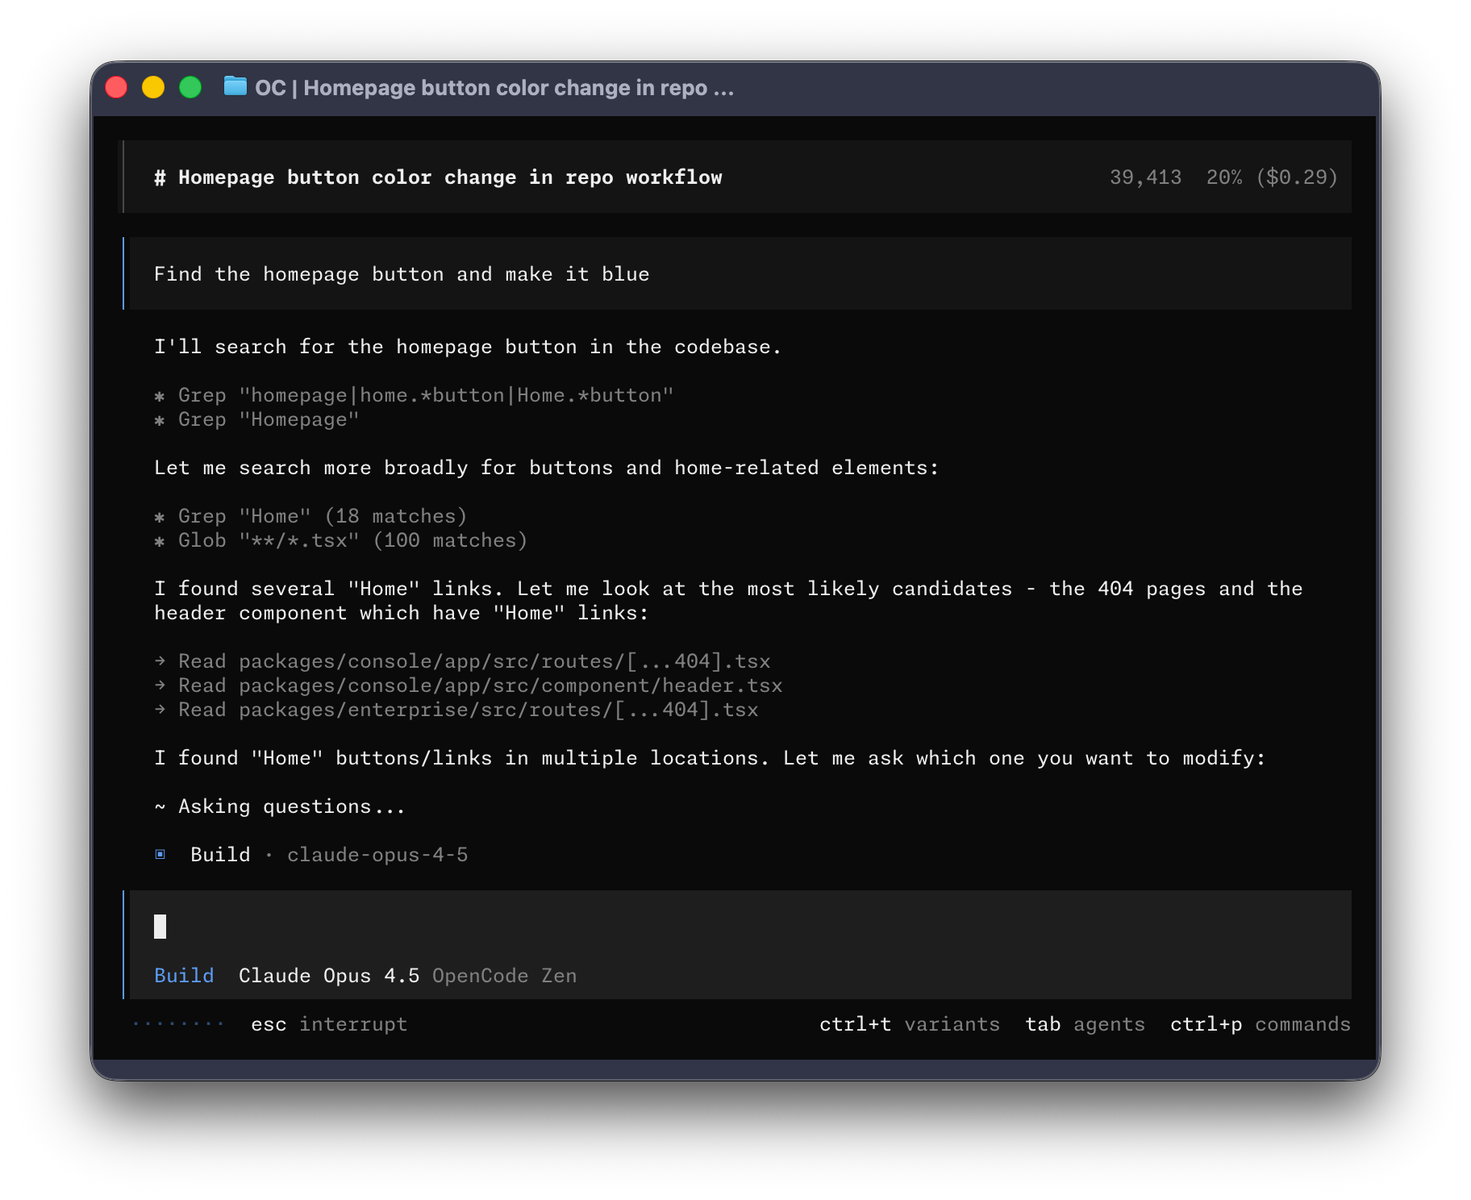 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 ashizzz/cve-2026-22610
Scans Angular projects for XSS vulnerabilities in SVG elements and unsafe bindings, generating a vulnerability report with line numbers and…
 renio-wow/cve-2026-51416
Analyzes a specific CVE in WeChat OAuth handler, identifying unbounded HTTP response reads leading to denial of service, with remediation guidance.
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 langbyyi/cve-2026-22785
Exploit tool for CVE-2026-22785, a critical code injection in orval < 7.18.0. Provides shell command execution and file scanning to demonstrate the…
 s1ko/cve-2026-52617
Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.