

gortex-PoC
 squeeze440/gortex-poc
PoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).
code-analysisexploitationinformation-gathering+4
squeeze440/gortex-pocPoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).
 squeeze440/obsidian-note-toolbar-poc
PoC — frontmatter-driven arbitrary JavaScript execution in Note Toolbar for Obsidian (GHSA-q8cw-3m8c-5pf2, CVE-2026-87002, CVSS 7.0).
 squeeze440/openlore-poc
PoC — path traversal via unsanitized LLM-derived domain field in OpenLore (GHSA-5j8x-q7q6-58j5, CVE-2026-87001, CVSS 4.7).
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…
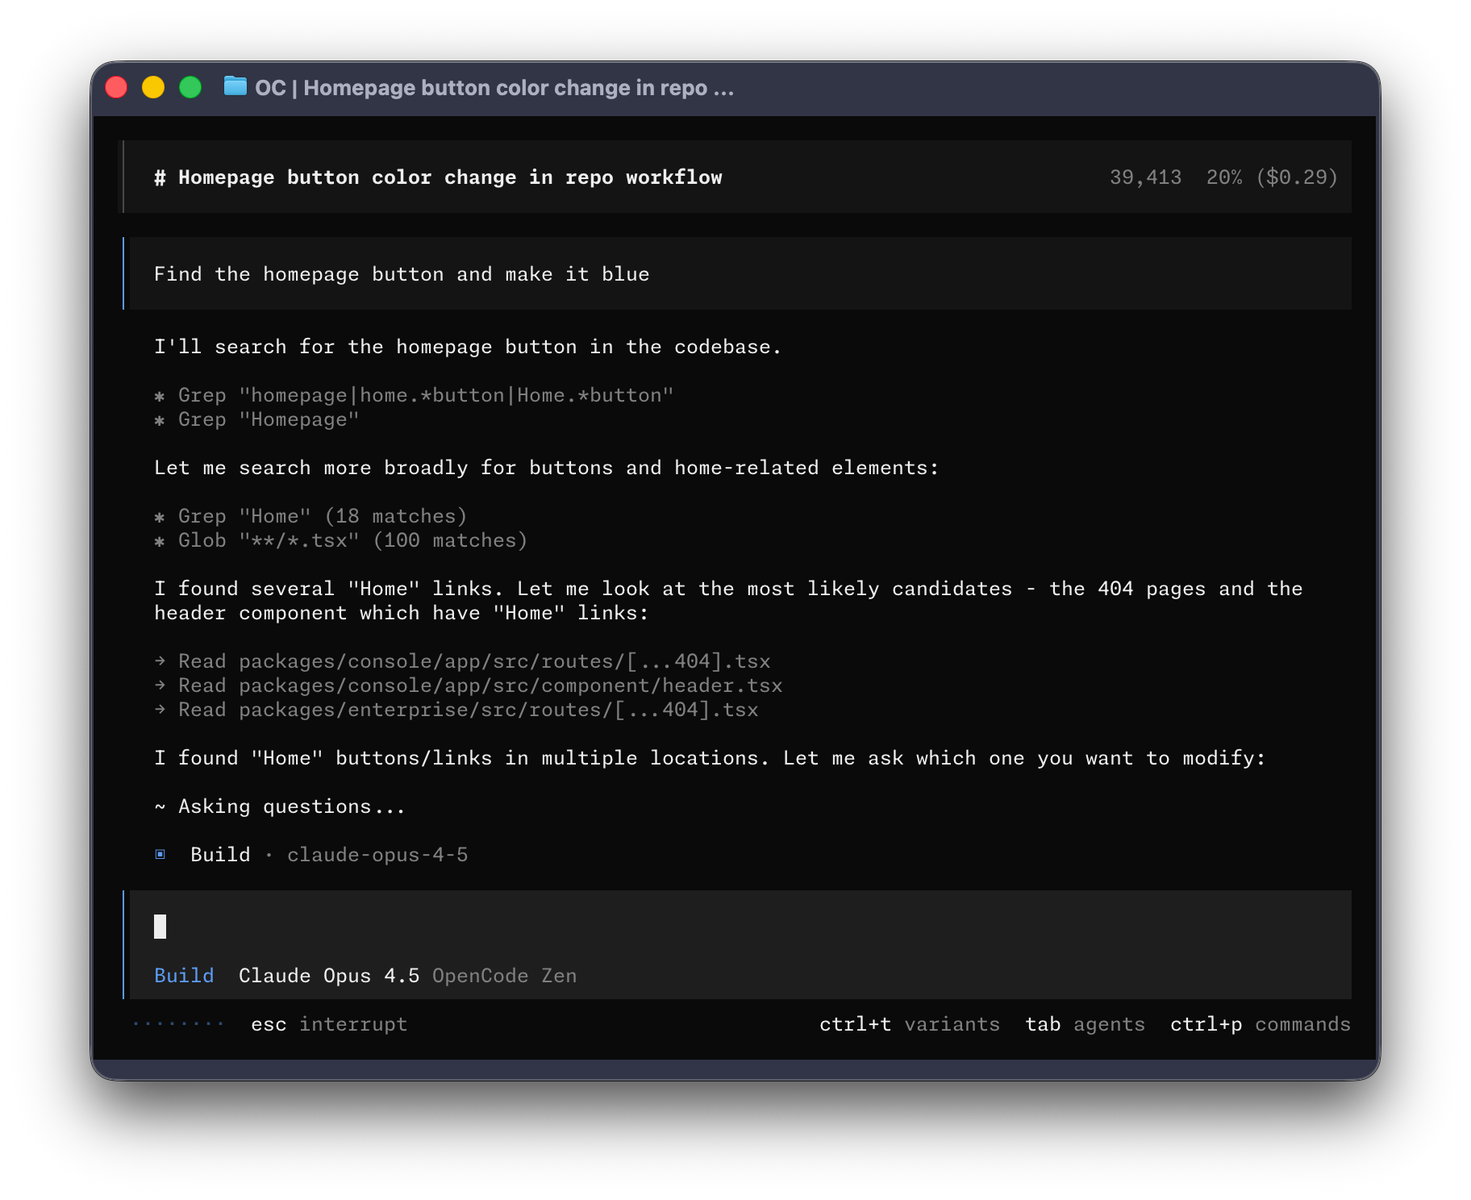 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 jax7sec/cve-2021-44529
Exploit for CVE-2021-44529, a code injection vulnerability in Ivanti EPM Cloud Service Appliance allowing unauthenticated arbitrary code execution as…
 asama7706r-ui/strilight
Lifts x86-64 binary loops into closed-form SMT constraints via strided interval analysis, enabling O(1) symbolic execution and crackme key recovery.
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 anna-kravets/codeql-buffer-overflow-variant
Synthetic CWE-120 stack buffer overflow variant of CVE-2020-8597 (pppd EAP) as a CodeQL static-analysis target
 eset/wslink-vm-analyzer
WslinkVMAnalyzer is a tool to facilitate analysis of code protected by a virtual machine featured in Wslink malware
 imran-parray/mind-maps
Mind-Maps of Several Things
 m417z/x64dbg-xfg-marker
An x64dbg plugin which marks XFG call signatures as data
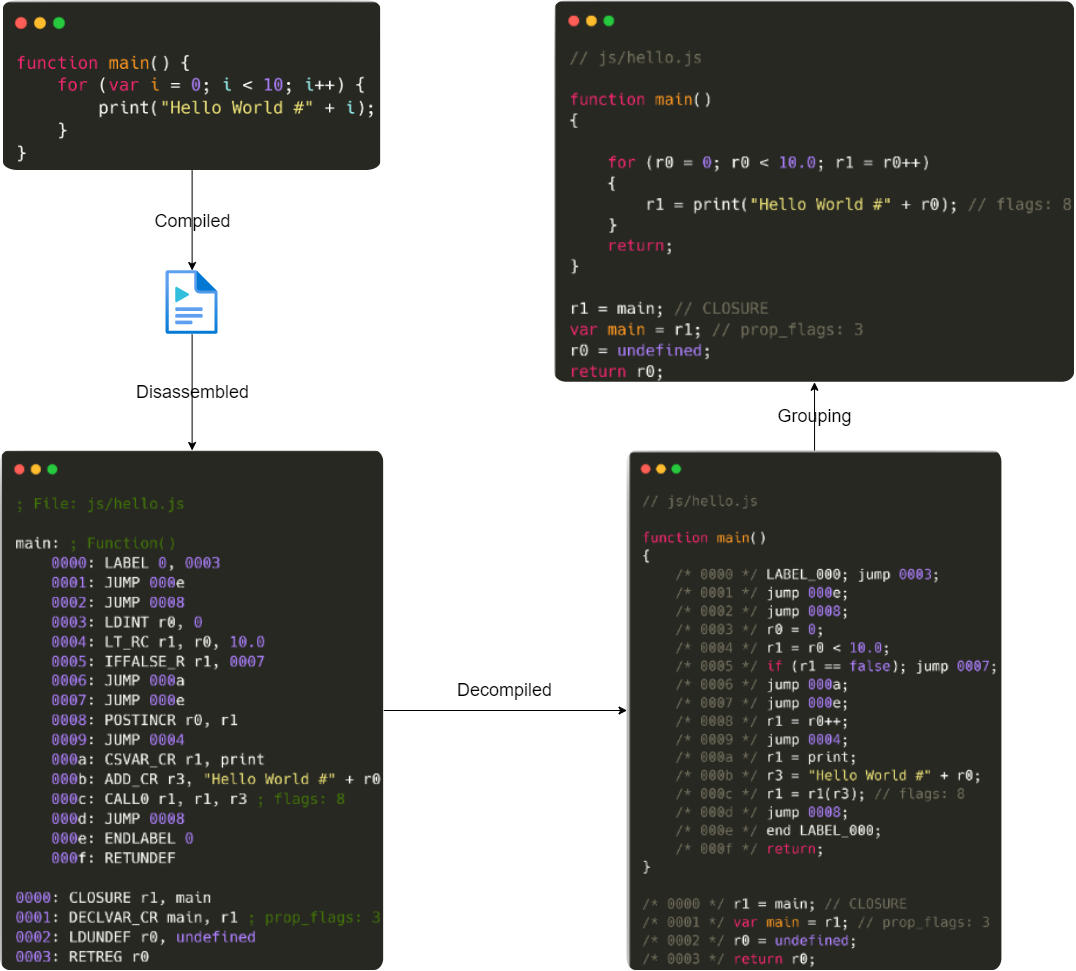 nccgroup/detaped
Detaped is a Python disassembler and decompiler for Duktape. The intended use is for source code review and analysis in situations where you only…
 nccgroup/matt.net
Matt.Net is a simple GUI wrapper around Microsoft's CAT.NET Code Auditing Tool
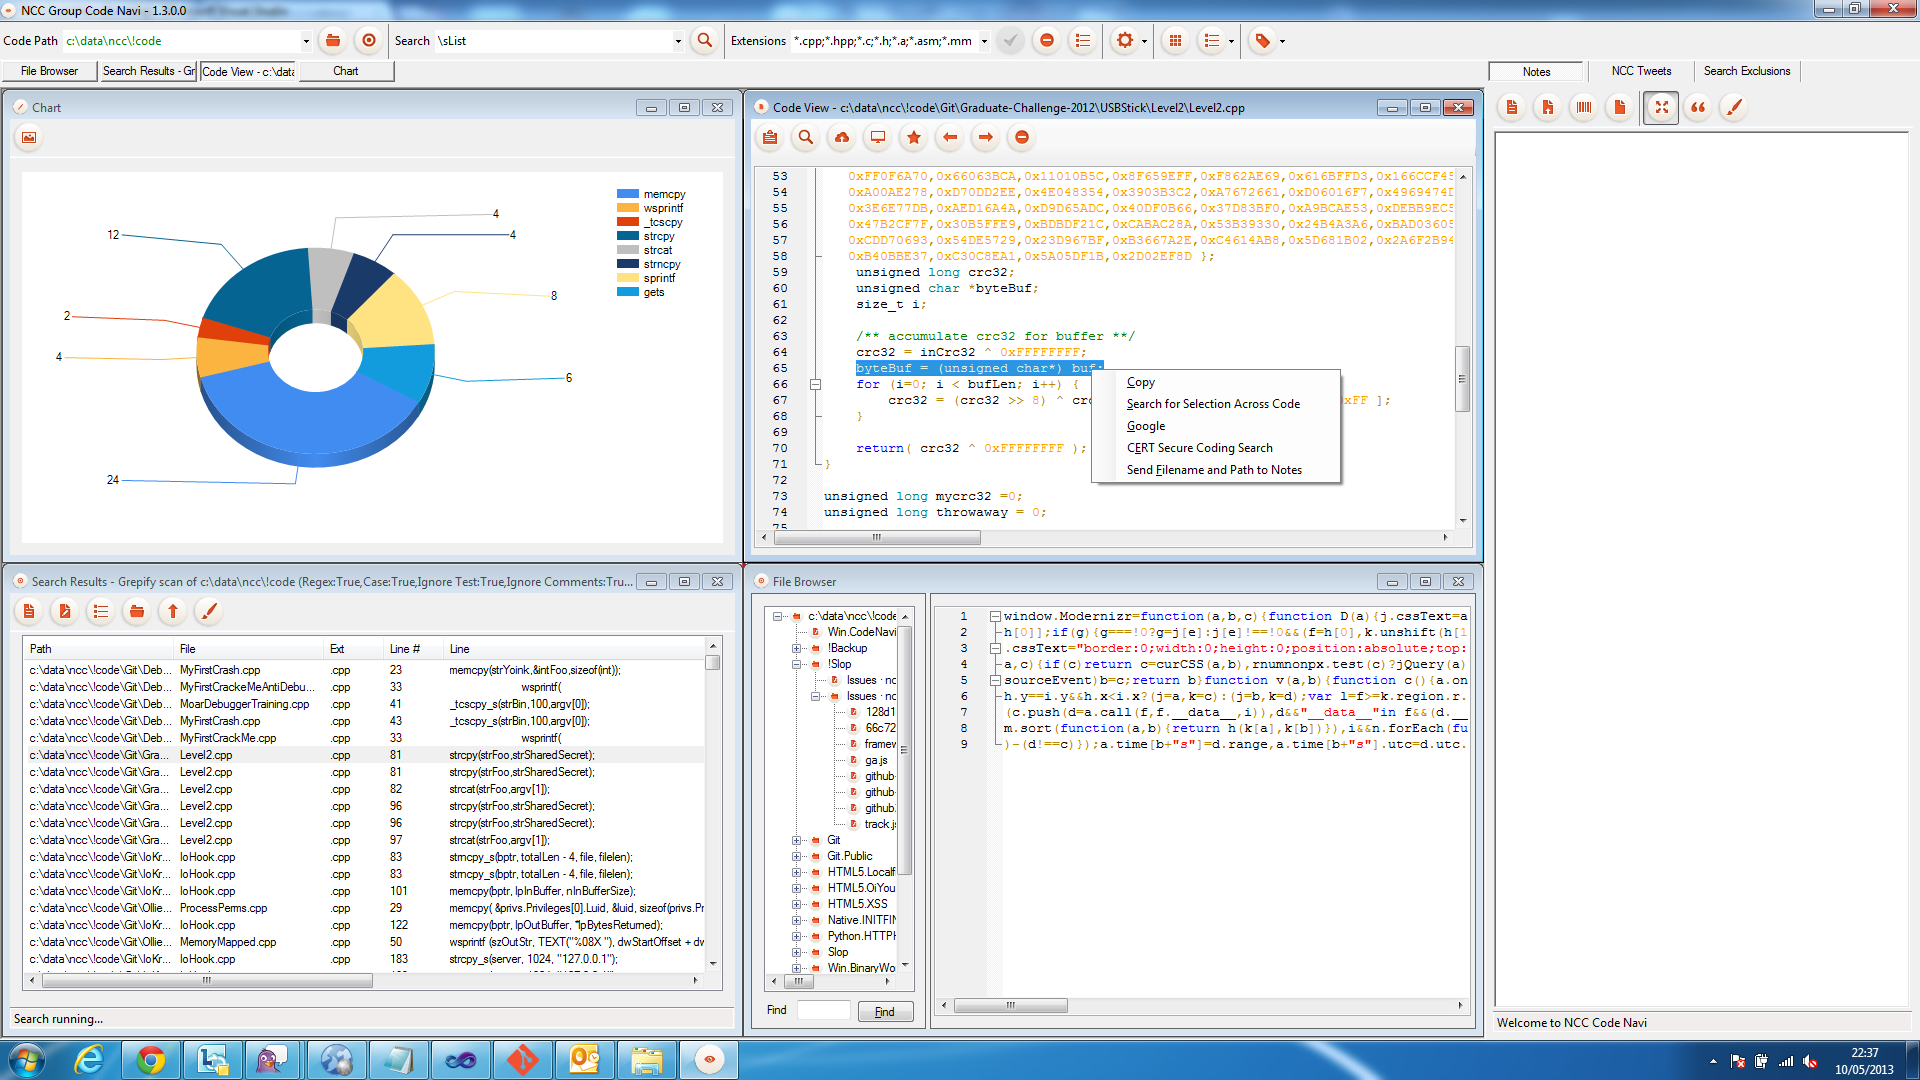 nccgroup/ncccodenavi
NCC Code Navigator
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…