

pycdc
 ejfkdev/pycdc
Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
binary-analysiscode-analysisdebuggers+4
8
ejfkdev/pycdcDecompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 viruscamp/luadec
Lua Decompiler for lua 5.1 , 5.2 and 5.3
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 gmh5225/fracture-
🐈⬛ WIP Suite for reverse engineering JVM applications
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 gmh5225/antidbg-unabomber
VMP improved idea (old AmogusPlugin)
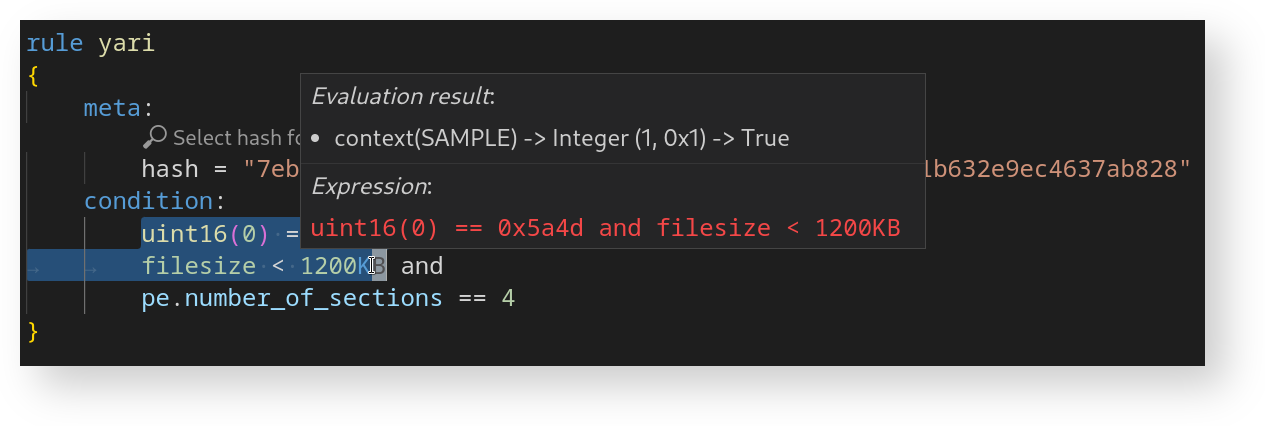 avast/yari
YARI is an interactive debugger for YARA Language.
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
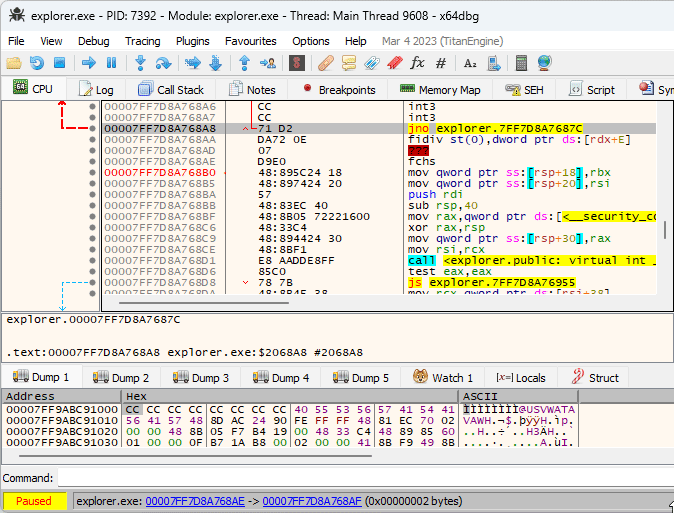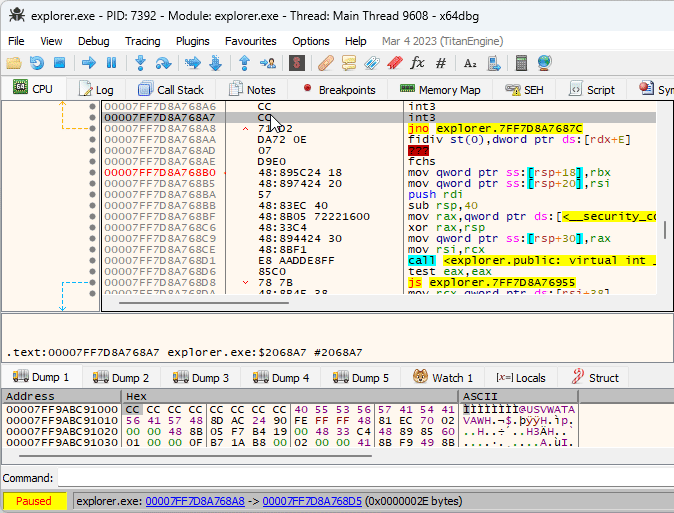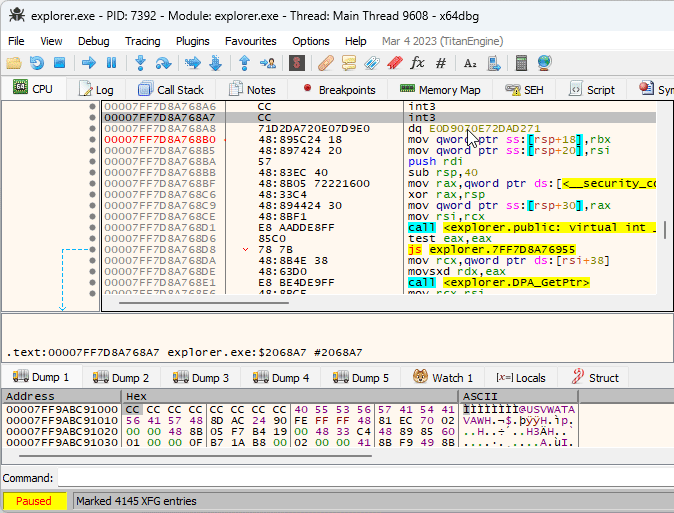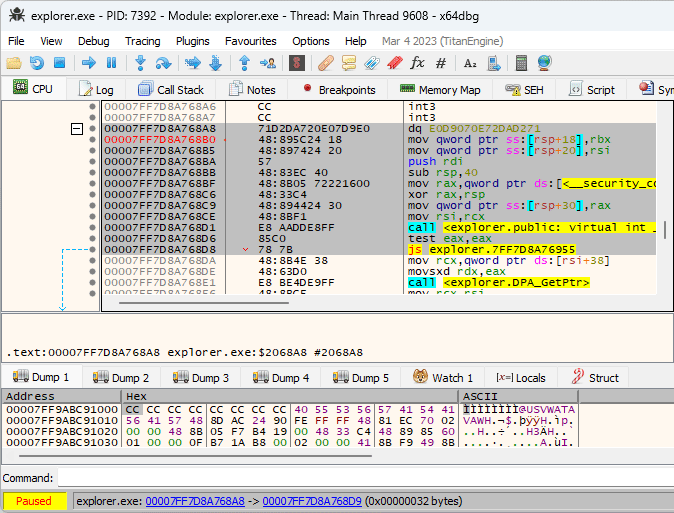 m417z/x64dbg-xfg-marker
An x64dbg plugin which marks XFG call signatures as data
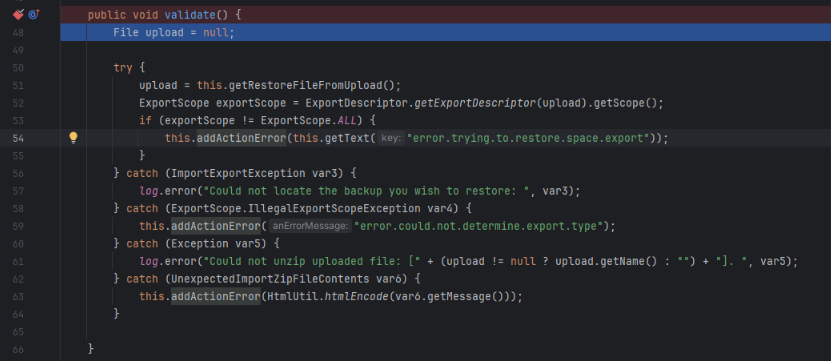 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby