
Arkari
 komimoe/arkari
Yet another llvm based obfuscator based on goron.
anti-botbinary-analysiscode-analysis+4
komimoe/arkariYet another llvm based obfuscator based on goron.
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 quarkslab/qsynthesis
Greybox Synthesizer geared for deobfuscation of assembly instructions.
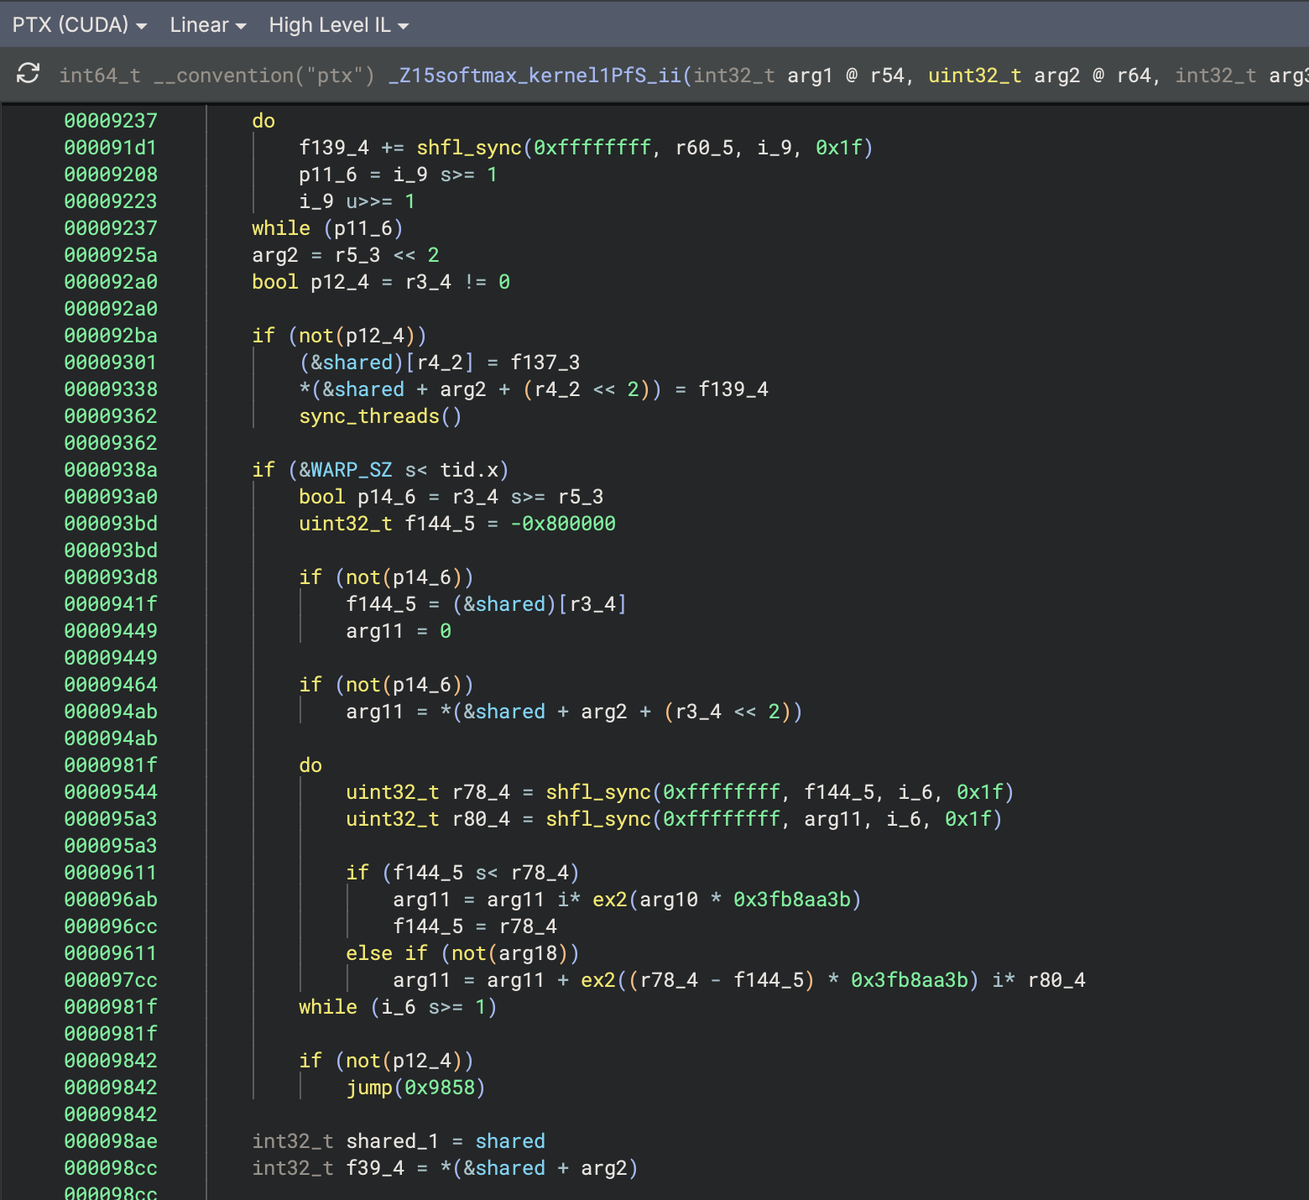 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
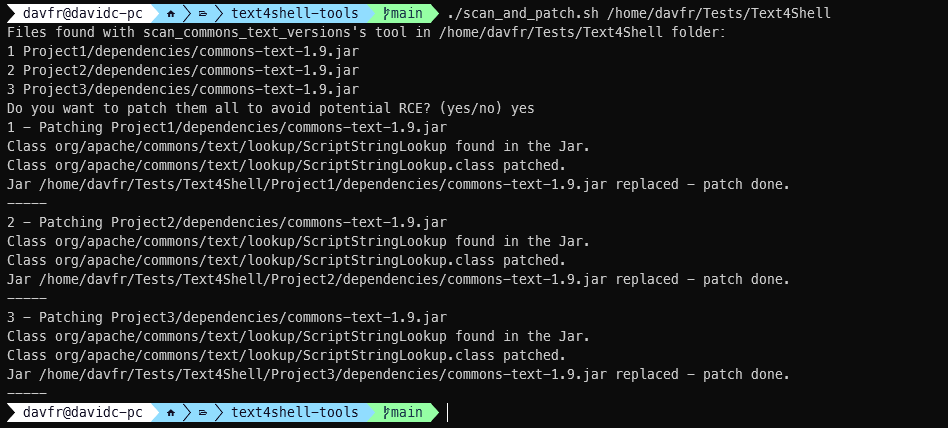 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
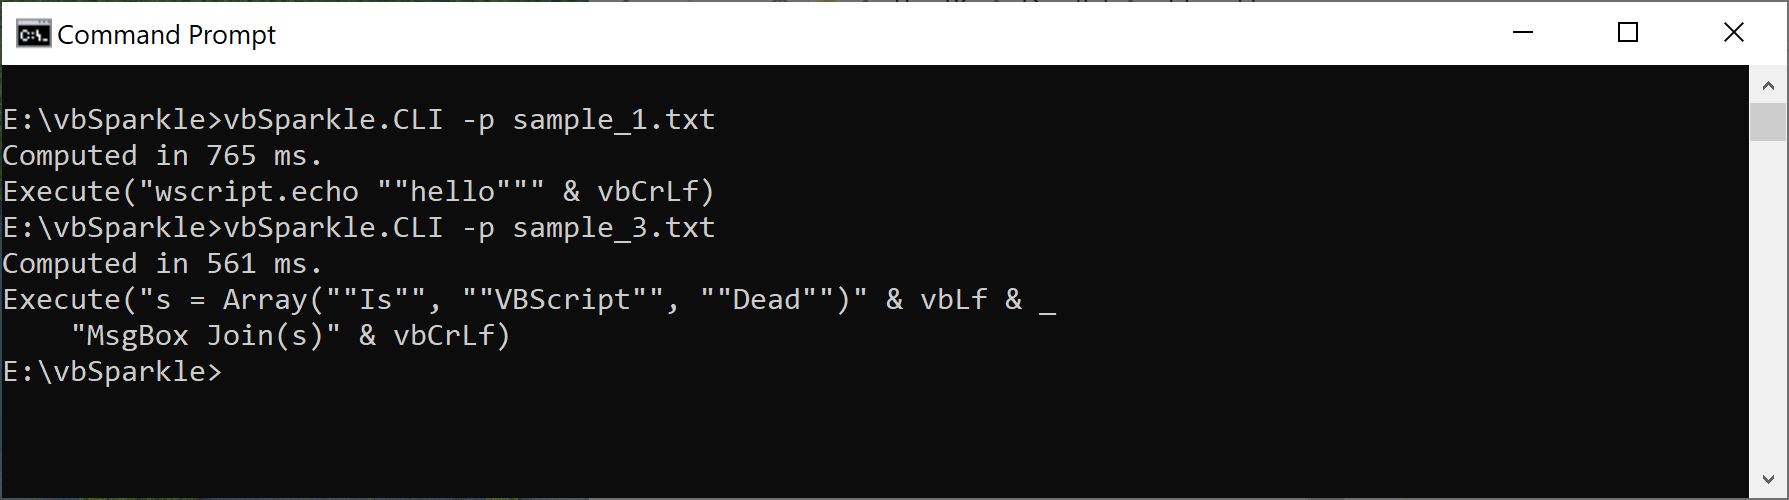 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
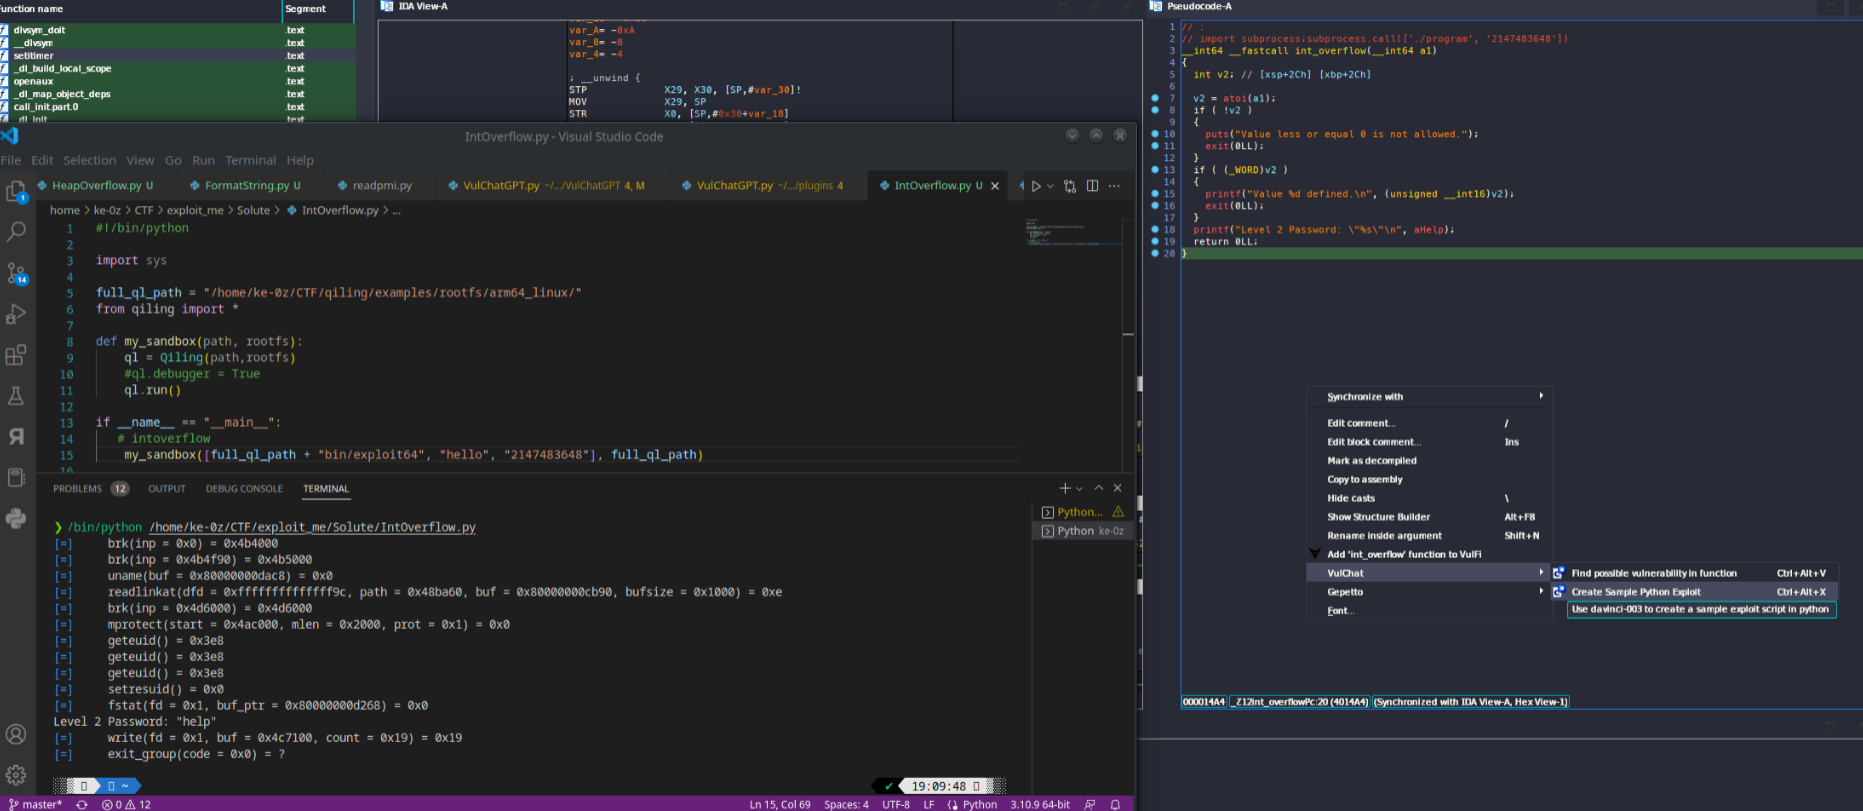 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
 samsung/utopia
UT based automated fuzz driver generation
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 vinsontang1/dcvd
The code in "DCVD: Dual-Channel Cross-Modal Fusion for Joint Vulnerability Detection and Localization"
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx