

alibi
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
api-securitycode-analysisconfiguration-auditing+7
10
owasp-noir/alibiCross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
 3ele-projects/cve-2026-39440-funnelforms-fix
Drop-in WordPress plugin that blocks the vulnerable Demo Import handler in FunnelForms Pro to mitigate Remote Code Execution (CVE-2026-39440).
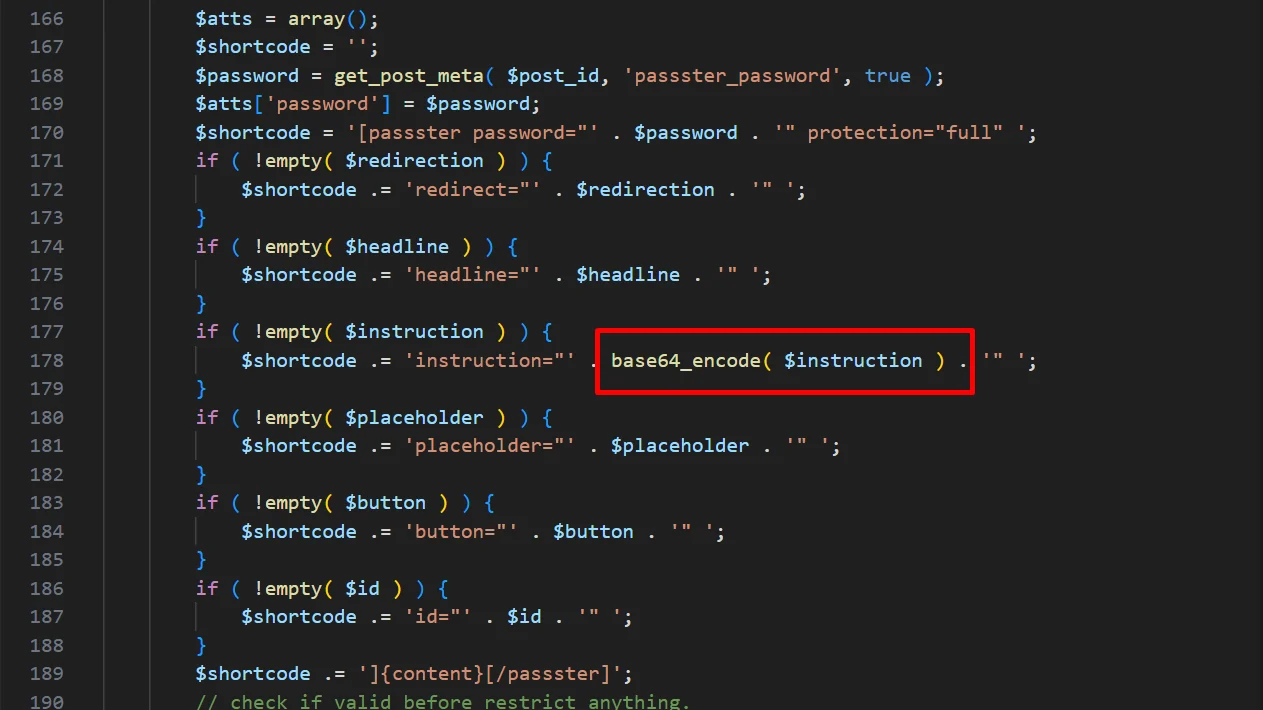 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…
 zimshk/cve-2025-59528.yaml
YAML-based proof-of-concept for CVE-2025-59528, demonstrating remote code execution in Flowise via the CustomMCP node's unsafe JavaScript evaluation.
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 binsec/xyntia
Xyntia, the black-box deobfuscator
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
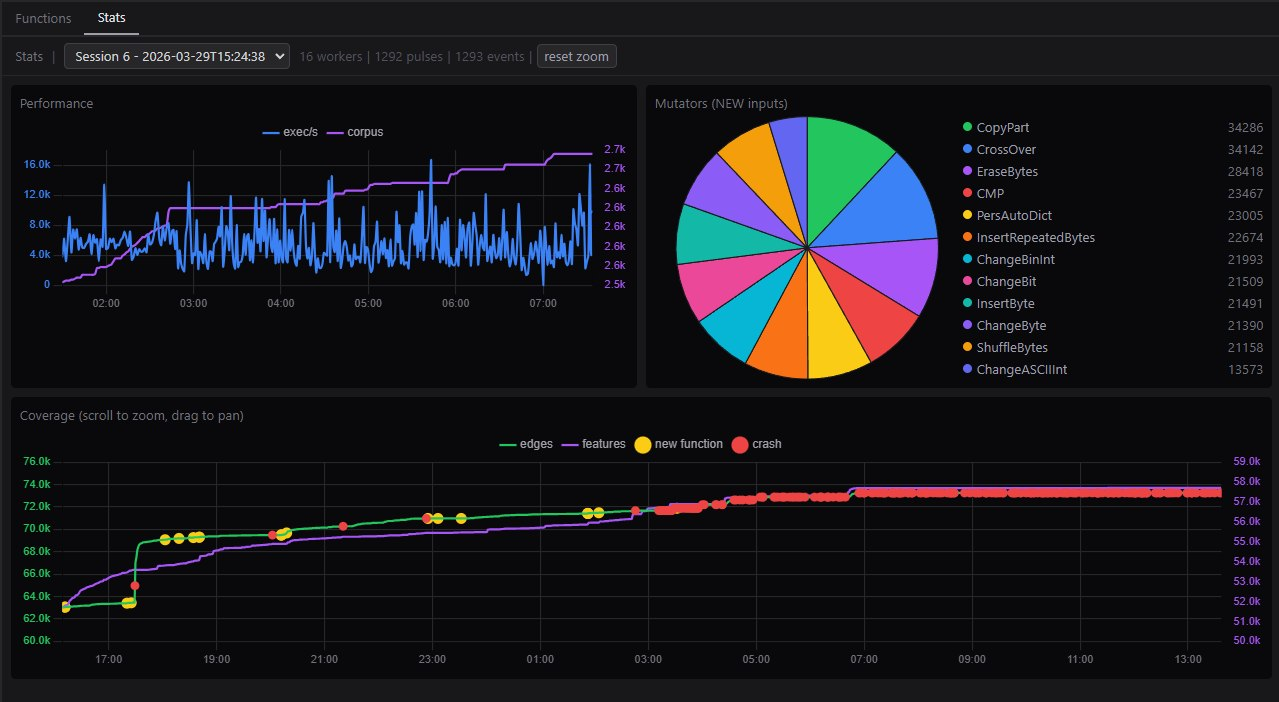 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
