
IAT-Hook
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
binary-exploitationcode-analysismalware-analysis+4
gmh5225/iat-hookC++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
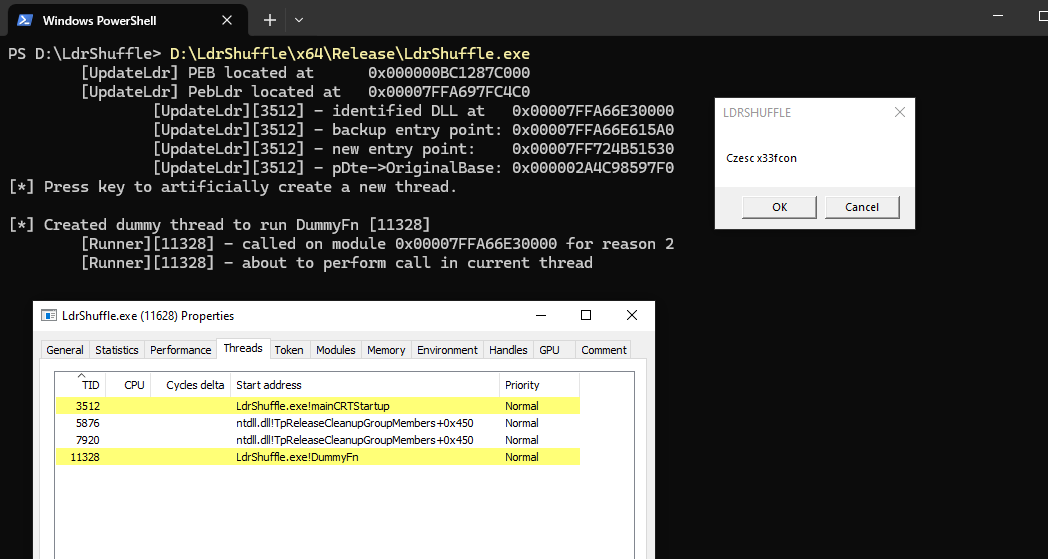 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
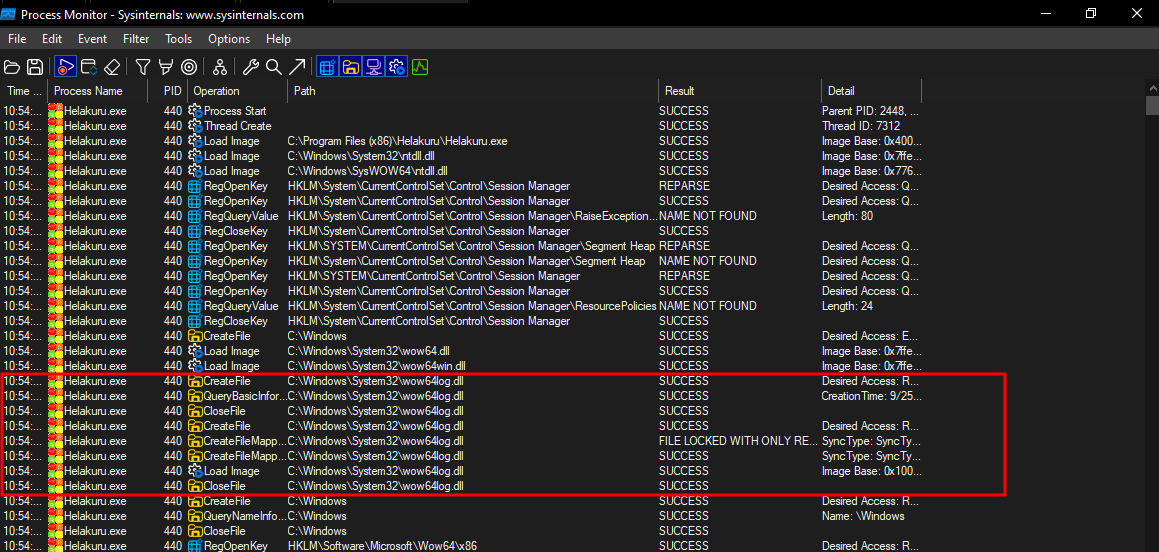 surajhacx/helakuruv.1.1-dllhijack
Helakuru Version 1.1 DLL Hijack - CVE-2024-48605
 ashr/cve-2017-8759-exploits
Two versions of CVE-2017-8759 exploits
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 tylous/limelighter
A tool for generating fake code signing certificates or signing real ones
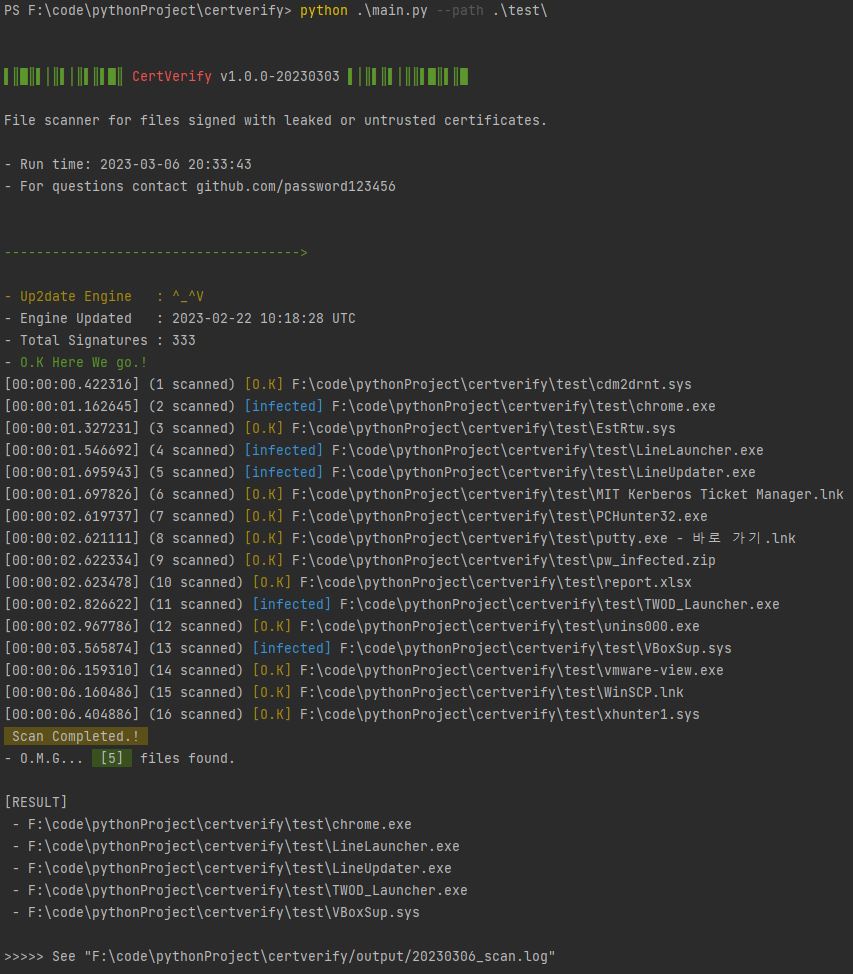 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.