

CVE-2026-65320-fastcore
 rahulreddykarne/cve-2026-65320-fastcore
Documents CVE-2026-65320, a tar-slip path traversal in fastcore's untar_dir(), with a harmless proof-of-concept demonstrating arbitrary file write…
code-analysiseducationexploitation+3
rahulreddykarne/cve-2026-65320-fastcoreDocuments CVE-2026-65320, a tar-slip path traversal in fastcore's untar_dir(), with a harmless proof-of-concept demonstrating arbitrary file write…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 s1ko/cve-2026-52617
Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…
 0xmrma/cve-2026-5061
Consul Template validated where a symlink pointed during template evaluation, but its later dependency fetch read the original path. Retargeting the…
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 nxgn-kd01/react2shell-scanner
Detect CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Fast, accurate scanner with zero false positives.
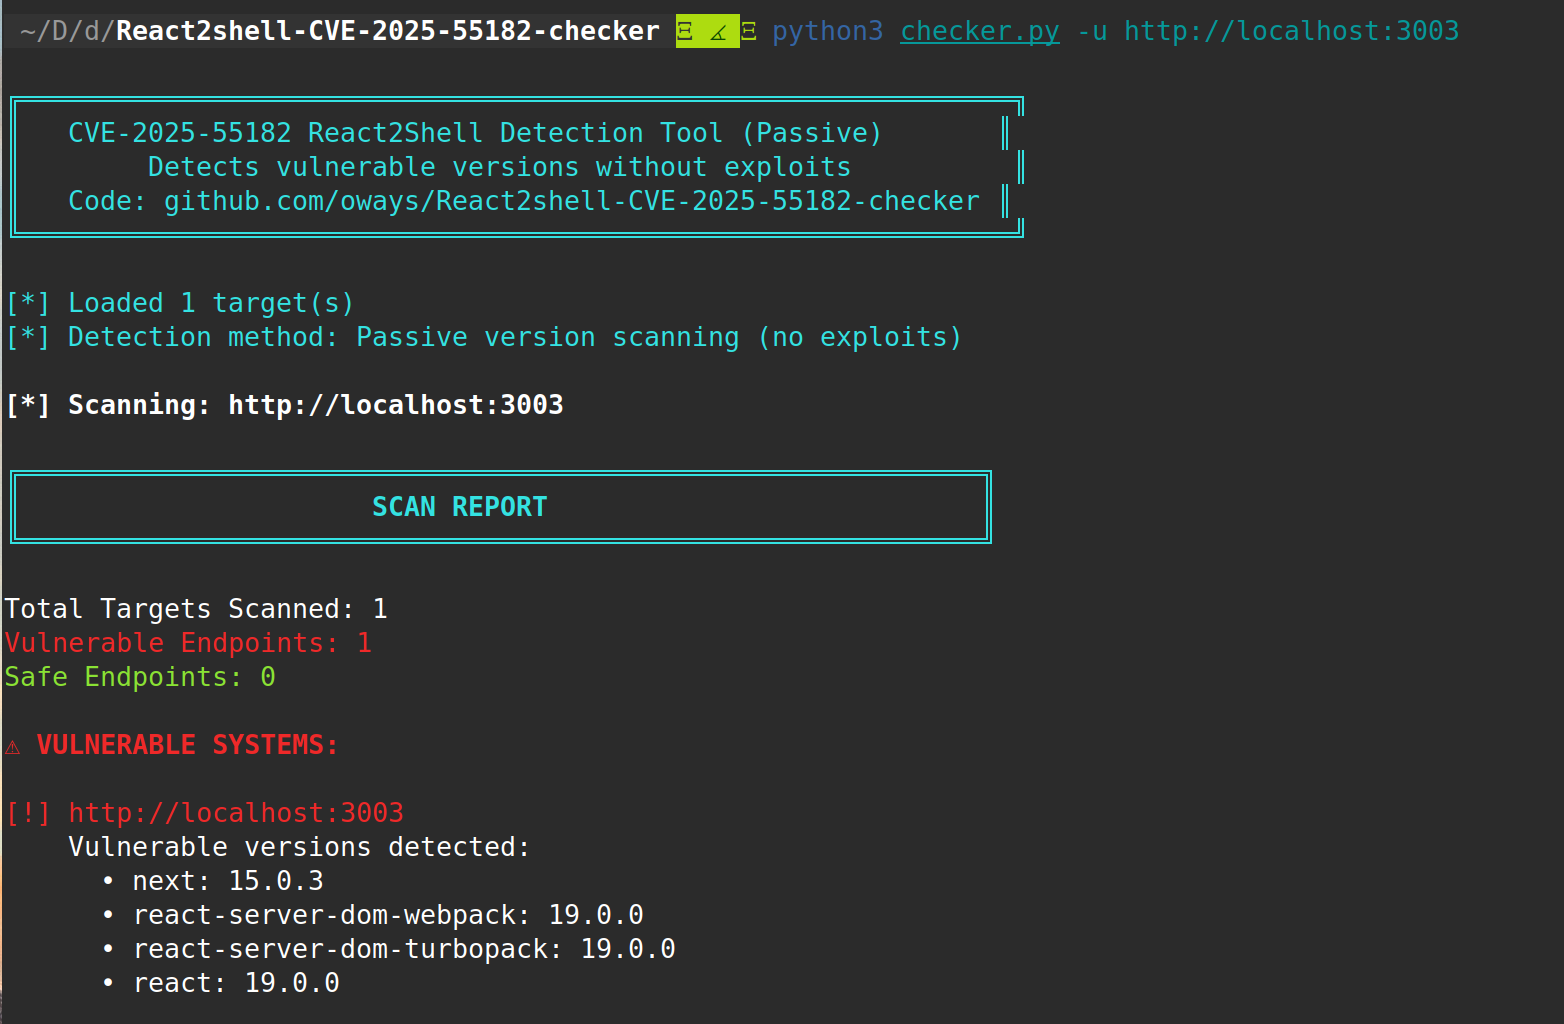 oways/react2shell-cve-2025-55182-checker
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…
 shoucheng3/jenkinsci__workflow-multibranch-plugin_cve-2022-25175_706-vd43c65dec013
Exploit for CVE-2022-25175 targeting Jenkins Pipeline: Multibranch plugin, enabling automated exploitation of a specific vulnerability in CI/CD…
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 tina94happy/spring-web-5xx-mitigated-version
Mitigated version for CVE-2016-1000027 spring web.