
CVE-2026-25747
 oscerd/cve-2026-25747
CVE-2026-25747 - Camel LevelDB Deserialization Vulnerability
code-analysiseducationexploitation+3
oscerd/cve-2026-25747CVE-2026-25747 - Camel LevelDB Deserialization Vulnerability
 ltranquility/cve-2024-21644-poc
Proof-of-concept exploit for CVE-2024-21644, demonstrating remote code execution vulnerability with Python-based automation and colored output.
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
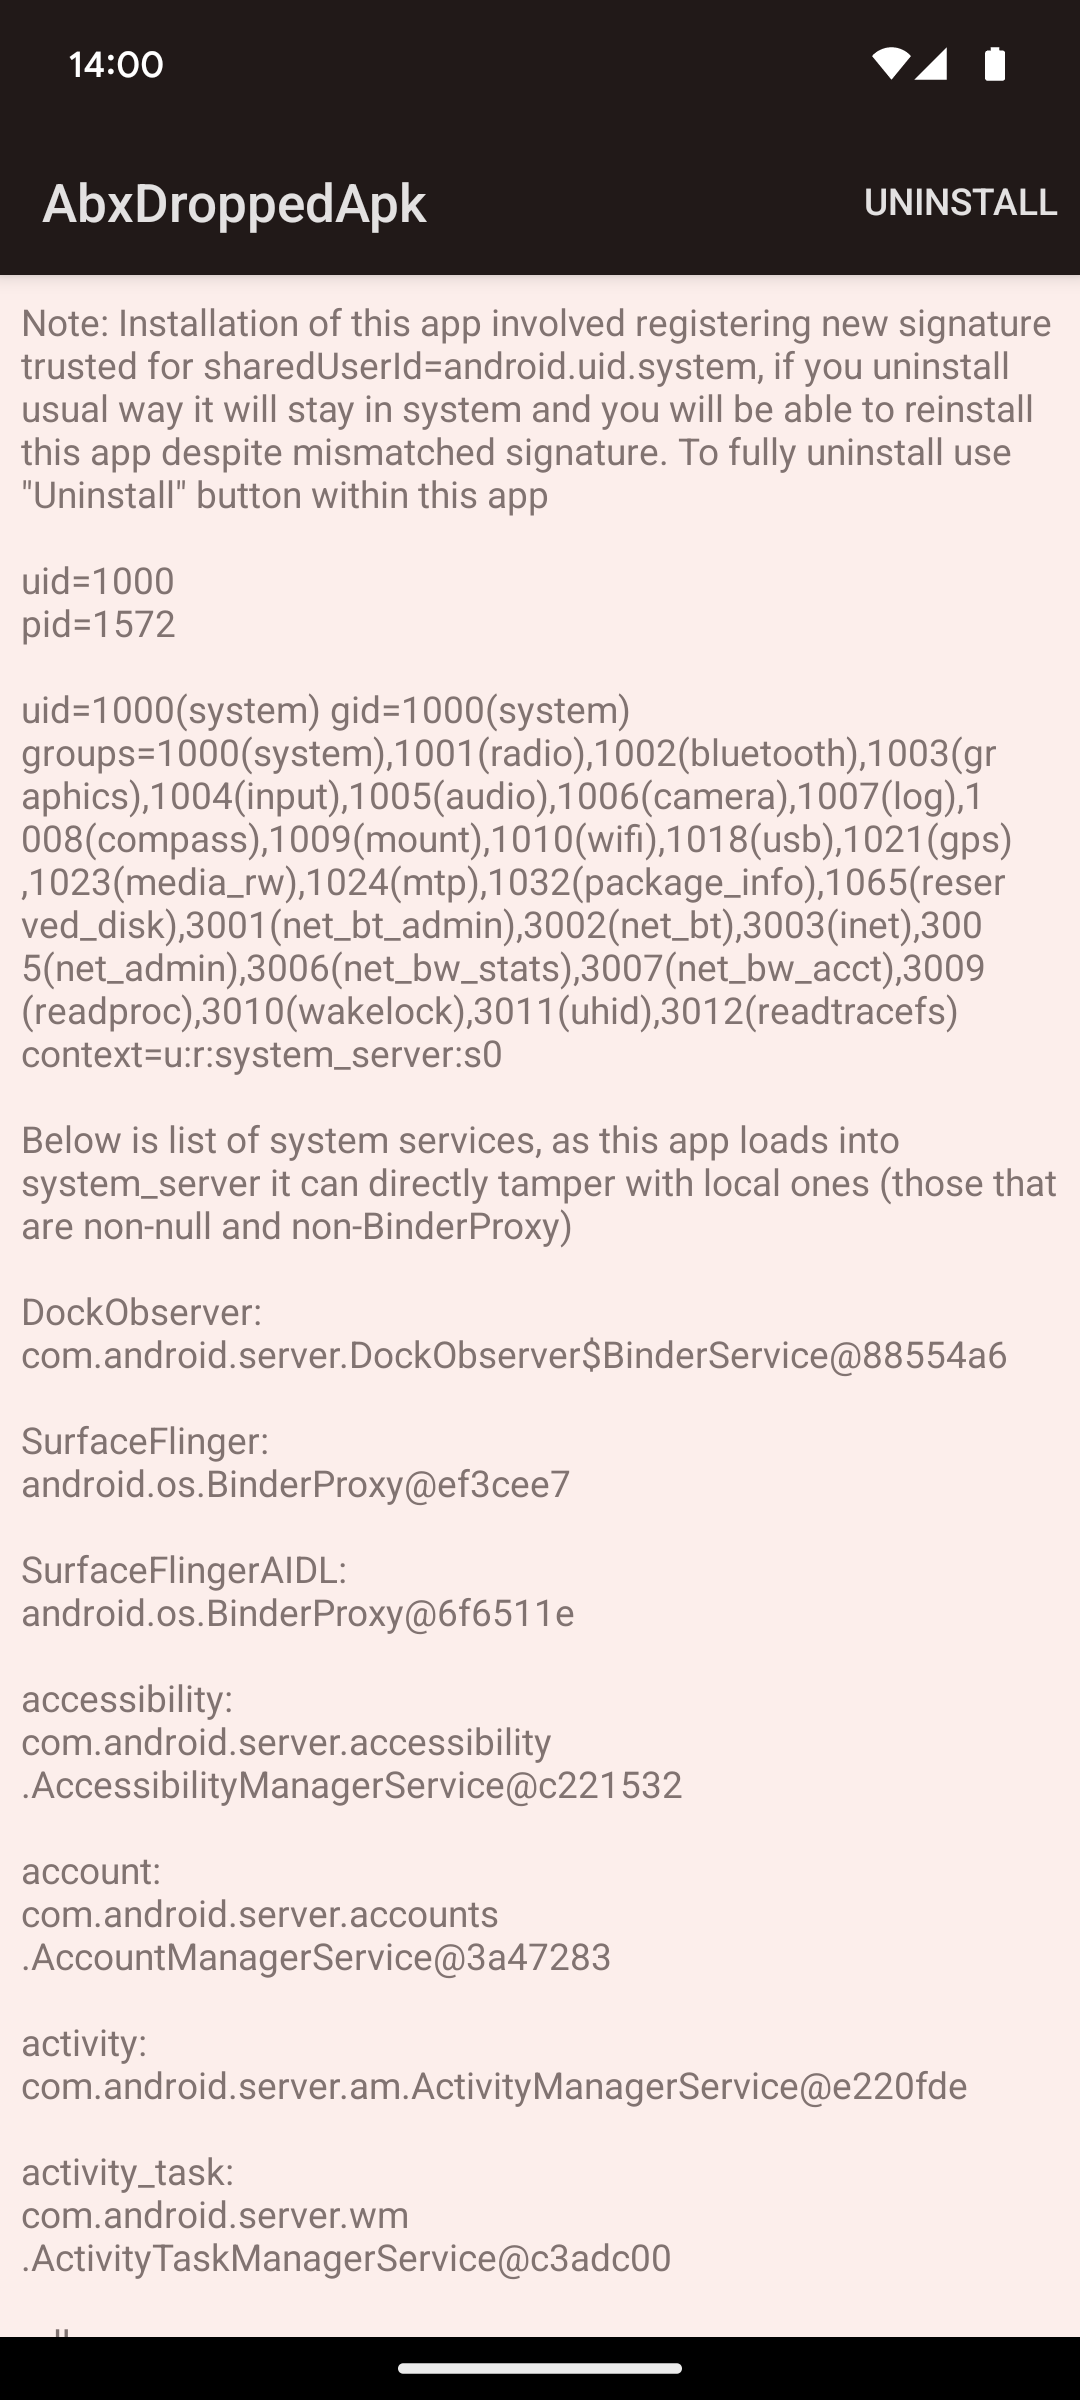 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 eqstlab/cve-2024-23998
PoC for CVE-2024-23998
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
 jacklosingheart/ghsa-4cx5-89vm-833x-poc
GHSA-4cx5-89vm-833x/CVE-2024-52800
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)
 nastar-id/cve-2024-7094
CVE-2024-7094 Vulnerability checker
 jacklosingheart/cve-2024-55875
CVE-2024-55875 | GHSA-7mj5-hjjj-8rgw | http4k first CVE
 martinhaunschmid/cve-2024-52301-research
A bit of research around CVE-2024-52301
 nyamort/cve-2024-52301
Proof-of-concept exploit for CVE-2024-52301 demonstrating environment manipulation in Laravel via injected URL parameters, with detailed code…
 cybercrowcc/cve-2024-48990
Technical analysis and proof-of-concept for CVE-2024-48990, a privilege escalation vulnerability in needrestart allowing local attackers to execute…
 p33d/cve-2024-43363
Python exploit script to test Cacti instances for CVE-2024-43363 RCE via log poisoning. Checks version, injects PHP payload into device names, and…
 ptrstr/cve-2024-32830-poc
PoC code to download files with CVE-2024-32830