LinusWare-Source-Code-Internal

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.

Proof-of-concept exploit for CVE-2022-42899, demonstrating remote code execution in Apache Commons Text 1.5-1.9 via StringSubstitutor interpolation…

Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…

Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'

Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)

Remote code execution exploit for CVE-2019-11043 targeting Nginx with php-fpm. Includes Go and pre-compiled exploit binaries for testing vulnerable…

Wux Blog Editor <= 3.0.0 - Unauthenticated Arbitrary File Upload

Proof-of-concept for authenticated arbitrary file upload in Sitecore 10.3, enabling webshell deployment and remote code execution via the import…

Python exploit for CVE-2018-15133, achieving remote code execution on vulnerable Laravel applications via insecure deserialization of encrypted…

CVE-2023-46818 Python3 Exploit for ISPConfig <= 3.2.11 (language_edit.php) PHP Code Injection Vulnerability

Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…

Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…

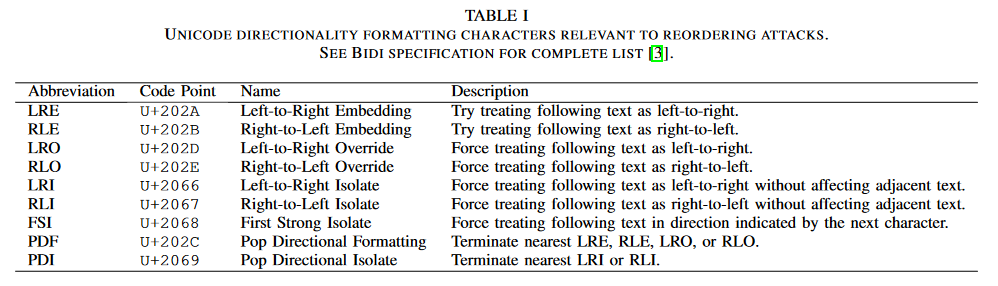
Generate malicious files using recently published bidi-attack (CVE-2021-42574)

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…

CVE-2021-3129-Laravel Debug mode

CVE-2025-64512: pdfminer.six pickle deserialization rce; .pickle.gz + pdf generator w/ custom payloads

[CVE-2017-9822] DotNetNuke Cookie Deserialization Remote Code Execution (RCE)