LinusWare-Source-Code-Internal

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

Sandboxed Lisp dialect for the JVM with immutable data structures, macros, and over 900 core functions. Ideal for safe scripting, automation, and…

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…

My experiments in weaponizing Nim (https://nim-lang.org/)

Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…

Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!

CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…

Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch

A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis

CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…

To reproduce CVE-2021-31630

Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.

Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…

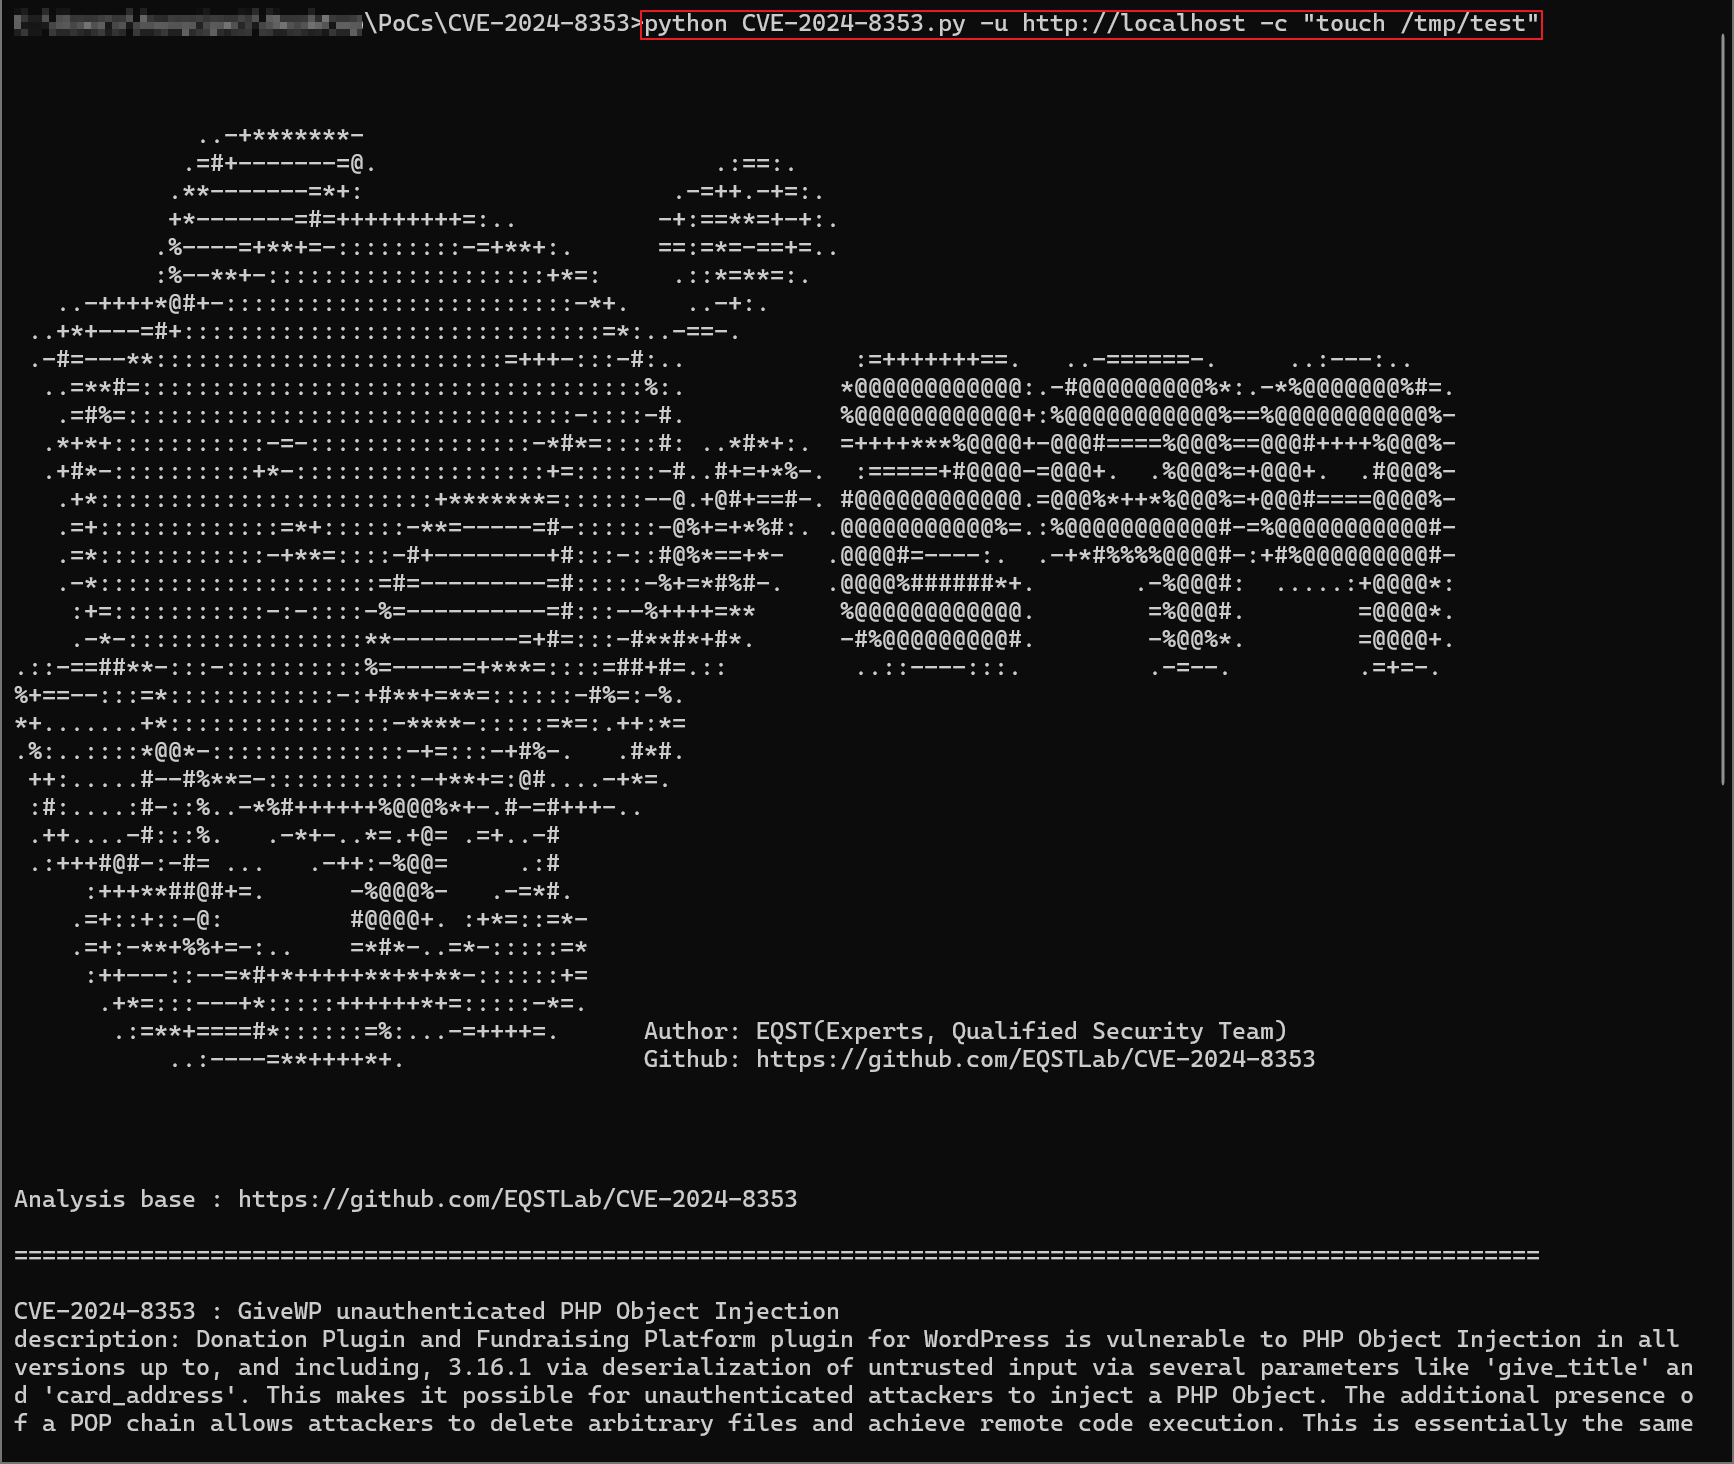
GiveWP PHP Object Injection exploit

PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…

Java SDK for building analytics pipelines that process and enrich unstructured text data with annotations, type systems, and modular analysis engines.

Mutation testing on X.509 Certificate Validation IN OpenSSL v.1.1.1h, based on CVE-2021-3450.

Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE