

CVE-2018-6574-POC
 duckzsc2/cve-2018-6574-poc
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
code-analysisexploitationpenetration-testing+2
duckzsc2/cve-2018-6574-pocProof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 asavior2/cve-2018-6574
CVE-2018-6574 go get RCE
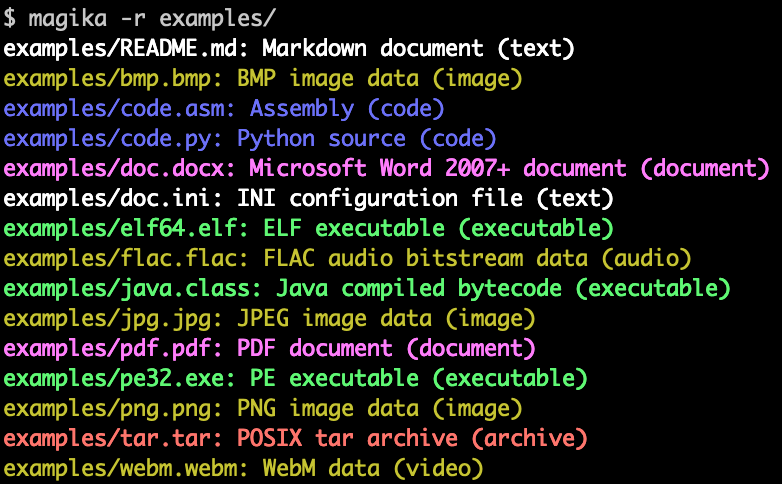 google/magika
Fast and accurate AI powered file content types detection
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
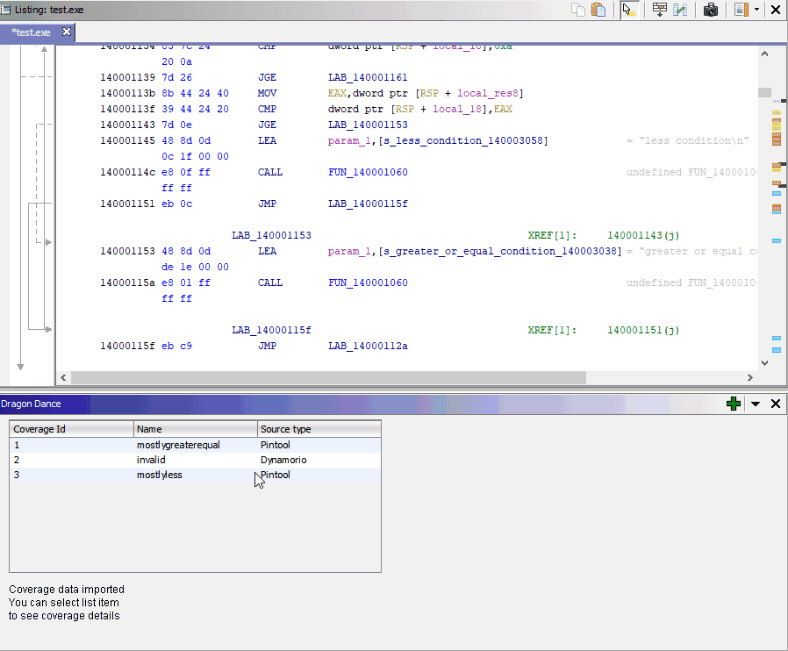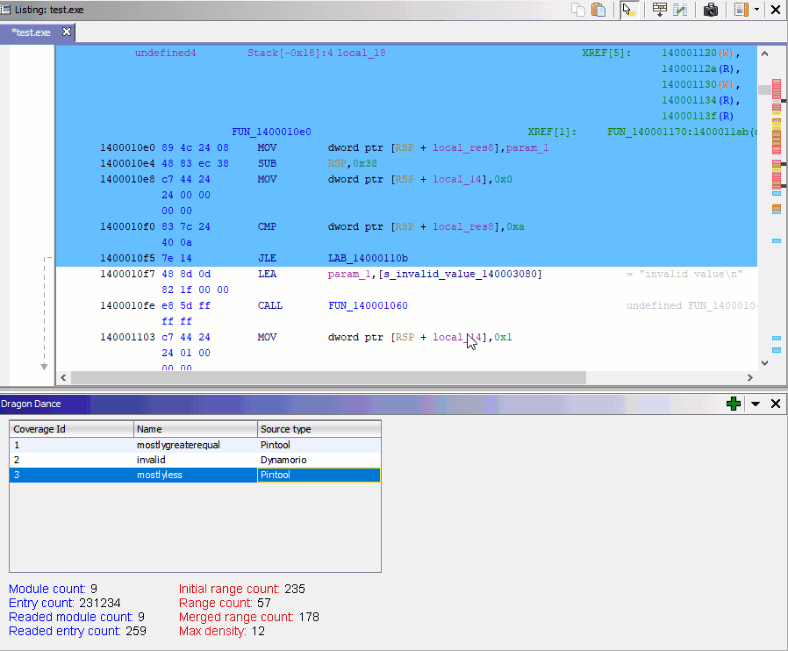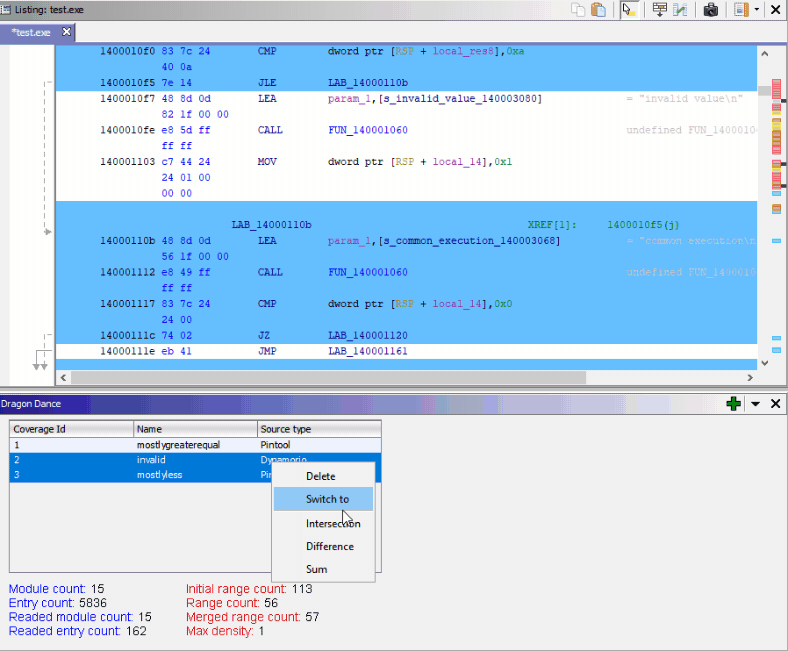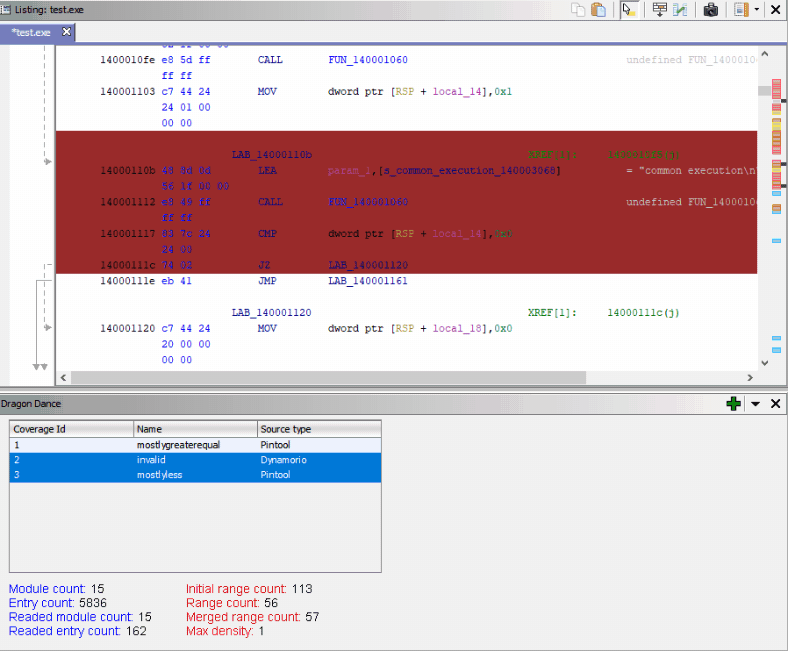 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 josue87/givemesecrets
Use regular expressions to get sensitive information from a given repository (GitHub, pip or npm).
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
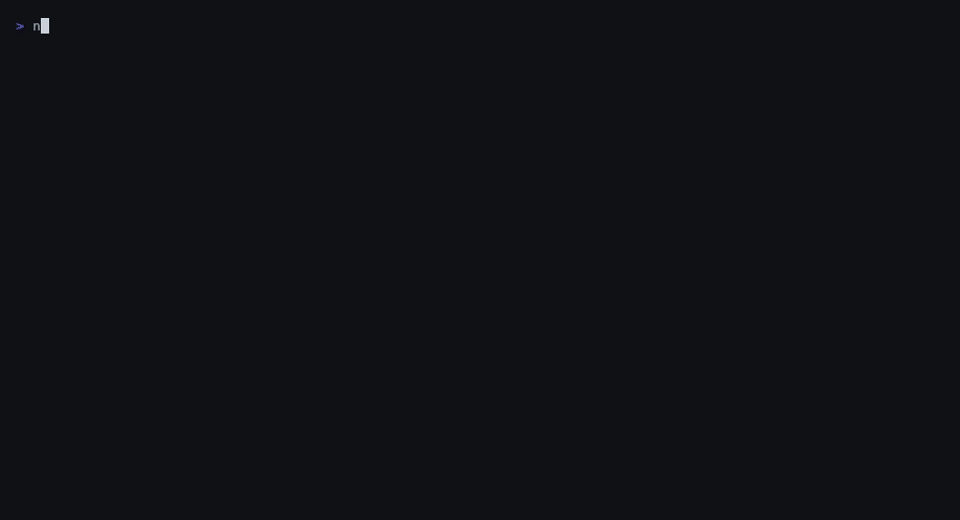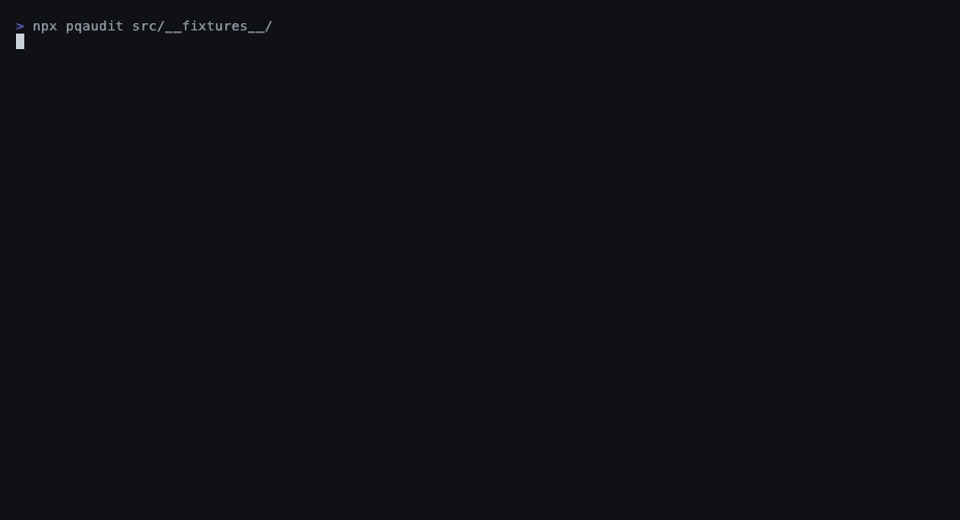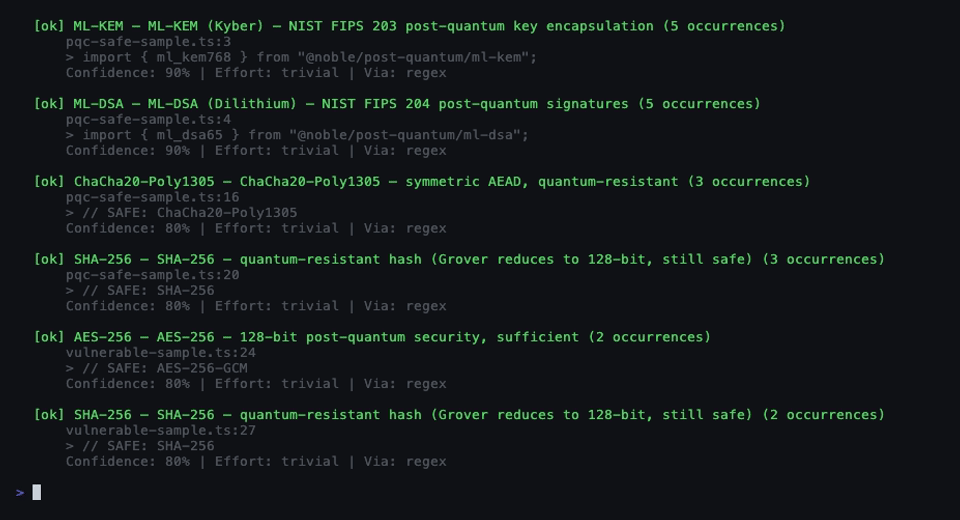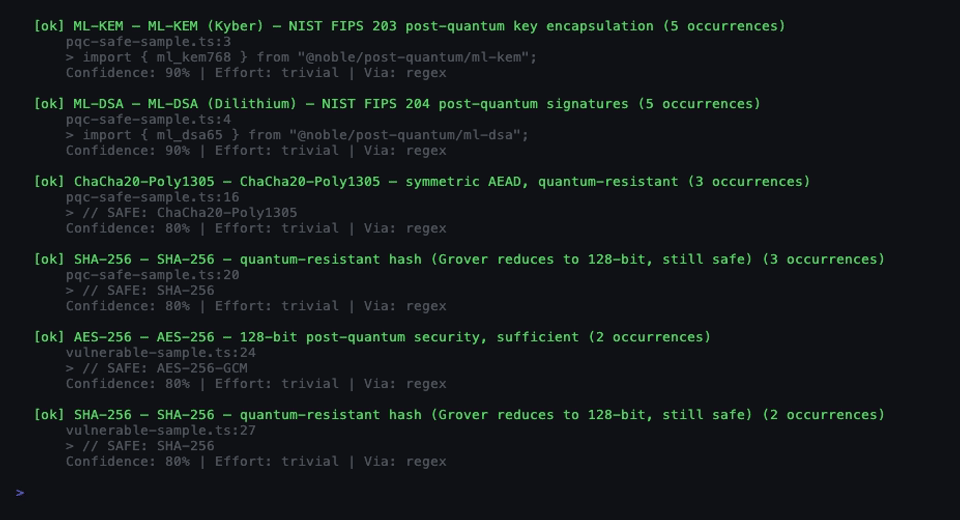 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
 0x00-0x00/cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution Exploit
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build