
bandit
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
code-analysisstatic-code-analysisvulnerability-analysis
pycqa/banditBandit is a tool designed to find common security issues in Python code.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
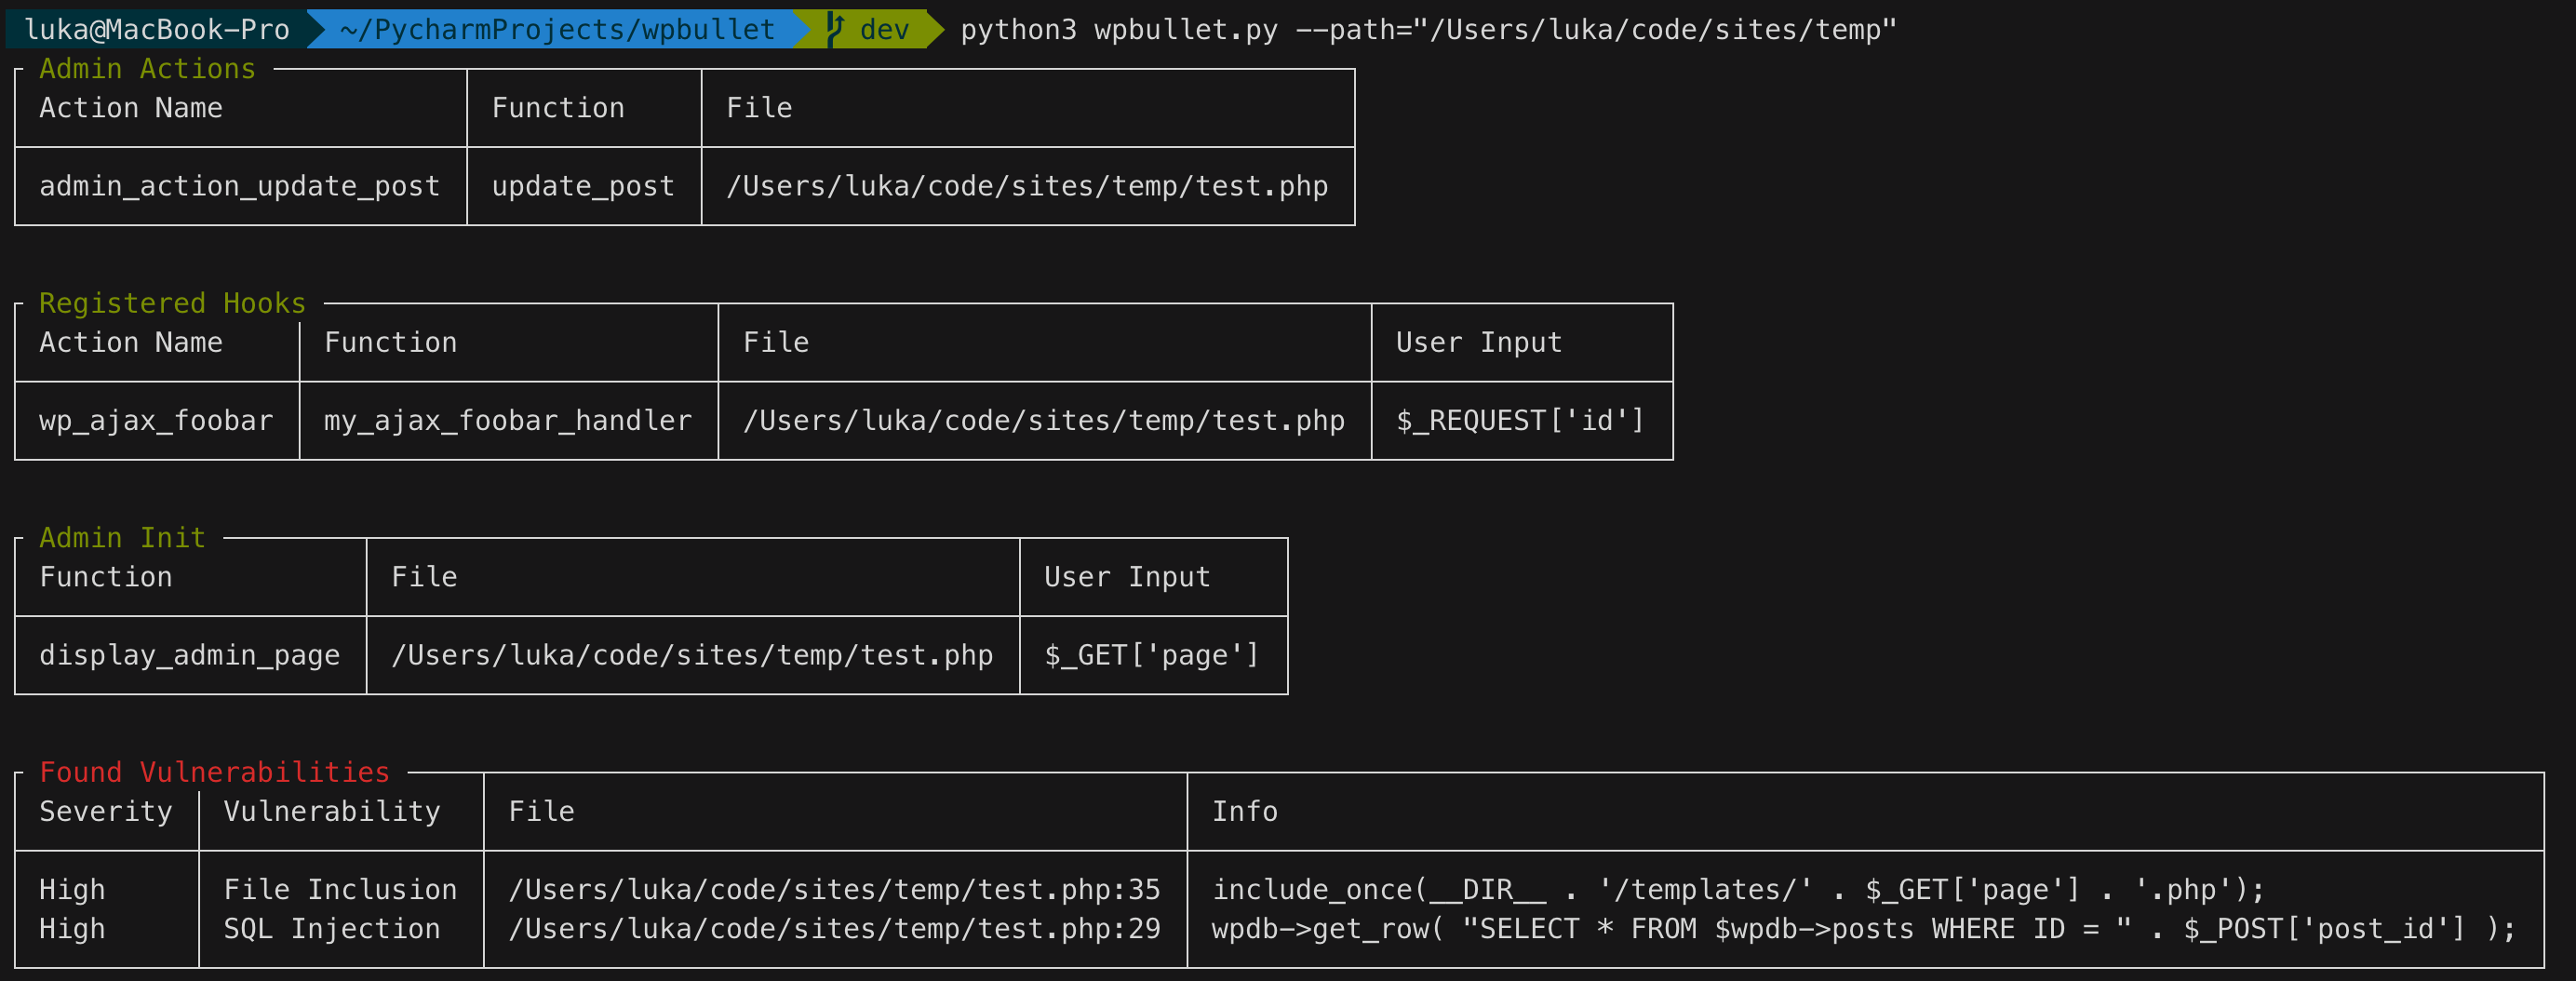 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
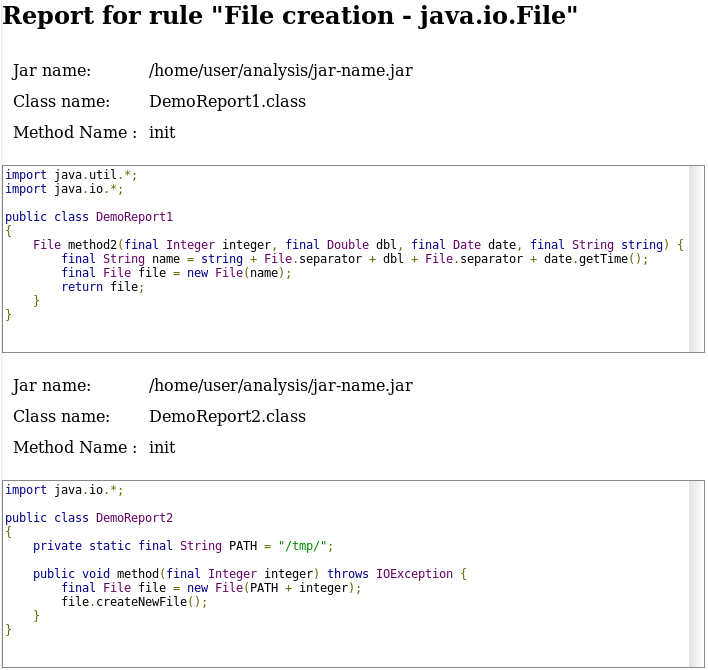 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 inettgmbh/checkmk-log4j-scanner
Checkmk extension that scans JAR, WAR, EAR, and AAR files for Log4j versions vulnerable to CVE-2021-44228 by inspecting META-INF pom.properties…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…