

alter-zero
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
ai-securitycode-analysiscommand-and-control+6
10819h 49m ago
linuztx/alter-zeroRAM efficient terminal agent harness for coding, cybersecurity, and automation.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 louiselalanne/cve-2023-49314
Proof-of-concept exploit for CVE-2023-49314 demonstrating code injection in Asana Desktop on macOS via Electron Fuses, with automated vulnerability…
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 manuelschipper/nah
a guard that blocks catastrophic agent actions
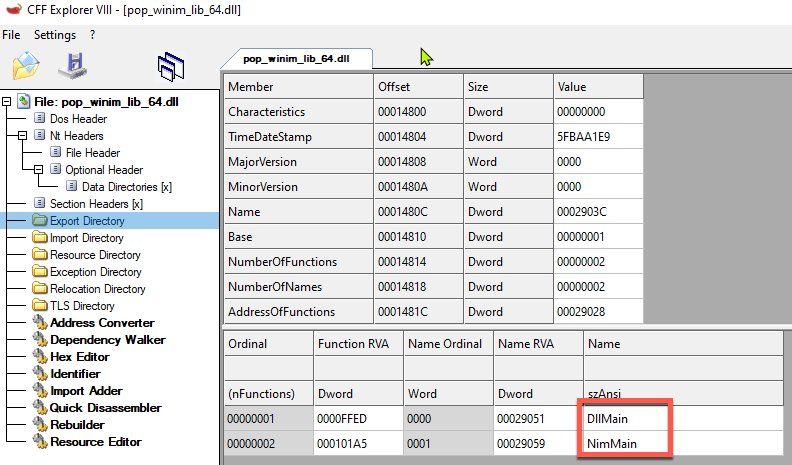 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
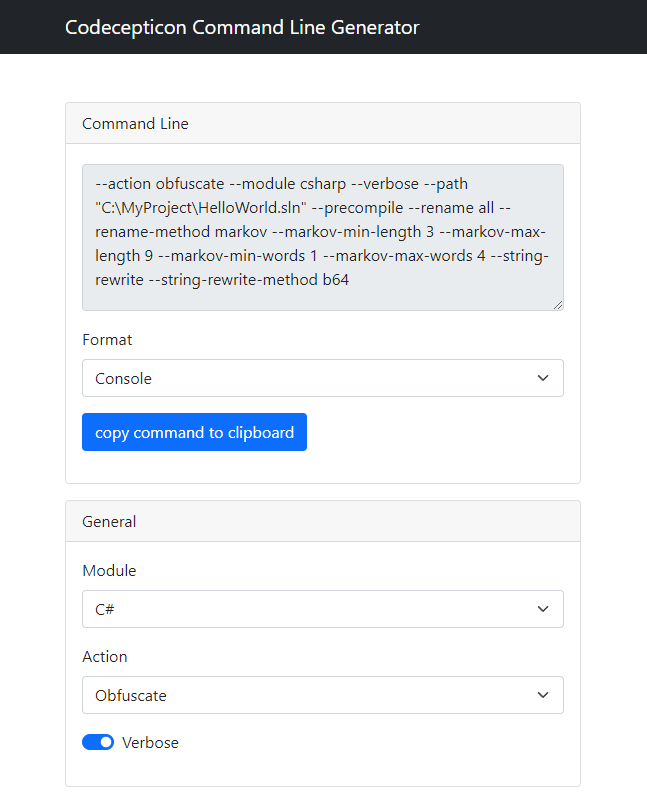 accenture/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
 tranquac/openplc_v3
To reproduce CVE-2021-31630
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
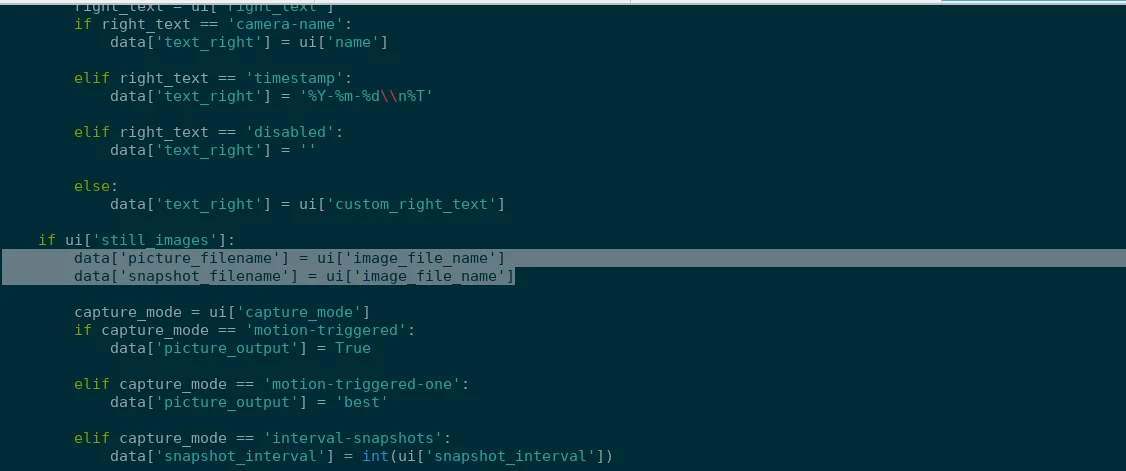 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
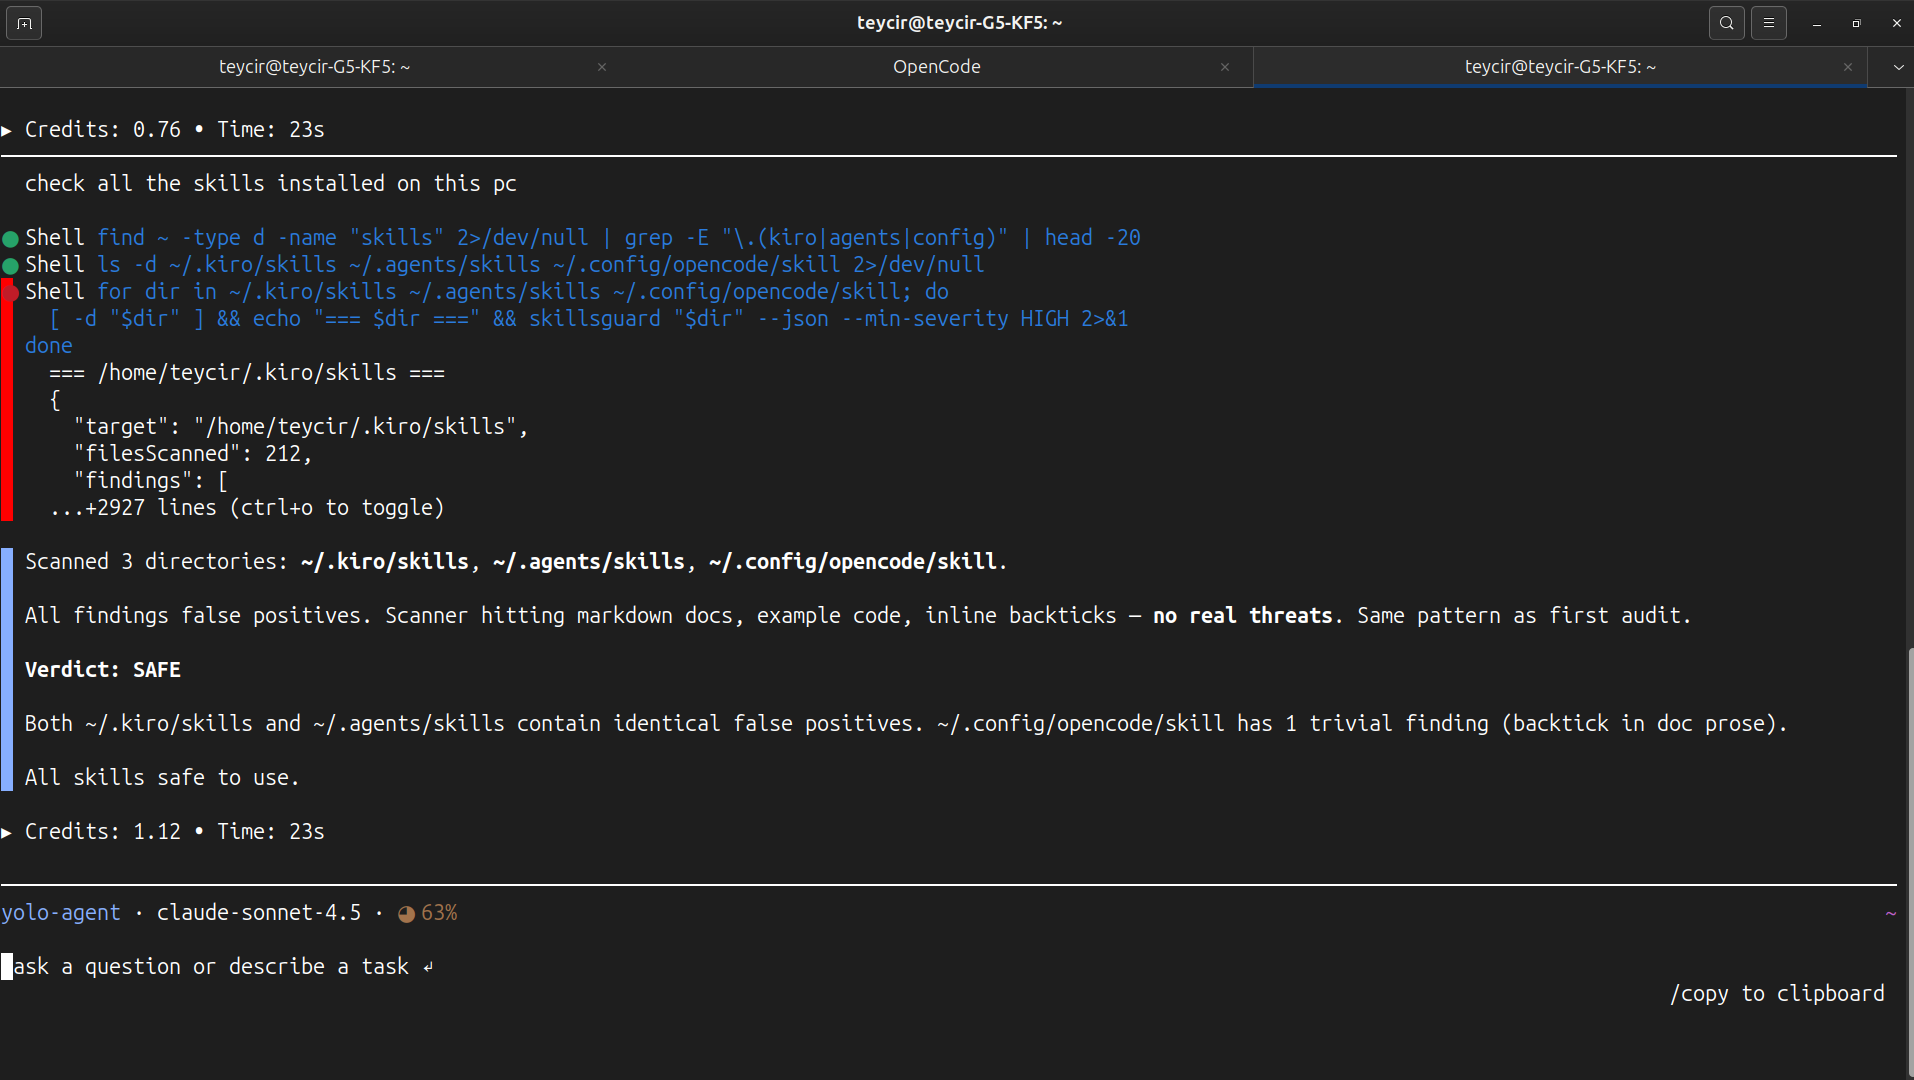 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
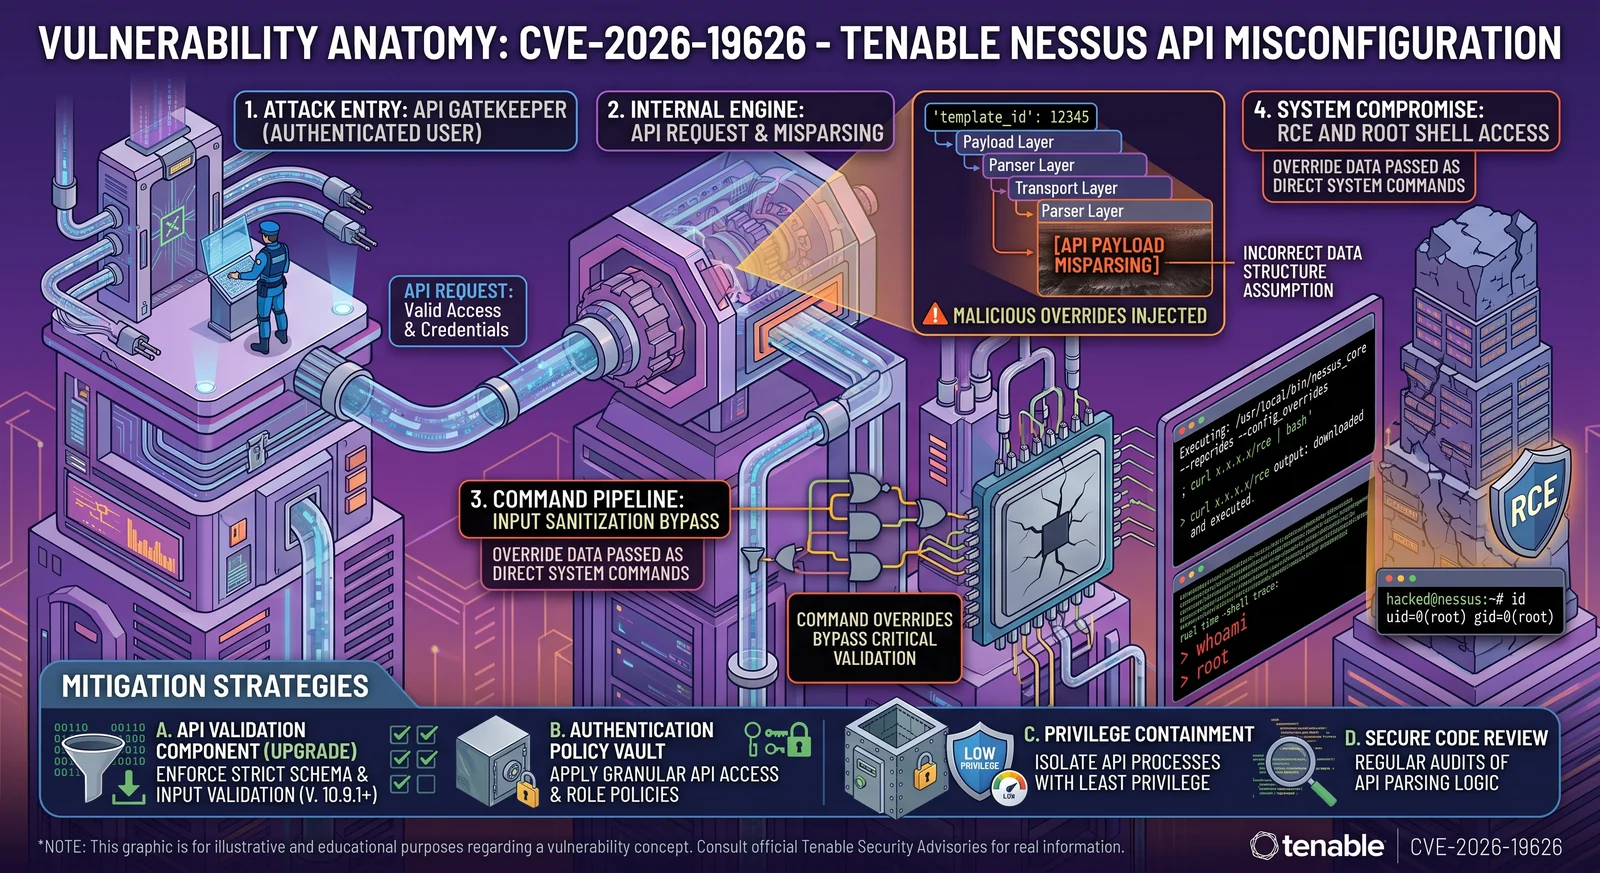 h00die/poc-cve-2026-19626
Proof-of-concept exploit for CVE-2026-19626, an authenticated remote code execution in SecurityCenter report generation, demonstrating a non-admin…
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
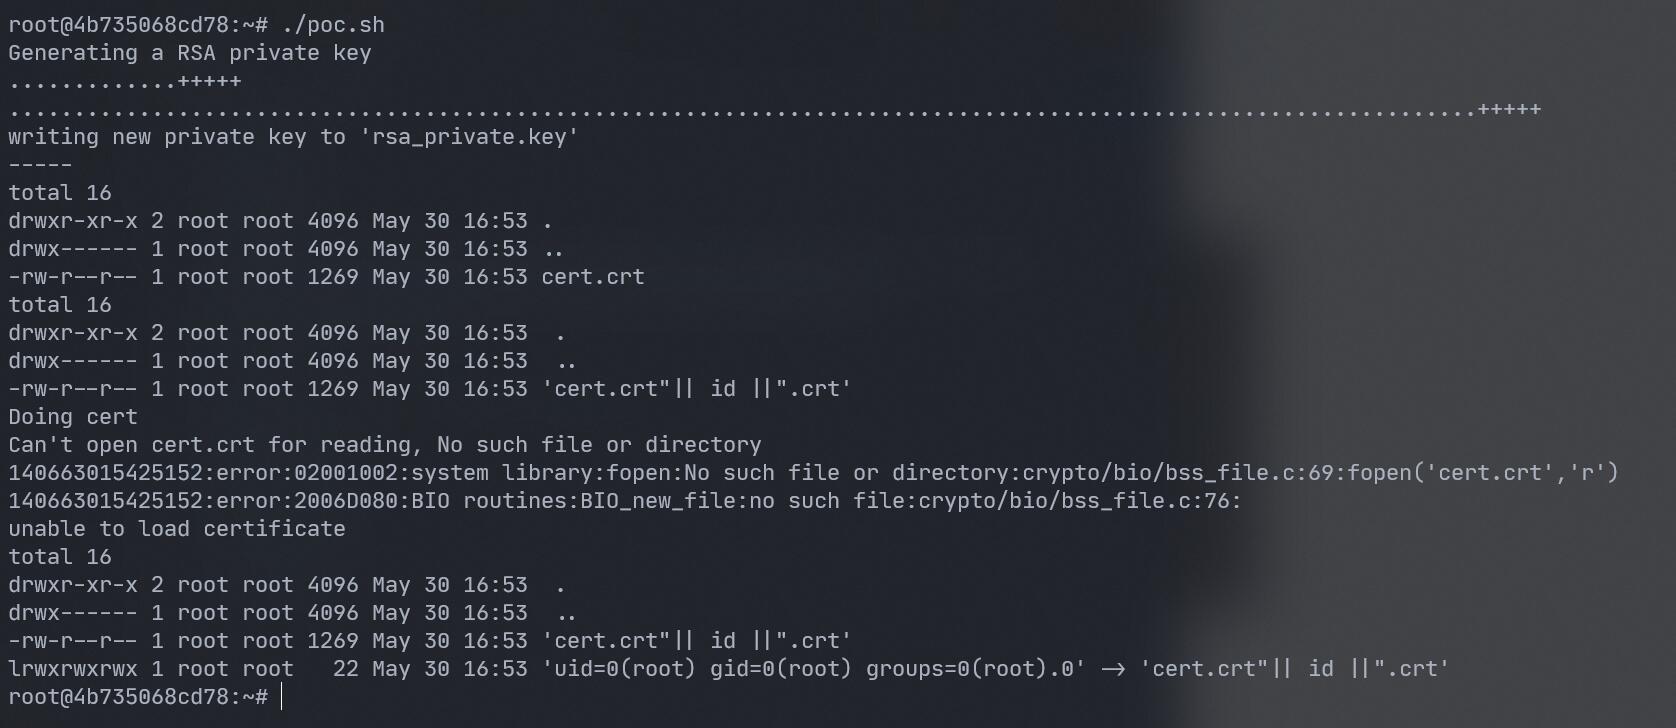 rama291041610/cve-2022-1292
CVE-2022-1292 OpenSSL c_rehash Vulnerability