
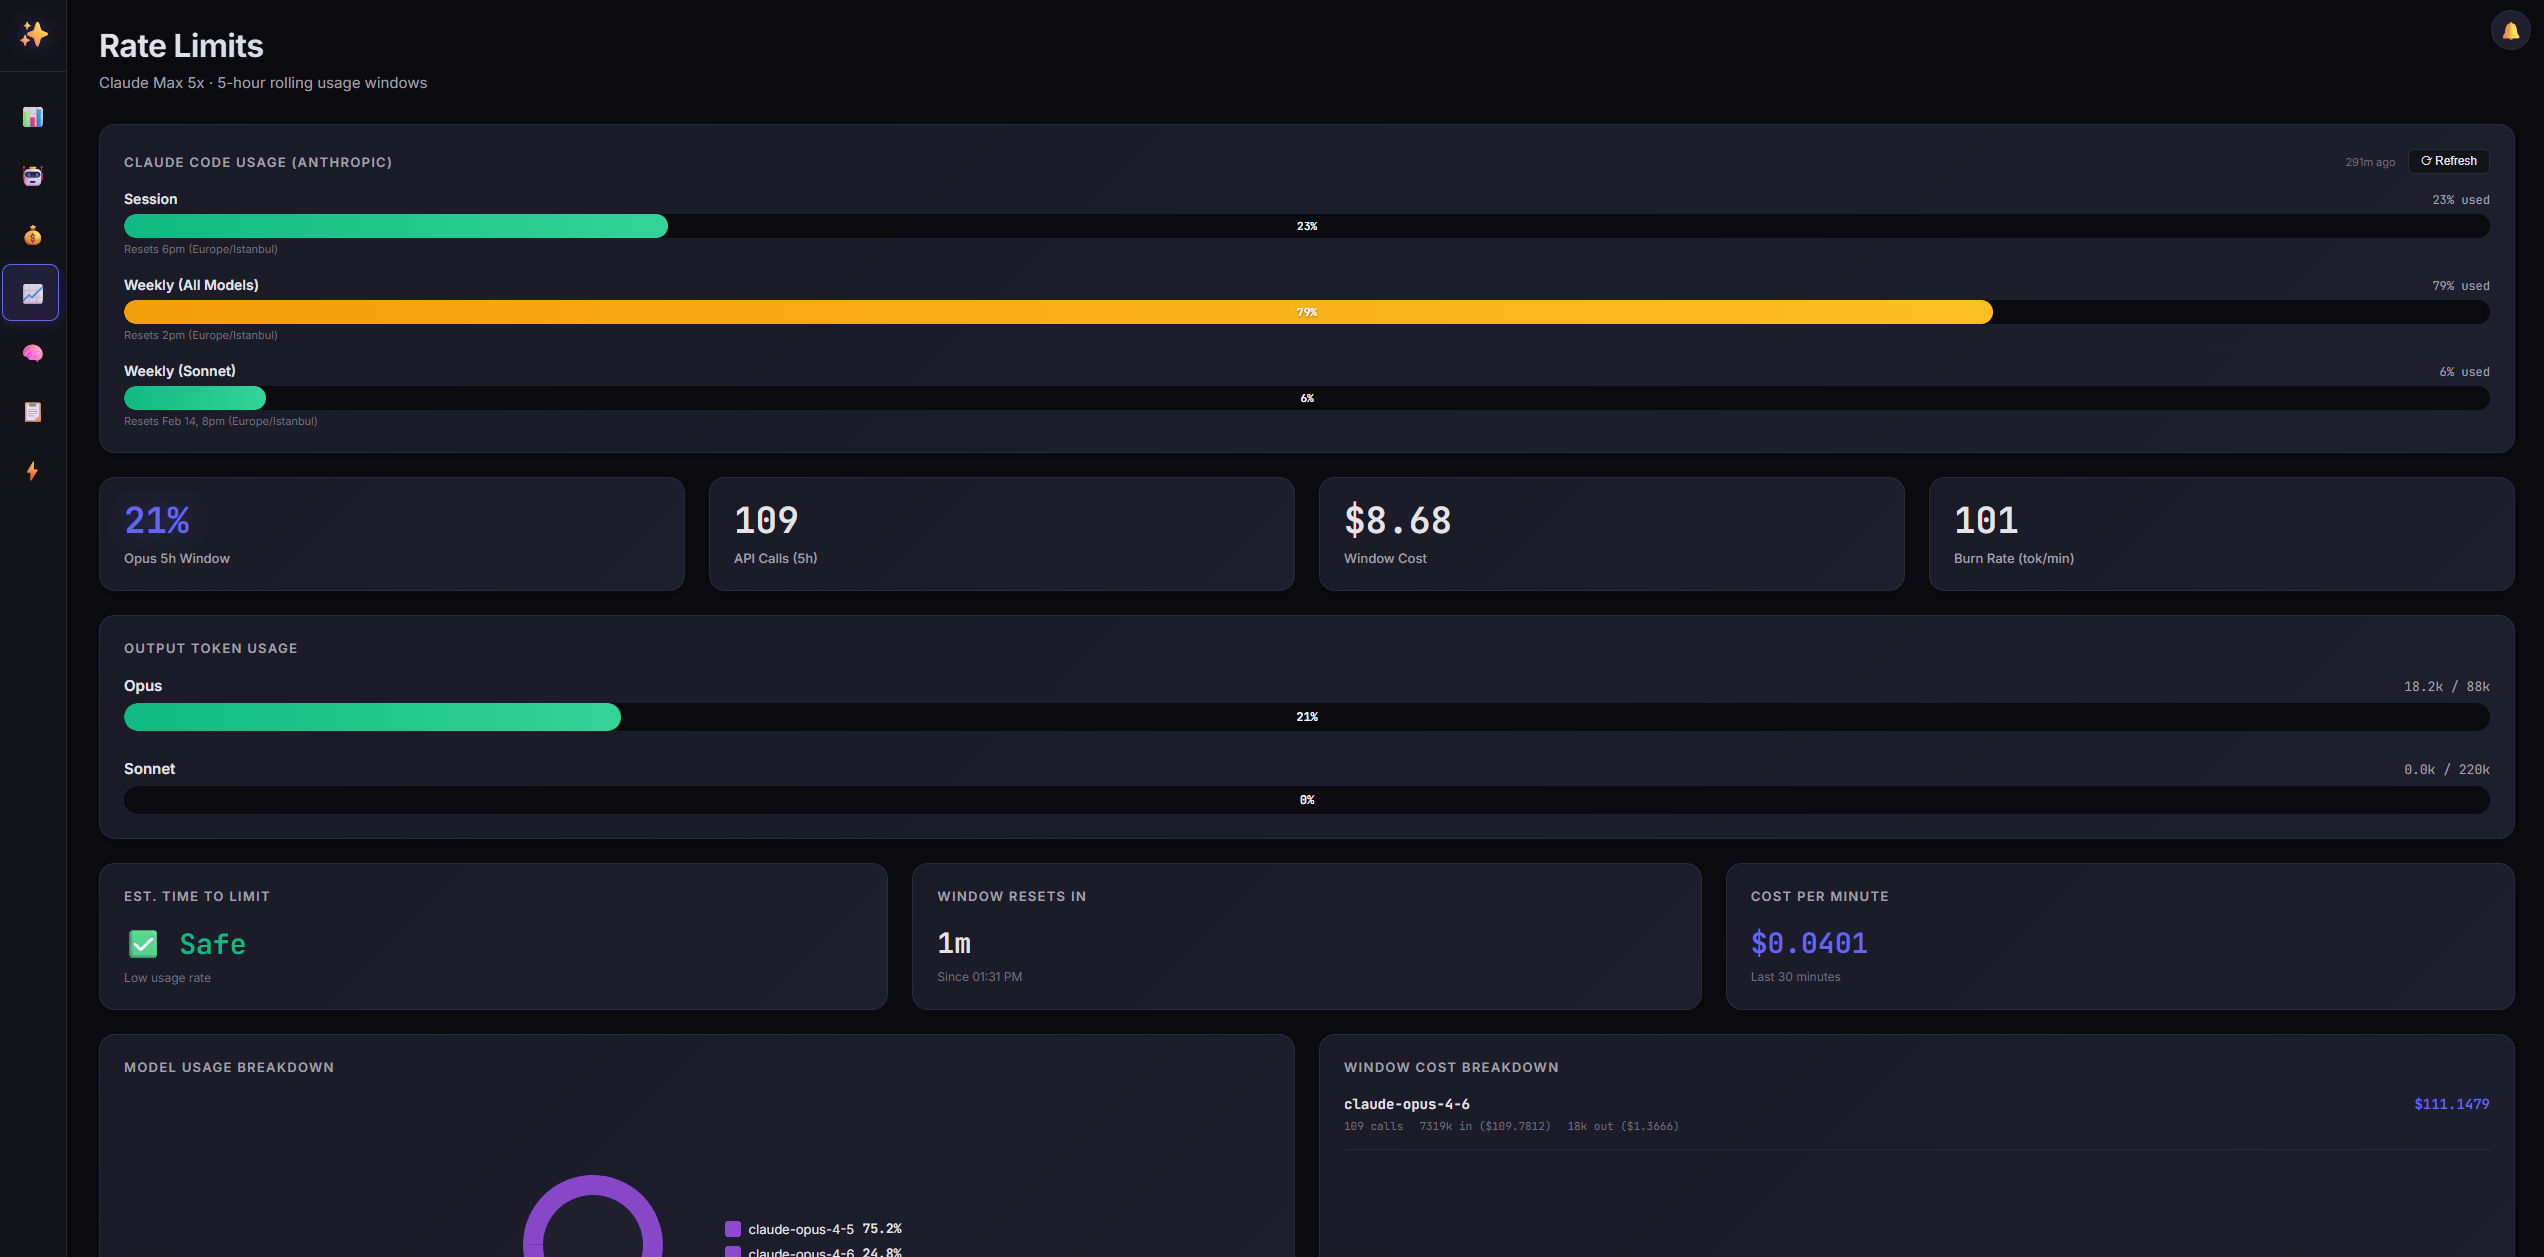
openclaw-dashboard
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
api-securityauthenticationcloud-security+7
701
tugcantopaloglu/openclaw-dashboard🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
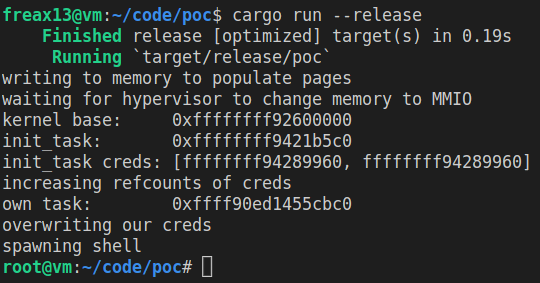 freax13/cve-2023-46813-poc
Proof-of-concept exploit for CVE-2023-46813 targeting AMD SEV-SNP. Escalates privileges by manipulating hypervisor memory type changes to swap task…
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 discordianfish/cve-2022-0185-crash-poc
Docker container that runs a crash proof-of-concept for CVE-2022-0185, a Linux kernel vulnerability. Designed for unprivileged execution to test…
 oscerd/cve-2026-43867
Reproducer for CVE-2026-43867 — Apache Camel camel-pqc AwsSecretsManagerKeyLifecycleManager unsafe key-metadata deserialization (RCE)
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 benzamir/cve-2026-7791
Local Privilege Escalation in Amazon WorkSpaces via TOCTOU and Arbitrary File Write
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 grabesec/xcp_ng_cve-2026-43284_tester
Tester for CVE-2026-43284
 glutenfree69/zigraceexploit
CVE-2021-25741 POC in Zig
 fevar54/poc_cve-2025-29943_write-what-where-condition
Proof-of-concept for CVE-2025-29943 exploiting an undocumented stack engine bit in AMD Zen CPUs to corrupt the stack pointer in SEV-SNP protected…
 mrk336/cve-2025-27480-the-silent-gateway-risk
Letting attackers run malicious code without needing a cracked password, user interaction, or even a foothold in your network. That’s CVE-2025-27480
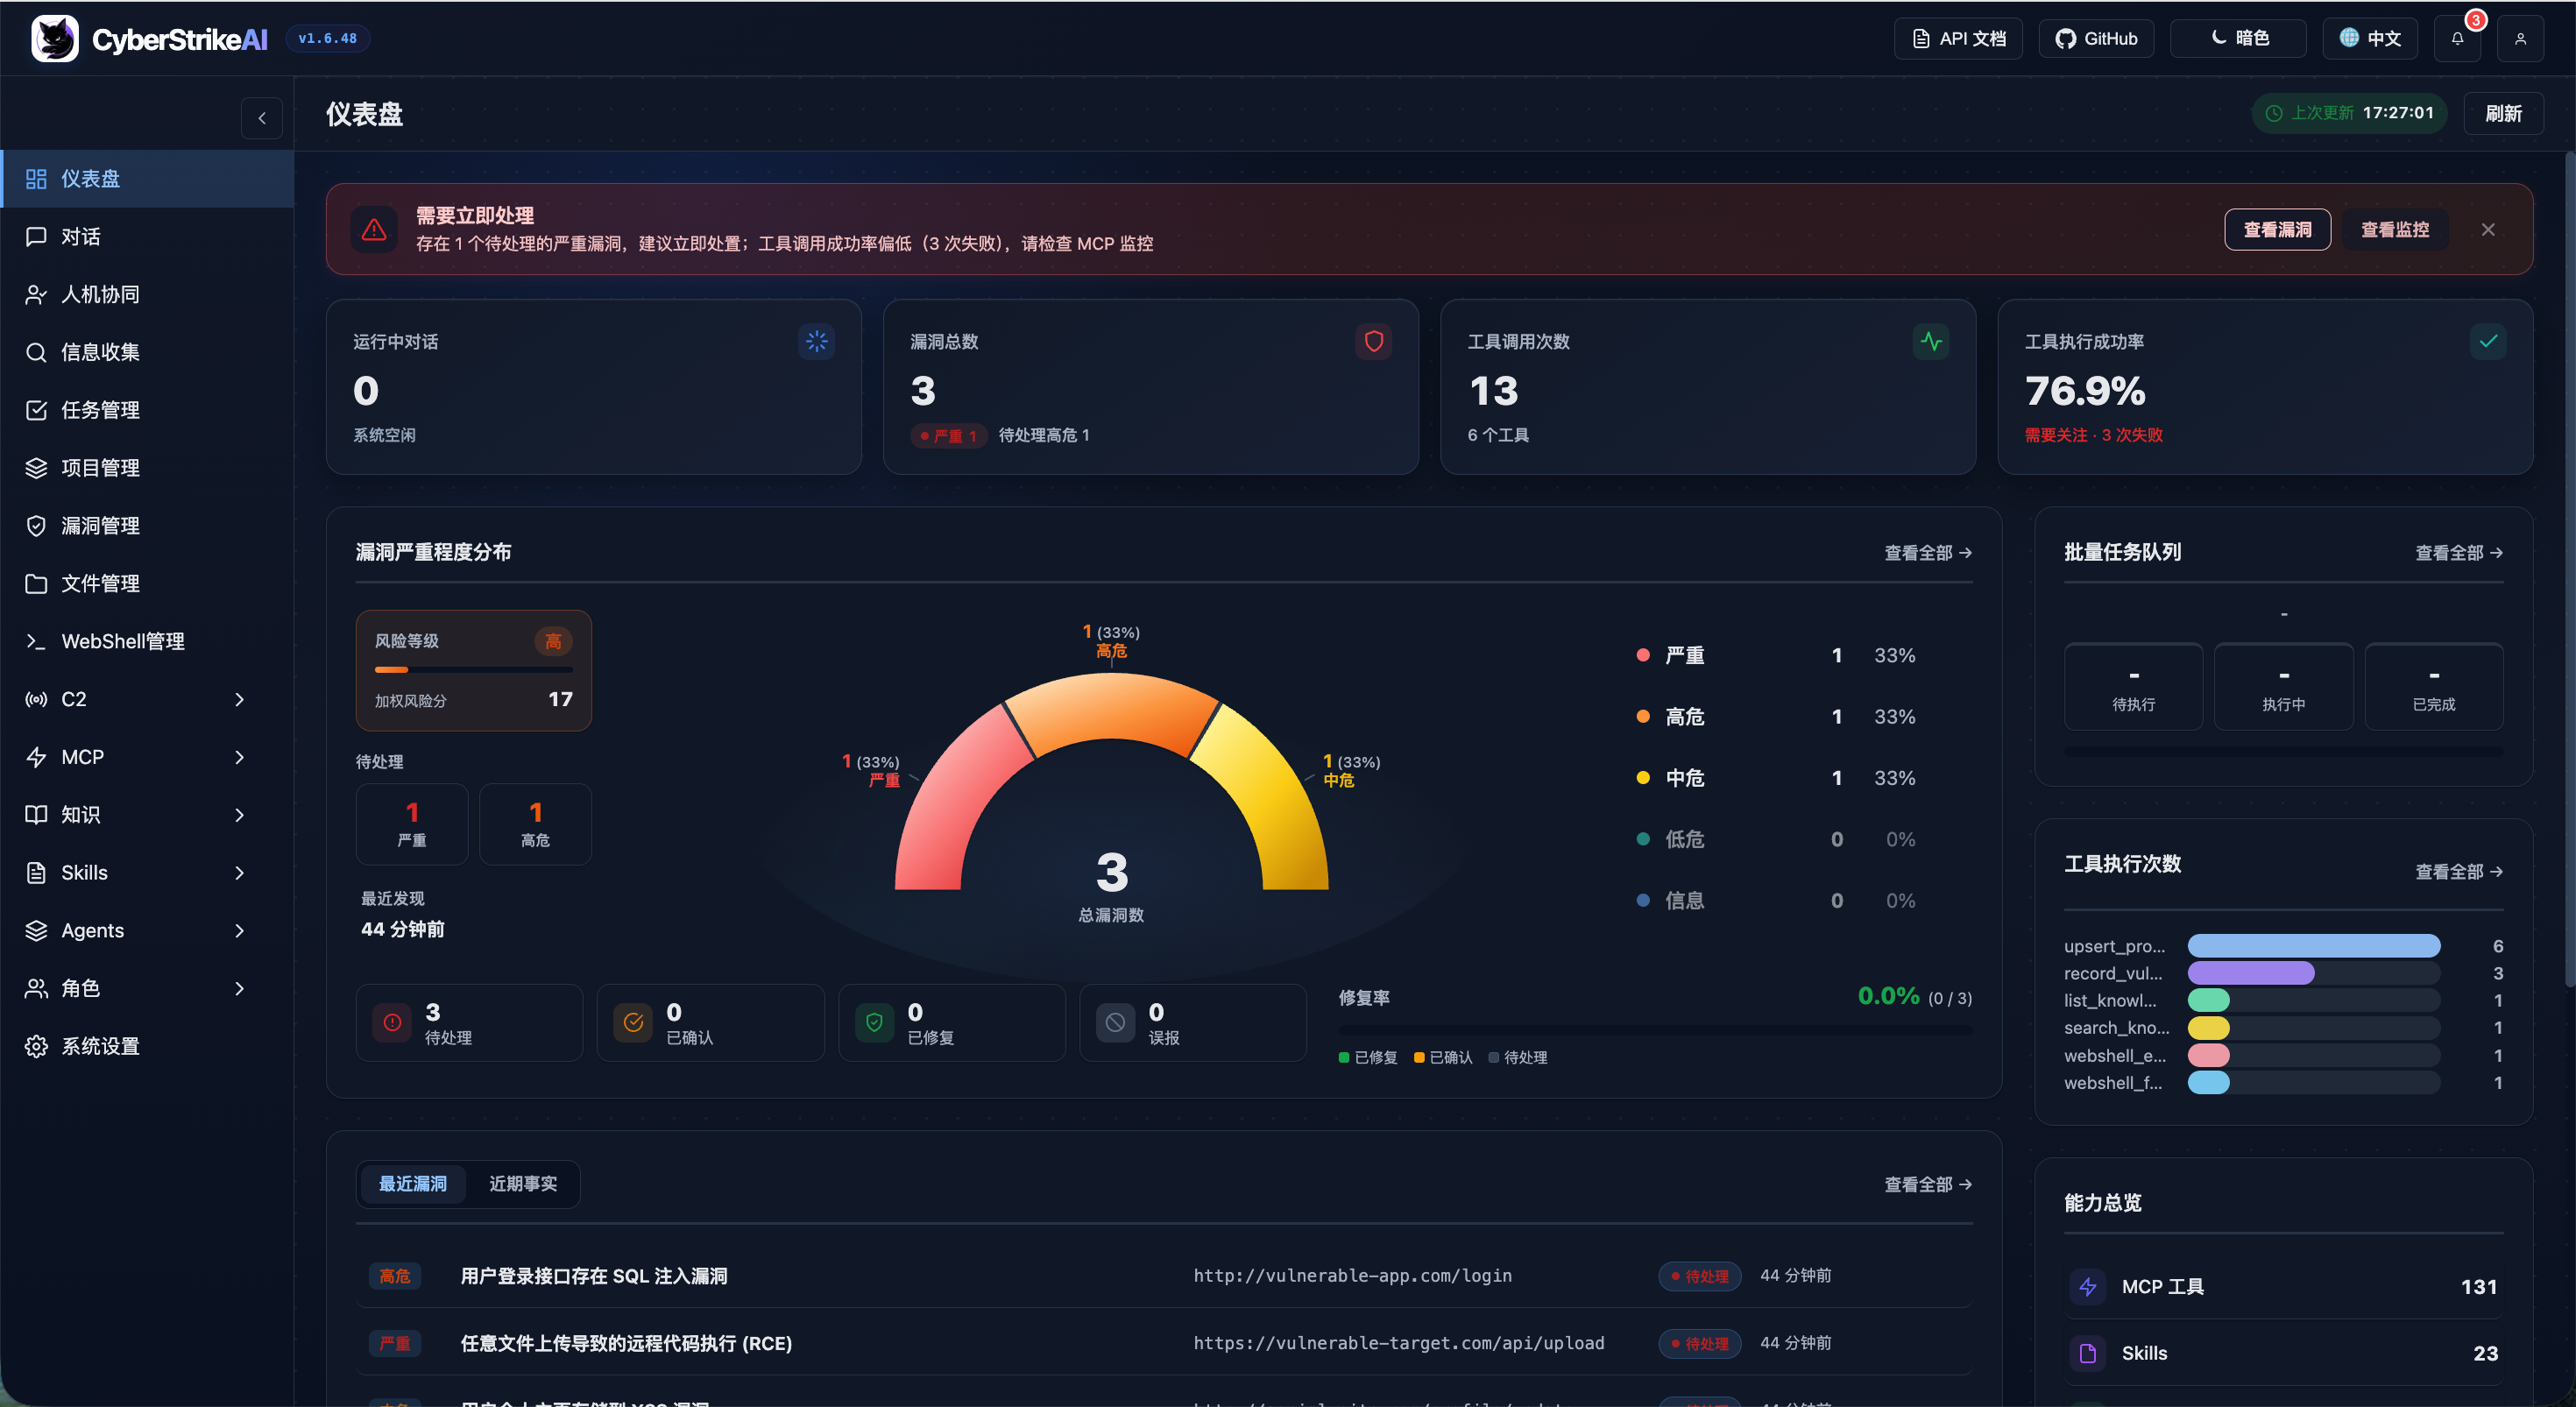 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…