
CVE-2020-8554
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
cloud-securityconfiguration-auditingcontainer-security+3
1
jrmurray000/cve-2020-8554OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 professionallyevil/harpoon
A collection of scripts, and tips and tricks for hacking k8s clusters and containers.
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 in3tinct/taken
Takeover subdomains using AWS dangling elastic ips and have a working POC for Subdomain Takeover.
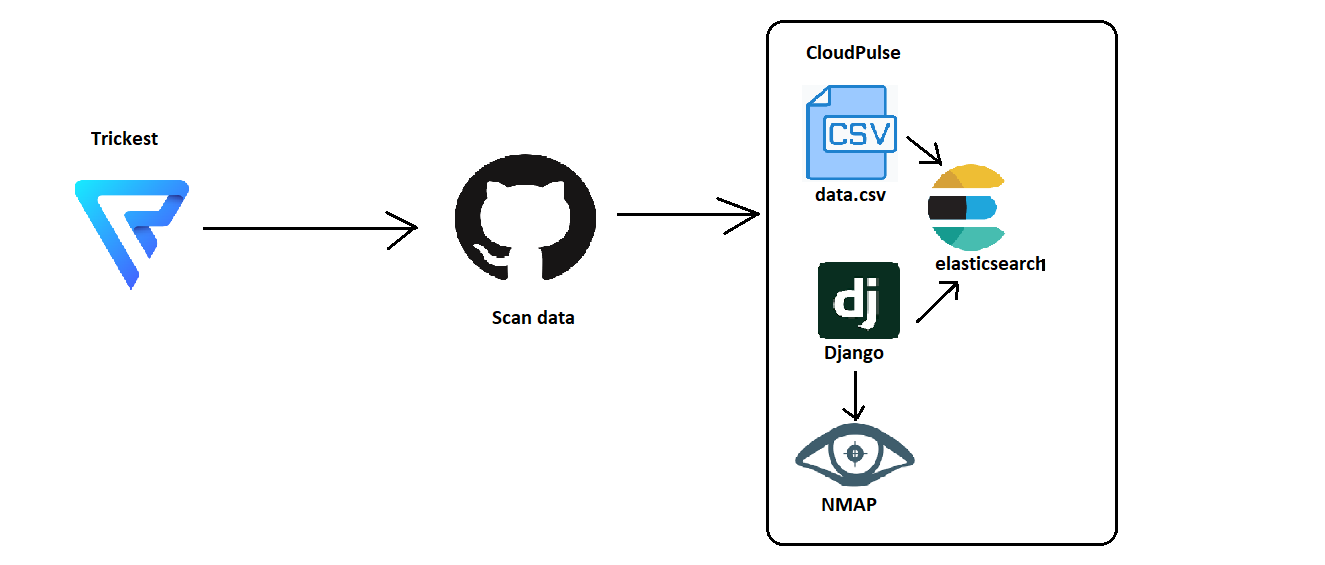 yousseflahouifi/cloudpulse
SSL certificate-based reconnaissance engine for discovering AWS cloud assets, including IPs, subdomains, and domains, with active port scanning for…
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 assetnote/ghostbuster
Eliminate dangling elastic IPs by performing analysis on your resources within all your AWS accounts.
 mokokash/ejbca-pqc-lab
Pure PQC two-tier PKI hierarchy using ML-DSA-65 (NIST FIPS 204) on EJBCA Community Edition — Root CA + Sub CA with CRL and OCSP