eclipse__hawkbit_CVE-2020-27219_0-3-0M6

Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…

Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…

Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…

Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.

Salt recipe for shellshock (CVE-2014-6271)

A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …

PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…

Batch upgrade all your Next.js apps to patched versions - fight back against CVE-2025-55183/55184/67779

HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…

Docker-based proof-of-concept demonstrating CVE-2025-23320 in NVIDIA Triton inference server, exploiting shared memory key leakage to trigger an…

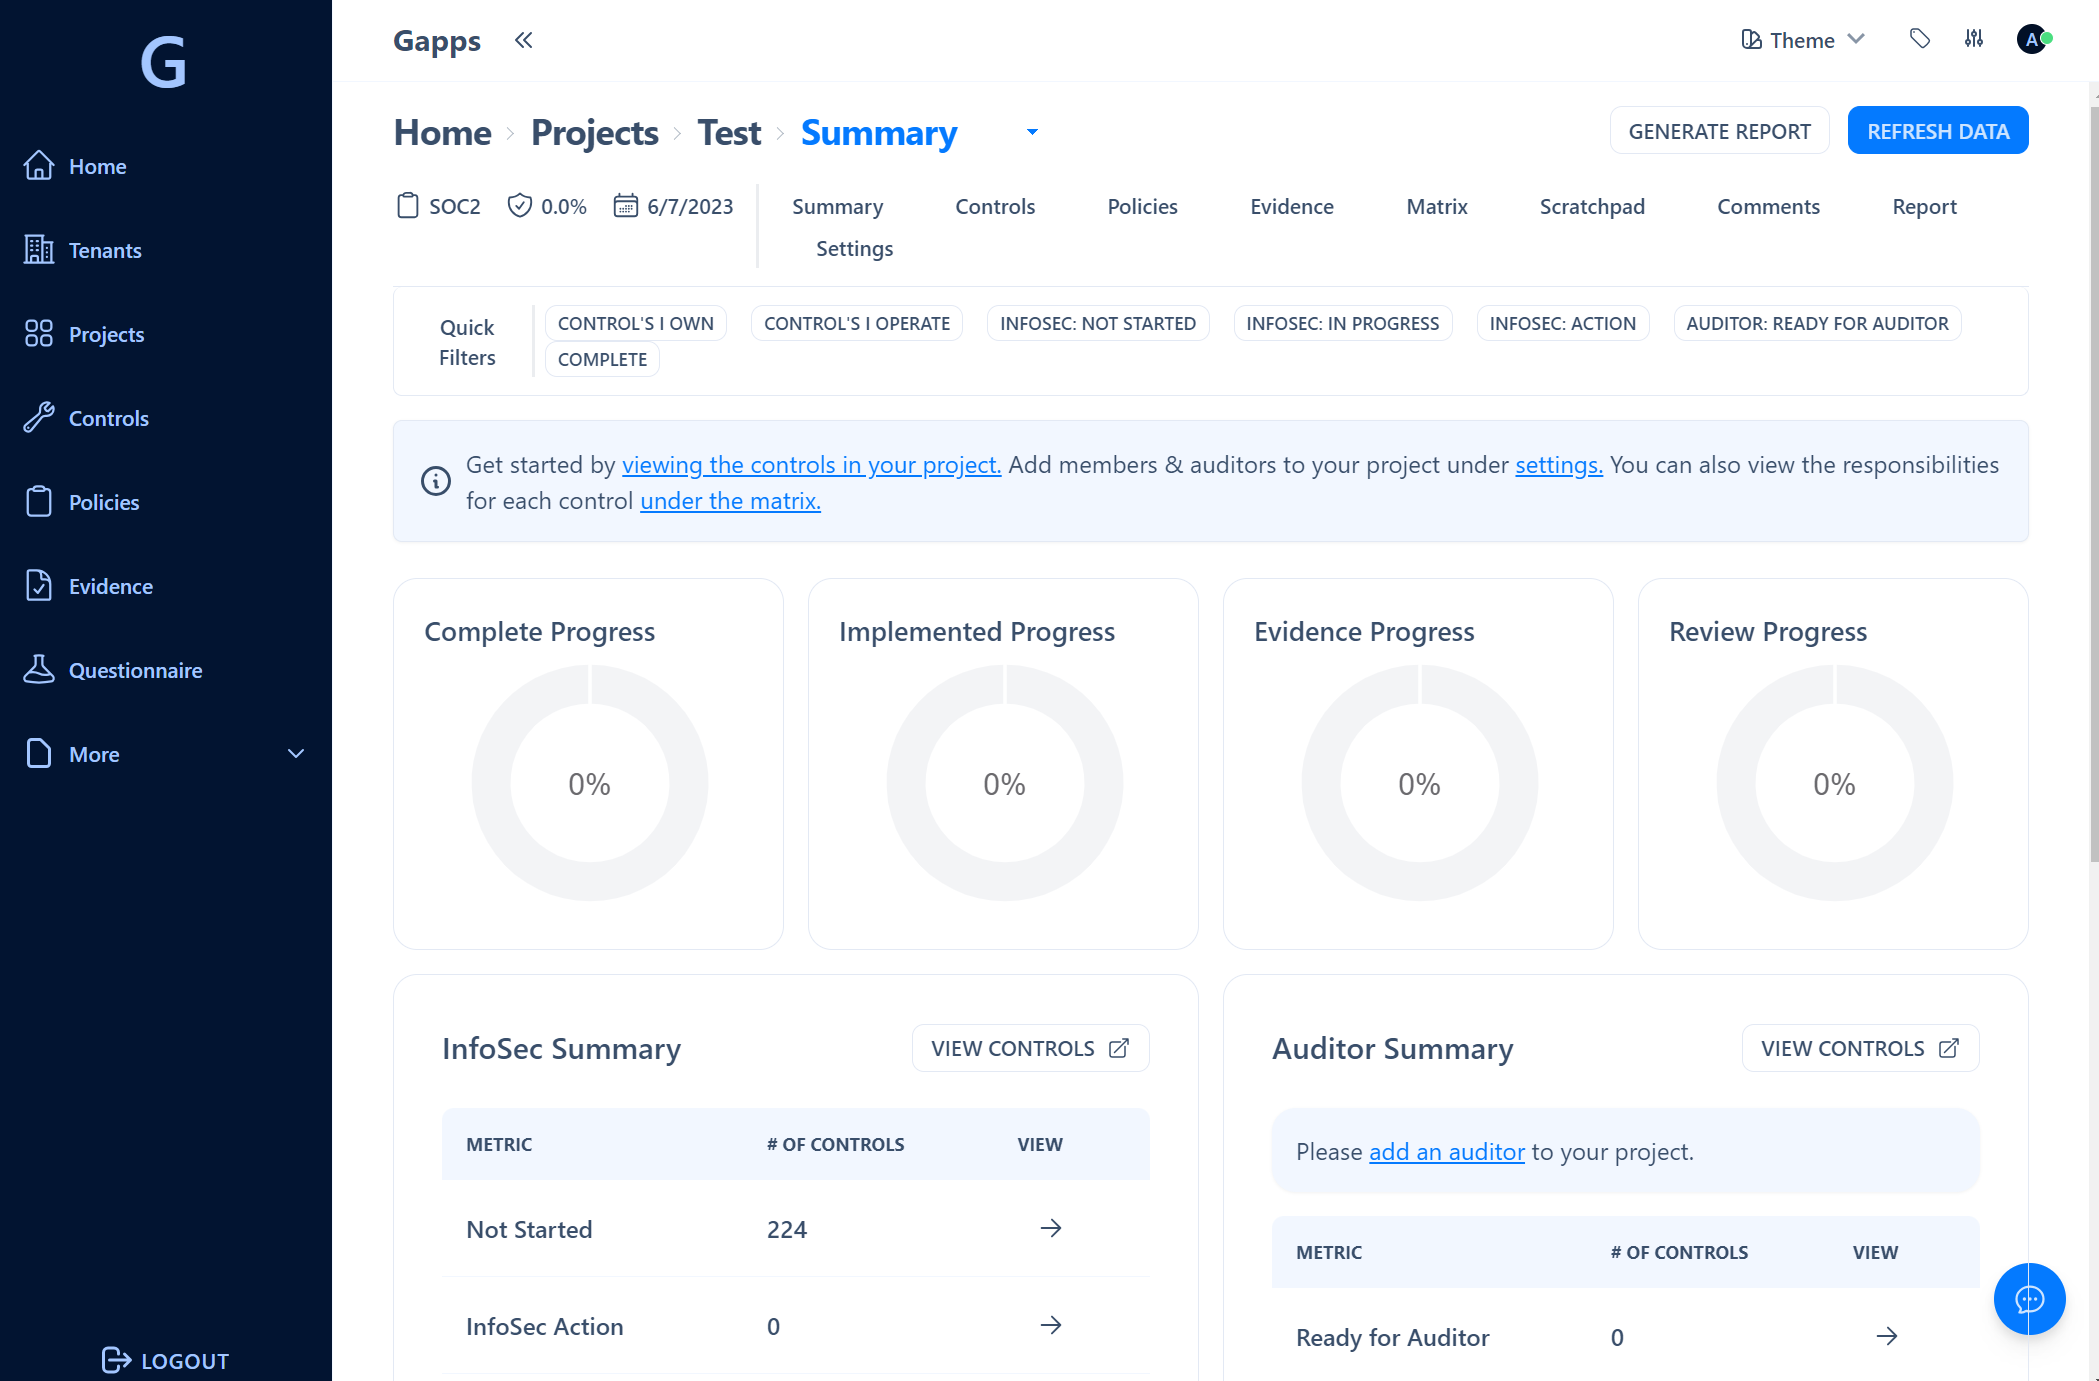
Security compliance platform - SOC2, CMMC, ASVS, ISO27001, HIPAA, NIST CSF, NIST 800-53, CSC CIS 18, PCI DSS, SSF tracking

Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities


CVE-2021-25741 POC in Zig

Remote Code Execution in LocalStack 0.12.6