

o365-attack-toolkit
 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365
cloud-securitydata-exfiltrationemail-security+5
1.1k
mdsecactivebreach/o365-attack-toolkitA toolkit to attack Office365
 synacktiv/gh-hijack-runner
A python script to create a fake GitHub runner and hijack pipeline jobs to leak CI/CD secrets.
 george0papasotiriou/cve-2026-3333-dns-rebinding-to-steal-cloud-metadata
Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.
 dshamany/privatesphare
An at-rest encrypted filesharing application with multiple clients who seek to share privately, without tracking.
 shoucheng3/asf__nifi_cve-2023-34468_1-21-00
Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.
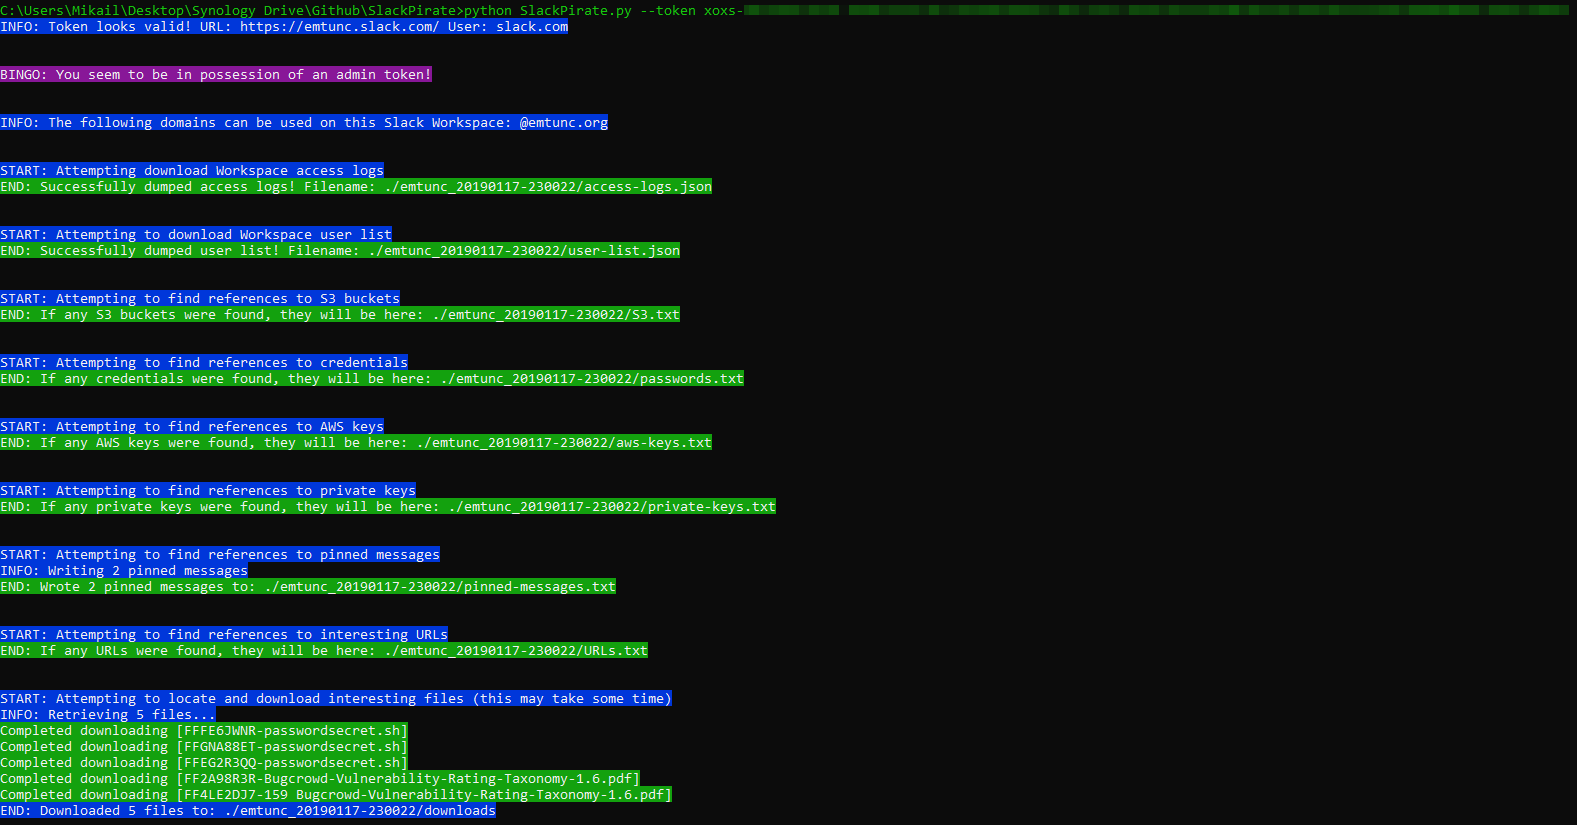 emtunc/slackpirate
Slack Enumeration and Extraction Tool - extract sensitive information from a Slack Workspace
 luemmelsec/apex
Azure Post Exploitation Framework
 moloch--/leakdb
Web-Scale NoSQL Idempotent Cloud-Native Big-Data Serverless Plaintext Credential Search
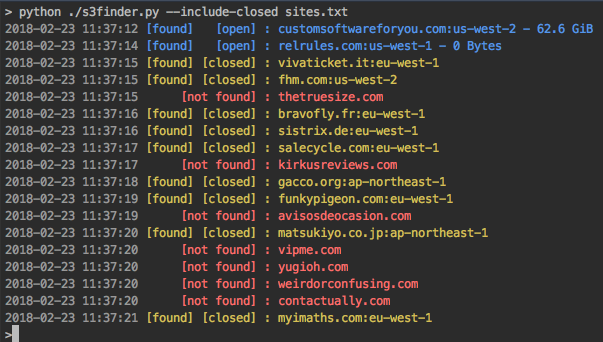 yehgdotnet/s3scanner
Scan for open S3 buckets and dump
 antisnatchor/phishlulz
Automated phishing campaign toolset that spawns dedicated AWS EC2 instances with integrated PhishingFrenzy and BeEF, plus subdomain discovery and…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
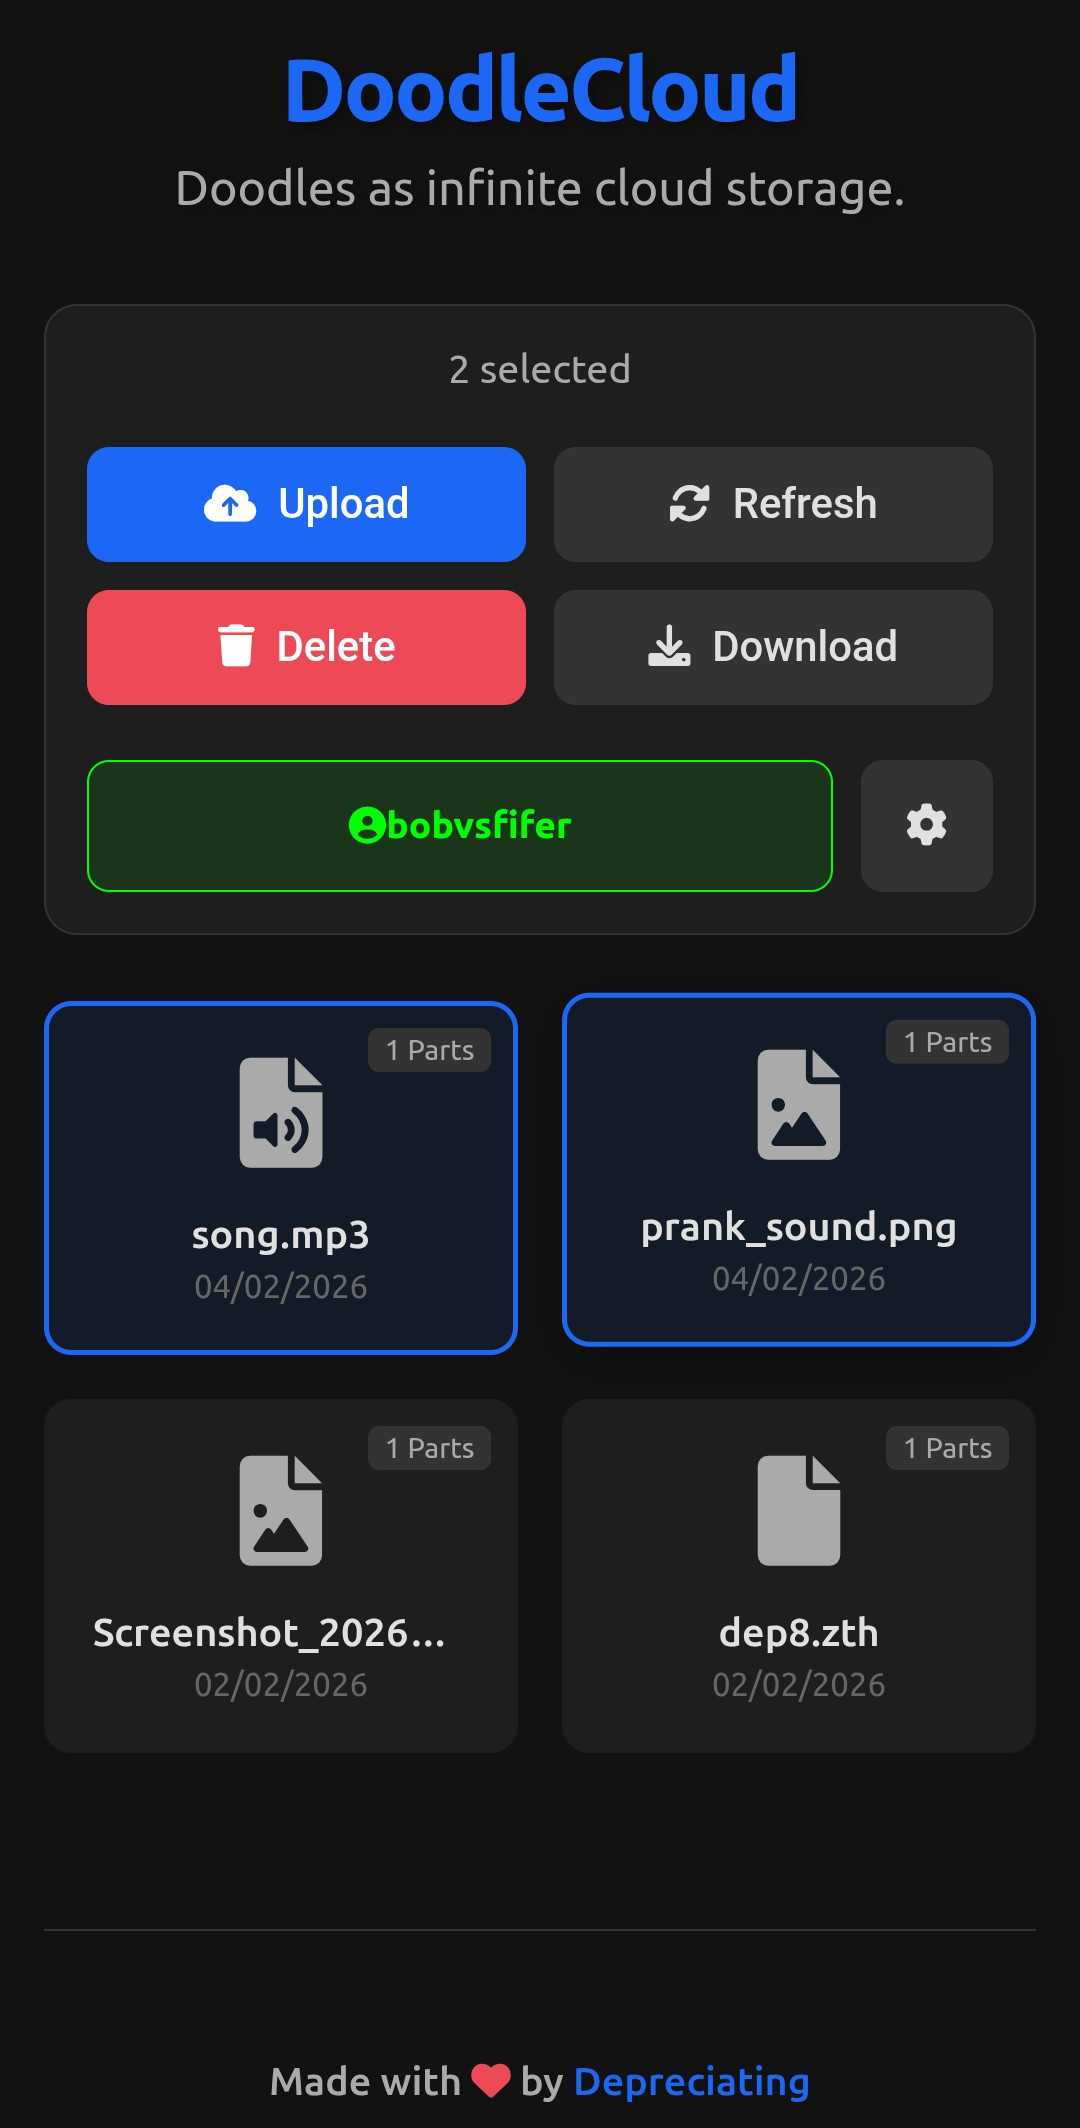 depreciating/doodlecloud
Cloud Storage using Instagram.
 cuerz/cve-2023-28432
CVE-2023-28432 MinIO敏感信息泄露检测脚本
 krishsharma0413/syncord
Syncord is a CLI-based file synchronization and storage tool that uses Discord as an encrypted file storage.
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)