

grapheneX
 graphenex/graphenex
Automated System Hardening Framework
cloud-securityconfiguration-auditingdefensive-tools+2
graphenex/graphenexAutomated System Hardening Framework
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…
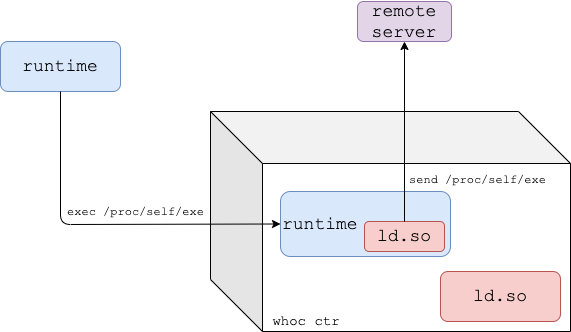 twistlock/whoc
A container image that exfiltrates the underlying container runtime to a remote server
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 vinieger/vinieger-cve-2025-48384-dockerfile
PoC dockerfile image for CVE-2025-48384
 patrickpichler/grafana-cve-2024-9264
Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 rtvkiz/minimal
Minimal CVE Hardened container image collection
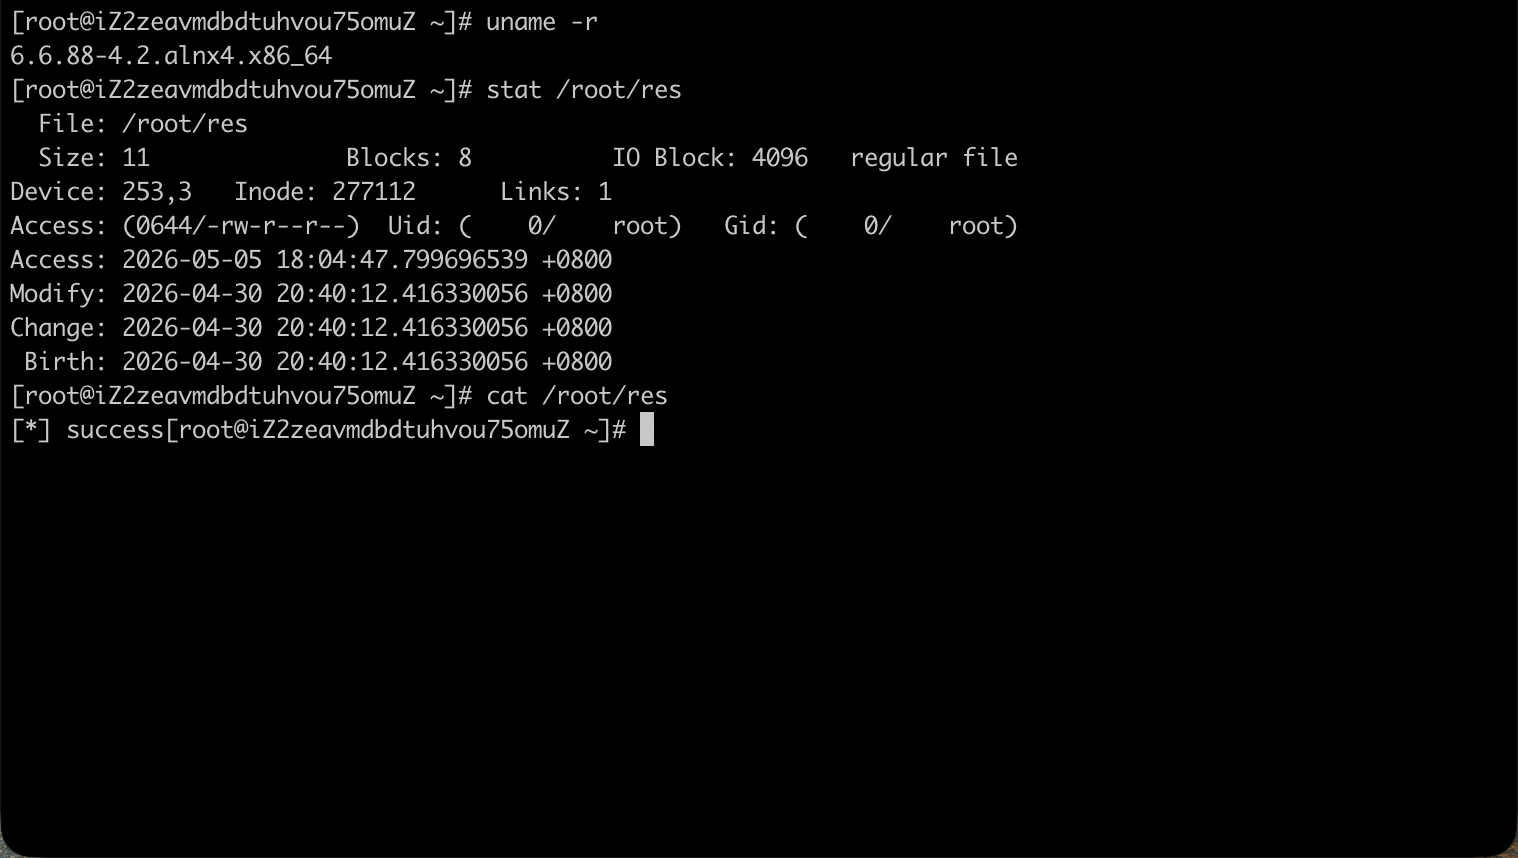 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 jackdpeterson/imagick_secure_puppet
Puppet module to harden ImageMagick policy.xml against CVE-2016-3714 by restricting dangerous image processing directives.
 logsec/cve-2013-0212
Exploit for CVE-2013-0212 targeting OpenStack Glance image service. Demonstrates authentication bypass vulnerability for security testing and…
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 devenes/text4shell-cve-2022-42889
Kubernetes Lab for CVE-2022-42889