
libvirt-CVE-2014-1447
 tagatac/libvirt-cve-2014-1447
Libvirt - Unauthenticated DoS Vulnerability (Exploit & Time Randomization to Thwart It)
cloud-securityexploitationpenetration-testing+1
tagatac/libvirt-cve-2014-1447Libvirt - Unauthenticated DoS Vulnerability (Exploit & Time Randomization to Thwart It)
 appsec-forge/appsec-forge
Structured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…
 jinlei-chen-uwo/cve-2024-34351-demo
Minimal Next.js 14.0.0 demo app for CVE-2024-34351 SSRF vulnerability. Includes exploit setup, interactsh confirmation, Burp interception, and AWS…
 imohammed28/cve-2024-10220-test
Kubernetes gitRepo volume vulnerability (CVE-2024-10220) exploit for controlled HPC security research, demonstrating arbitrary command execution on…
 surendrapuppala7/cve-2025-45955
Proof-of-concept exploit for CVE-2025-45955 demonstrating Server-Side Request Forgery (SSRF) in DonWeb Ferozo hosting platform, enabling internal…
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability
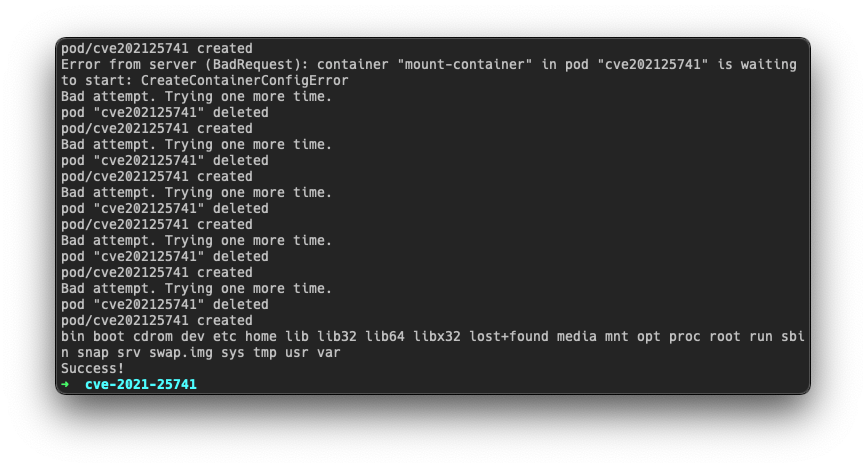 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 gteissier/cve-2017-10617
Proof-of-concept exploit for Juniper Contrail XXE vulnerability (CVE-2017-10617) with Docker-based lab environment demonstrating local file…
 0rx1/cve-2021-43858
Exploit for MinIO privilege escalation vulnerability CVE-2021-43858, allowing unauthorized access to cloud storage. Written in Go, run with 'go run…
 shadowbyte1/cve-2026-42154
Proof-of-concept exploit for CVE-2026-42154, a denial-of-service vulnerability in Prometheus Remote Read endpoint via crafted Snappy-compressed…
 china-china/minio_cve-2023-28432_exp
Exploit for MinIO information disclosure vulnerability CVE-2023-28432, allowing unauthorized access to sensitive environment variables.
 xenom0rph97/cve-2024-30896
Proof-of-concept exploit for CVE-2024-30896, a privilege escalation vulnerability in InfluxDB allowing allAccess token holders to gain operator-level…
 zpxlz/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…
 gobysec/cve-2023-28432
Exploit for CVE-2023-28432, a sensitive information disclosure vulnerability in MinIO's verify interface, allowing attackers to read system…
 zhangguanzhang/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626, a runc container escape vulnerability allowing host file system access via crafted working directory in…
 sh-ubh/cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105, a Kubernetes privilege escalation vulnerability allowing unauthorized command execution in pods via…
 shoucheng3/asf__nifi_cve-2023-34468_1-21-00
Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.