
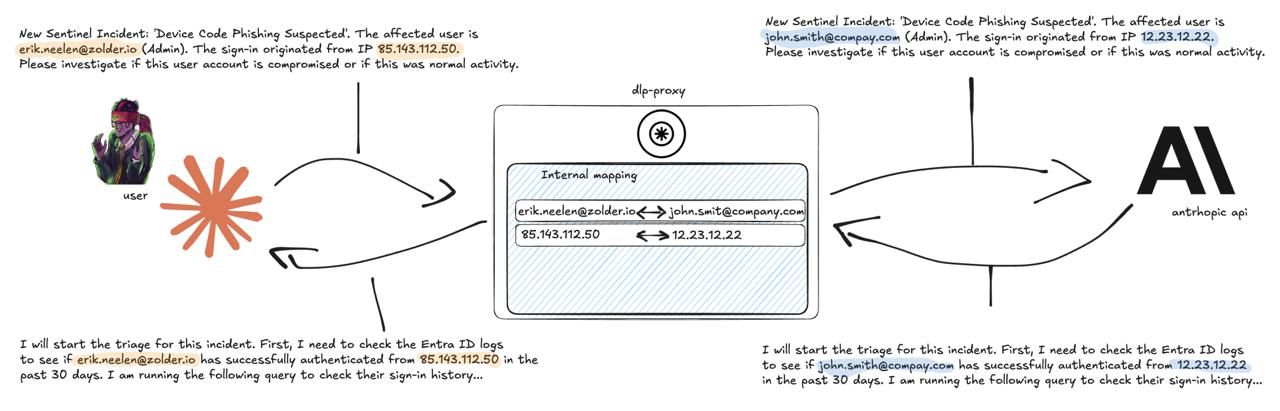
token-proxy
 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
ai-securityapi-securitycloud-security+6
28
zolderio/token-proxyA transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 knqyf263/cve-2020-10749
Proof-of-concept exploit for CVE-2020-10749 demonstrating Kubernetes MitM attacks via IPv6 rogue router advertisements between pods.
 george0papasotiriou/cve-2026-23007-serverless-cold-start-memory-remanence-data-leakage-
Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…

 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 bytedance/elkeid
Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
 cyberhades/hardening-k8s-containers
Hands-on lab demonstrating Kubernetes container hardening by comparing default vs. security-enhanced deployments of a vulnerable note-taking…
 george0papasotiriou/cve-2026-21002-serverless-cold-start-credential-leakage-via-reused-tmp
PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…
 tylermontneyacc/updatewindowsre-cve-2022-41099
Script to update Windows Recovery Environment to patch against CVE-2022-41099
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it