
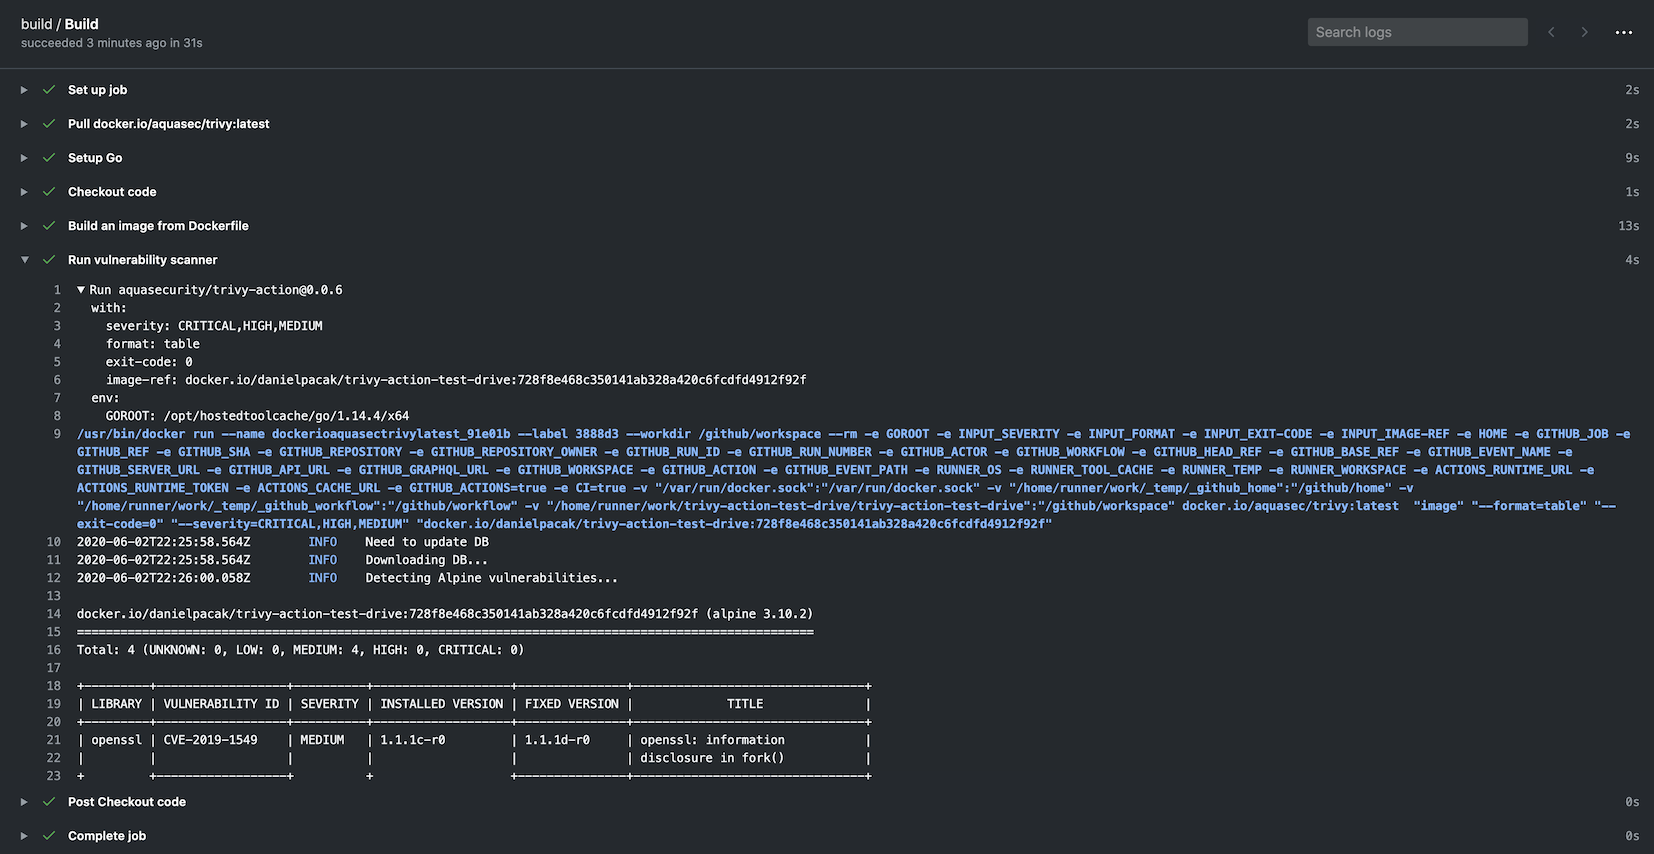
trivy-action
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
cloud-securitycode-analysiscontainer-security+5
1.5k
aquasecurity/trivy-actionRuns Trivy as GitHub action to scan your Docker container image for vulnerabilities
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 msaad00/agent-bom
Open-source cloud and AI security platform: scan code, dependencies, containers, cloud and AI agents/MCP into one security graph. Self-host free in…
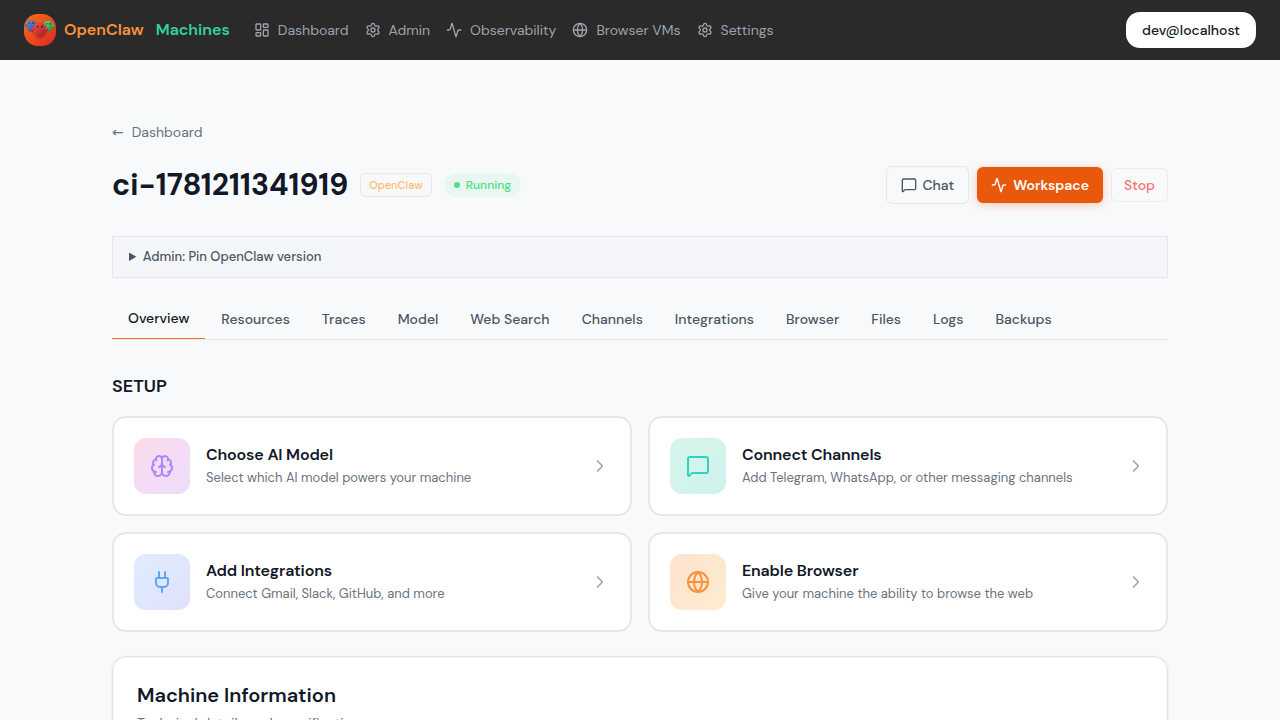 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 controlplaneio/simulator
Kubernetes Security Training Platform - focusing on security mitigation
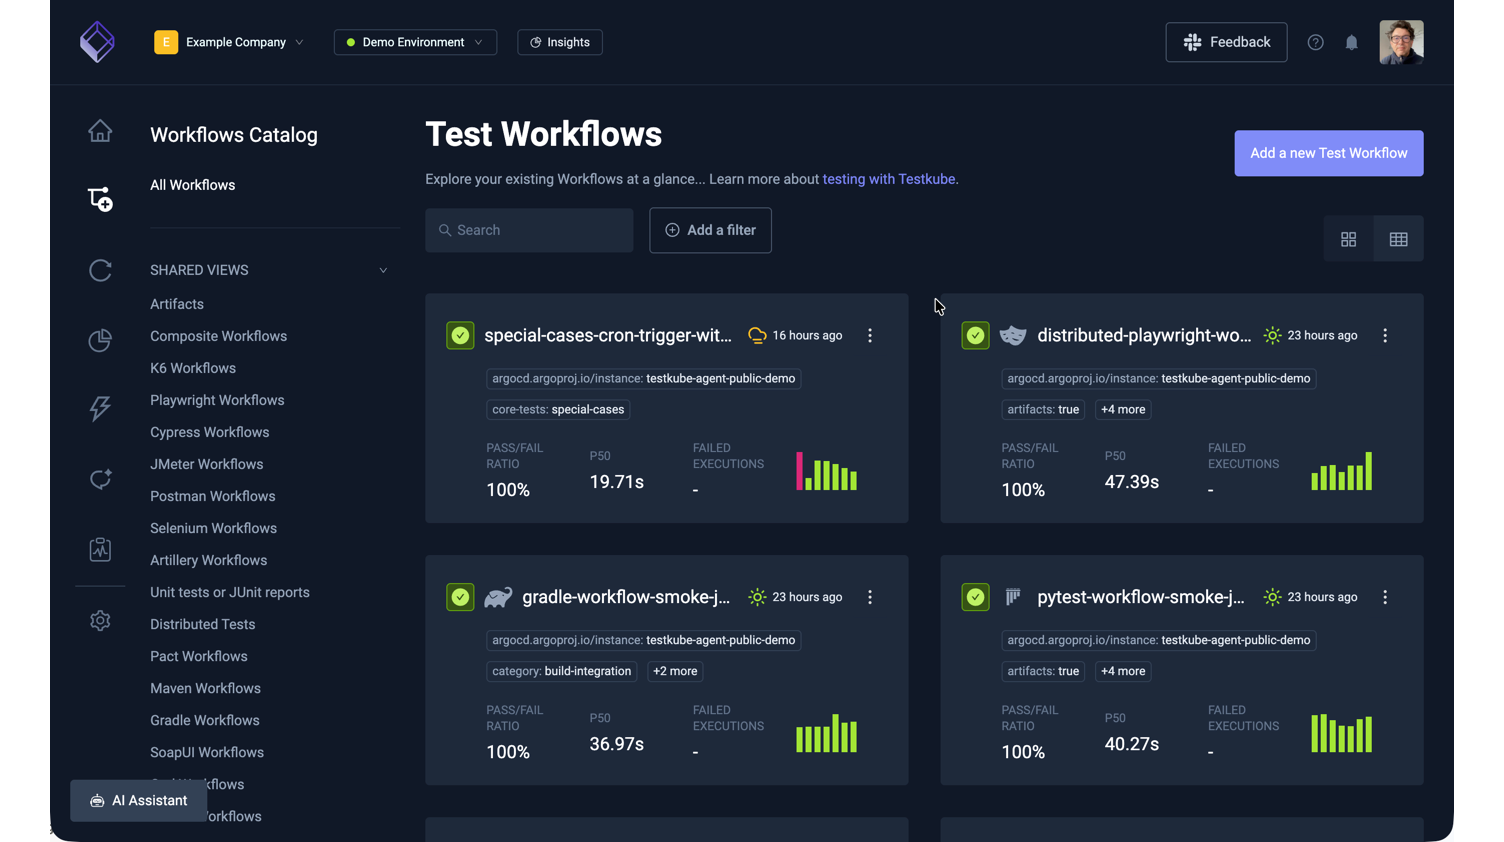 kubeshop/testkube
☸️ The Open Testing Platform for AI-Driven Engineering Teams
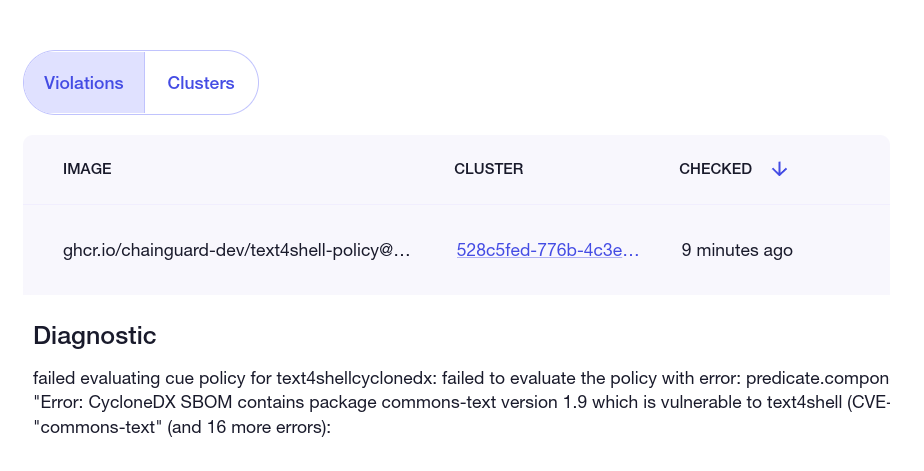 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.