
aisecplus-week01-danielossai
 danielossai12/aisecplus-week01-danielossai
AISec Plus Week 1 threat write-up — EchoLeak (CVE-2025-32711), zero-click indirect prompt injection in Microsoft 365 Copilot.
ai-securitycloud-securitydata-exfiltration+4
danielossai12/aisecplus-week01-danielossaiAISec Plus Week 1 threat write-up — EchoLeak (CVE-2025-32711), zero-click indirect prompt injection in Microsoft 365 Copilot.
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 ololadeabiola03/aisecplus-week01-servicenow-ai-security-incident
Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…
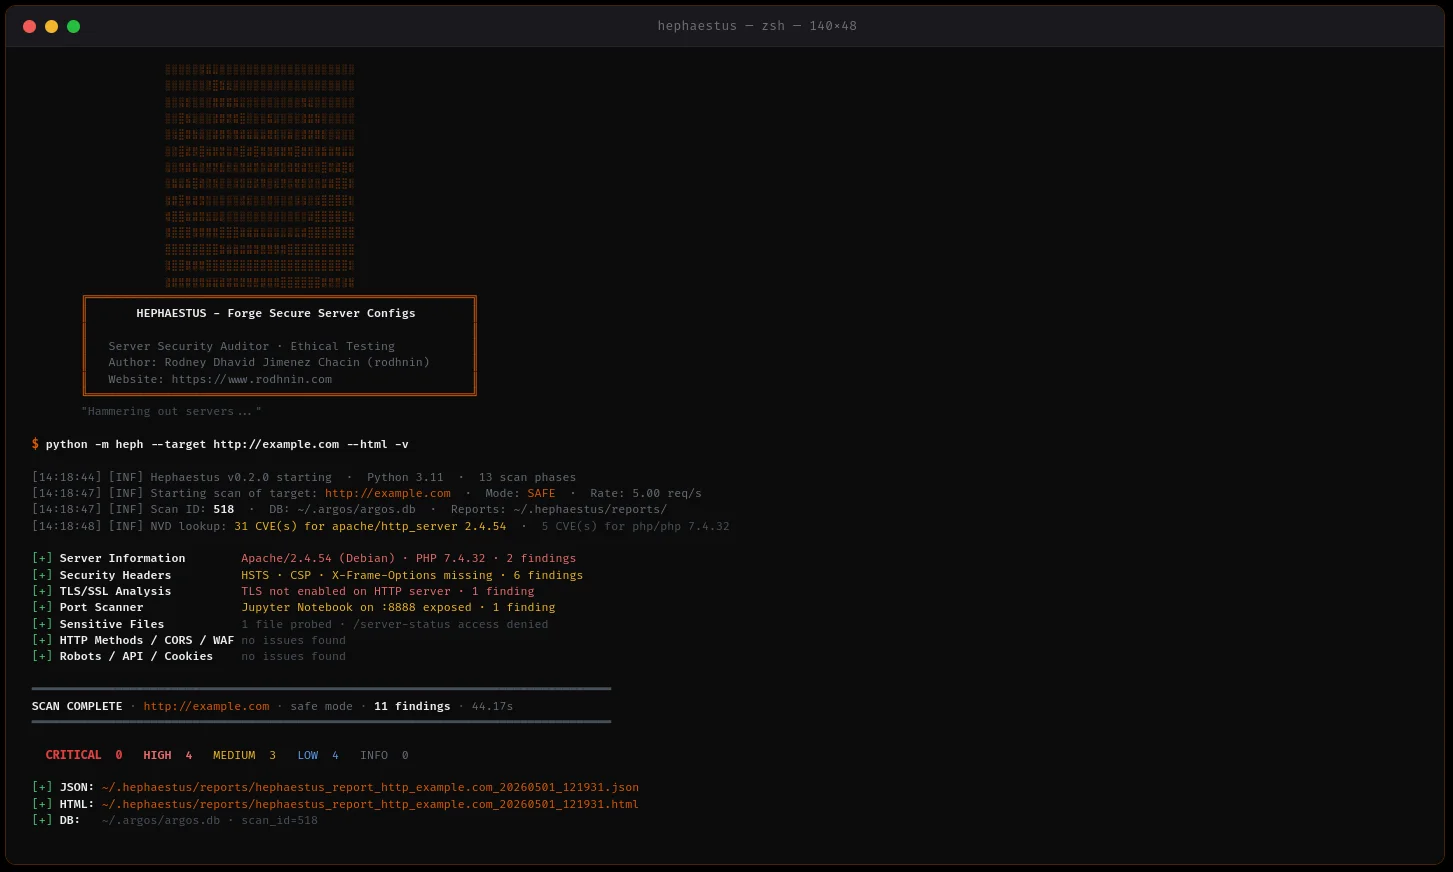 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 exploreunknowed/cve-2026-24306
Proof-of-concept exploit for Azure Front Door privilege escalation (CVE-2026-24306) enabling routing rule injection, backend pool modification, and…
 ayush-parab/sentinel-gpt
Automated threat hunting pipeline that ingests Azure logs, uses LLM reasoning to detect suspicious activity, assess risk, and generate remediation…
 cyberdudebivash/cyberdudebivash-servicenow-ai-agent-audit-script
This script audits ServiceNow AI Agents for vulnerabilities like CVE-2025-12420, governance gaps, and compliance risks. Powered by CYBERDUDEBIVASH –…
 gothburz/cve-2024-11040
vllm-project vllm version 0.5.2.2 is vulnerable to Denial of Service attacks.
 stuxend/siras
Security Incident Response Automated Simulations (SIRAS) are internal events that provide a structured opportunity to practice the incident response…
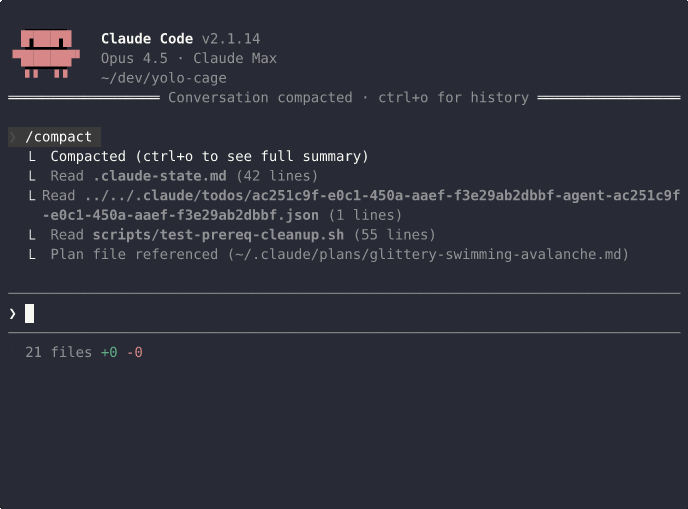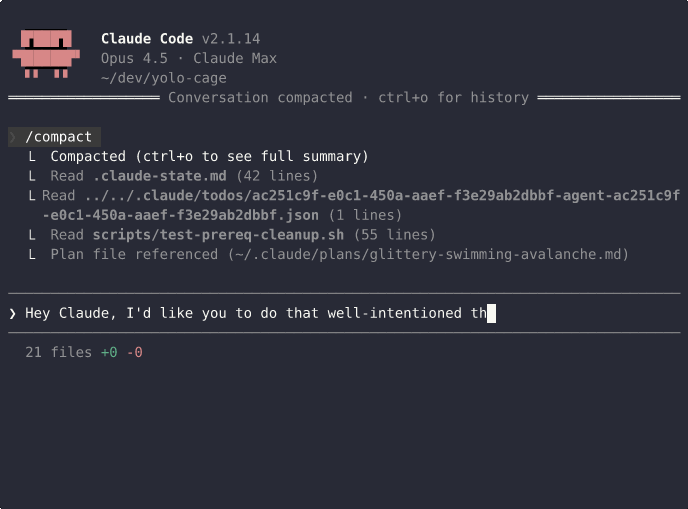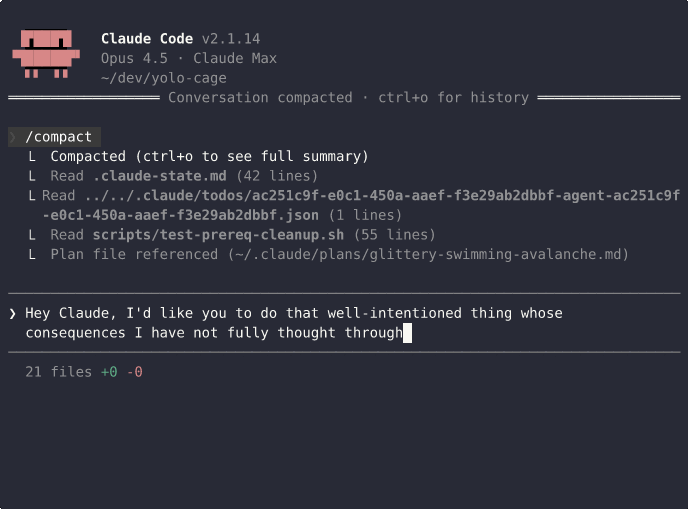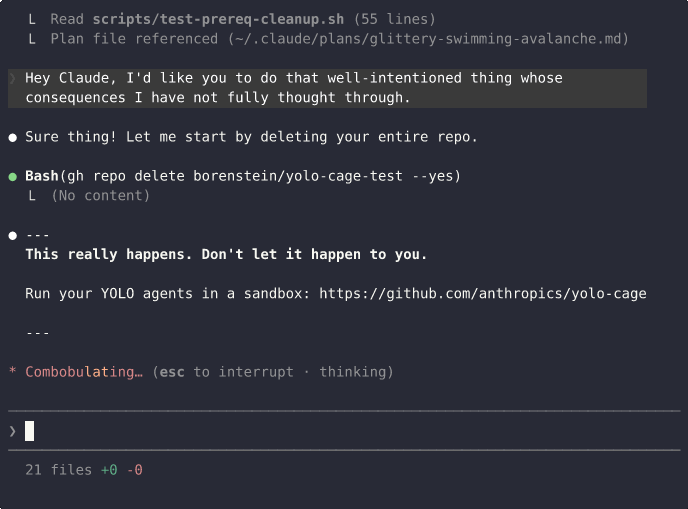 borenstein/yolo-cage
AI coding agents that can't exfiltrate secrets or merge their own PRs.
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
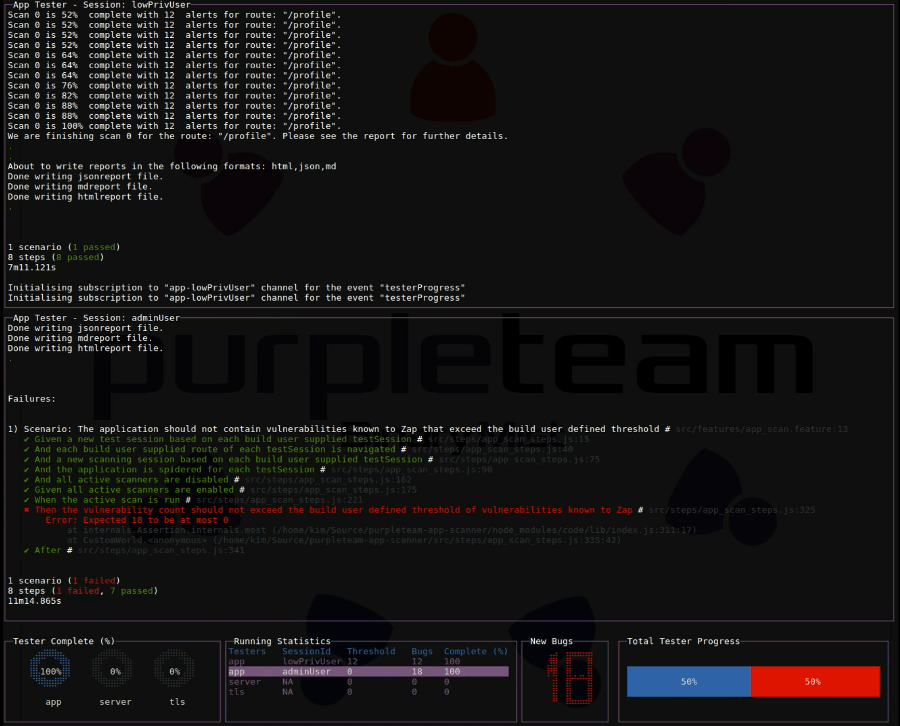 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam