
CVE-2022-0492-Docker-Breakout-Checker-and-PoC
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
cloud-securitycontainer-escapecontainer-security+6
t1erno/cve-2022-0492-docker-breakout-checker-and-pocDocker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 snailsploit/cve-2026-3288
Walkthrough: ingress-nginx Configuration Injection via rewrite-target Annotation
 heroku/heroku-cve-2013-0156
Inspect all of your heroku apps to see if they are running a vulnerable version of Rails
 twistlock/k8s-cve-2020-8554-mitigations
Prisma Cloud Compute Admission rules to mitigate Kubernetes CVE-2020-8554
 oscerd/cve-2026-40564
CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…
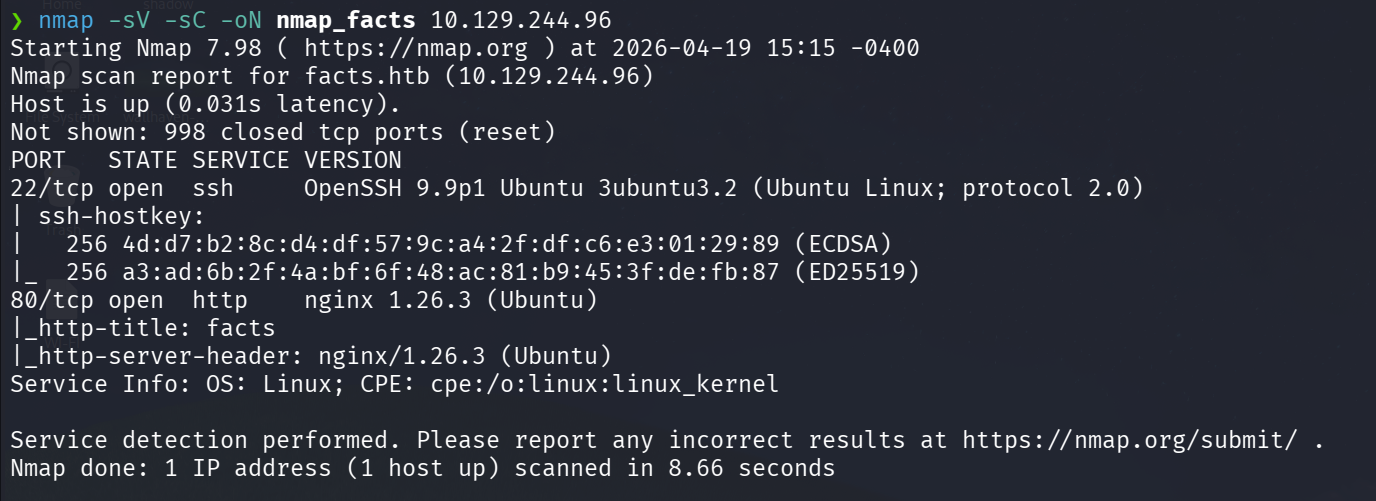 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 snailsploit/cve-2026-32794
CVE-2026-32794: TLS Certificate Verification Bypass in Apache Airflow Databricks Provider
 rrespxwnss/cve-2025-63571
Proof of concept demonstrating Server-Side Request Forgery in ChatGPT, allowing attackers to force the AI to make arbitrary HTTP requests, exposing…
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
 smaranchand/bucky
Bucky (An automatic S3 bucket discovery tool)
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 williavs/nextjs-security-update
Batch upgrade all your Next.js apps to patched versions - fight back against CVE-2025-55183/55184/67779
 rotemreiss/robusto
Robust Subdomain Takeover Tool
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
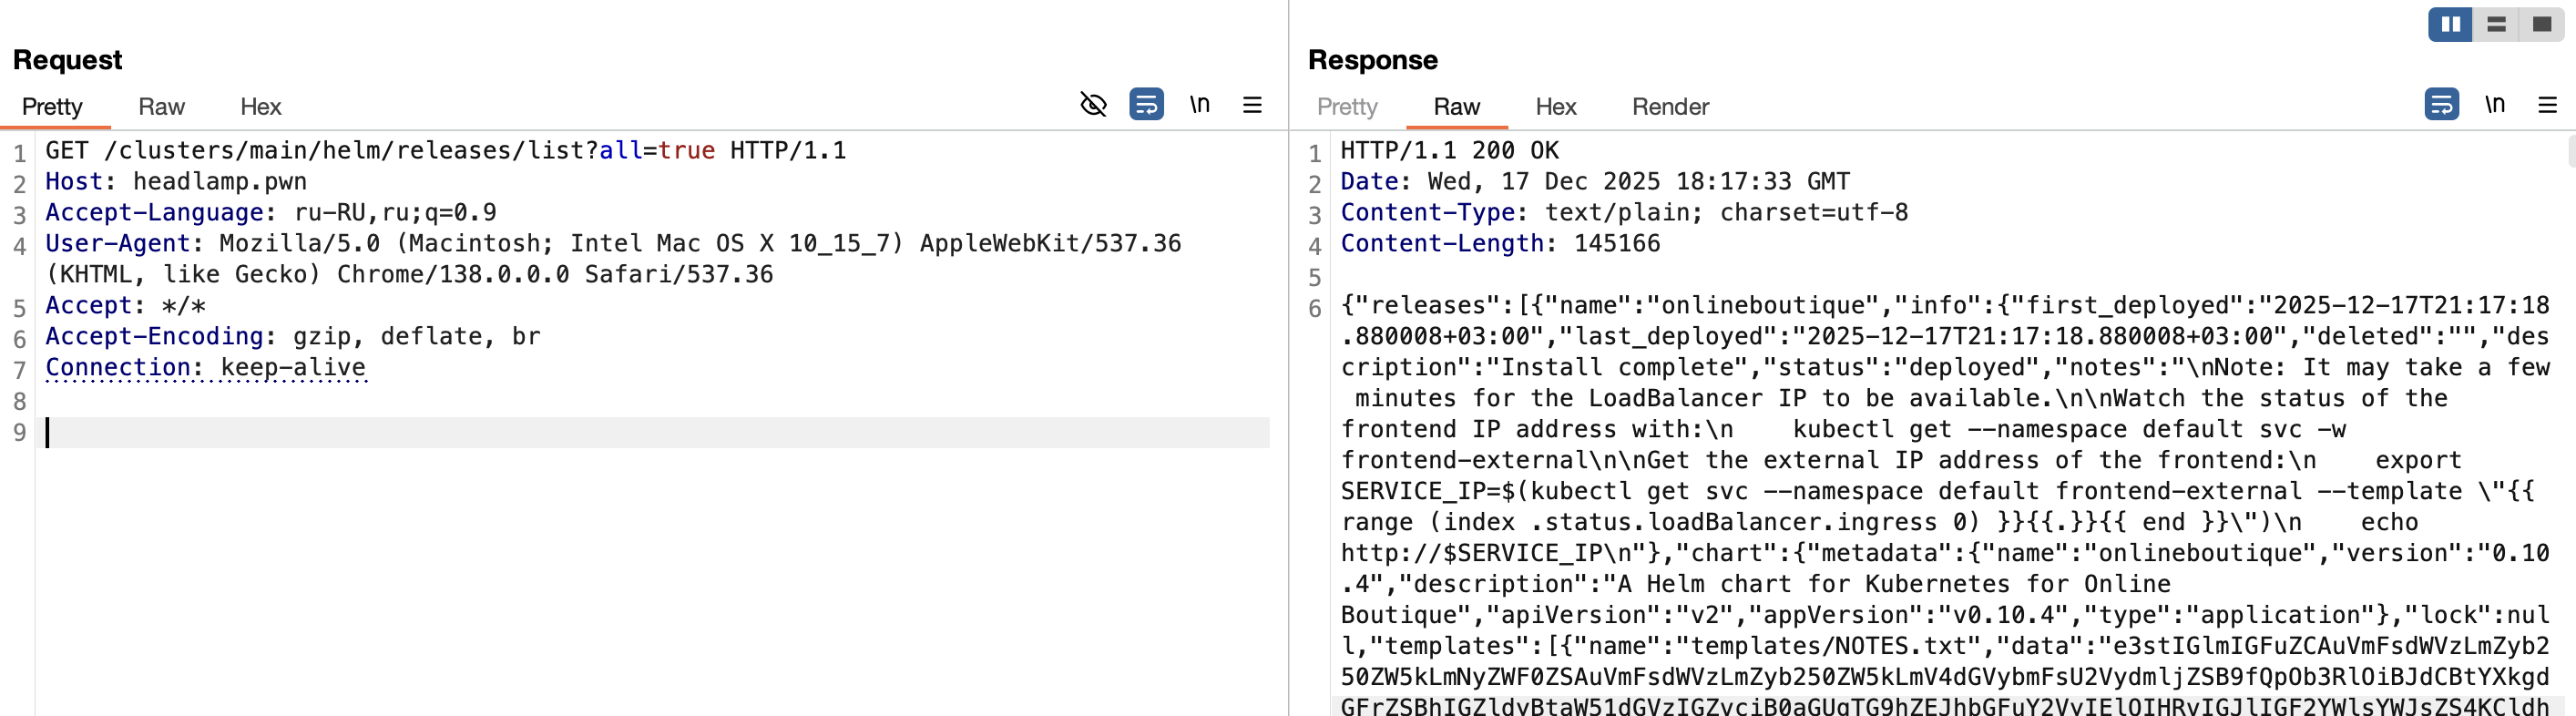 r0binak/cve-2025-14269
CVE-2025-14269 PoC exploit

 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam