
CVE-2019-1002101-Helpers
 brompwnie/cve-2019-1002101-helpers
PoC helper scripts and Dockerfile for CVE-2019-1002101
cloud-securitycontainer-securityexploitation+3
6
brompwnie/cve-2019-1002101-helpersPoC helper scripts and Dockerfile for CVE-2019-1002101
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 cgwalters/container-cve-2021-22555
Containerized reproducer for CVE-2021-22555 Linux privilege escalation, with seccomp mitigation profiles and deployment guidance for Kubernetes and…
 irsl/google-osconfig-privesc
Proof of concept about the privilege escalation flaw identified in Google's Osconfig
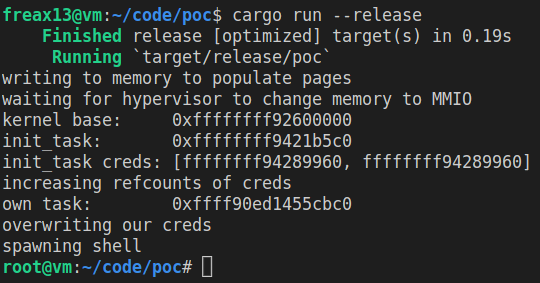 freax13/cve-2023-46813-poc
Proof-of-concept exploit for CVE-2023-46813 targeting AMD SEV-SNP. Escalates privileges by manipulating hypervisor memory type changes to swap task…
 r0binak/cve-2024-0132
CVE-2024-0132 – Fully Weaponized NVIDIA Container Toolkit Exploit
 douglasmun/pagecache-lpe-containment-kit
Educational, defensive kit for two Linux page-cache-corruption LPEs (DirtyClone CVE-2026-43503, pedit COW CVE-2026-46331): hardening, detection,…
 666asd/cve-2024-23653
Proof-of-concept demonstrating CVE-2024-23653, a BuildKit container escape via a malicious Dockerfile frontend, using buildctl to inspect process…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 olezhaku/react2shell-toolkit
Toolkit for CVE-2025-55182, also known as React2Shell.
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
 ssst0n3/kata-cve-2020-2023-poc
Proof-of-concept exploit for Kata Containers container escape (CVE-2020-2023) using mknod to modify guest filesystem and overwrite system binaries…
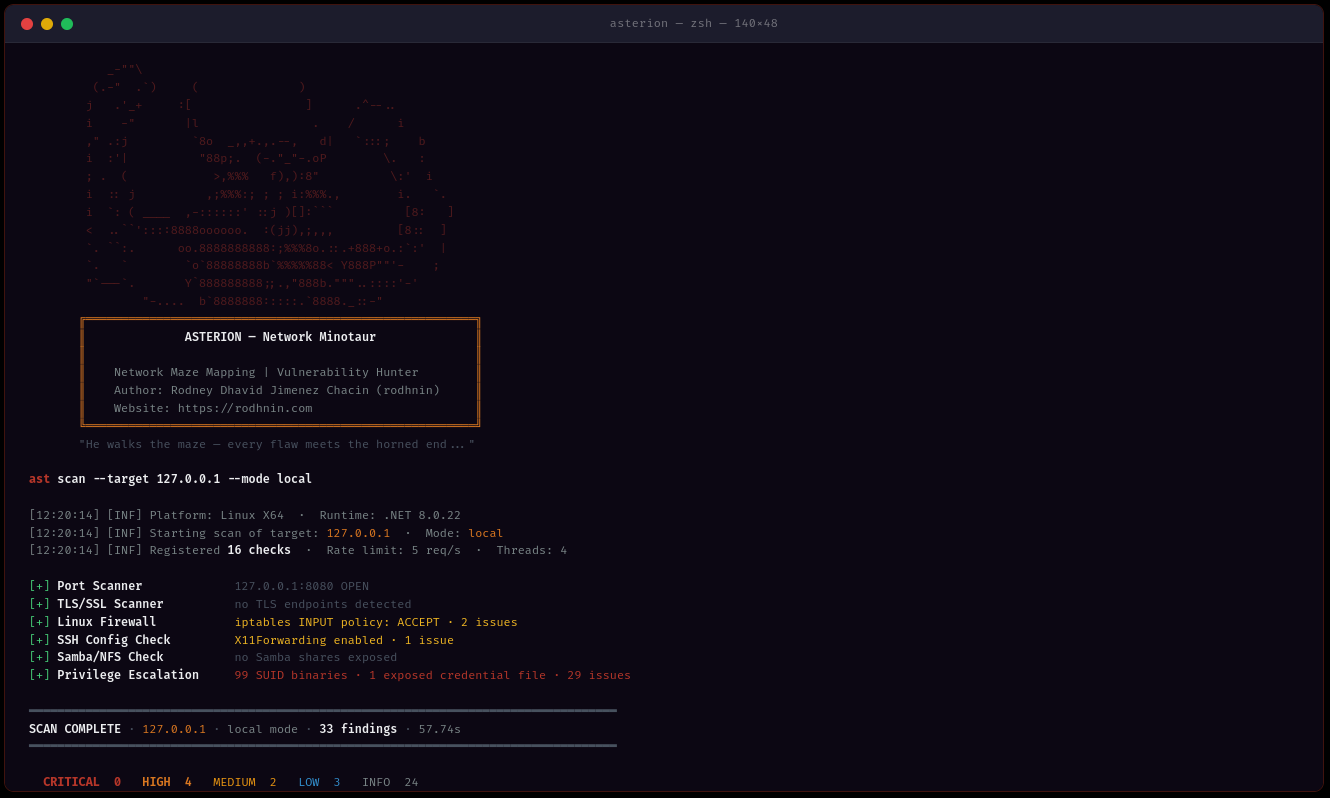 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 portbuster1337/cve-2026-20182
CVE-2026-20182 PoC - Cisco Catalyst SD-WAN Controller / Manager Authentication Bypass (CVSS 10.0)
 george0papasotiriou/cve-2026-21008-kubernetes-service-account-token-mounted-in-hostpath
Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…
 zhangguanzhang/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626, a runc container escape vulnerability allowing host file system access via crafted working directory in…
 george0papasotiriou/cve-2026-22015-serverless-function-environment-variable-injection-via-event
PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…