
heroku-CVE-2013-0269
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
cloud-securitydevsecopsmisconfiguration+2
2
heroku/heroku-cve-2013-0269Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…

 grabesec/xcp_ng_cve-2026-43284_tester
Tester for CVE-2026-43284
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
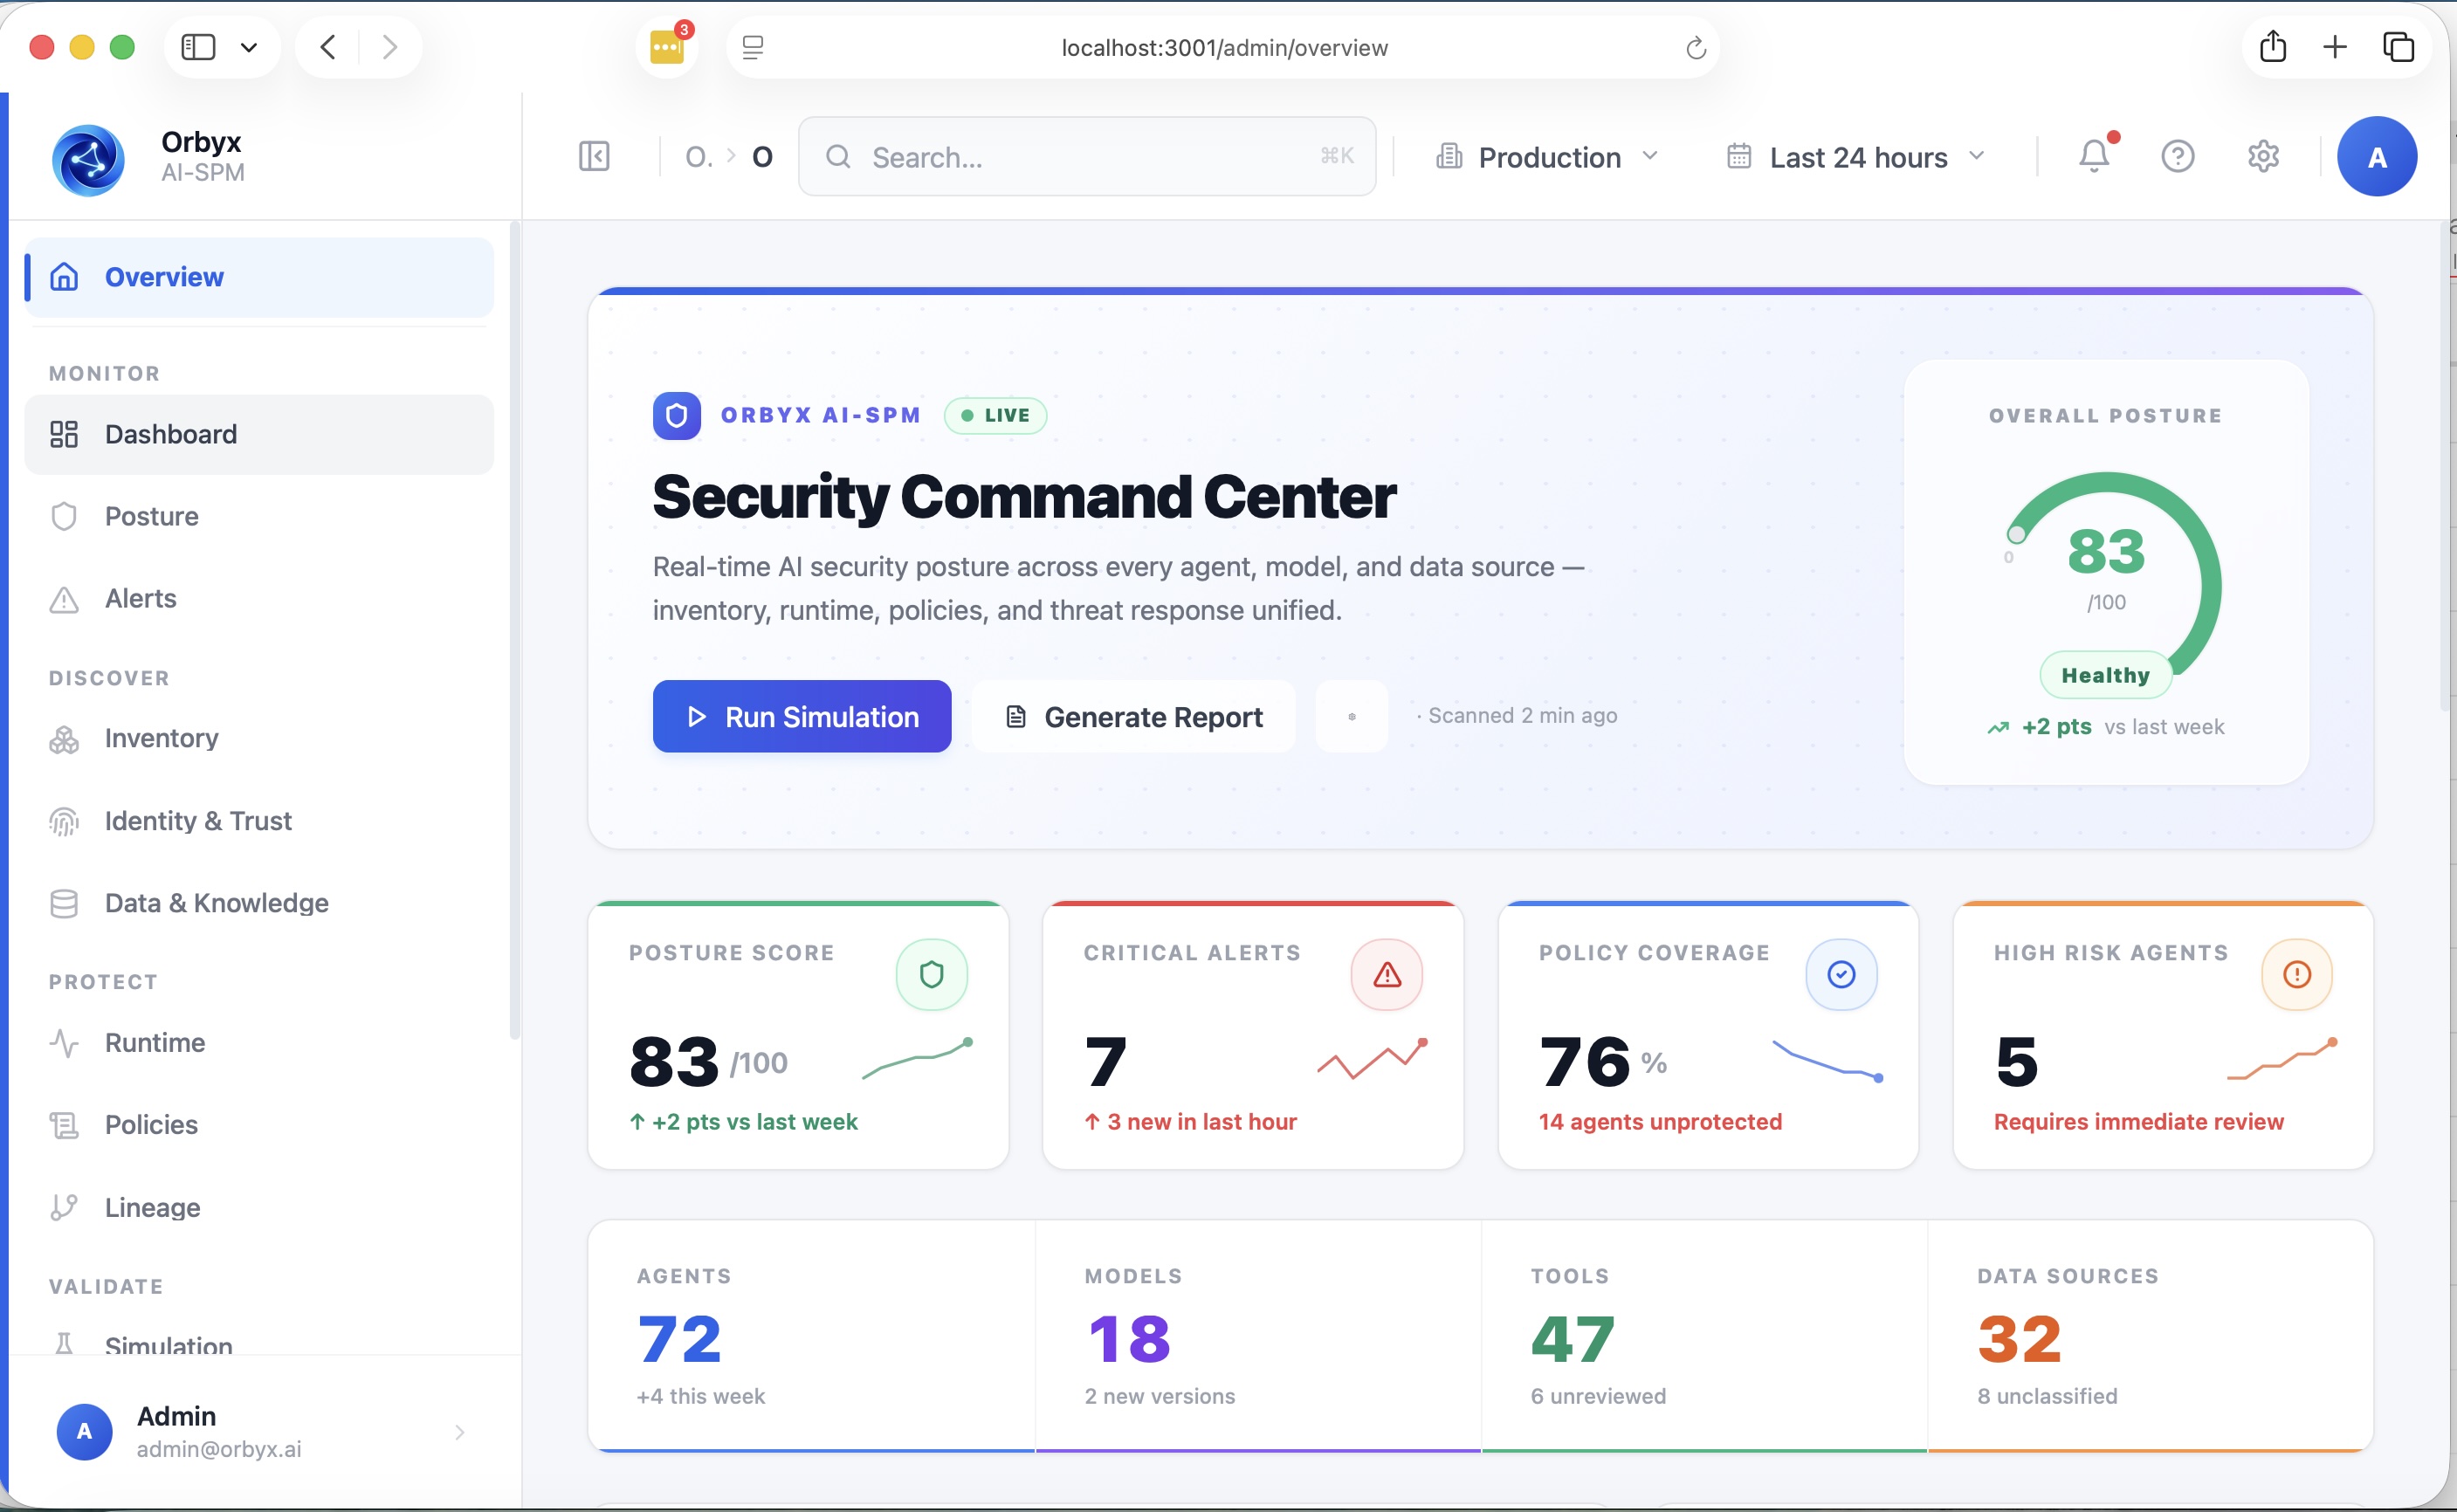 dshapi/ai-spm
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
 retrospected/purplekeep
Providing Azure pipelines to create an infrastructure and run Atomic tests.
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
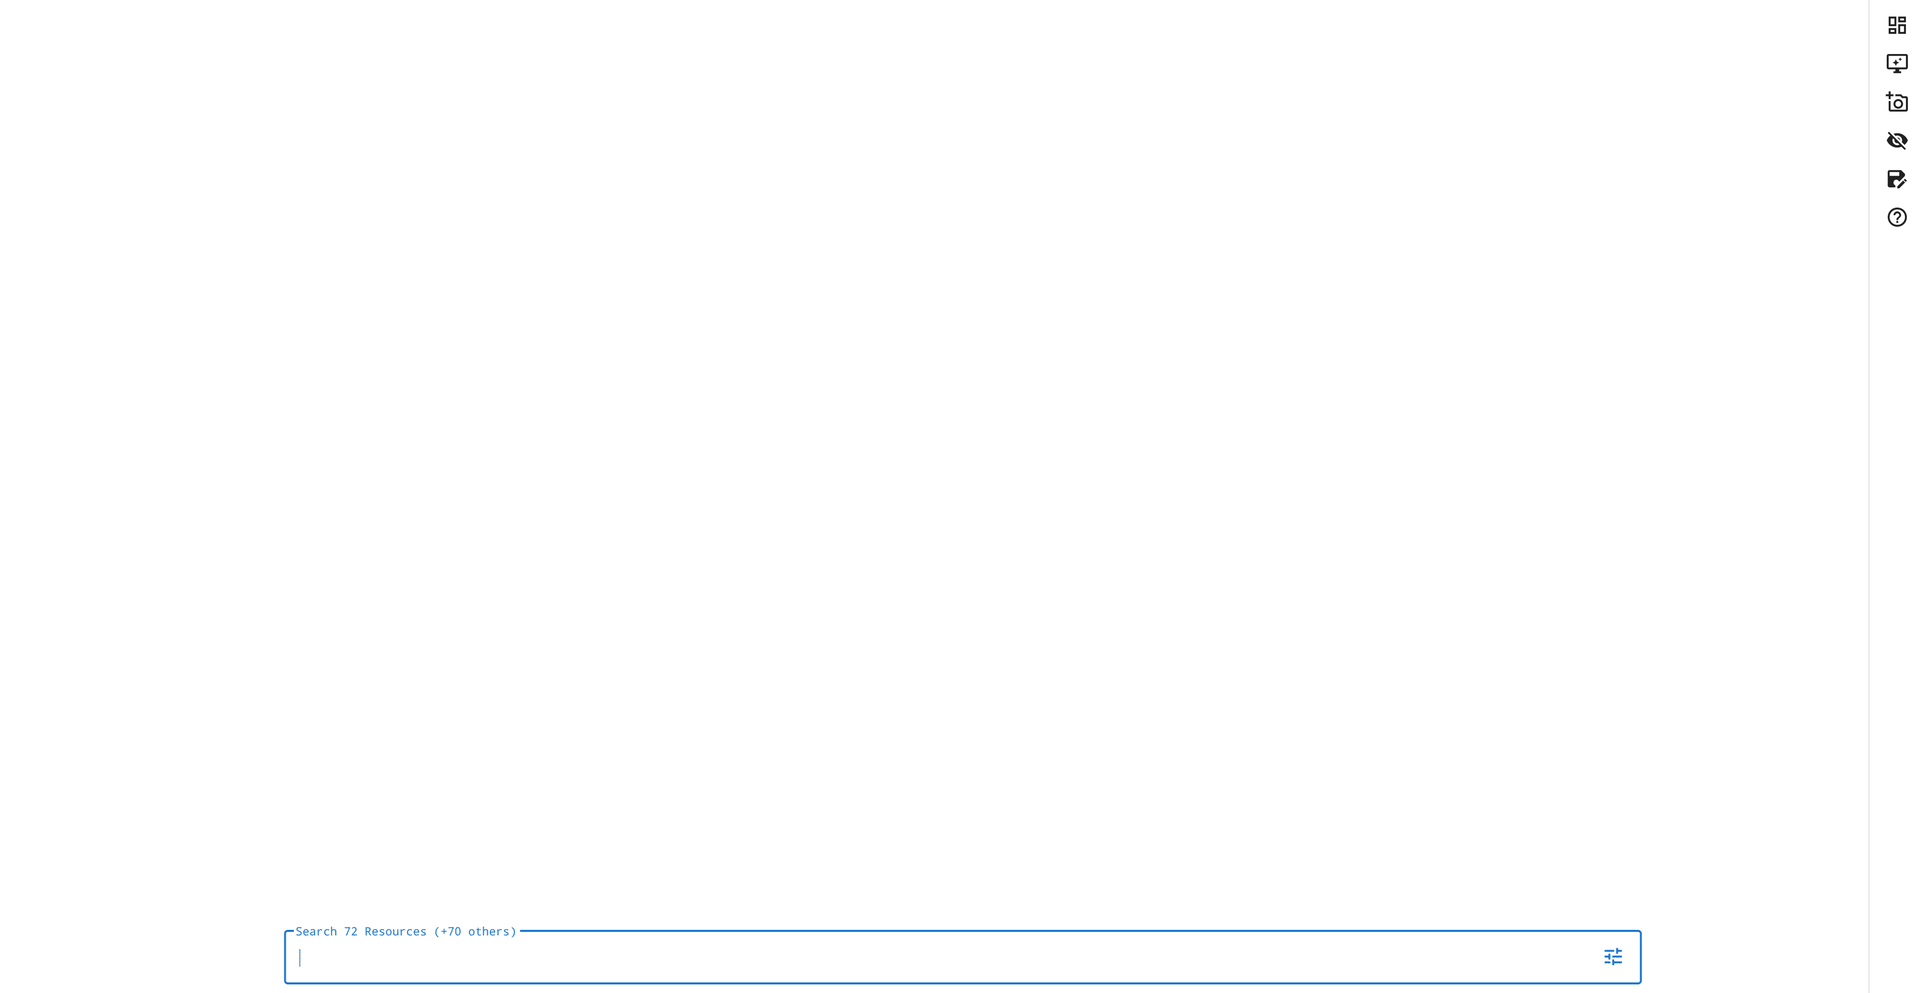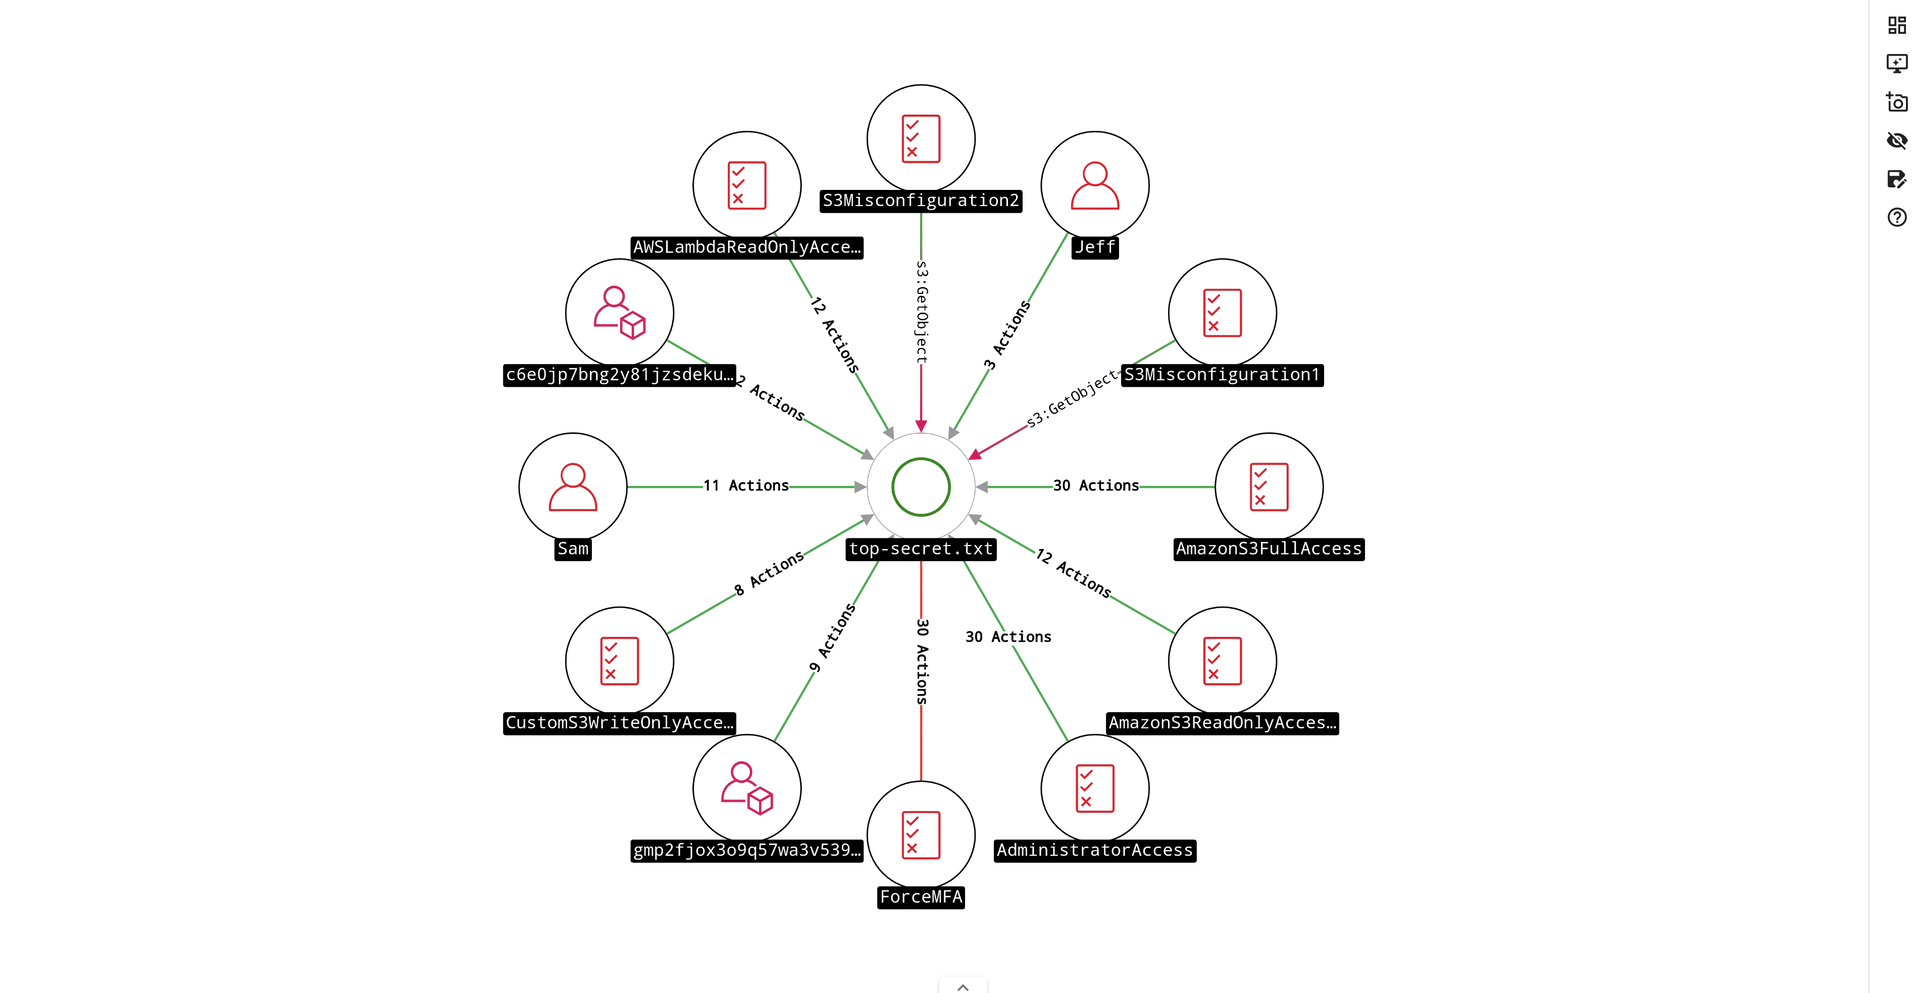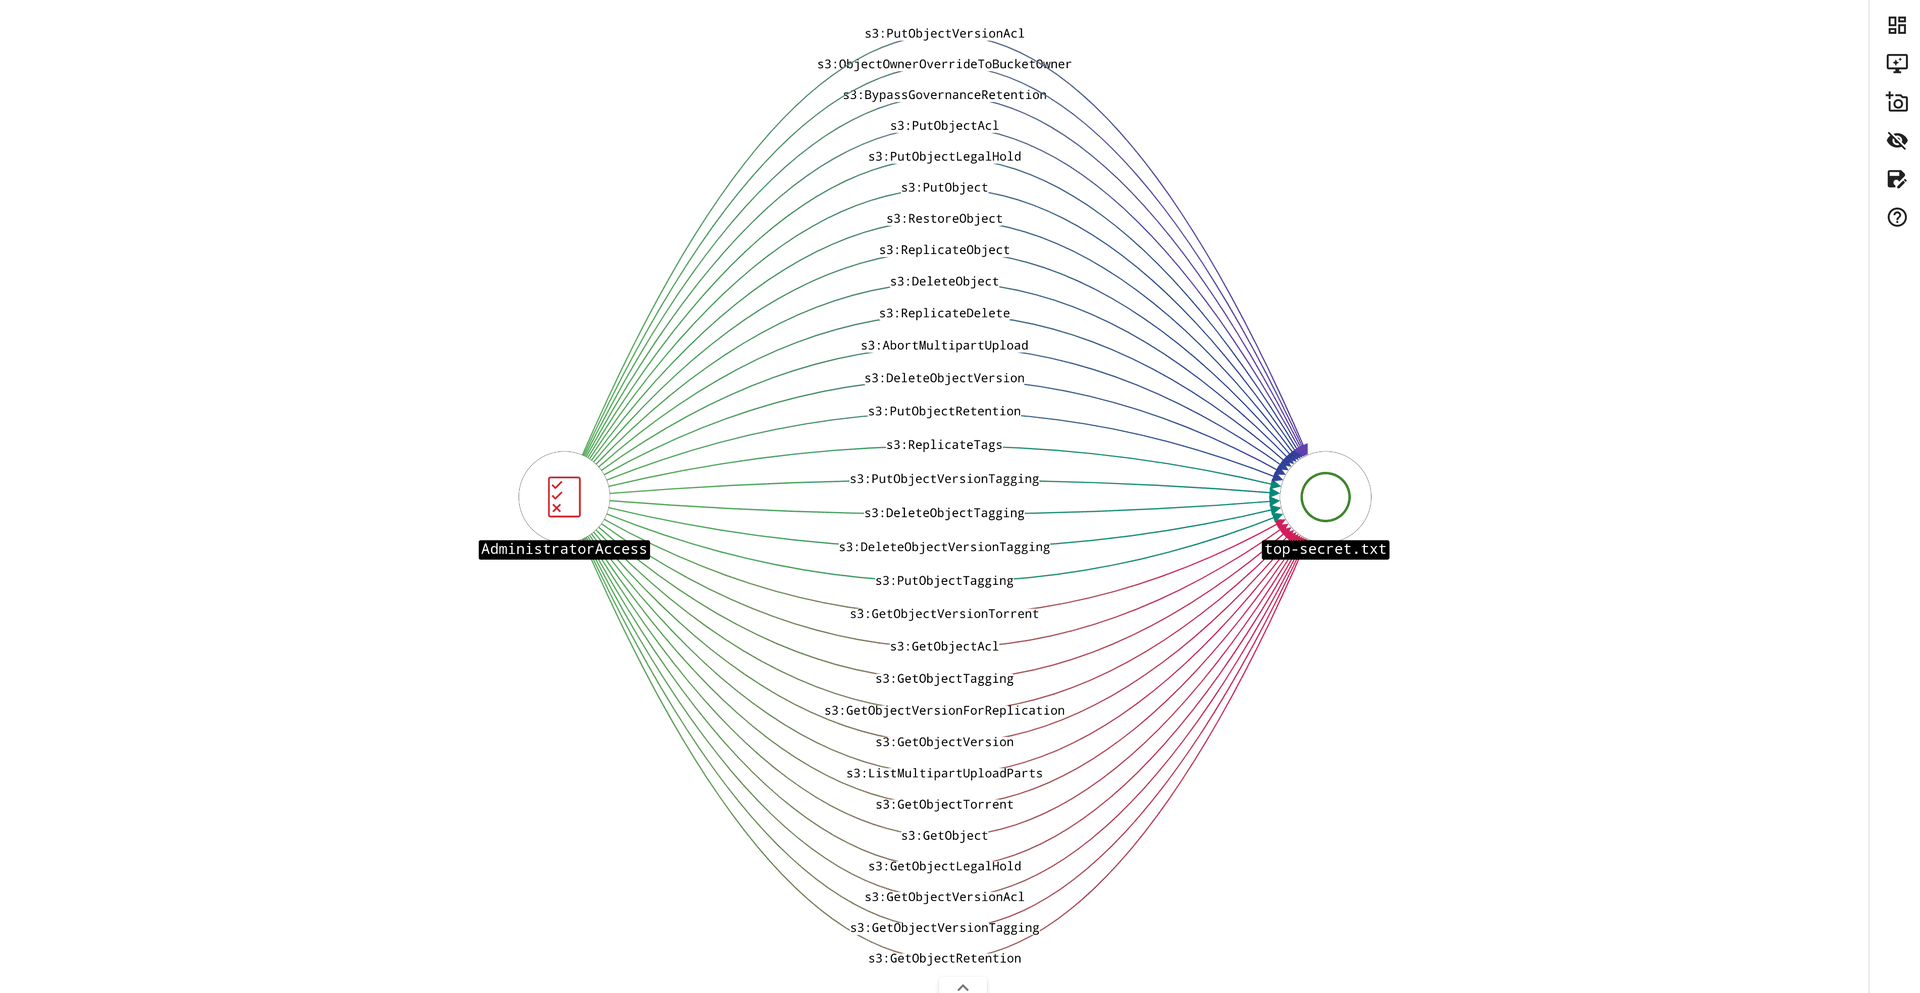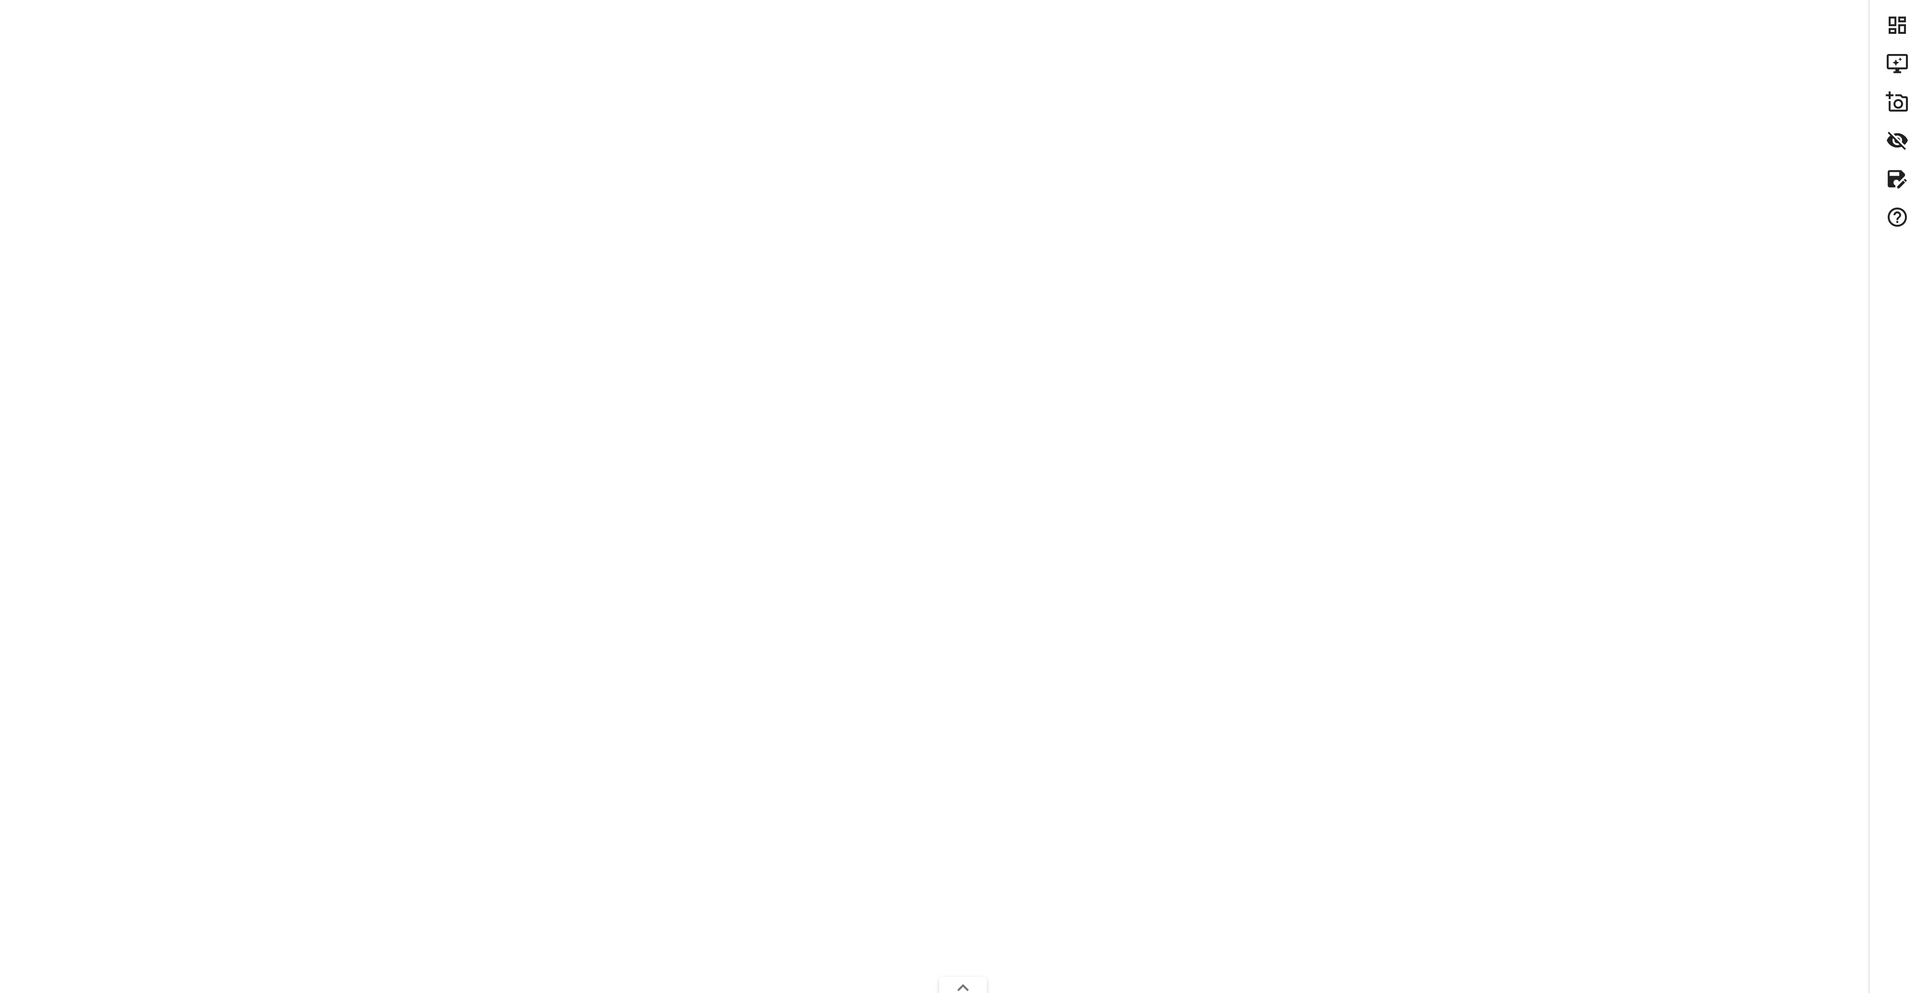 reverseclabs/awspx
A graph-based tool for visualizing effective access and resource relationships in AWS environments.
 assetnote/blind-ssrf-chains
An exhaustive list of all the possible ways you can chain your Blind SSRF vulnerability
 owasp/dvsa
a Damn Vulnerable Serverless Application
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 cyberhades/hardening-k8s-containers
Hands-on lab demonstrating Kubernetes container hardening by comparing default vs. security-enhanced deployments of a vulnerable note-taking…
 americanhanko/windows-security-cve-2017-8543
InSpec profile to verify a node is patched and compliant for CVE-2017-8543
 didoatanasov/cve-2021-44228
Ansible playbook that applies a global JVM environment variable to mitigate the Log4j CVE-2021-44228 remote code execution vulnerability across all…
 jenkinsci-cert/security-3314-3315
Workaround for disabling the CLI to mitigate SECURITY-3314/CVE-2024-23897 and SECURITY-3315/CVE-2024-23898