
cve-2021-43858
 0rx1/cve-2021-43858
Exploit for MinIO privilege escalation vulnerability CVE-2021-43858, allowing unauthorized access to cloud storage. Written in Go, run with 'go run…
cloud-securityexploitationpenetration-testing+2
3
0rx1/cve-2021-43858Exploit for MinIO privilege escalation vulnerability CVE-2021-43858, allowing unauthorized access to cloud storage. Written in Go, run with 'go run…
 olezhaku/react2shell-toolkit
Toolkit for CVE-2025-55182, also known as React2Shell.
 biitts/cve-2026-54917-seaweedfs-cross-bucket-traversal
PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…
 oscerd/cve-2026-46456
Reproducer for CVE-2026-46456 — Apache Camel camel-aws2-sqs inbound message-attribute header injection (Camel control-header injection via…
 biutrap/cve-2026-64849
Proof-of-concept exploit for CVE-2026-64849: triggers SSRF in MLflow webhook API via crafted POST, fetching cloud instance metadata from…
 gagaltotal/cve-2026-82329-poc
PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…
 kovachvl/cve-2026-54356
Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 maxwitat/check-aad-connect-for-cve-2021-36949-vulnerability
check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
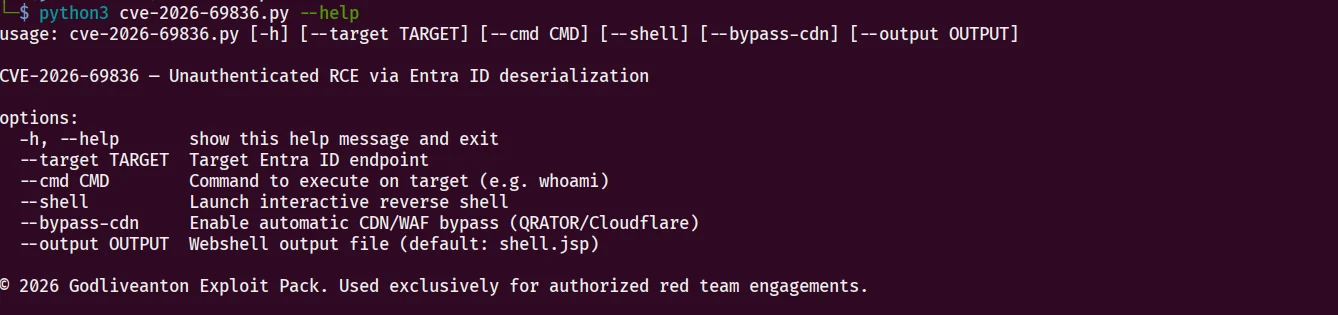 sentinel-aidefense/cve-2026-69836-exp
CVE-2026-69836 — Unauthenticated RCE via Entra ID deserialization
 syedhafiz1234/cve-2023-34039
CVE-2023-34039
 blackm4c/cve-2021-41805
HashiCorp Consul exploit with python. (CVE-2021-41805)
 tocong282/cve-2026-44578-poc
Proof-of-concept exploit for CVE-2026-44578, a Server-Side Request Forgery in Next.js WebSocket upgrade handler. Includes detection mode and…
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 grabesec/xcp_ng_cve-2026-31431_tester
Non-destructive detector for CVE-2026-31431 (Copy Fail) local privilege escalation in XCP-ng 8.3 Dom0, validating kernel vulnerability via page-cache…