CVE-2025-29810-check

Para verificar si tu entorno podría ser vulnerable al CVE-2025-29810, necesitamos hacer algunas comprobaciones básicas, como: Versión del sistema…

Para verificar si tu entorno podría ser vulnerable al CVE-2025-29810, necesitamos hacer algunas comprobaciones básicas, como: Versión del sistema…

Playbook update APT package because CVE-2019-3462

Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.

A script to change OpenSSL versions on Ubuntu to 1.1.1q to protect against CVE-2022-2097.

Kubernetes DaemonSet that hot-patches JVMs to mitigate Log4j2 vulnerabilities (CVE-2021-44228, CVE-2021-45046) by disabling JNDI lookups, providing…


eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…

Stage two containers

OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass

Mitigates CVE-2016-5195 aka DirtyCOW

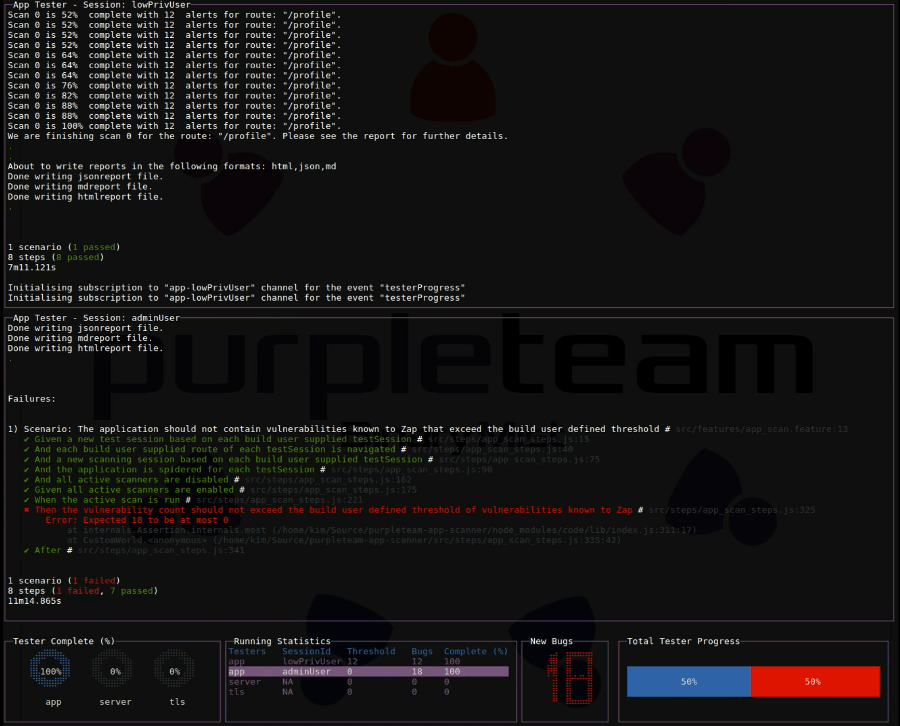
Server scanning component of purpleteam

Enumerate valid users within Microsoft Teams and OneDrive with clean output.

VirusTotal Wanna Be - Now with 100% more Hipster

AWS Serverless Security

CLI component of purpleteam

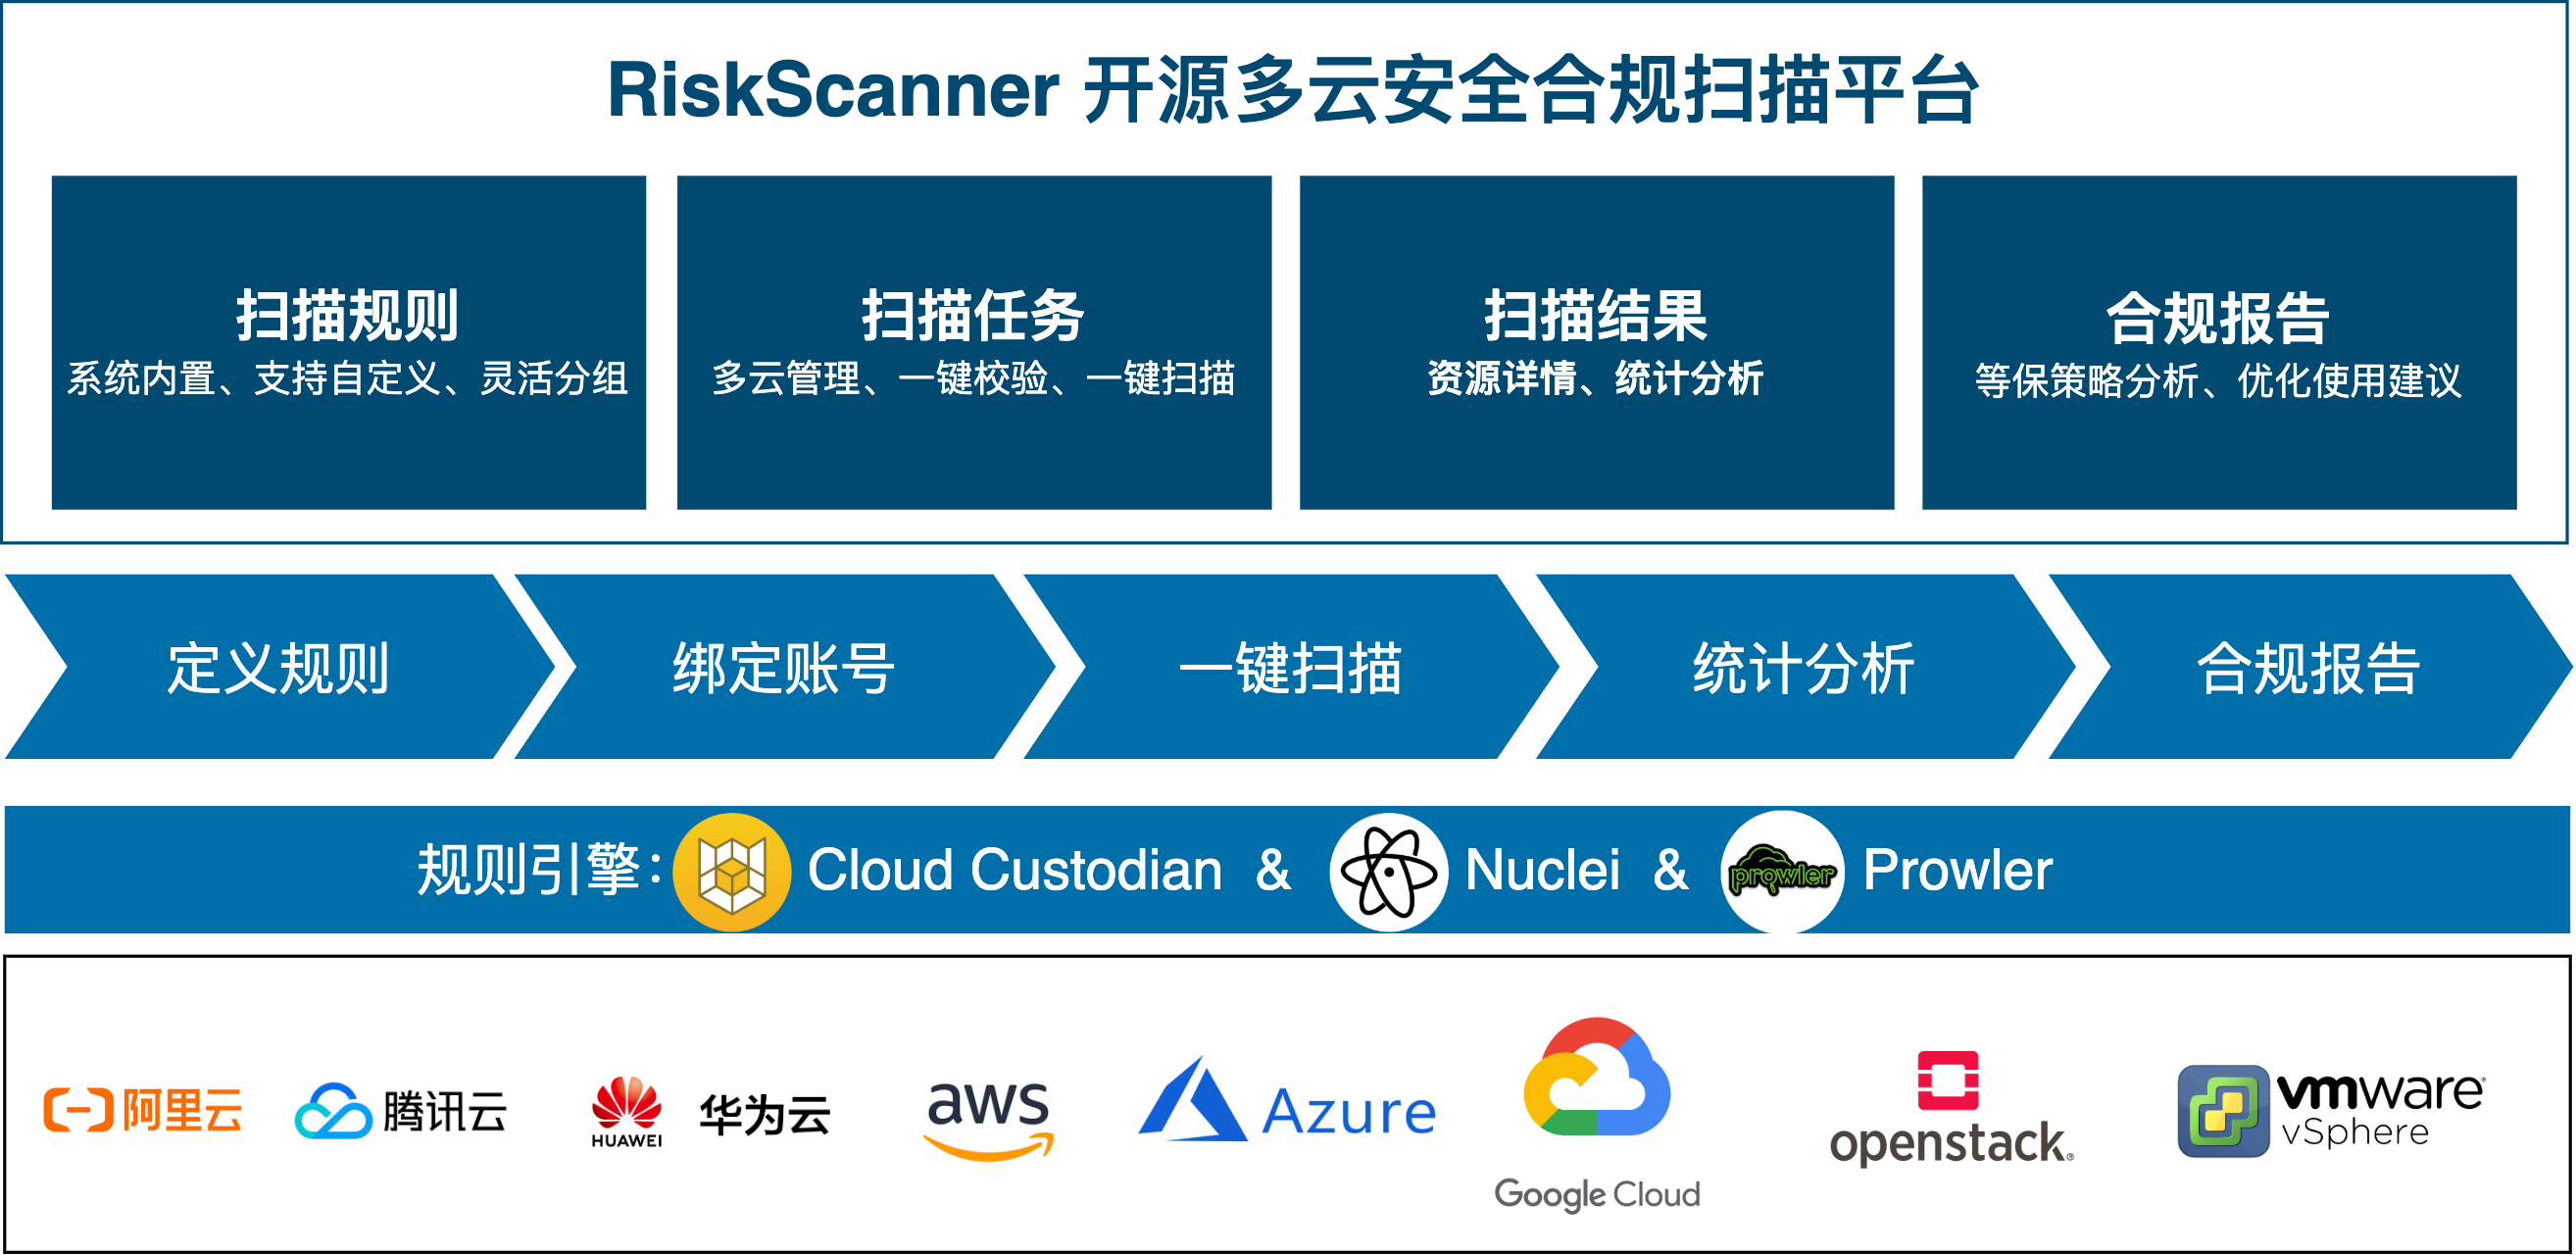
RiskScanner 是开源的多云安全合规扫描平台,基于 Cloud Custodian 和 Nuclei 引擎,实现对主流公(私)有云资源的安全合规扫描和漏洞扫描。

kube-scan: Octarine k8s cluster risk assessment tool

TLS checking component of purpleteam