

CVE-2025-63571
 rrespxwnss/cve-2025-63571
Proof of concept demonstrating Server-Side Request Forgery in ChatGPT, allowing attackers to force the AI to make arbitrary HTTP requests, exposing…
cloud-securityexploitationinformation-gathering+3
rrespxwnss/cve-2025-63571Proof of concept demonstrating Server-Side Request Forgery in ChatGPT, allowing attackers to force the AI to make arbitrary HTTP requests, exposing…
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 arbaaz29/cve-2022-3294
Privilege Escalation using nodes/proxy (create action allowed) and nodes/status (update/patch actions allowed)
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
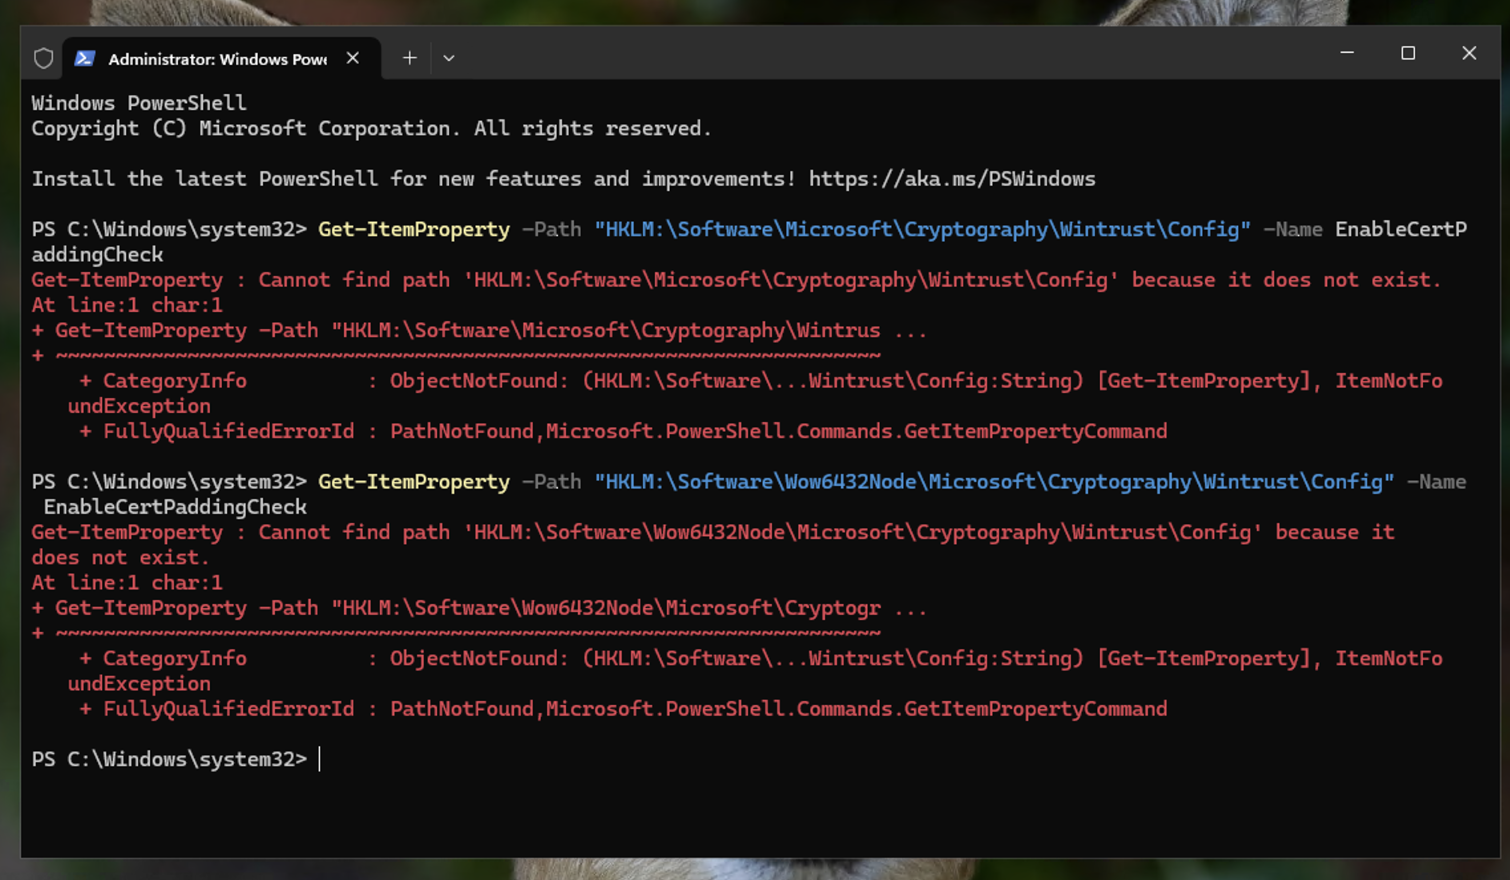 ksgassama-lab/vulnerability-remediation-cve-2013-3900
End-to-end remediation of CVE-2013-3900 using PowerShell and Tenable. Demonstrates vulnerability identification, registry hardening, and automated…
 eyodav/cve-2025-34159
A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…
 desaivinayak449/bug-bounty-reports-desai-vinayak
Bug bounty and vulnerability research reports by Desai Vinayak — includes CVE-2023-50290 (Apache Solr) and Zscaler subdomain takeover findings.
 x0da6h/poc-for-cve-2025-9074
一个容器逃逸漏洞POC
 mrk336/cve-2024-10220-kubernetes-gitrepo-volume-vulnerability
CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…
 xrayzen/cve-2025-9074-poc
2025年8月20日に公開されたDockerDesktopの脆弱性(対策済み)を実証する
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 patrickpichler/grafana-cve-2024-9264
Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
 jackdpeterson/imagick_secure_puppet
Puppet module to harden ImageMagick policy.xml against CVE-2016-3714 by restricting dangerous image processing directives.
 nickanderson/cfengine-cve-2016-2118
An example detection and remediation policy.
 istenrot/centos-dirty-cow-ansible
Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.
 thelsa/harbor-give-me-admin
harbor(<1.7.6/1.8.3) privilege escalation (CVE-2019-16097)
 im007/cve-2023-23397
PowerShell script to detect and remediate CVE-2023-23397 privilege escalation vulnerability in Microsoft Outlook and Exchange environments.
 randomrobbiebf/bucket-brute
Aws S3 Tko Tool