POC-CVE-2026-42826-2026-42826-Microsoft-Azure-DevOps-Information-Disclosure-Vulnerability

Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…

Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…


Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…

CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)

Proof-of-concept demonstrating an authorization bypass in Traefik's Kubernetes Gateway provider (CVE-2026-54761) via a crossProviderNamespaces…

Walkthrough: ingress-nginx Configuration Injection via rewrite-target Annotation

Automated detection of vulnerable domain configurations and subdomain takeover risks across cloud environments, with continuous monitoring and…

Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…

check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949

CVE-2026-55726: Publicly Listable Azure Blob Storage Container (device logs) - Gardyn (ICSA-26-183-03)

Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533

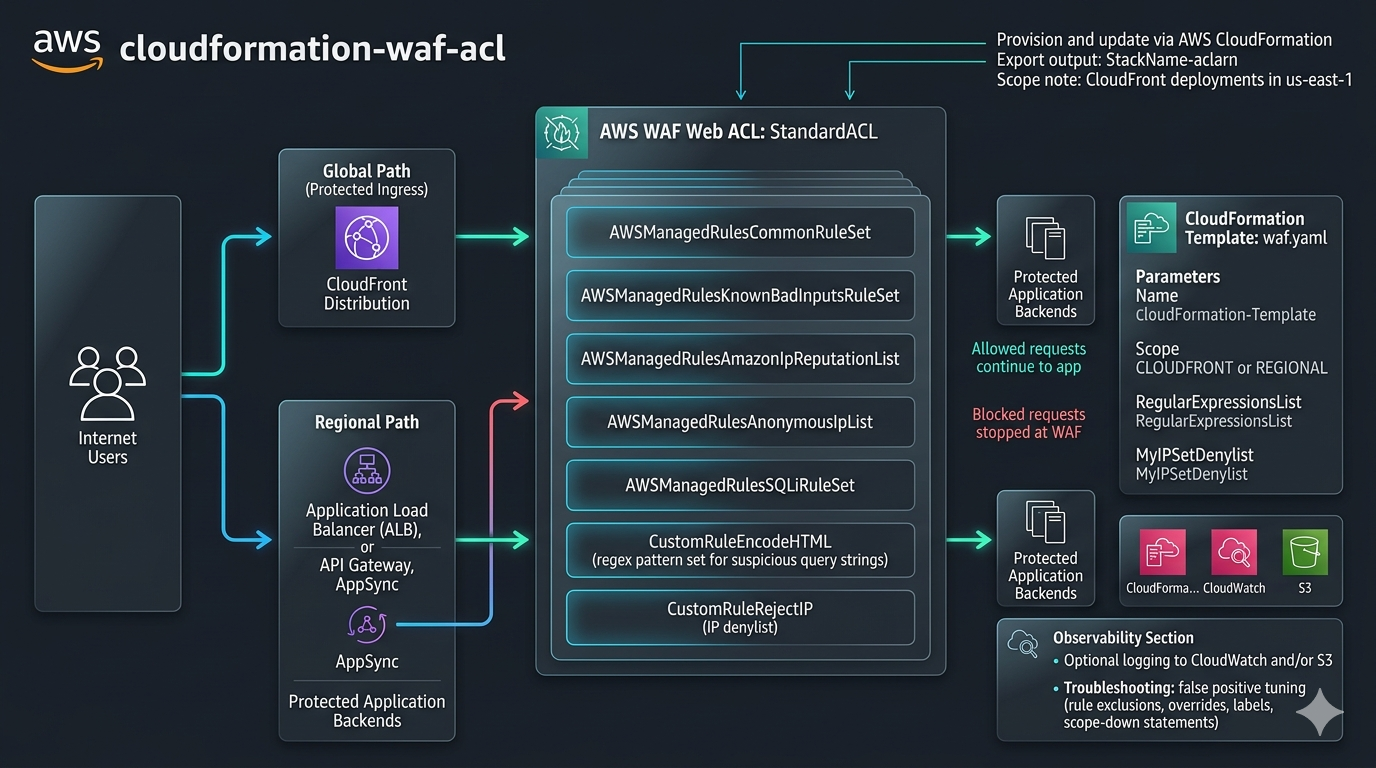
An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern…

Terraform module to manage AWS Security Groups. Currently, the ingress and egress rules support IPv4, IPv6, and Security Group ID inputs.

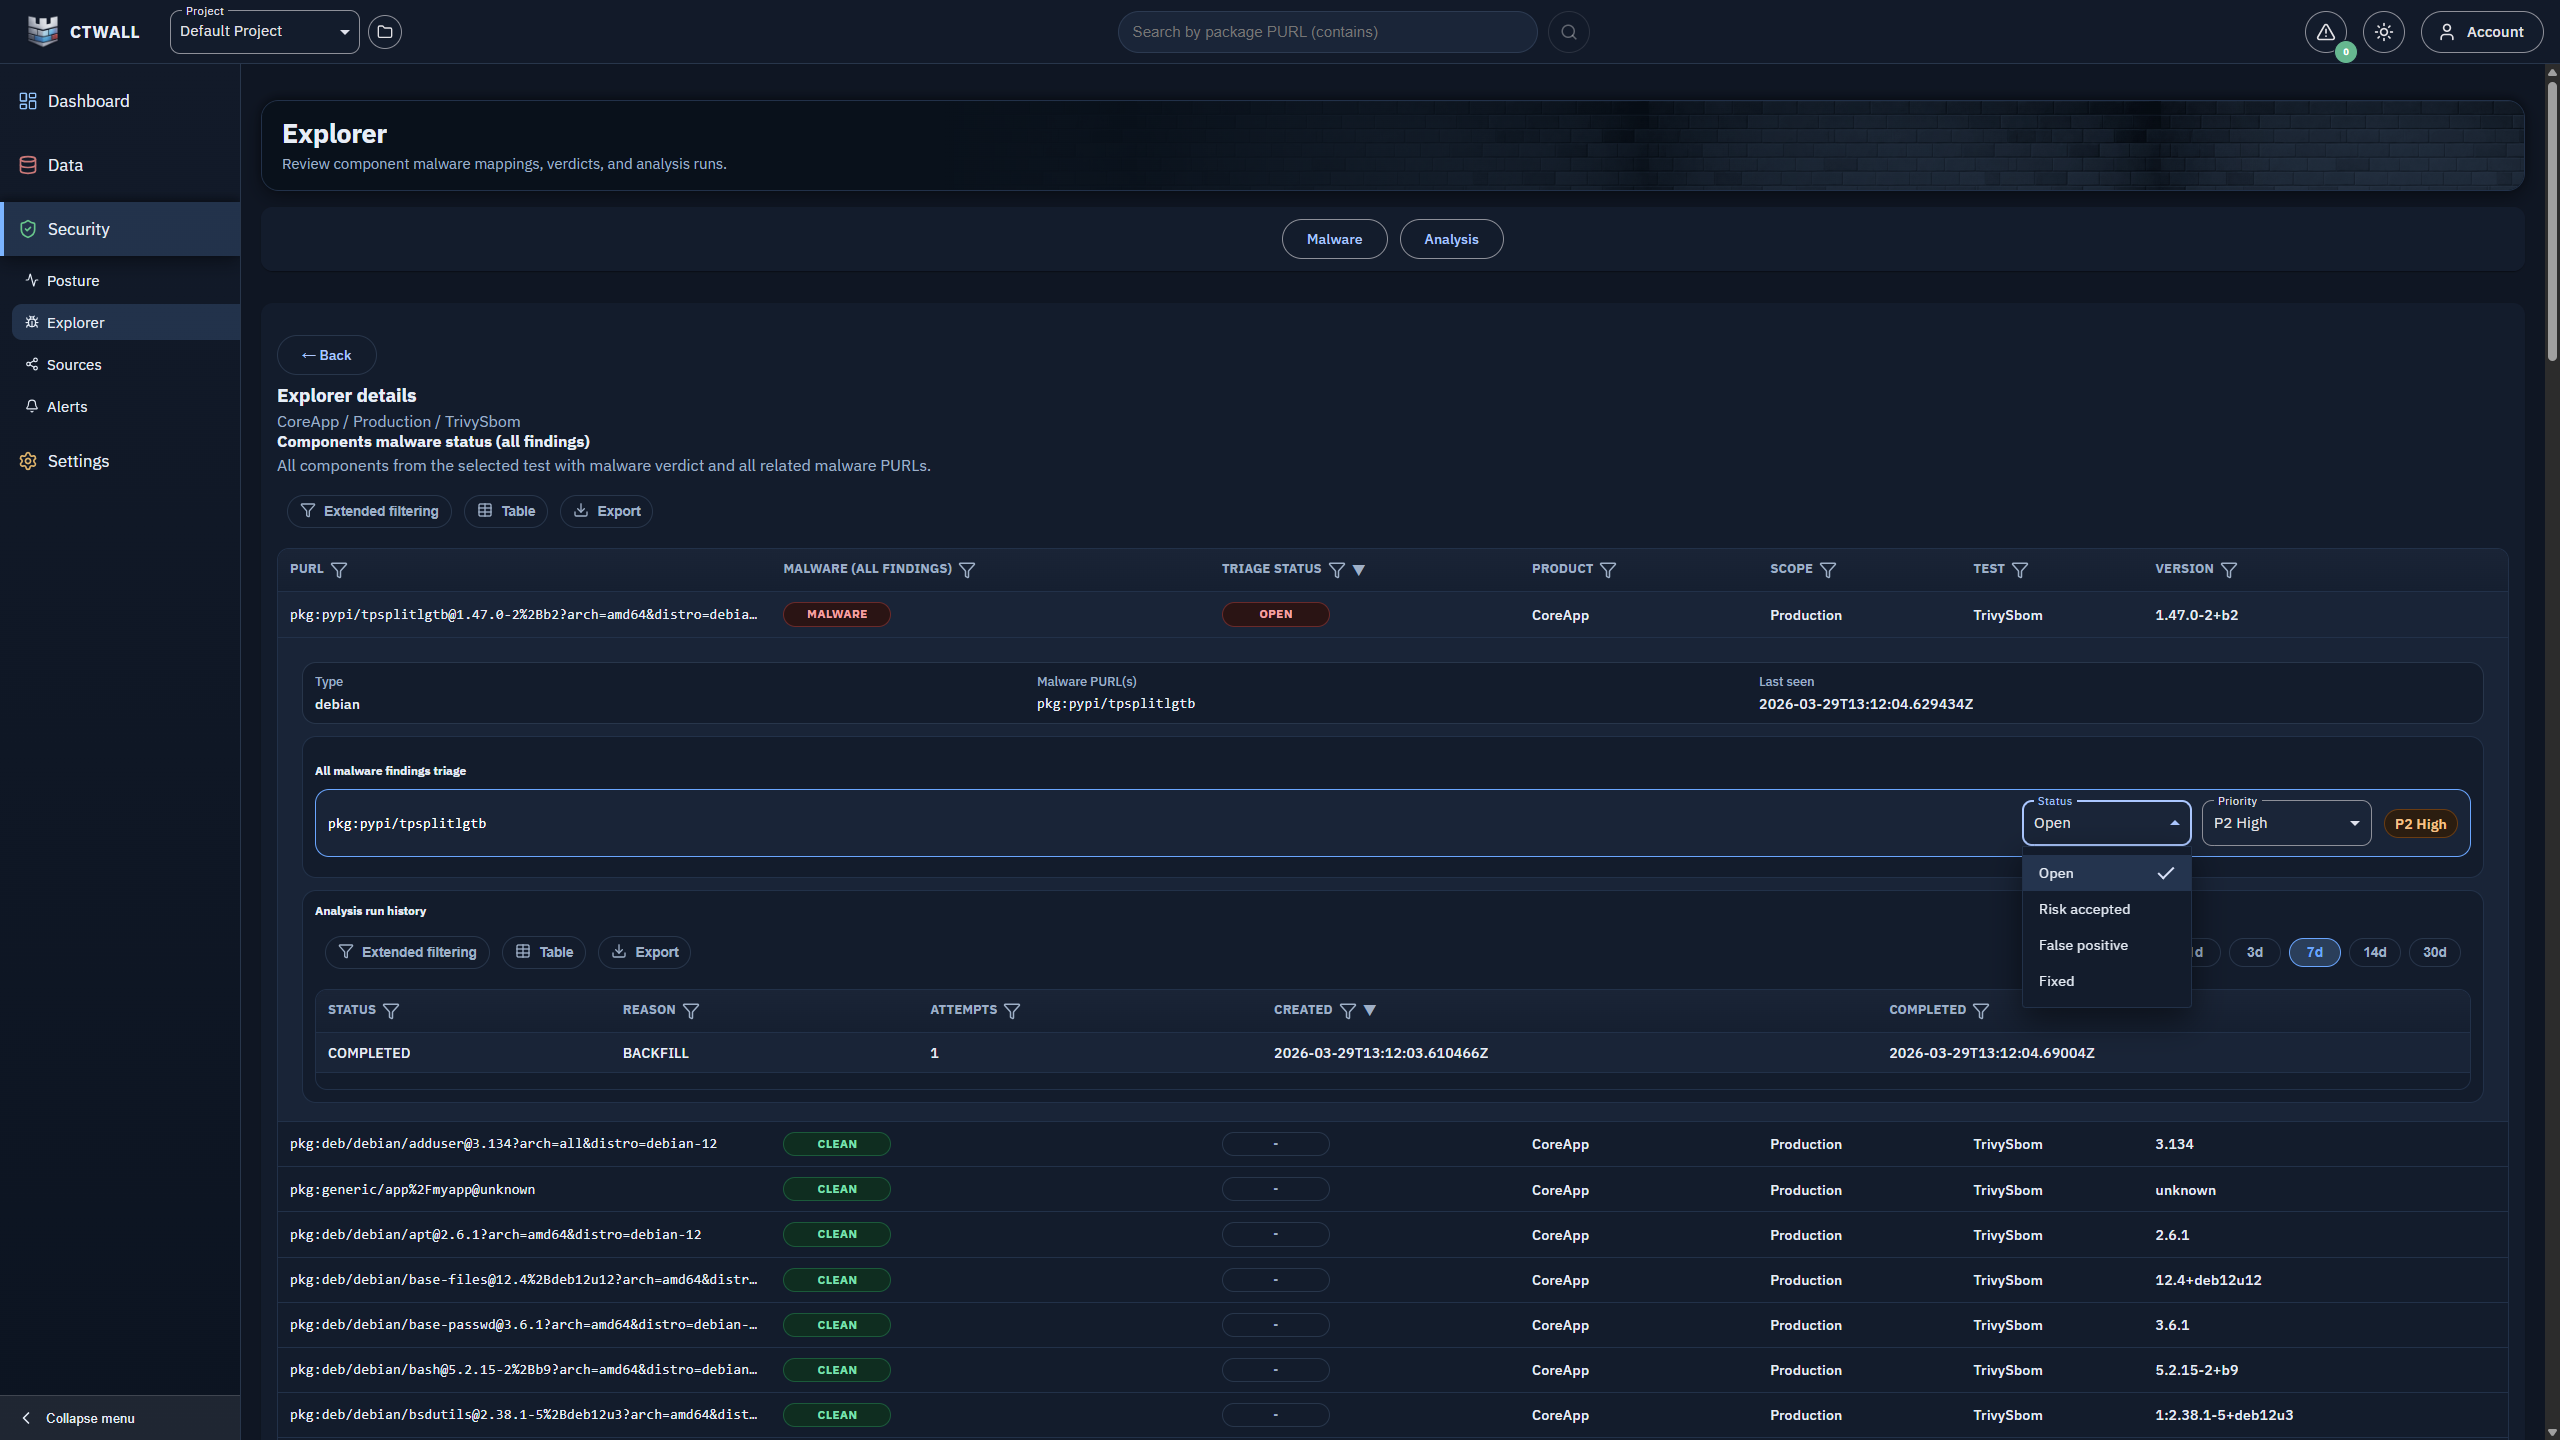
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

Robust Subdomain Takeover Tool

Crafting raw TCP/IP packets to send to poorly configured Kubernetes servers - CVE-2020-8558 PoC

Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…