d8-copy-fail-mitigation

Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…

Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…

Automated PowerShell orchestrator for applying Secure Boot mitigations against CVE-2023-24932 (BlackLotus). Handles registry changes, reboots,…

Ansible playbook to patch OpenSSL against CVE-2014-0291 and CVE-2015-0204 on Red Hat family servers, with automated service restart and verification.

Automated threat hunting pipeline that ingests Azure logs, uses LLM reasoning to detect suspicious activity, assess risk, and generate remediation…

End-to-end remediation of CVE-2013-3900 using PowerShell and Tenable. Demonstrates vulnerability identification, registry hardening, and automated…

Nuclei-based detection template for CVE-2023-27532 in Veeam Backup & Replication, enabling automated credential extraction vulnerability scanning…

Chef cookbook to detect and patch the Shellshock (CVE-2014-7169) bash vulnerability across servers using automated configuration management.

Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…

CI pipeline for building nxlog-ce on Ubuntu with CVE-2020-35488 vulnerability detection, enabling automated log collection and security auditing in…

Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).

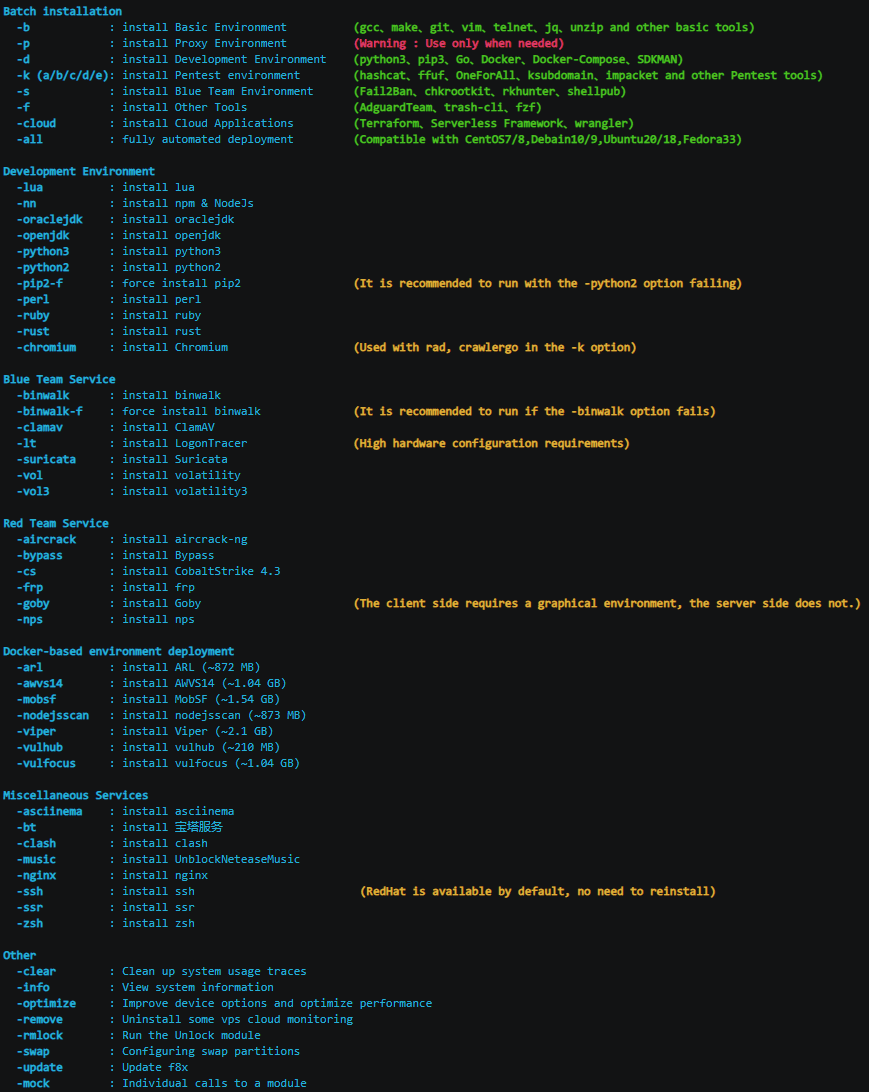
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

☸️ The Open Testing Platform for AI-Driven Engineering Teams

A lightweight caching proxy for package registries.

[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github

Authorized security-research reproduction of CVE-2025-15617 (GHSA-6xqr-4q5g-xc7x): artipacked GITHUB_TOKEN leak in wazuh FIM Windows integration…

Security-research lab: controlled reproduction of CVE-2024-4254 (GHSA-fc78-c36r-cc59) — deploy-website.yml fork checkout/code execution in…