
CVE-2023-27163-exploit
 jeanback1/cve-2023-27163-exploit
SSRF exploit for CVE-2023-27163 in request-baskets, enabling internal port scanning, cloud metadata probing, and service discovery via malicious…
cloud-securityexploitationport-scanning+3
jeanback1/cve-2023-27163-exploitSSRF exploit for CVE-2023-27163 in request-baskets, enabling internal port scanning, cloud metadata probing, and service discovery via malicious…
 mbanyamer/cve-2026-24514-kubernetes-dos
Proof-of-concept exploit for CVE-2026-24514, a memory exhaustion denial-of-service in ingress-nginx validating admission webhook, allowing…
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 abdurahmon3236/cve-2024-36539
PoC exploit for insecure permissions in Contour v1.28.3 that retrieves a Kubernetes service account token and accesses the cluster API, demonstrating…
 shefirot/cve-2024-3094
Basic POC to test CVE-2024-3094 vulnerability inside K8s cluster
 daryllundy/cve-2025-32711
PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
 aaronsvk/cve-2020-3956
PoC exploit for VMware Cloud Director RCE (CVE-2020-3956)
 lightspin-tech/red-detector
Automated vulnerability, misconfiguration, and rootkit scanner for AWS EC2 instances using Vuls, Lynis, and Chkrootkit via snapshot-based offline…
 oscerd/cve-2026-43867
Reproducer for CVE-2026-43867 — Apache Camel camel-pqc AwsSecretsManagerKeyLifecycleManager unsafe key-metadata deserialization (RCE)
 grabesec/xcp_ng_cve-2026-31431_tester
Non-destructive detector for CVE-2026-31431 (Copy Fail) local privilege escalation in XCP-ng 8.3 Dom0, validating kernel vulnerability via page-cache…
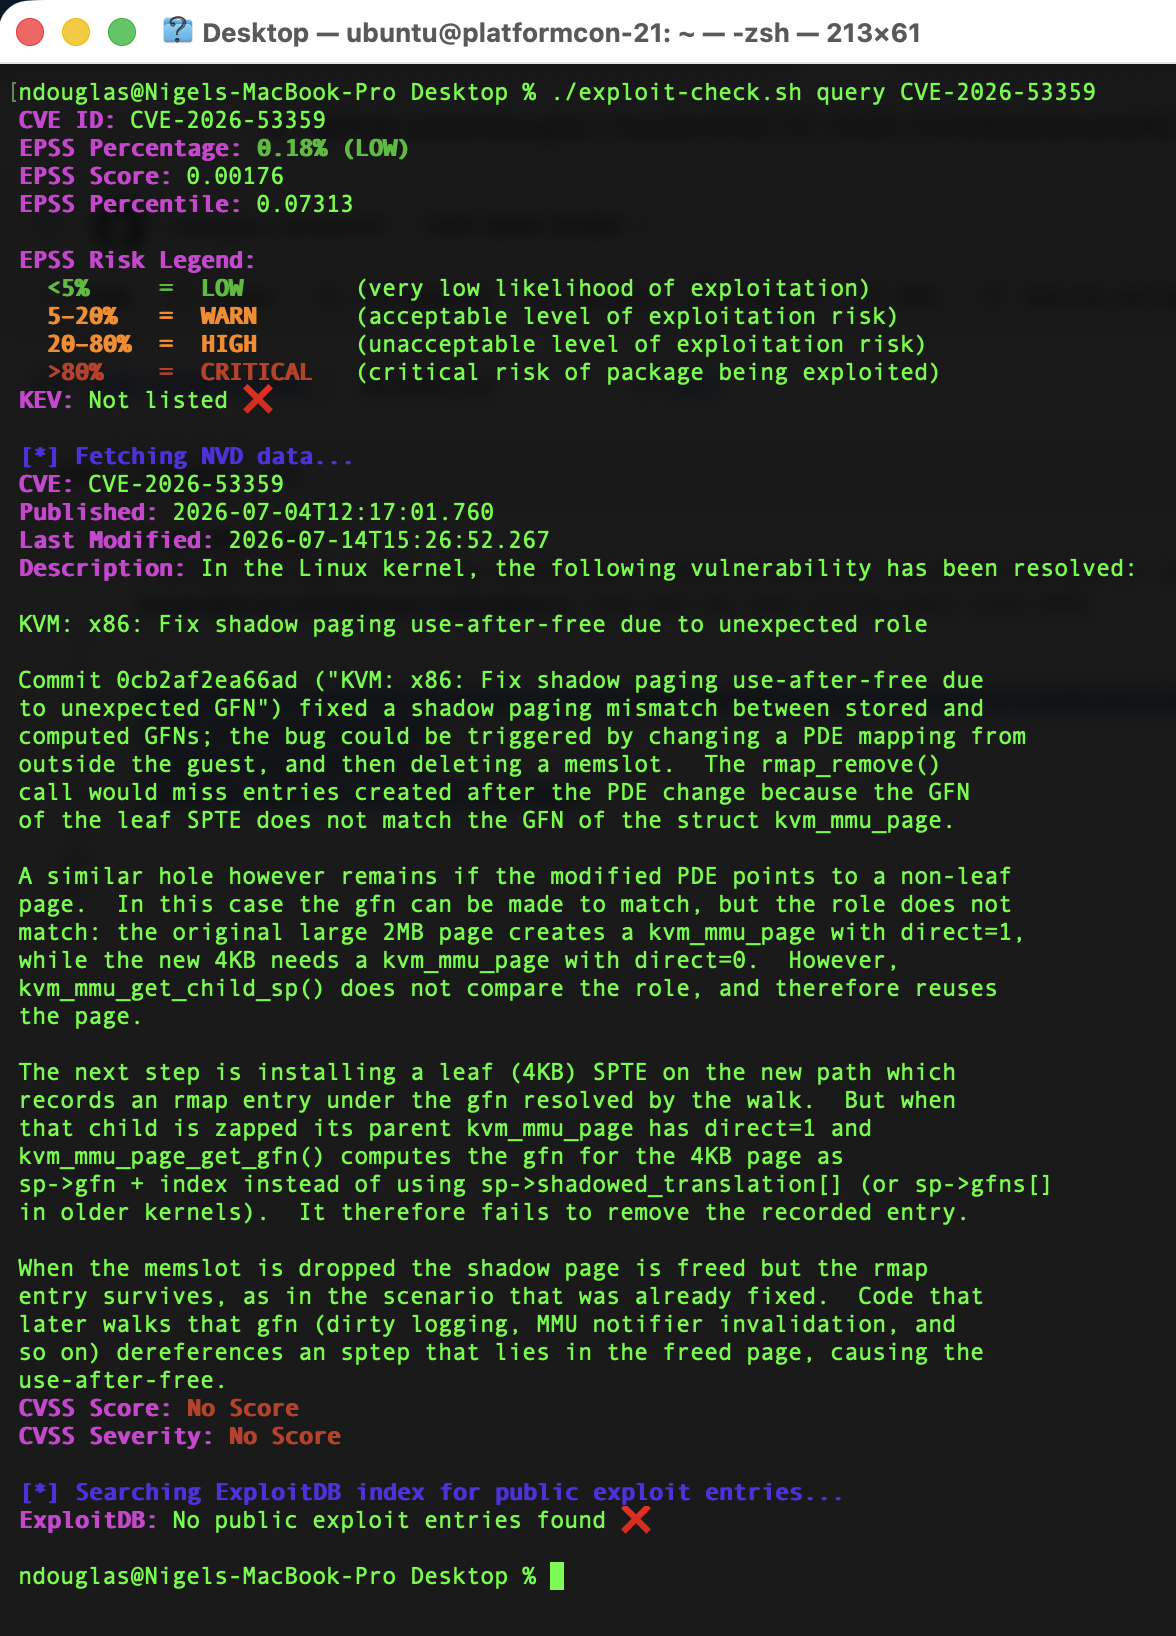 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 moshuum/tf-log4j-aws-poc
This project files demostrate a proof-of-concept of log4j vulnerability (CVE-2021-44228) on AWS using Terraform Infrastructure-as-a-code means.
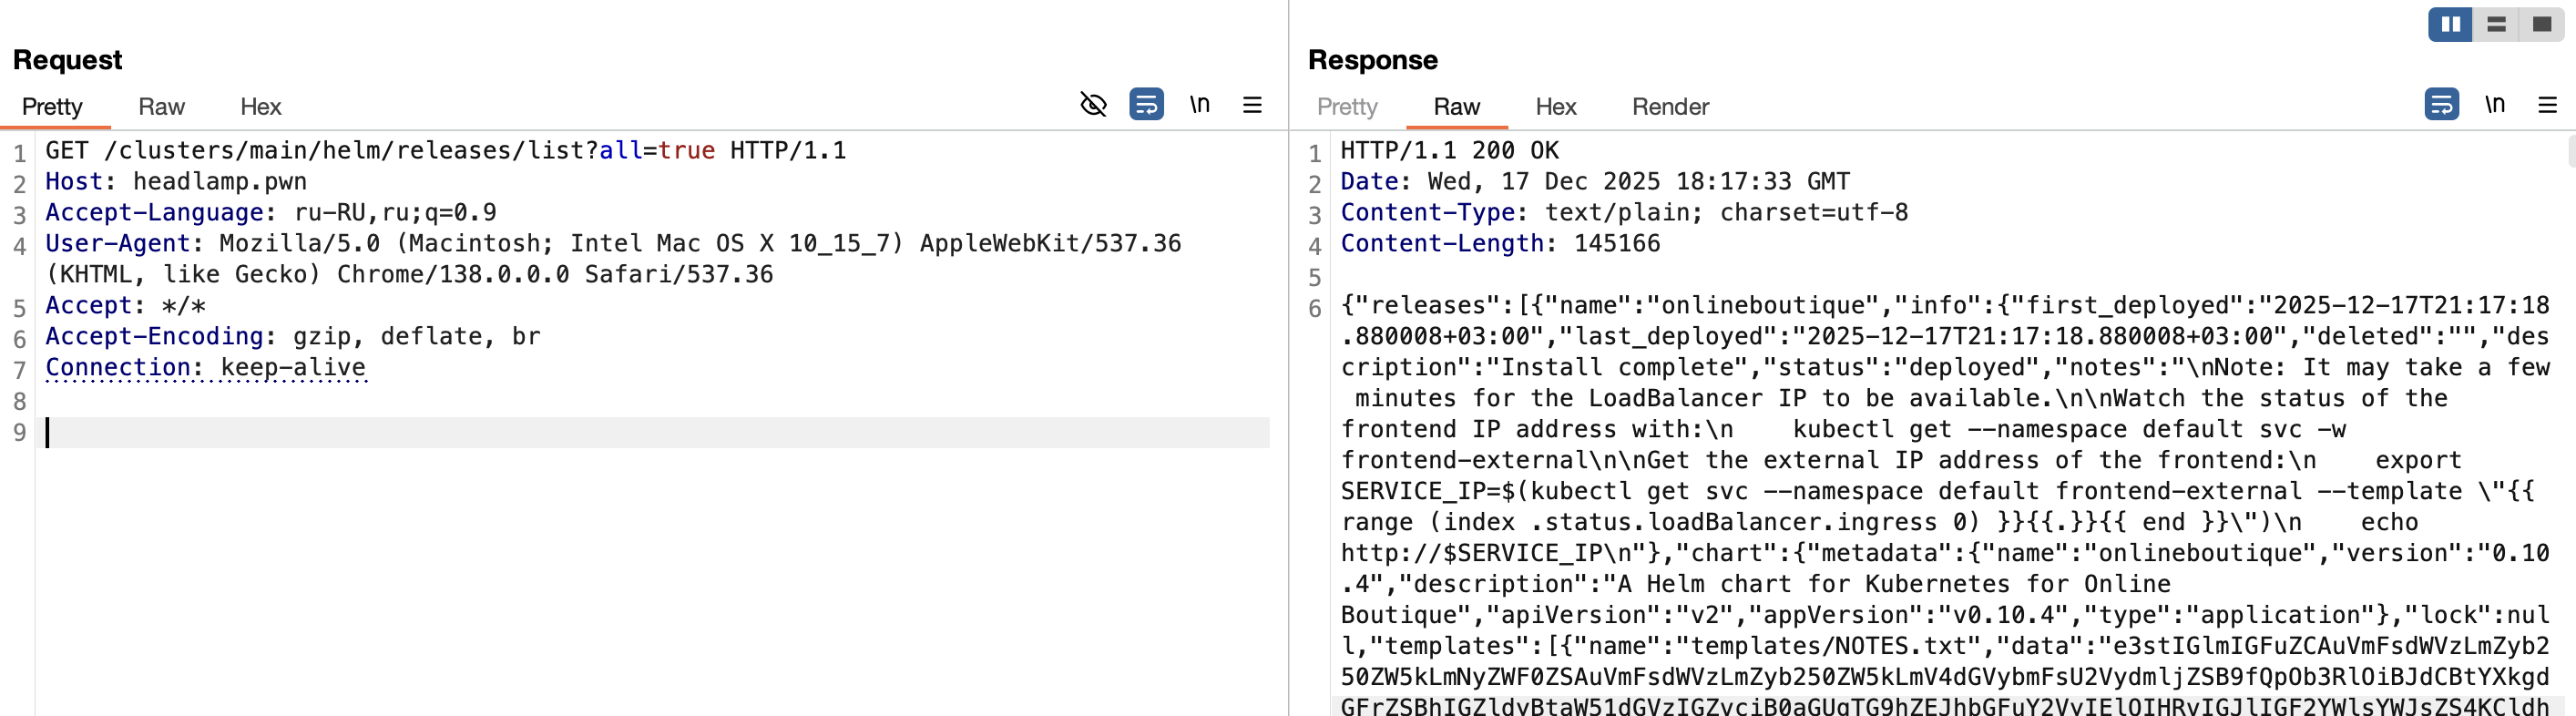 r0binak/cve-2025-14269
CVE-2025-14269 PoC exploit
 yunus-a1i/veeam-cve-2023-27532-mock
Nuclei-based detection template for CVE-2023-27532 in Veeam Backup & Replication, enabling automated credential extraction vulnerability scanning…
 shoucheng3/apache__rocketmq_cve-2023-33246_5-1-0
Exploit for CVE-2023-33246 targeting Apache RocketMQ 5.1.0, enabling remote code execution via crafted packet injection into the broker's update…
 shoucheng3/alibaba__nacos_cve-2021-44667_2-0-3
Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…