
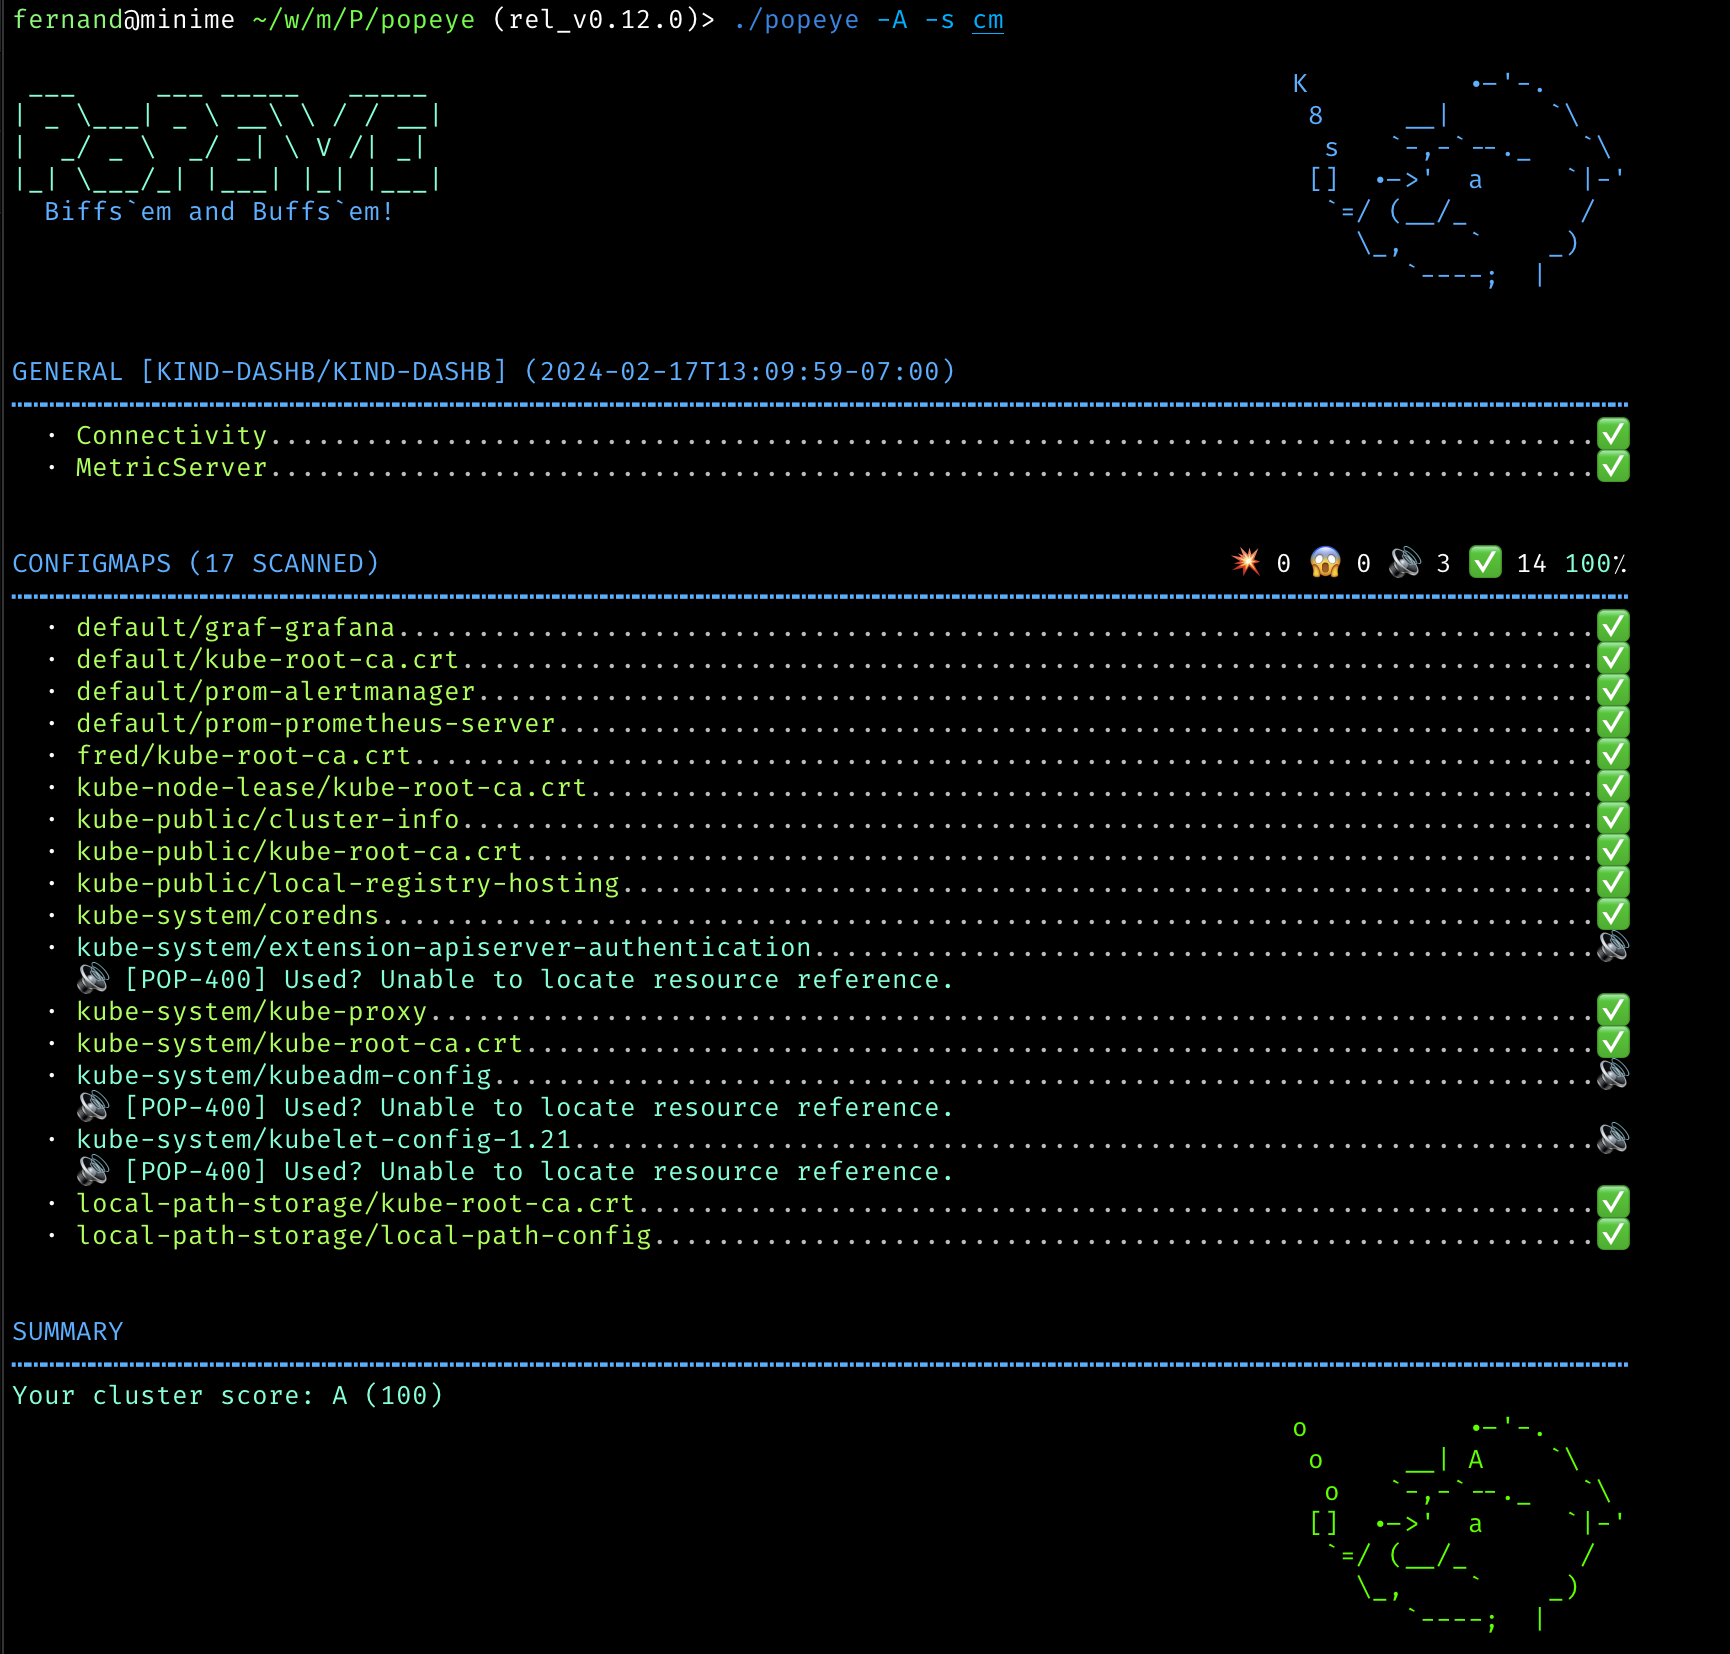
popeye
 derailed/popeye
👀 A Kubernetes cluster resource sanitizer
cloud-securityconfiguration-auditingcontainer-security+1
6.4k1 year ago
derailed/popeye👀 A Kubernetes cluster resource sanitizer
 cujanovic/ssrf-testing
SSRF (Server Side Request Forgery) testing resources
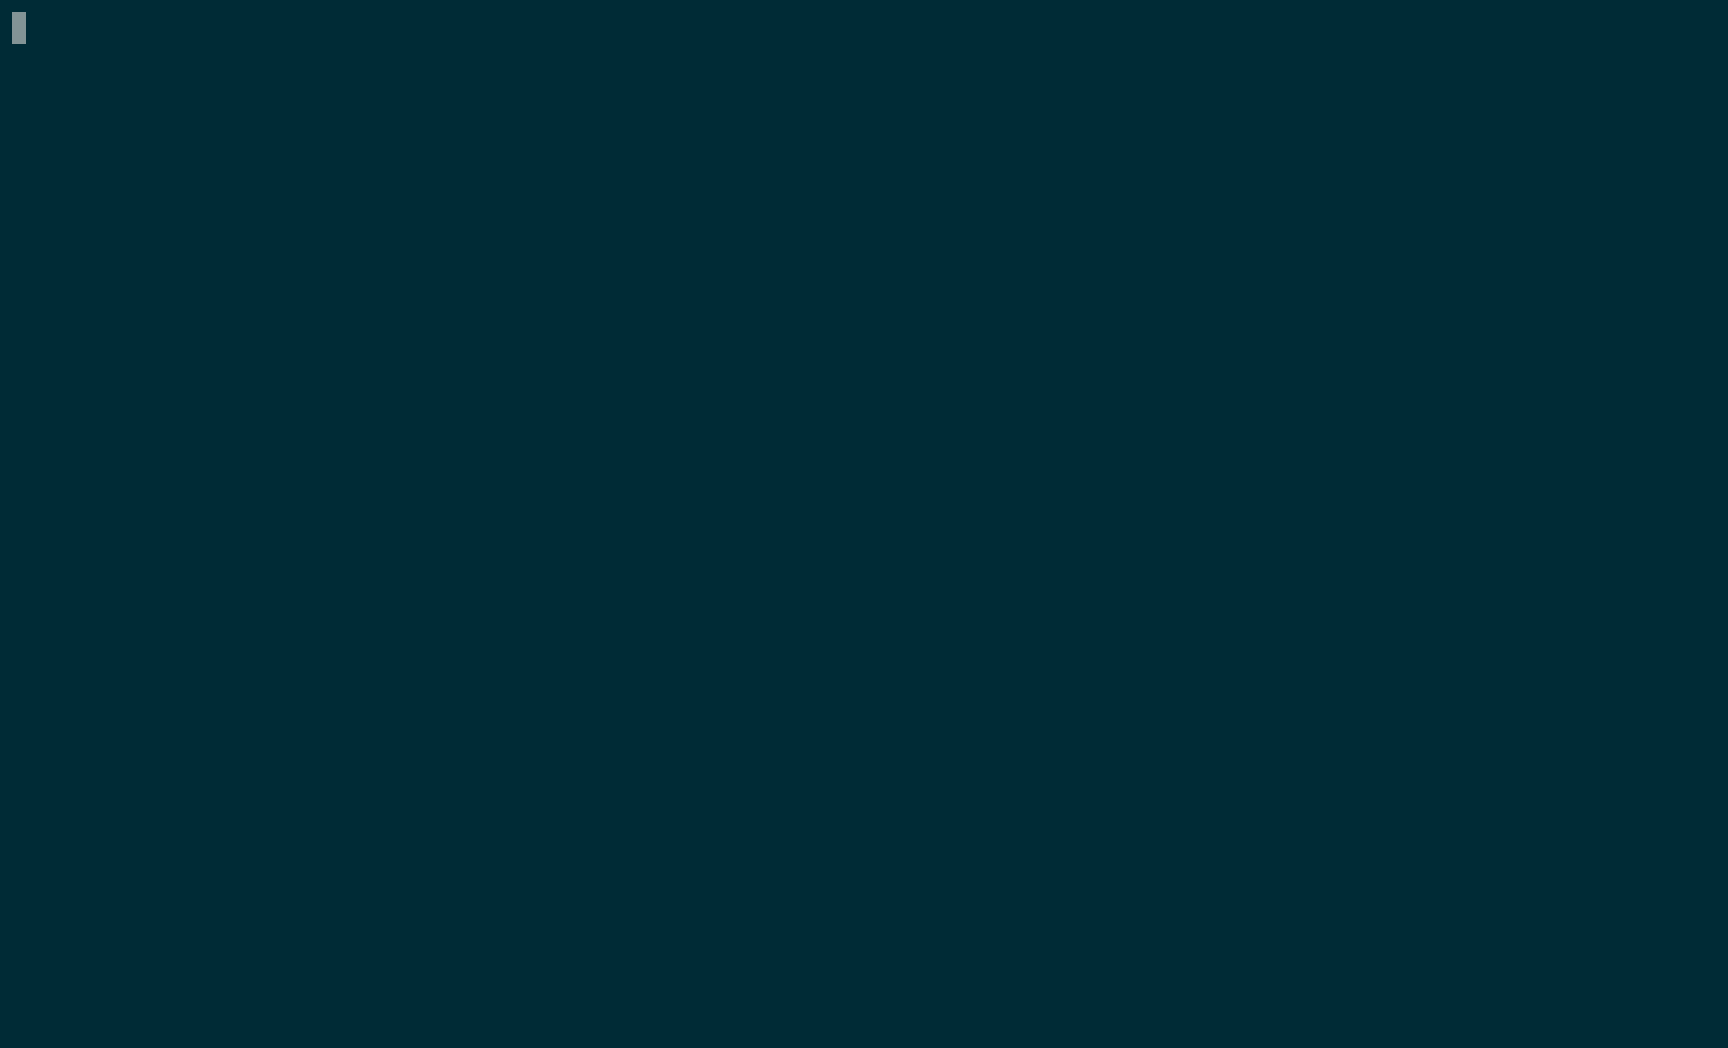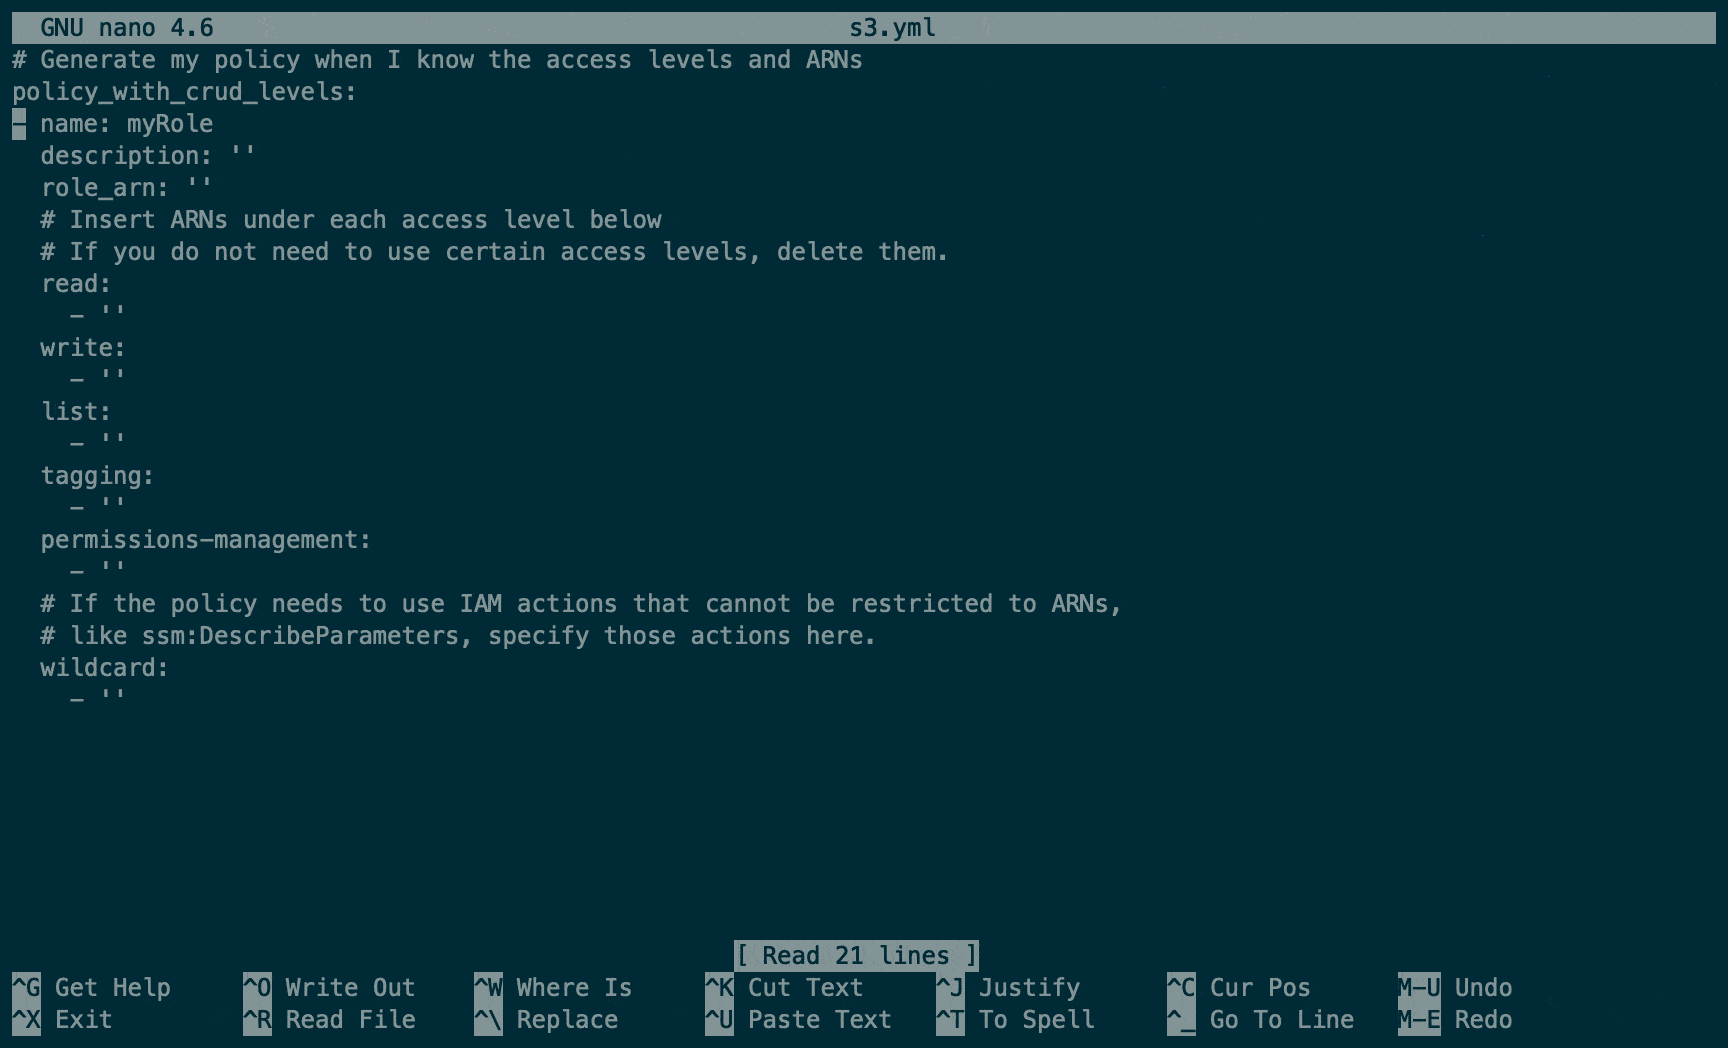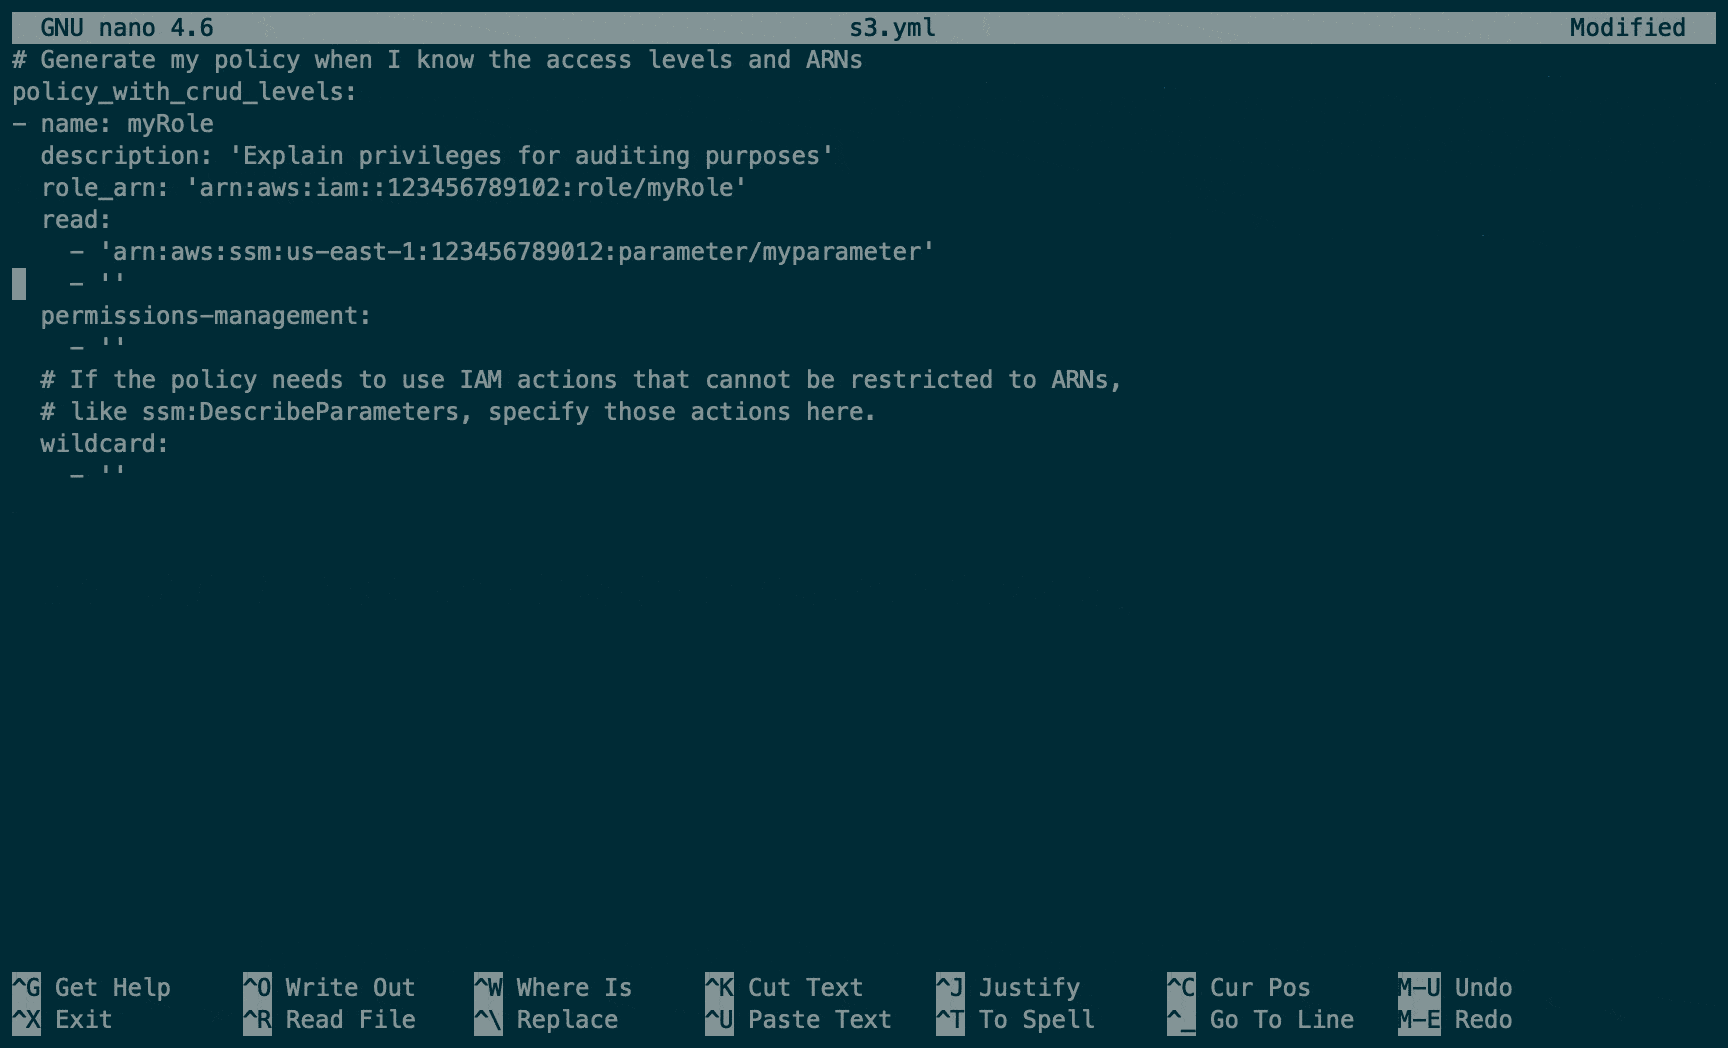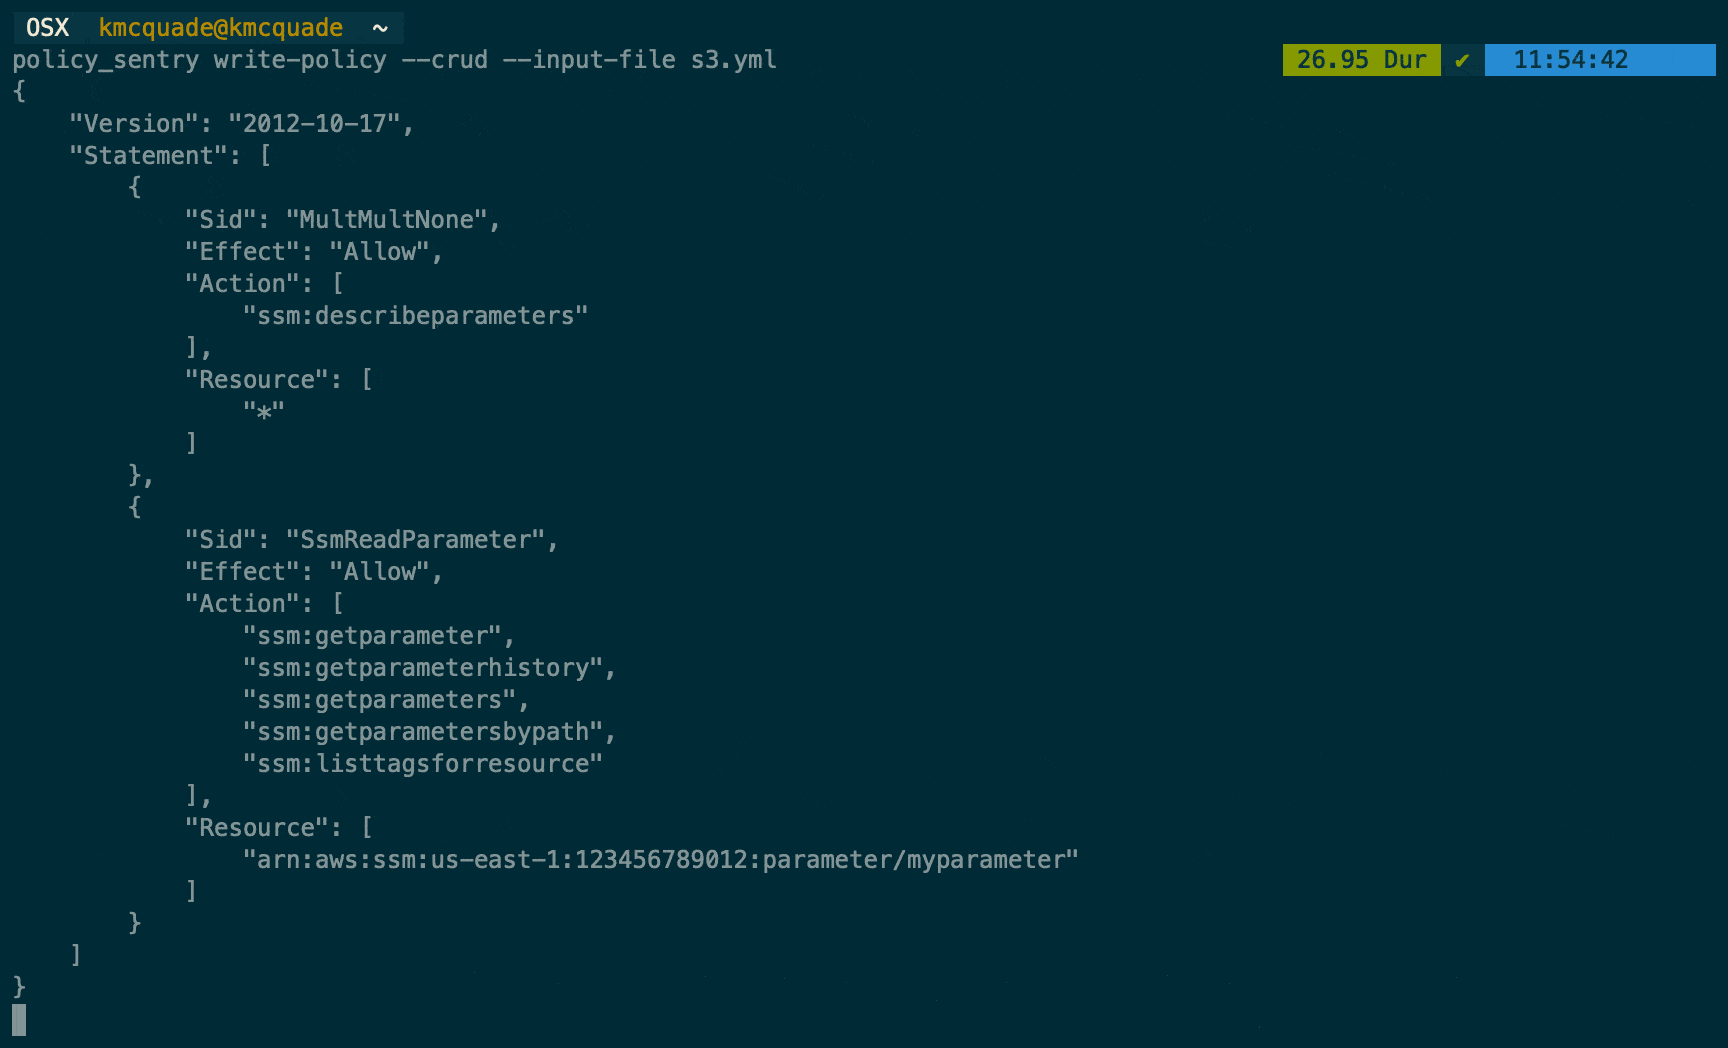 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 tmobile/pacbot
PacBot (Policy as Code Bot)
 hacktricks-wiki/hacktricks-cloud
Community-driven knowledge base for pentesting cloud environments and CI/CD pipelines: attack techniques, enumeration, privilege escalation, and…
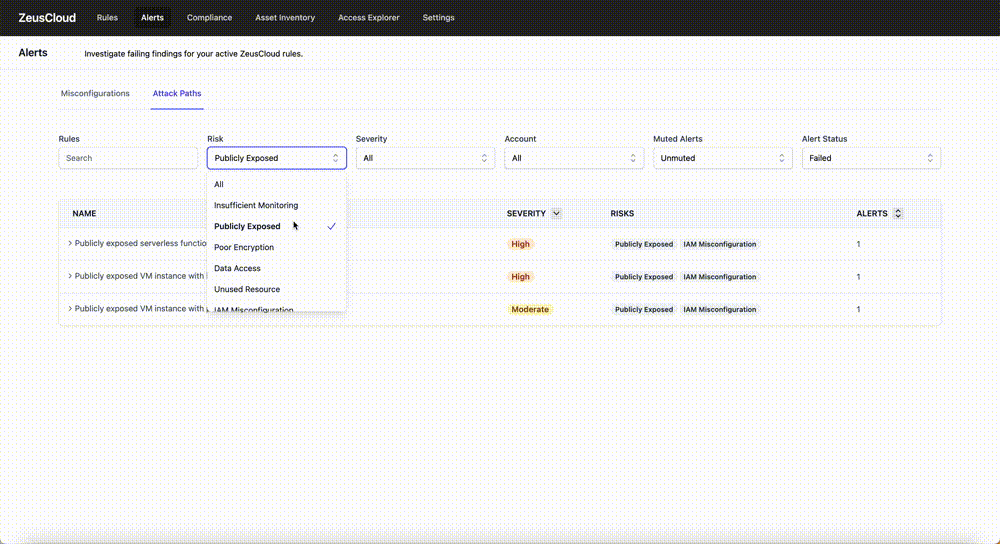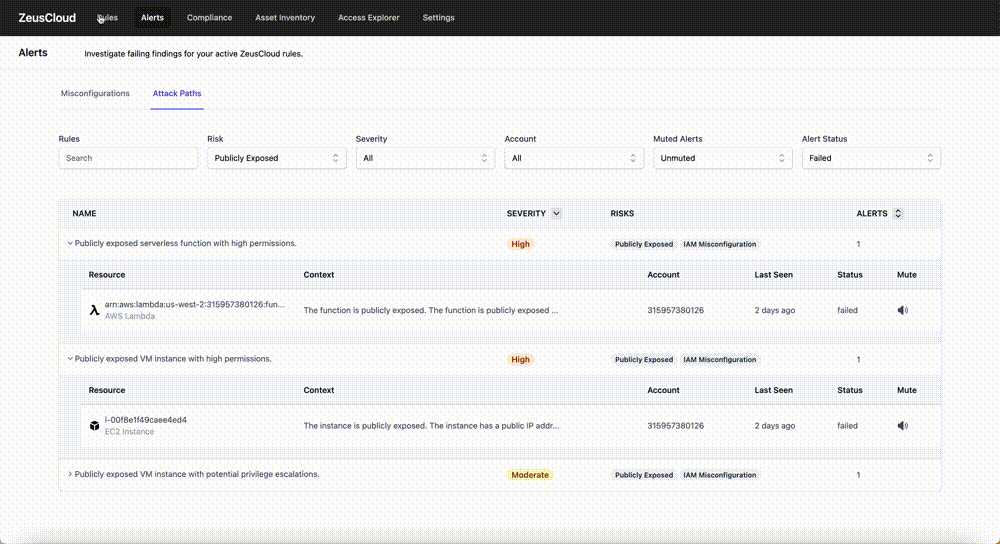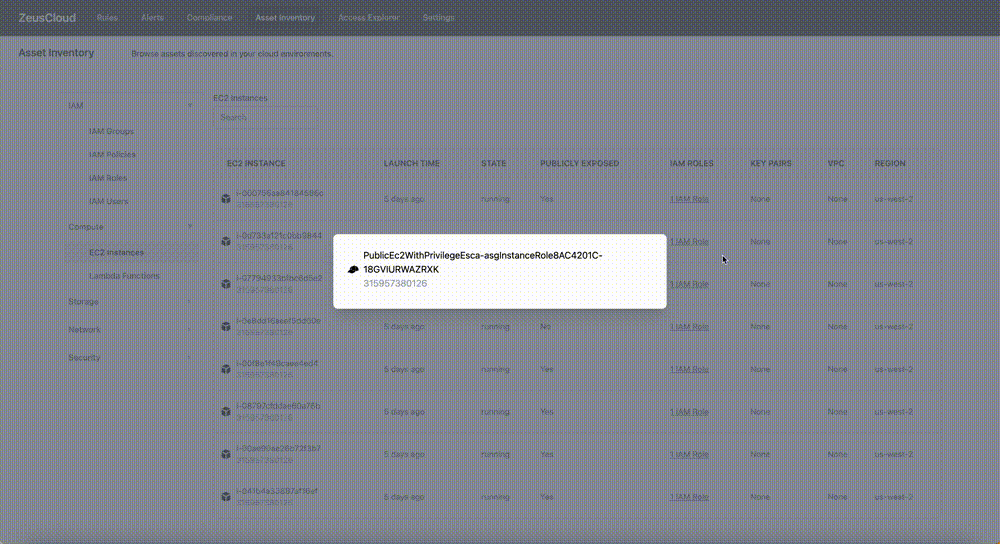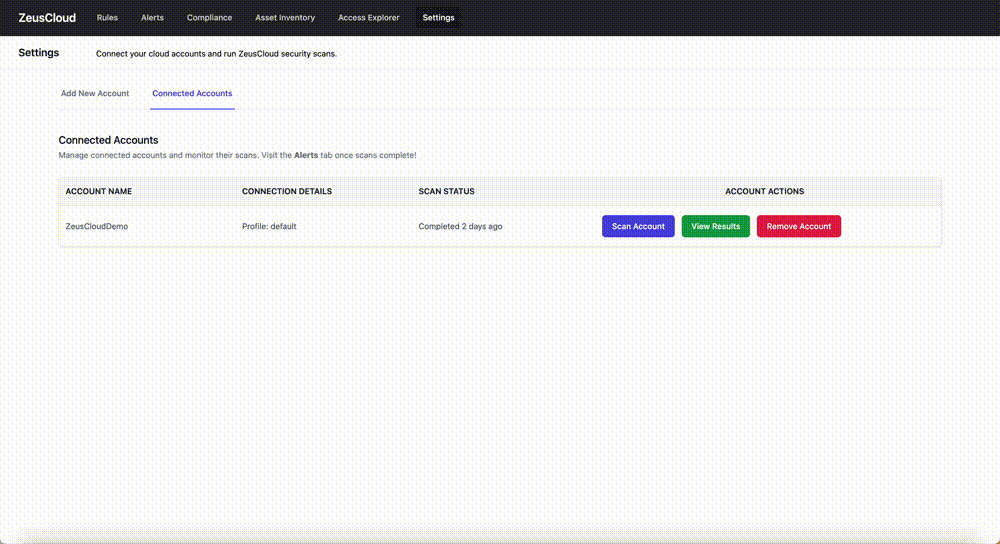 zeus-labs/zeuscloud
Open-source cloud security platform that discovers attack paths, identifies misconfigurations, visualizes IAM access, and provides step-by-step…
 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
 owasp/docker-security
Getting a handle on container security
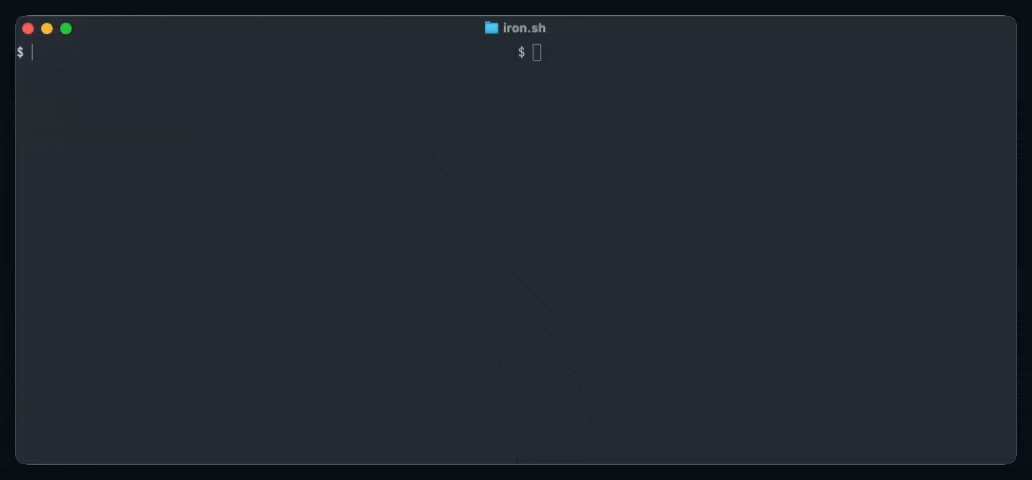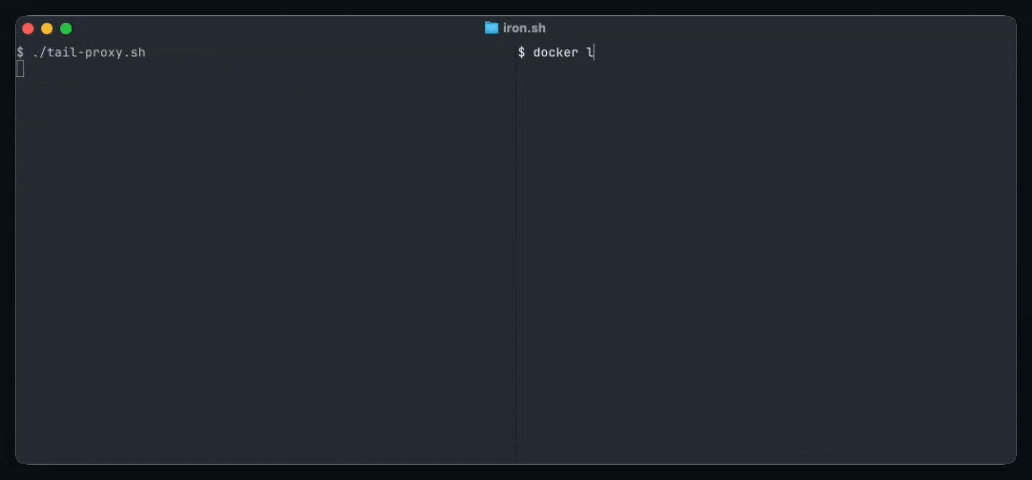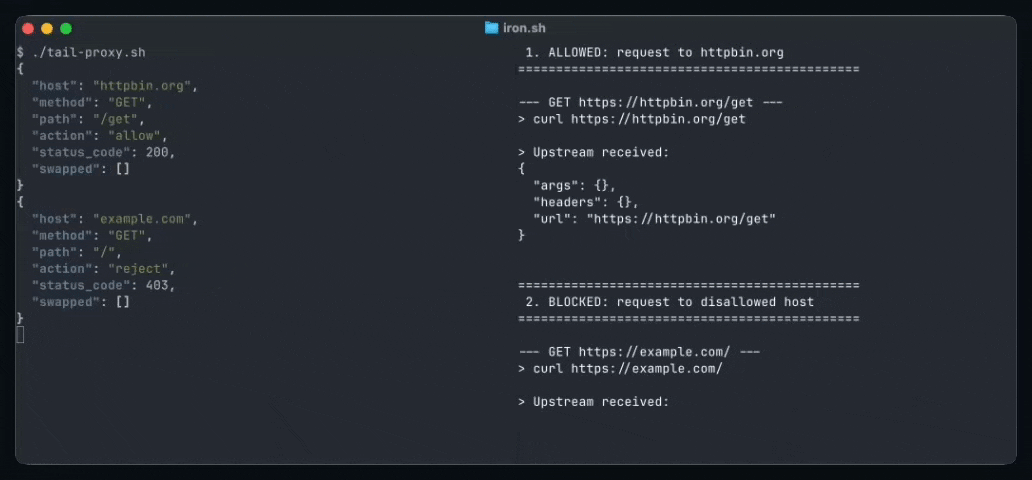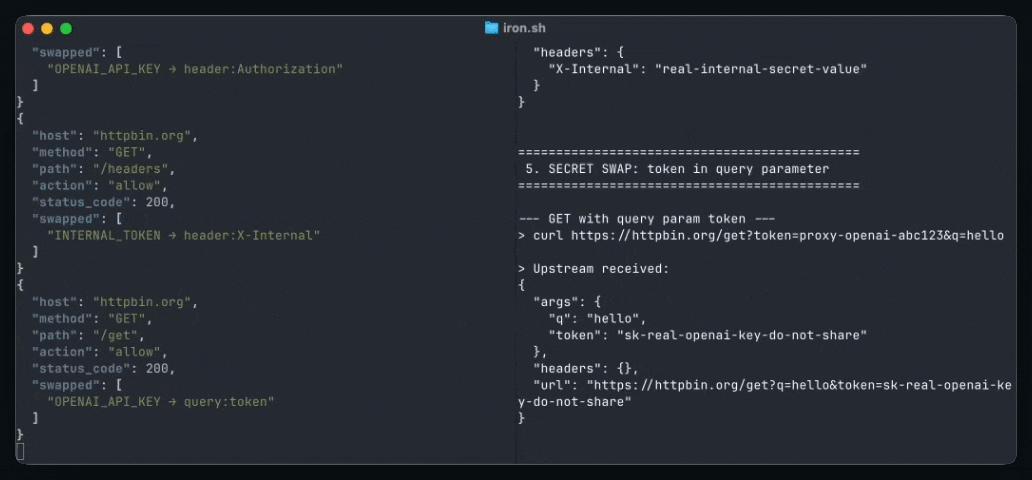 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
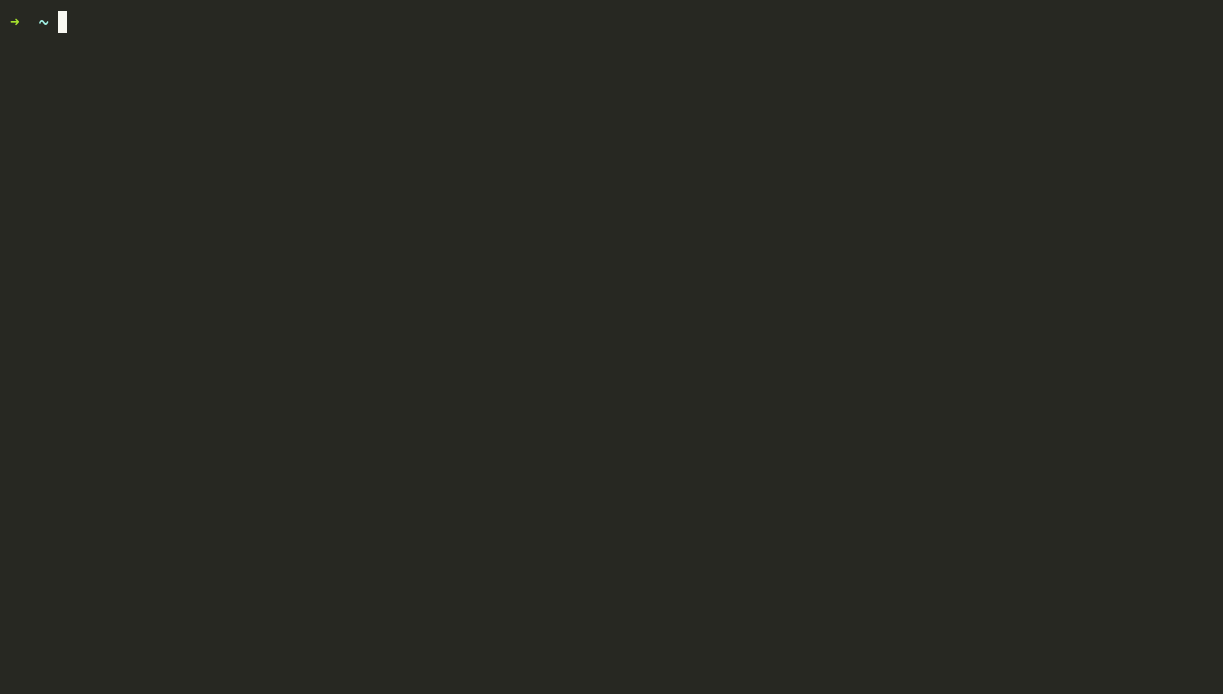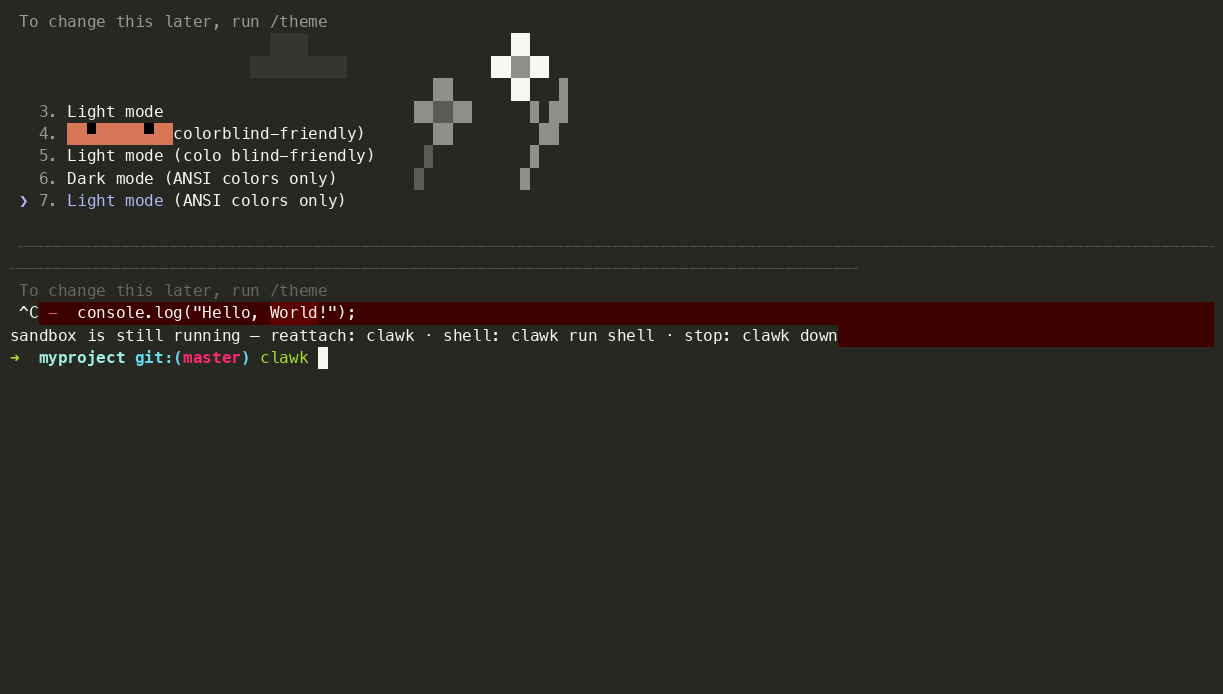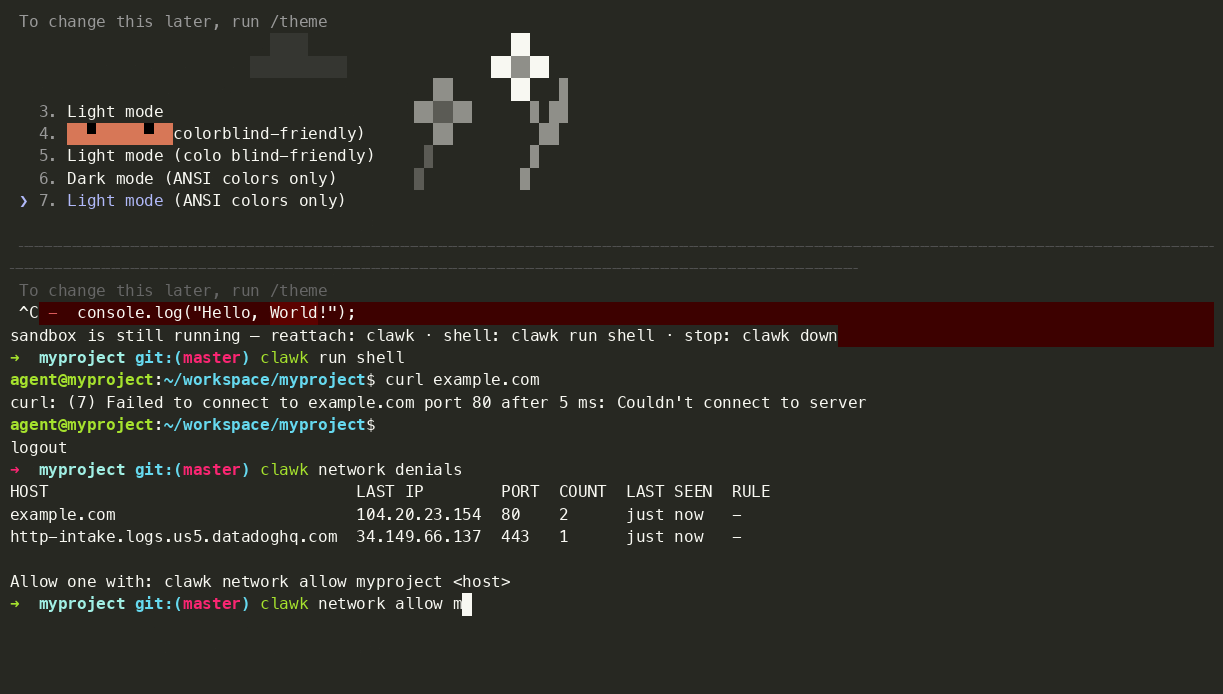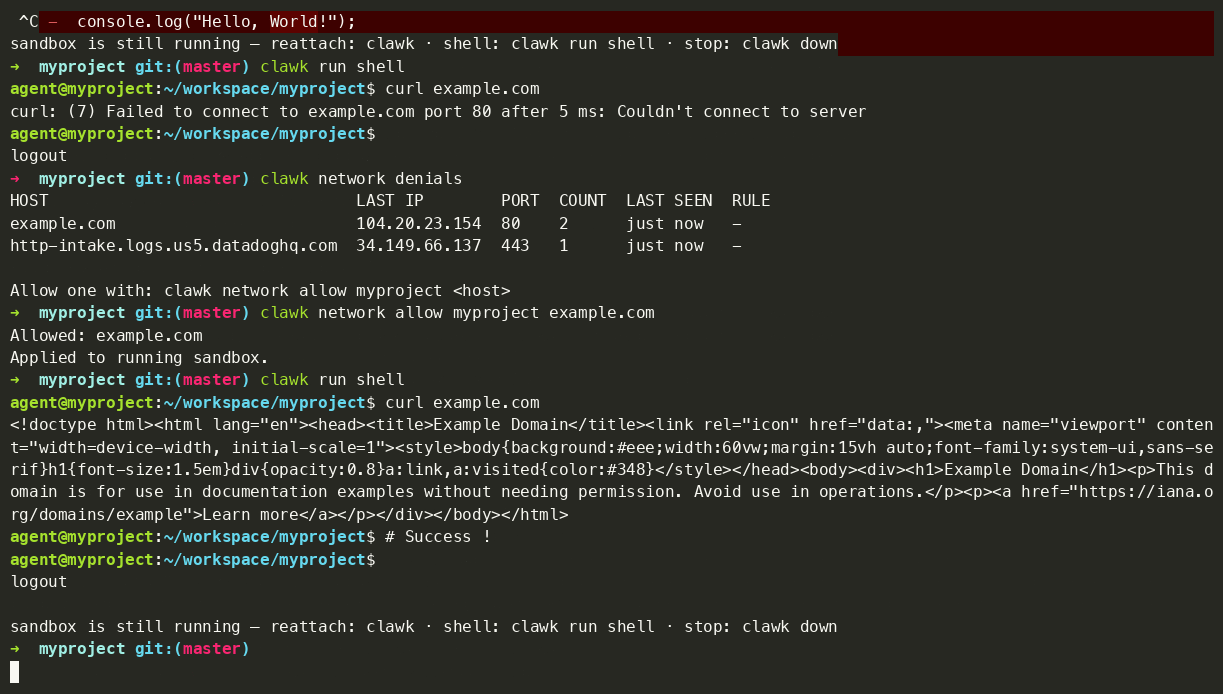 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 controlplaneio/simulator
Kubernetes Security Training Platform - focusing on security mitigation
 graphenex/graphenex
Automated System Hardening Framework
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
 yelp/amira
AMIRA: Automated Malware Incident Response & Analysis
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️