
KubeArmor
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
cloud-securitycontainer-securitydefensive-tools
kubearmor/kubearmorRuntime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
 enaqx/awesome-pentest
A collection of awesome penetration testing resources, tools and other shiny things
 infisical/infisical
Infisical is the open-source platform for secrets, certificates, and privileged access management.
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
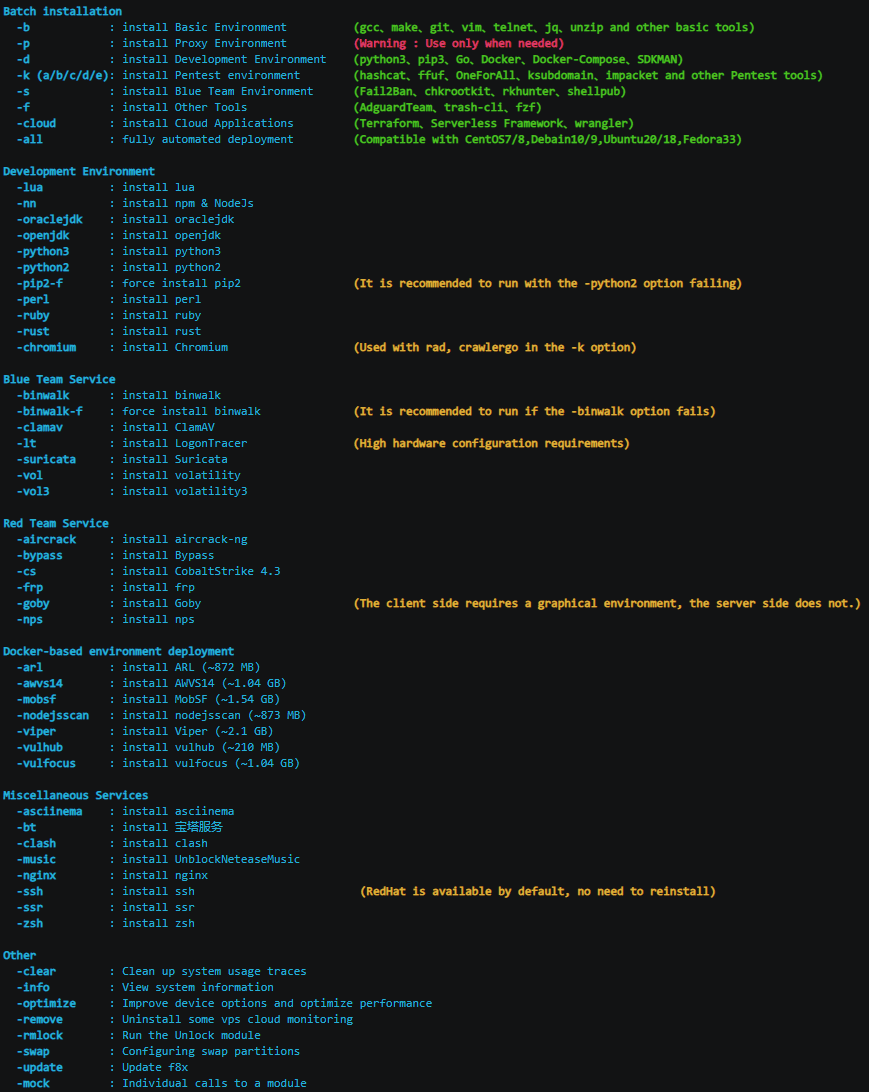 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
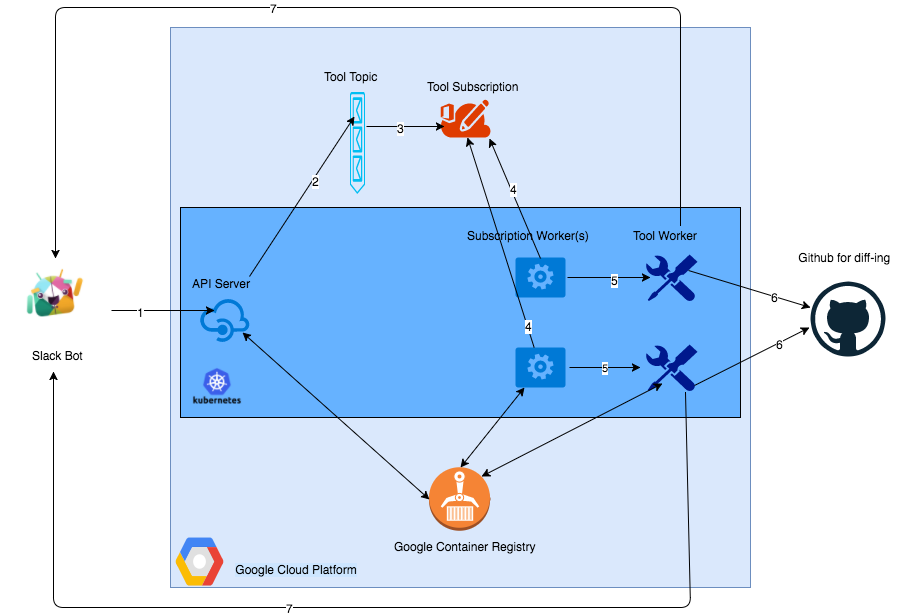 anshumanbh/kubebot
A security testing Slackbot built with a Kubernetes backend on the Google Cloud Platform
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
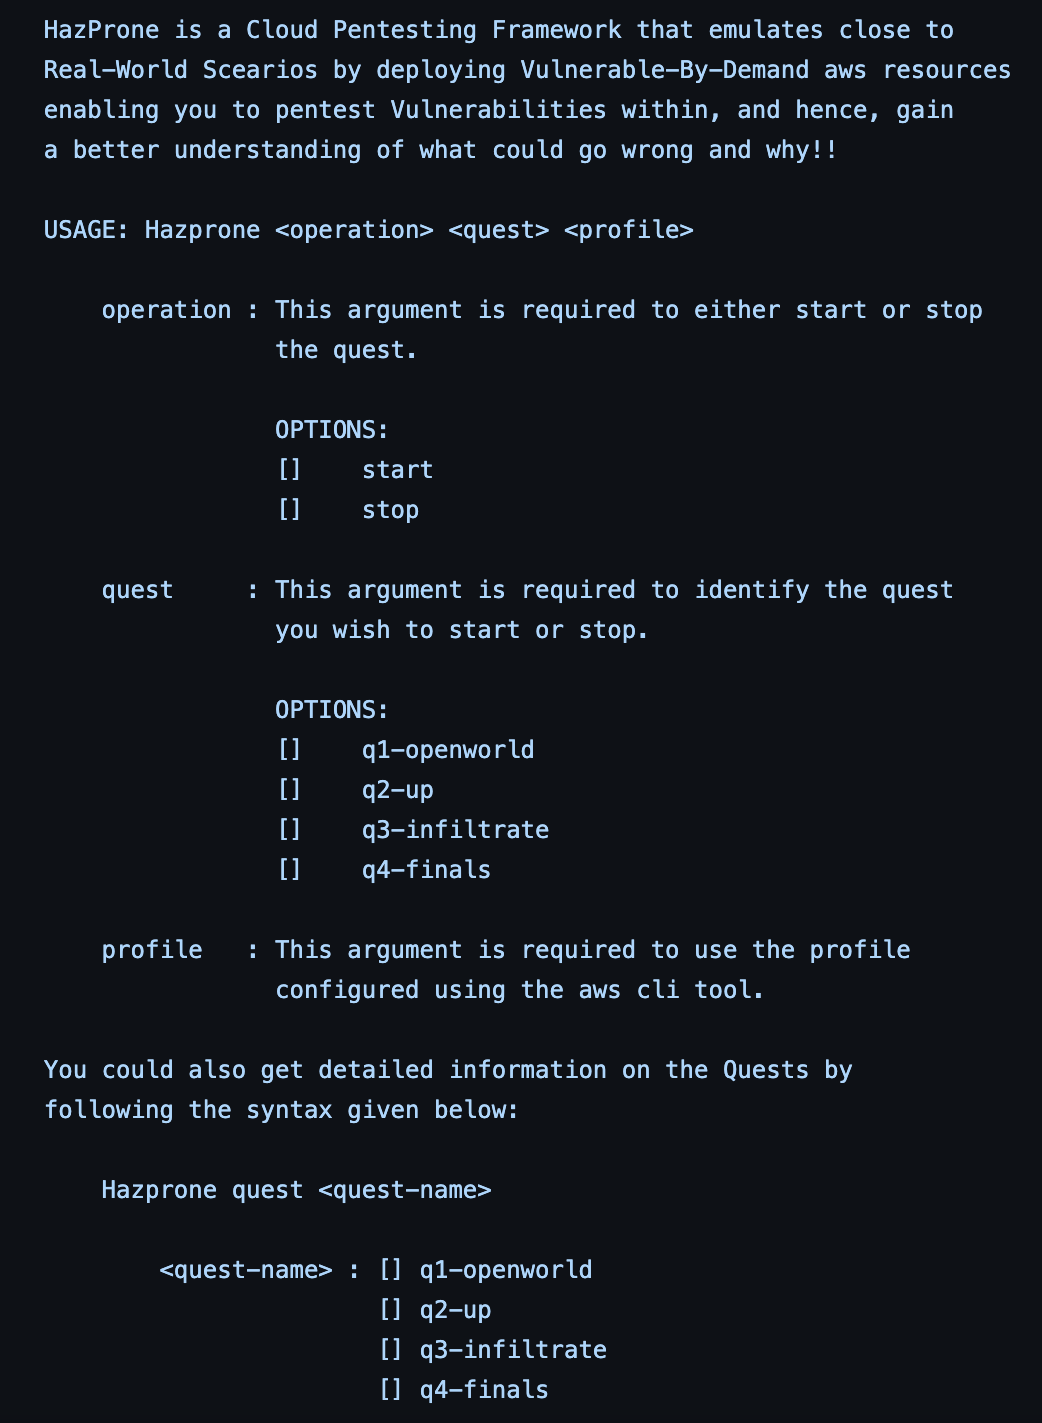 stafordtituss/hazprone
Cloud pentesting framework deploying vulnerable-by-demand AWS resources with quest-based scenarios to teach practical penetration testing and…
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 alexsvobo/nhi-zero-trust-bypass
Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…