
CVE-2022-29170
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
cloud-securityexploitationmisconfiguration+2
yijikeji/cve-2022-29170Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
 diedromeo/cve-2026-62201-openclaw-ssrf
Deep-dive analysis of CVE-2026-62201: OpenClaw sandbox exec-server network policy bypass (SSRF). Root cause, vulnerable vs patched code,…
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
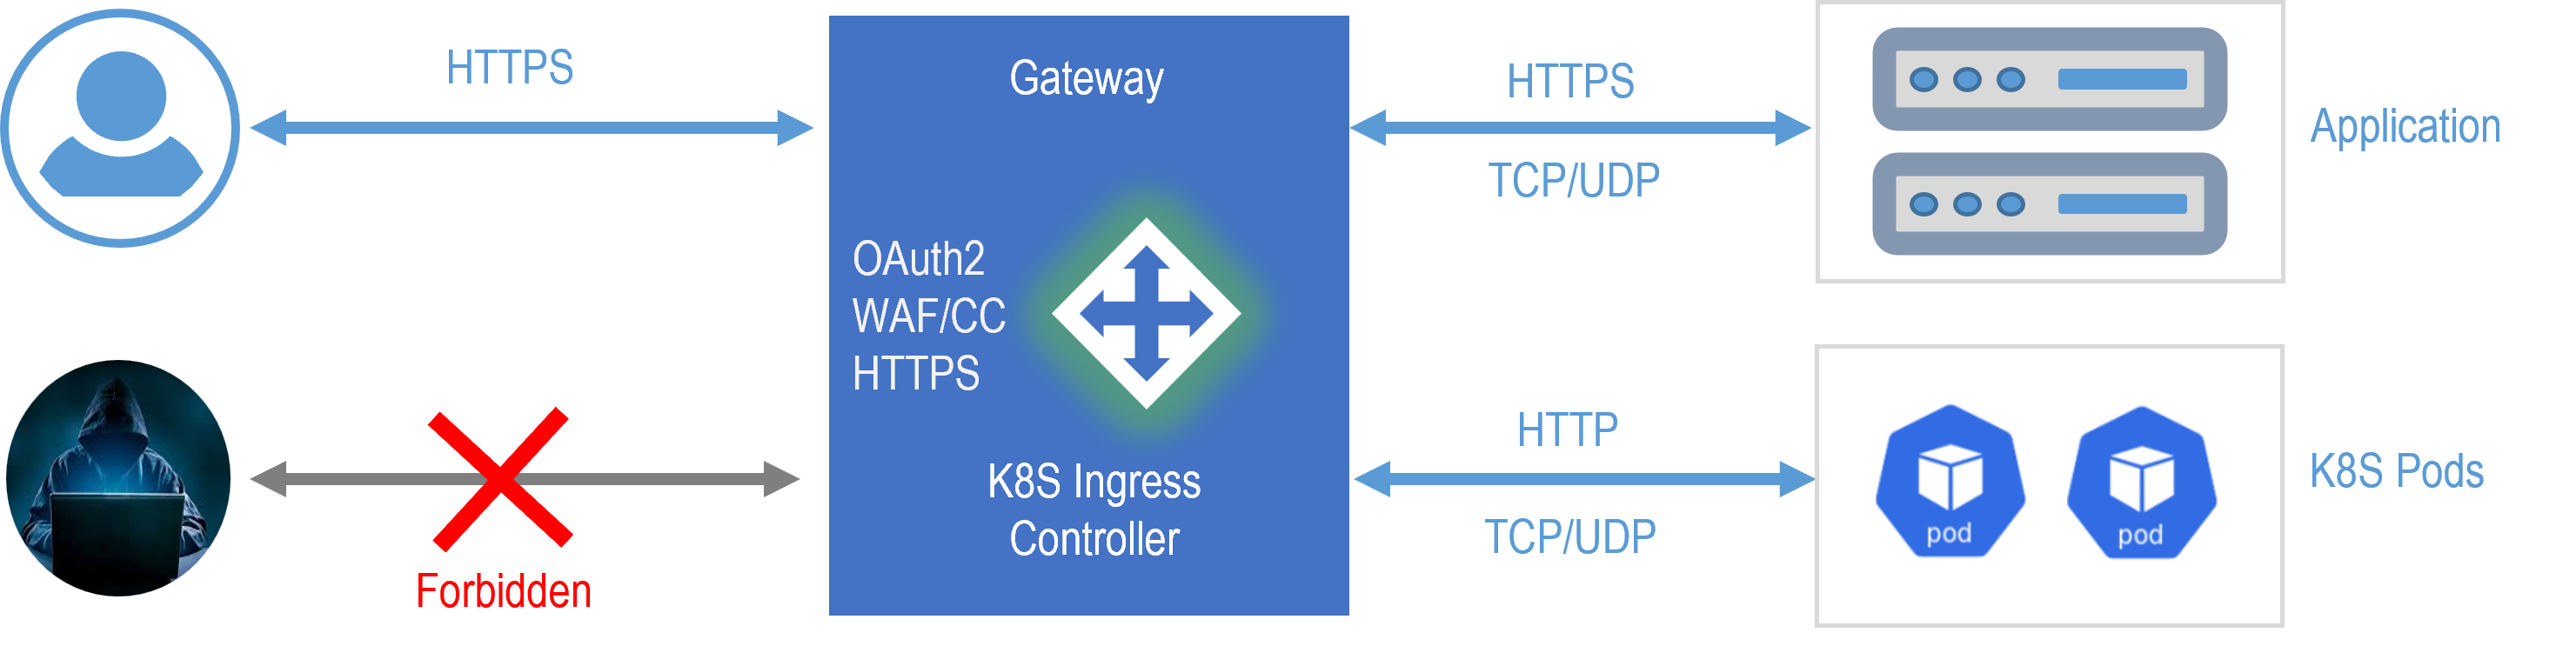 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 appliscale/cloud-security-audit
A command line security audit tool for Amazon Web Services
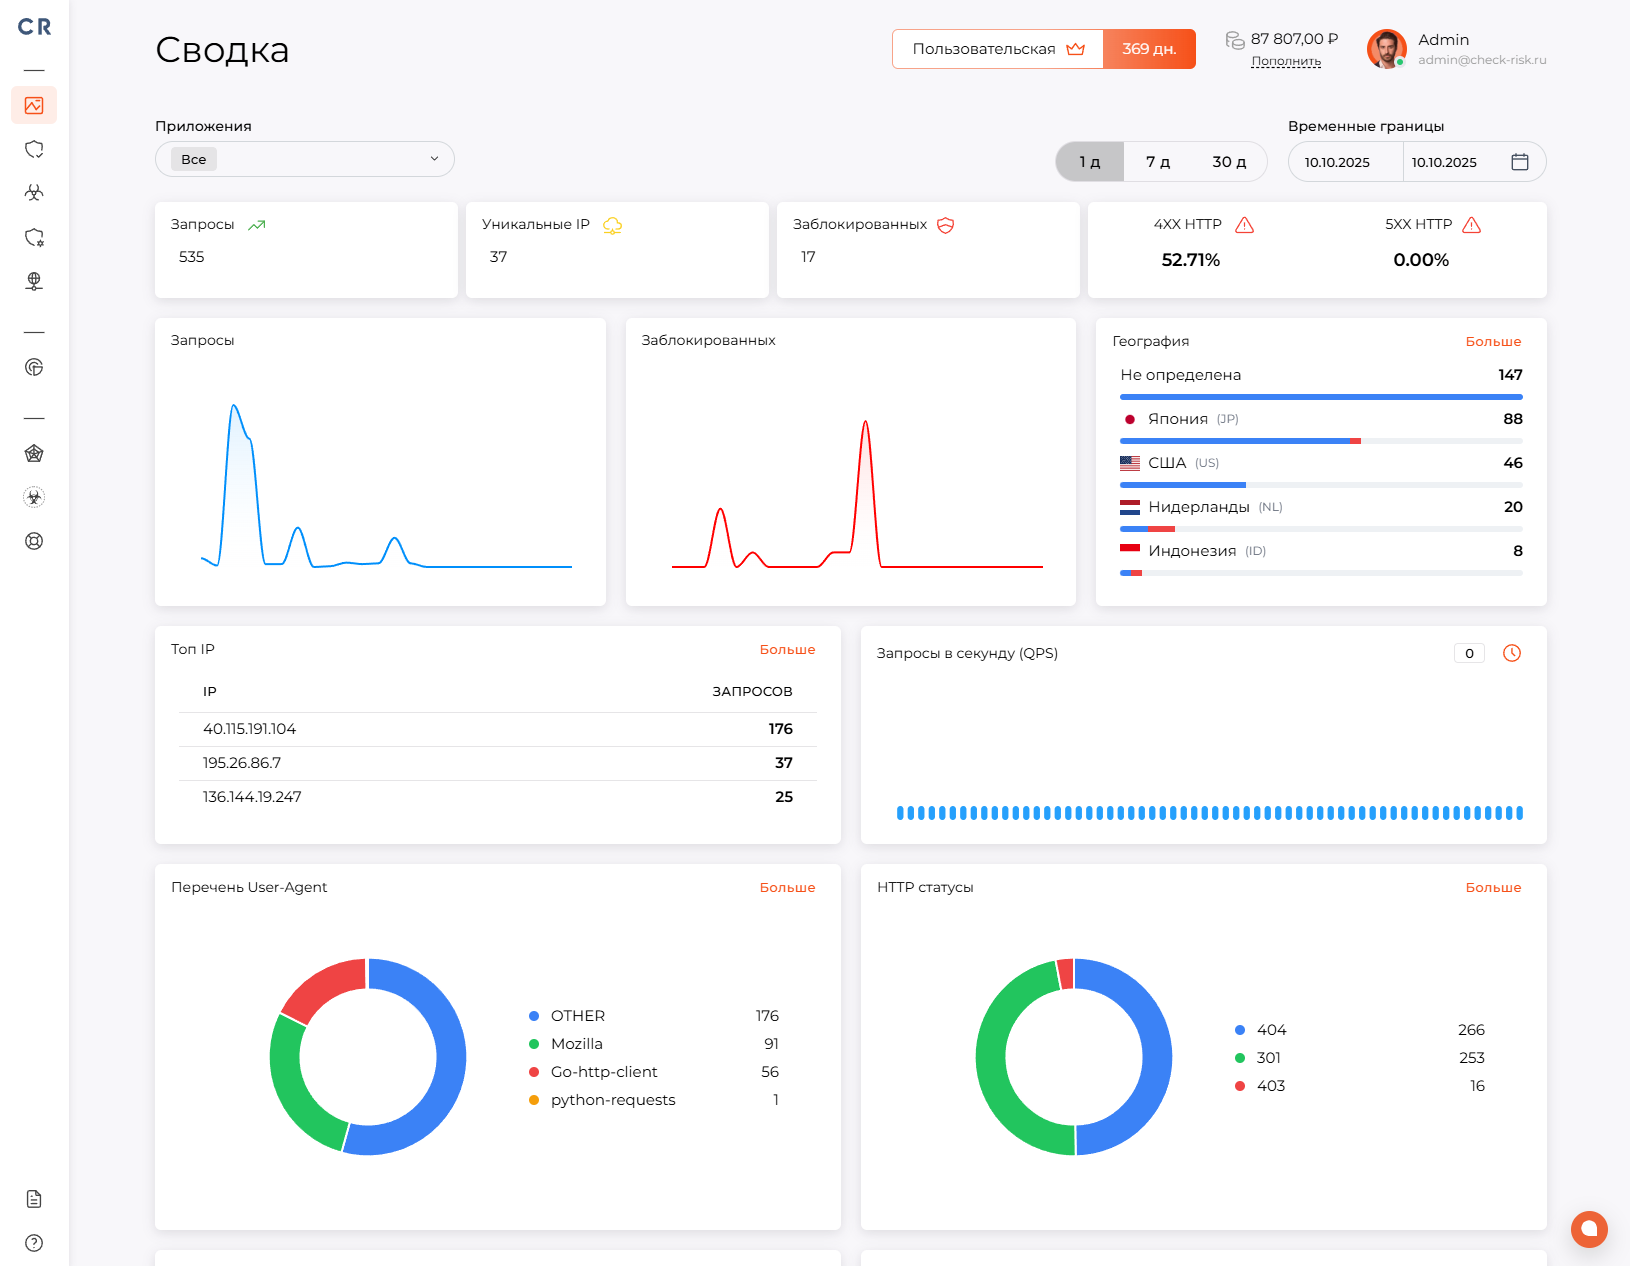 check-risk-waf/check-risk-waf
Cloud-based Web Application Firewall (WAF) providing L3/L7 protection against SQLi, XSS, DDoS, and bot attacks. Features AI assistant, anti-bot…
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security