syswarden
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
cloud-securityconfiguration-auditingdefensive-tools+4
382
duggytuxy/syswardenHost-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 eshlomo1/microsoft-sentinel-secops
SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
 defenxor/dsiem
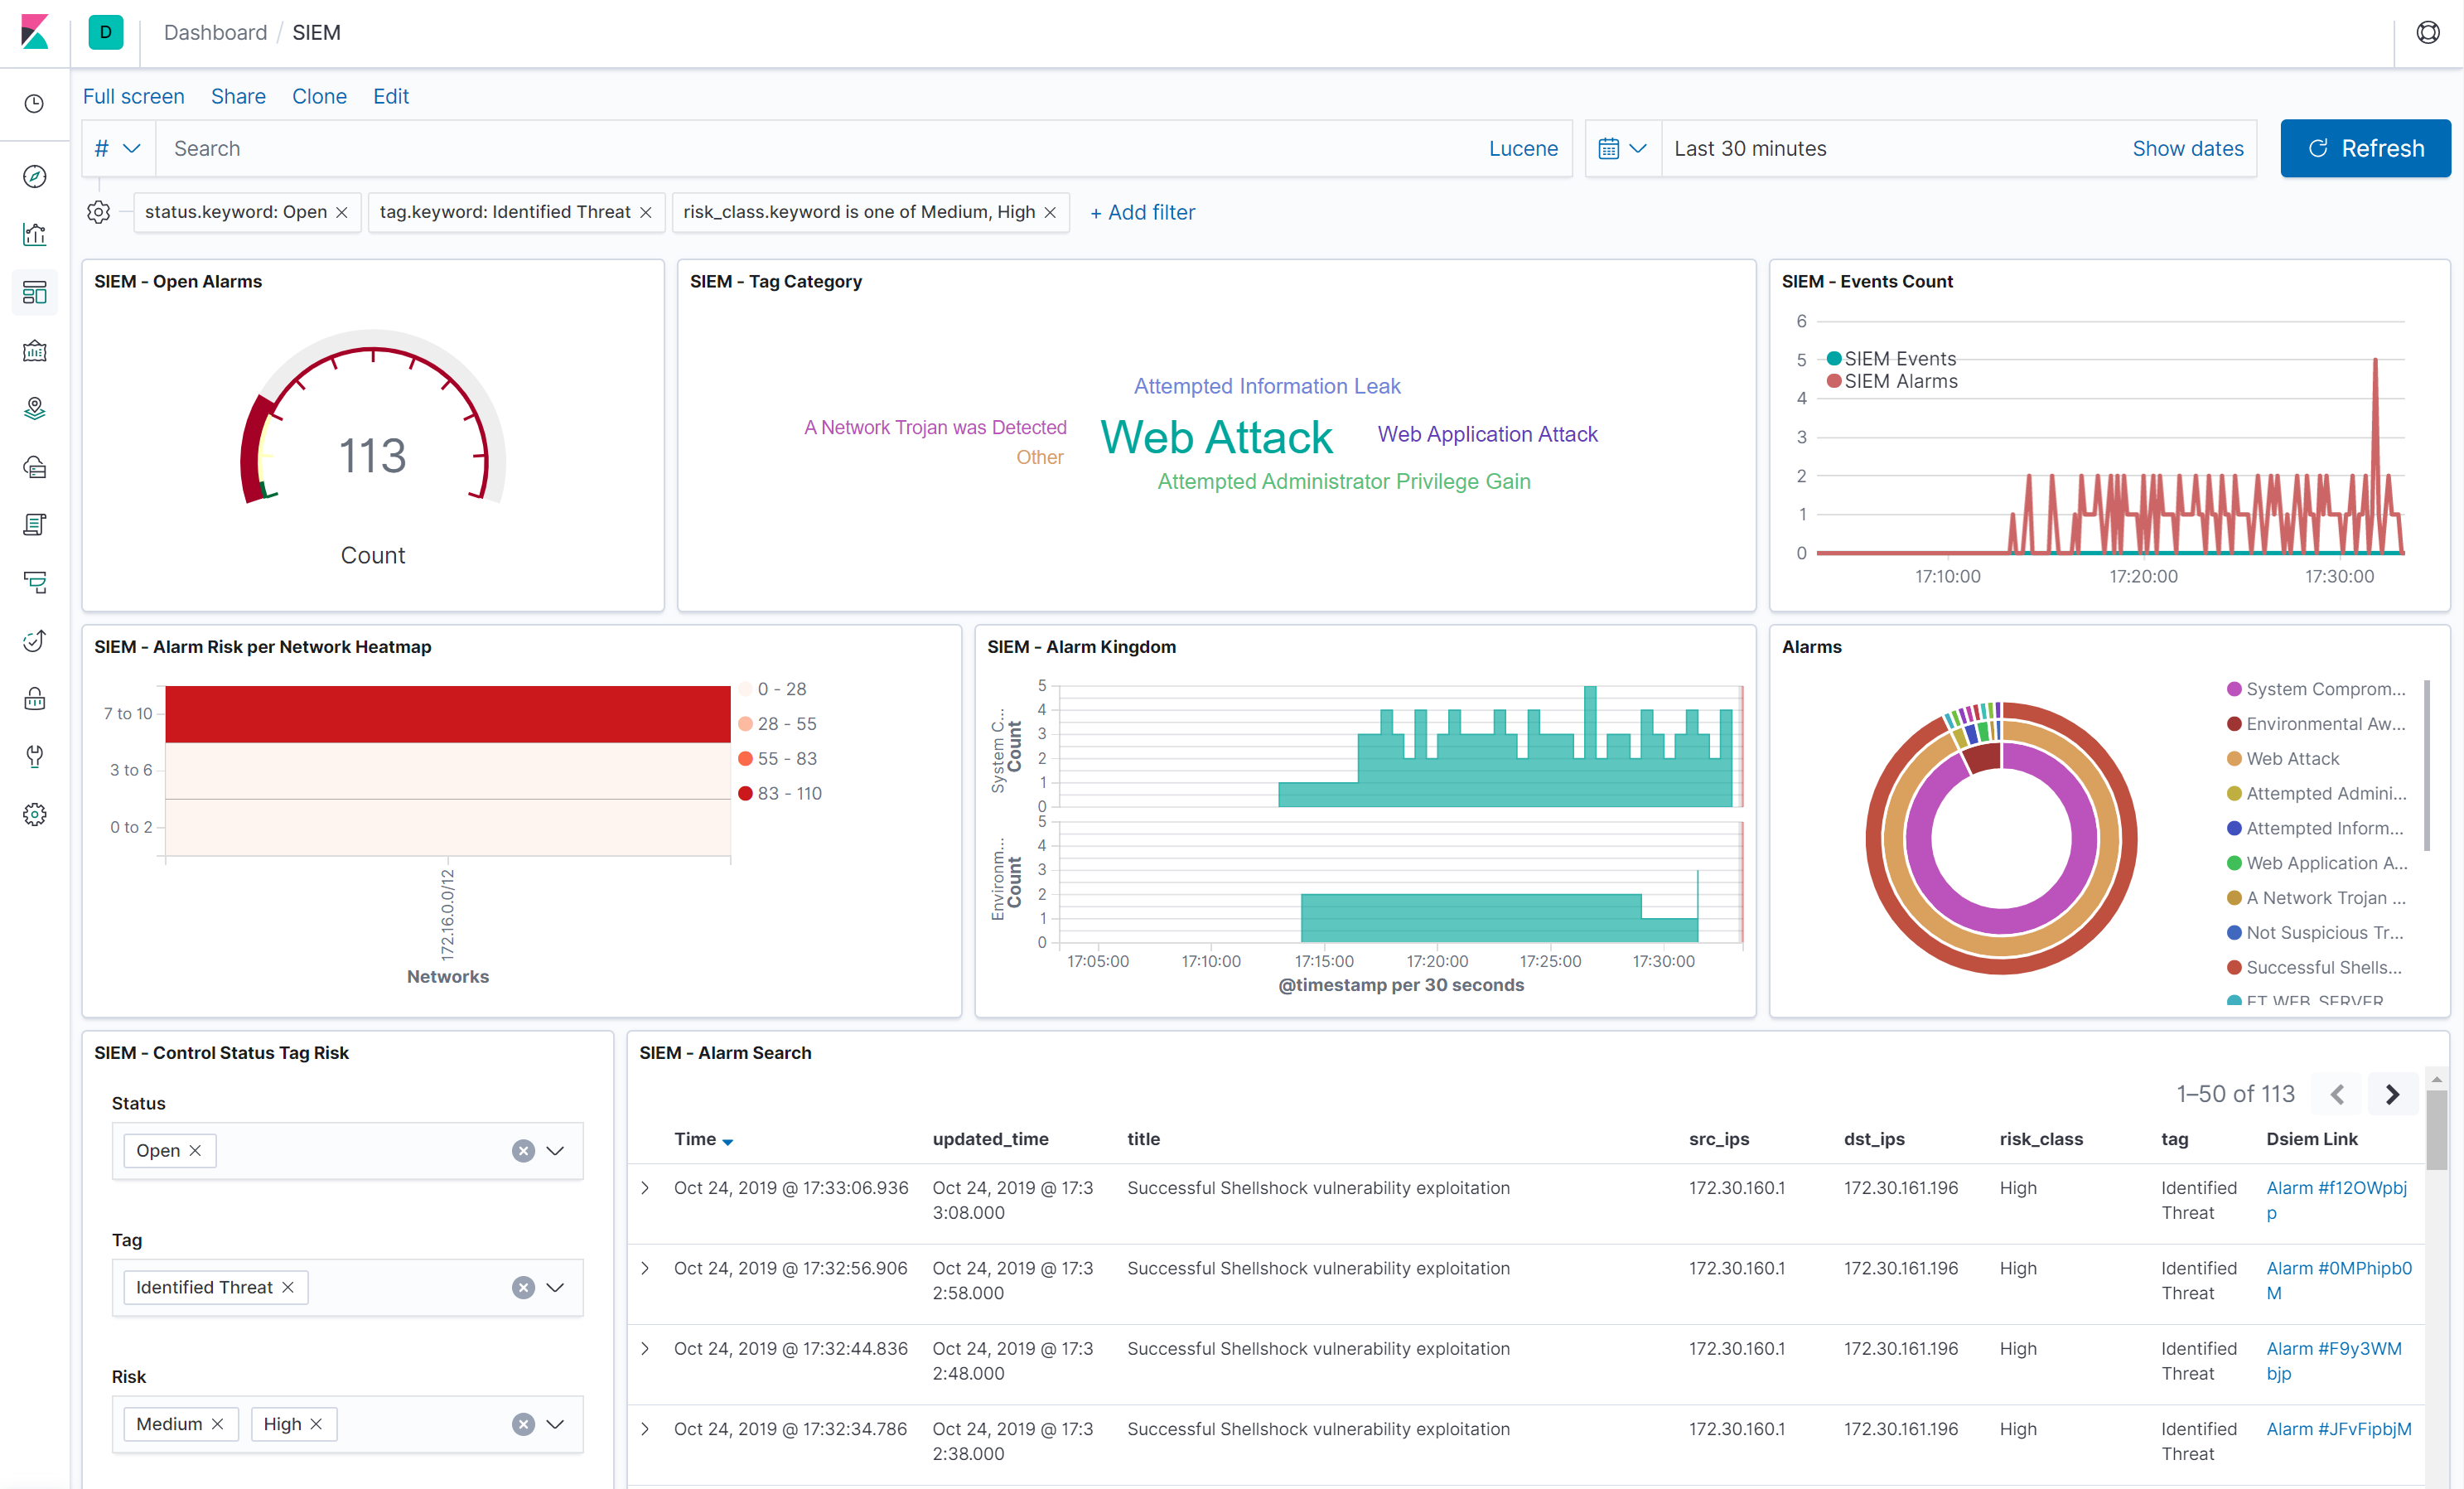
Security event correlation engine for ELK stack
 hybridbrothers/hunting-queries-detection-rules
The purpose of this repository is to share KQL queries to help identify security misconfigurations, hunt for specific patterns, or detect malicious…
 aleongx/kql_sentinel_cve-2025-21333
KQL para deteccion de CVE-2025-21333 en Sentinel