
reportly
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
cloud-securityidentity-access-managementincident-response+2
96
sap8899/reportlyAzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
 anrbn/gator
Modular GCP attack toolkit for offensive research, enabling reconnaissance, authentication manipulation, and exploitation of cloud functions,…
 404tk/cve-2022-46463
harbor unauthorized detection
 hazcod/claudleak
Hunt for AI coding artifacts containing secrets.
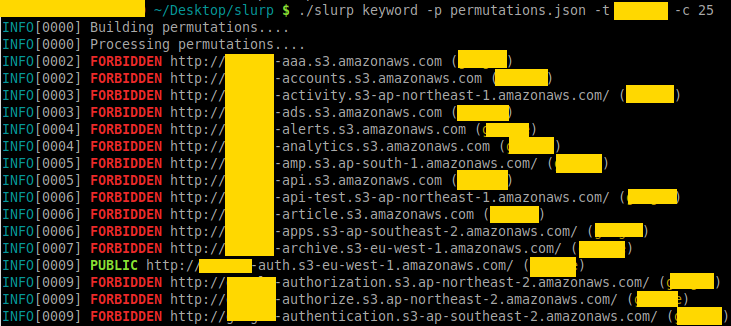
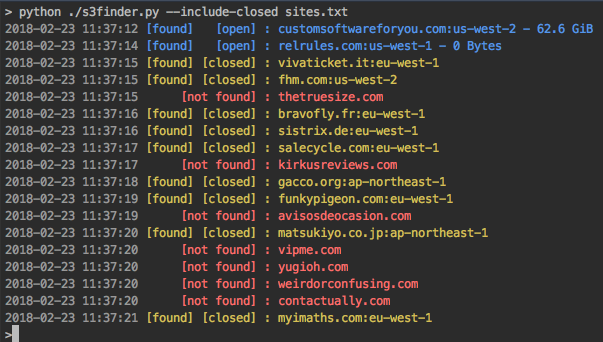 yehgdotnet/s3scanner
Scan for open S3 buckets and dump
 1n3/cloudhunter
Find unreferenced AWS S3 buckets which have CloudFront CNAME records pointing to them
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 halencarjunior/sss3
Automated S3 bucket security scanner that tests domain lists for publicly accessible buckets with listing permissions, exporting results for cloud…
 wearecloudar/s3-account-search
S3 Account Search
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
 yousseflahouifi/cloudpulse
SSL certificate-based reconnaissance engine for discovering AWS cloud assets, including IPs, subdomains, and domains, with active port scanning for…
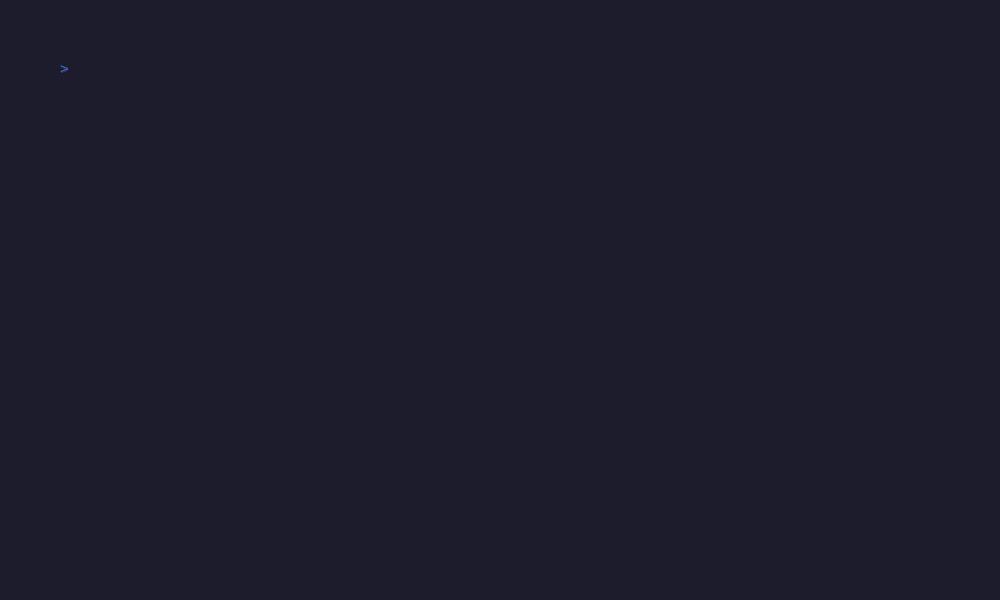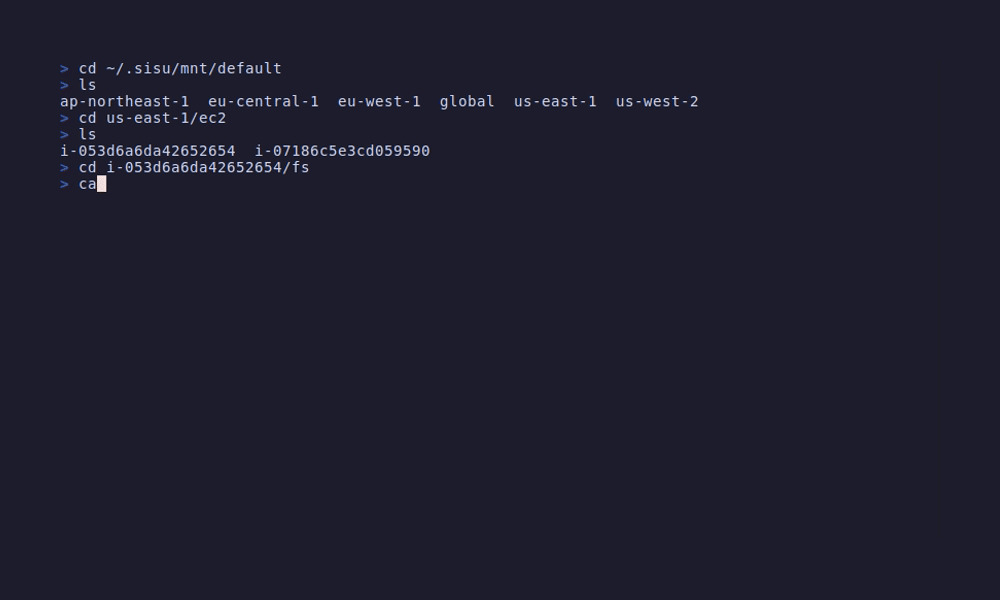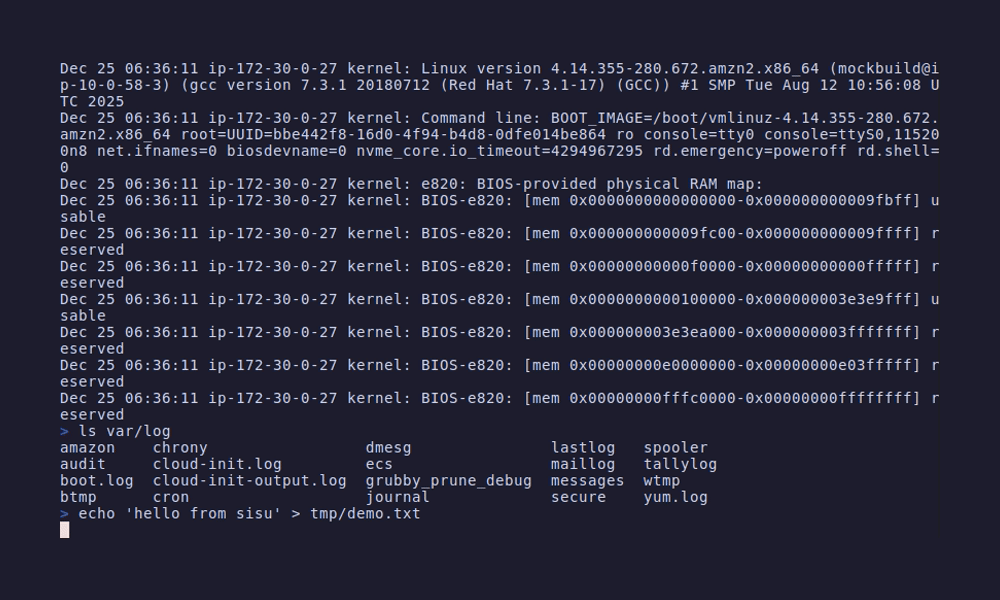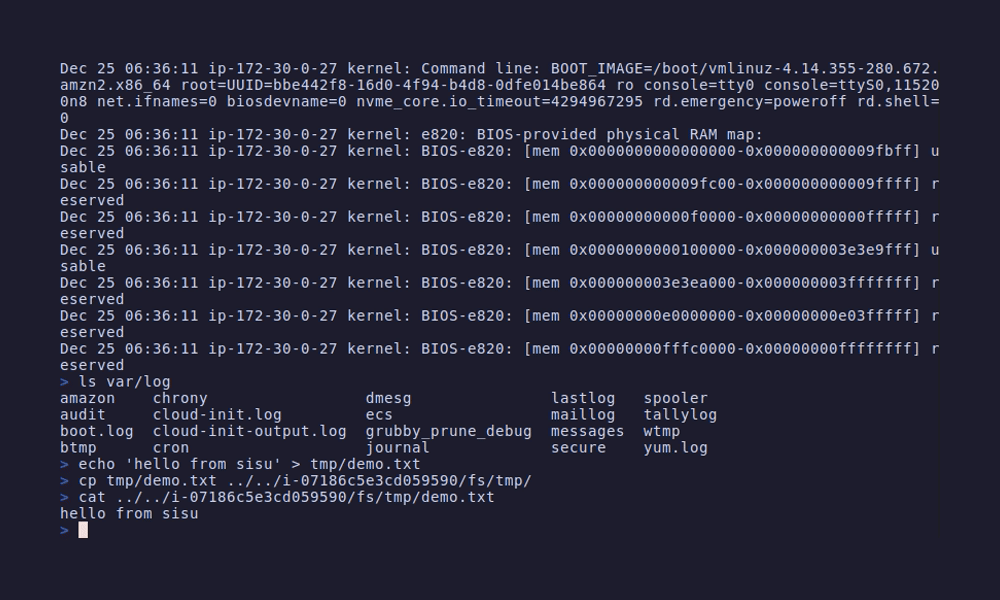 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
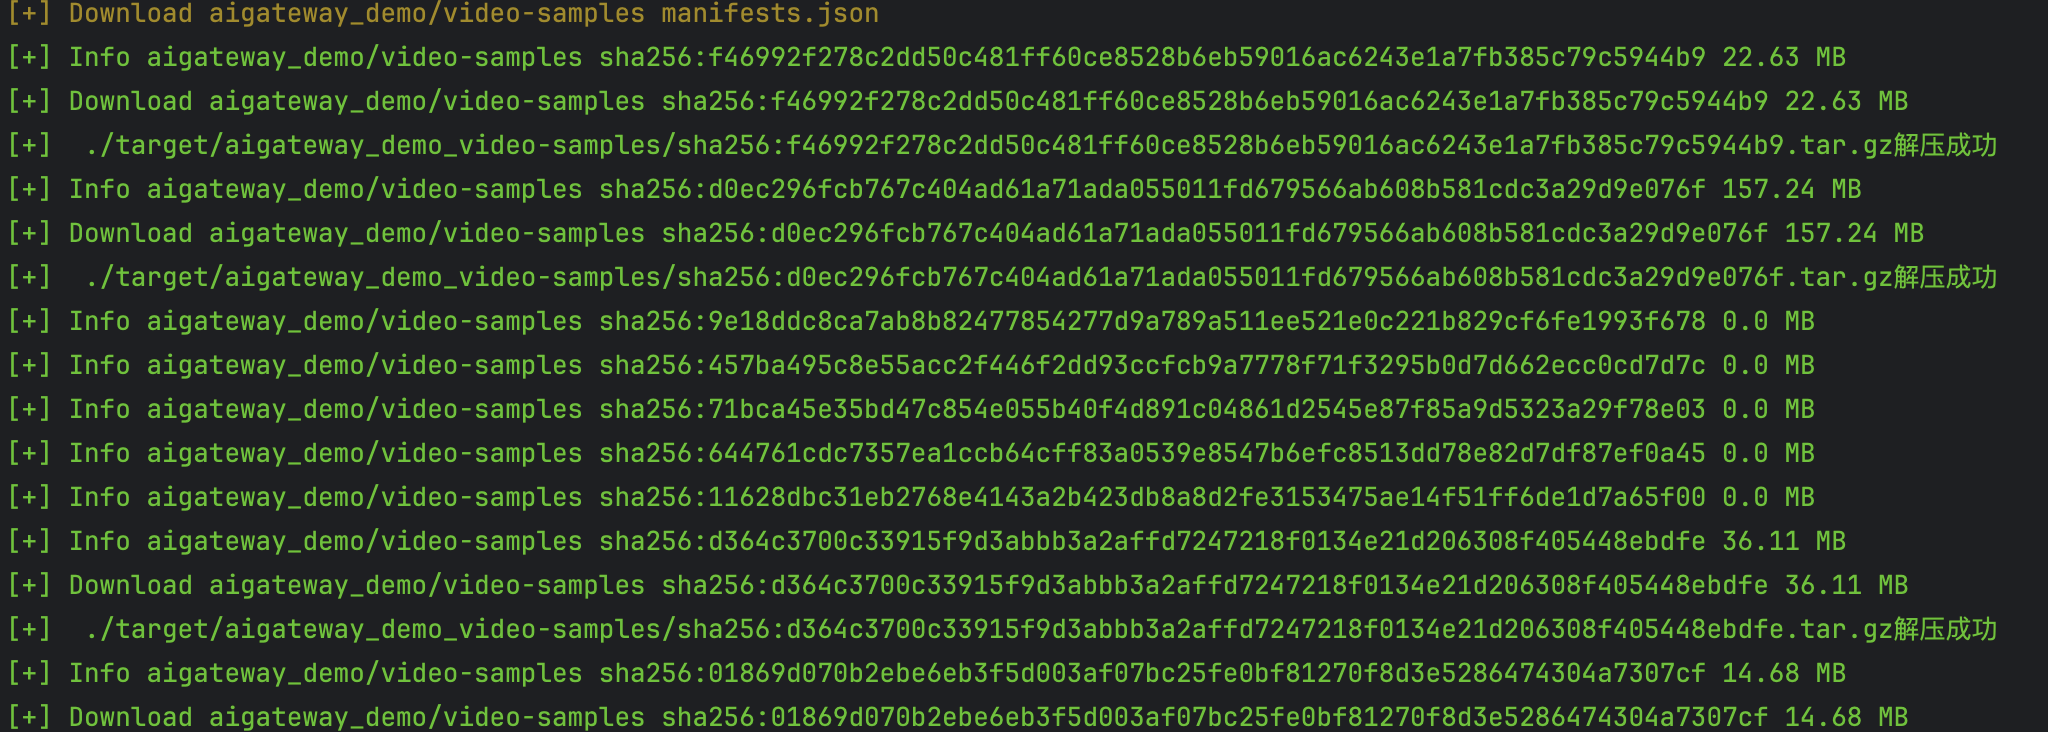 codesecurityteam/harbor
CVE-2022-46463 harbor公开镜像全自动下载脚本
 penteraio/cve-2022-22948
Scanner for CVE-2022-22948 an Information Disclosure in VMWare vCenter