
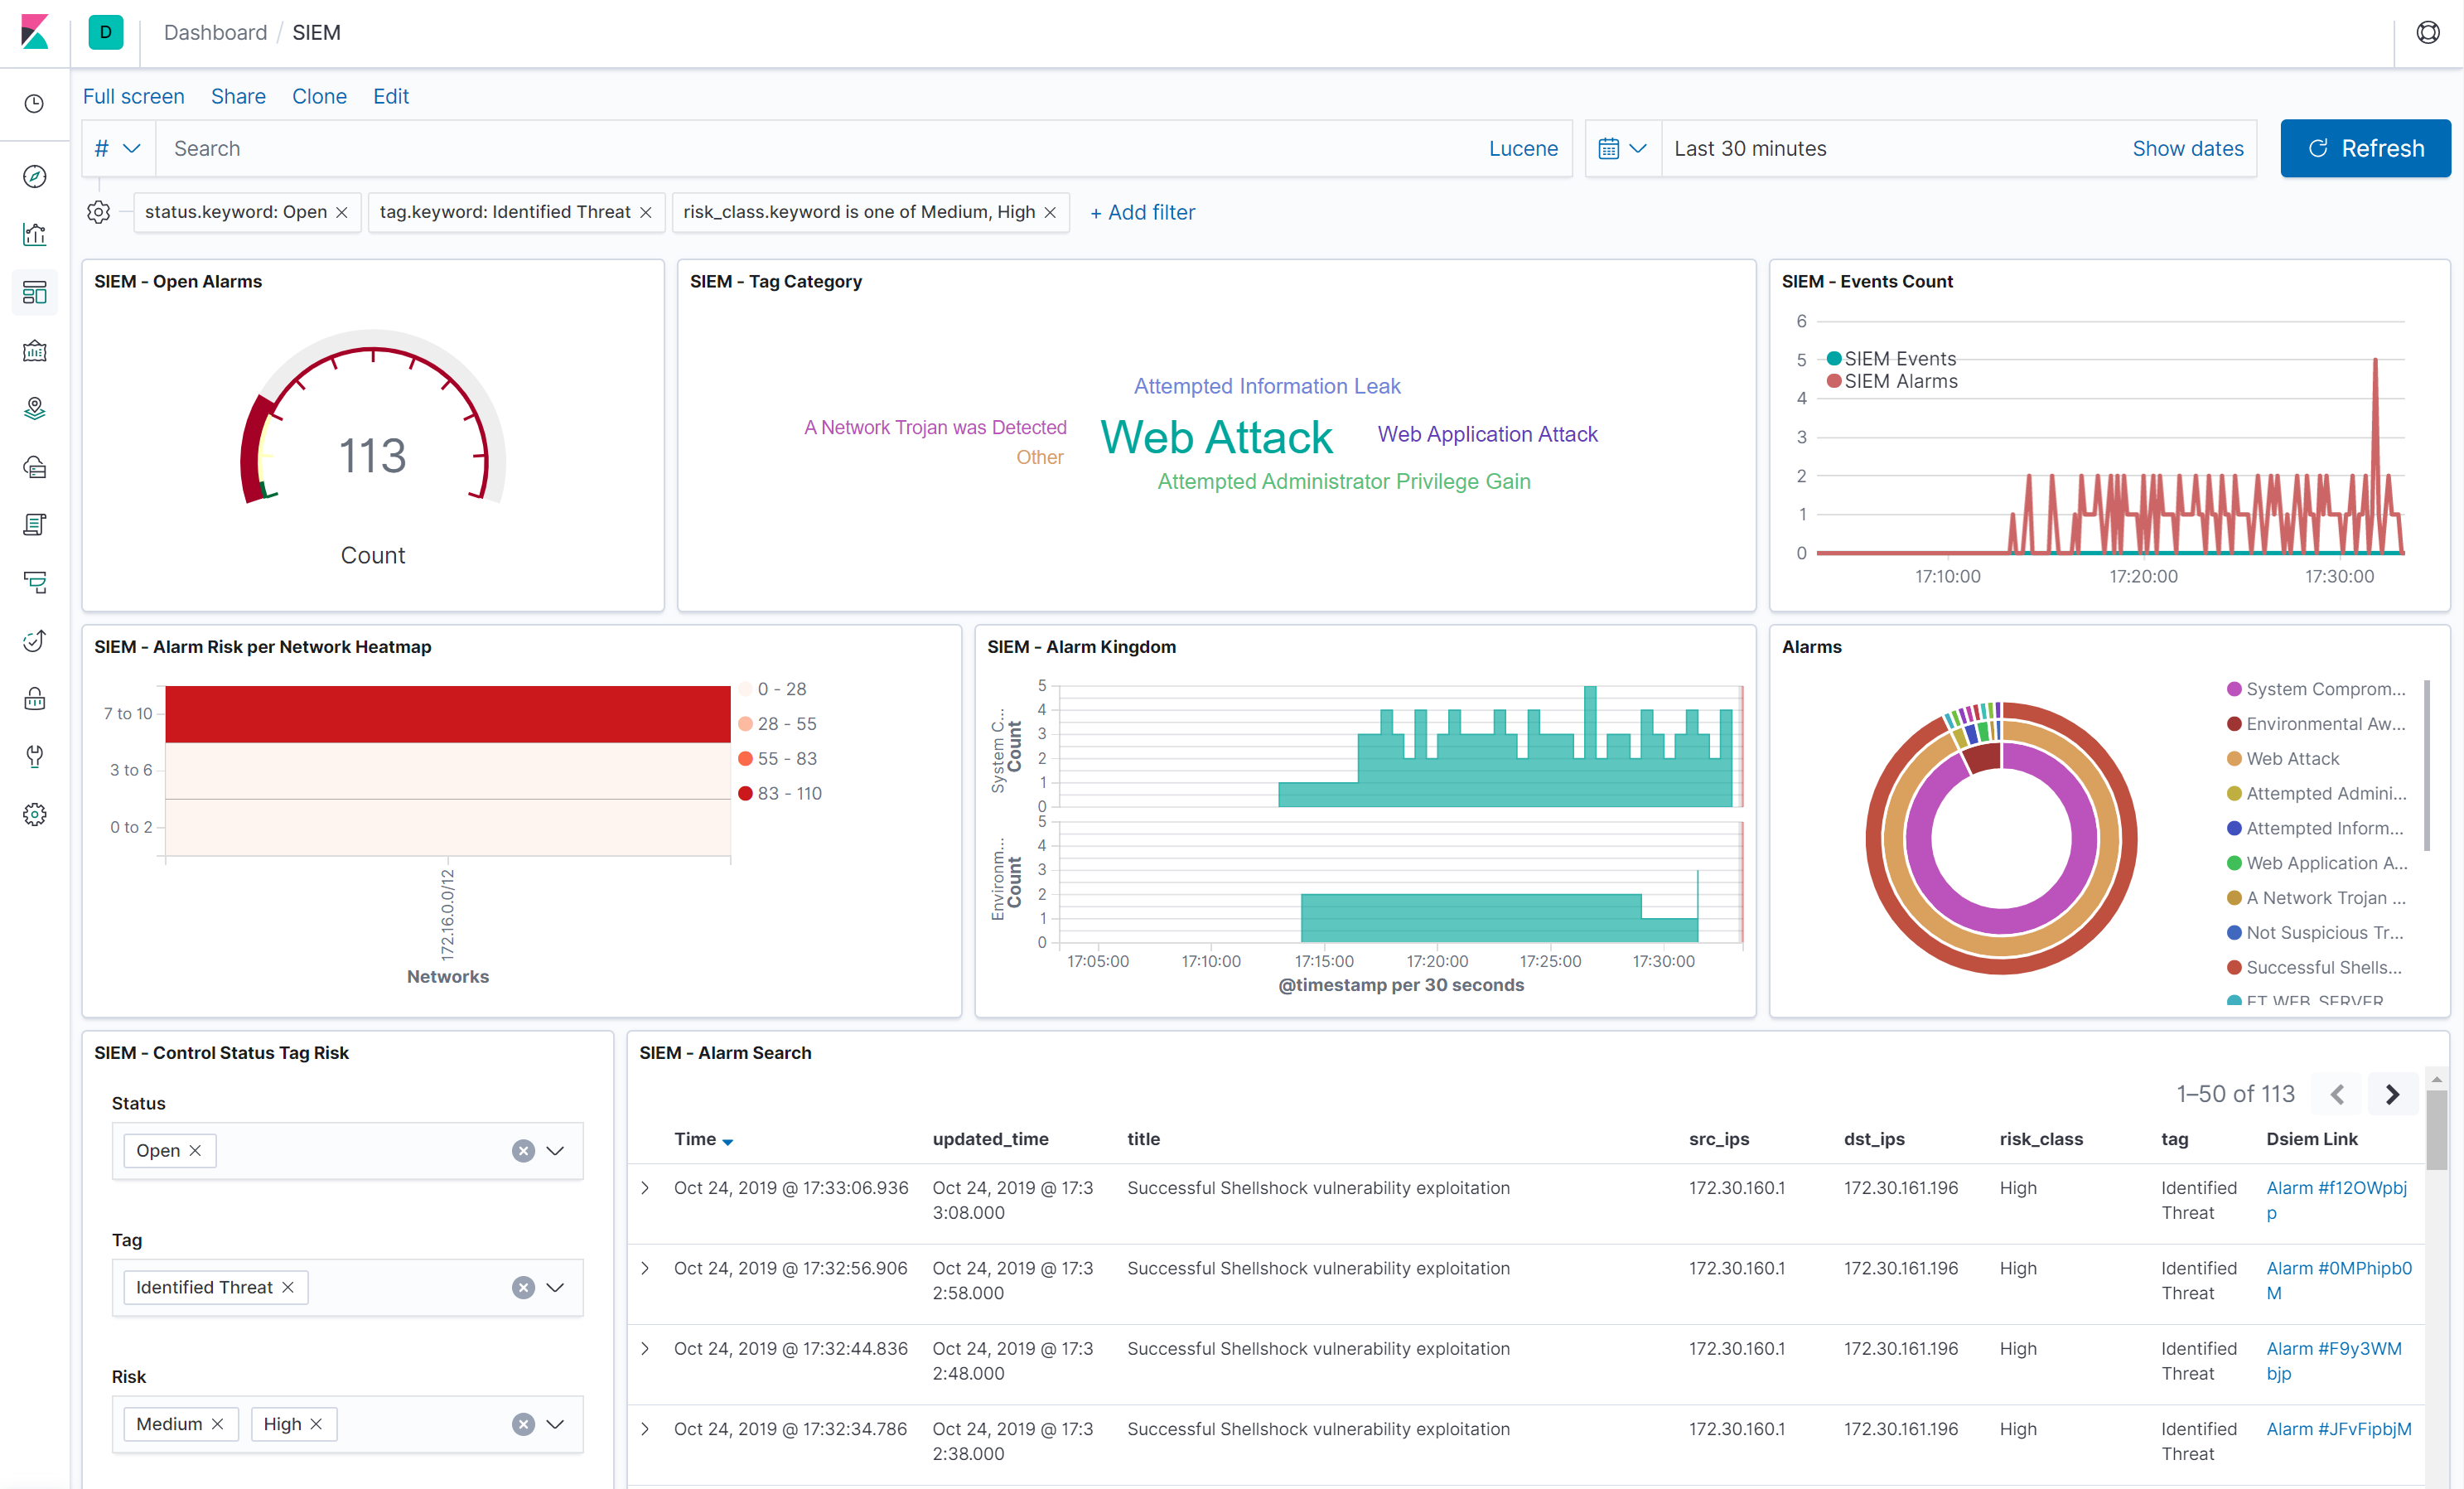
dsiem
 defenxor/dsiem
Security event correlation engine for ELK stack
cloud-securityincident-responseintrusion-detection+3
4462 years ago
defenxor/dsiemSecurity event correlation engine for ELK stack
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 owasp/serverless-top-10-project
OWASP Serverless Top 10
 vectra-ai-research/derf
Cloud-based attack emulation framework for executing offensive techniques and generating repeatable detection samples across AWS and GCP via a UI or…
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 ankur-katiyar/log4j-docker
Docker images and k8s YAMLs for Log4j Vulnerability POC (Log4j (CVE-2021-44228 RCE Vulnerability)
 4armed/cve-2023-5044
Go-based proof-of-concept exploit for CVE-2023-5044 in ingress-nginx, enabling authenticated remote command execution by creating crafted Kubernetes…
 alexzorin/cve-2017-2636-el
Ansible role for workaround for CVE-2017-2636 (Red Hat) - https://access.redhat.com/security/cve/CVE-2017-2636
 biitts/cve-2026-54917-seaweedfs-cross-bucket-traversal
PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
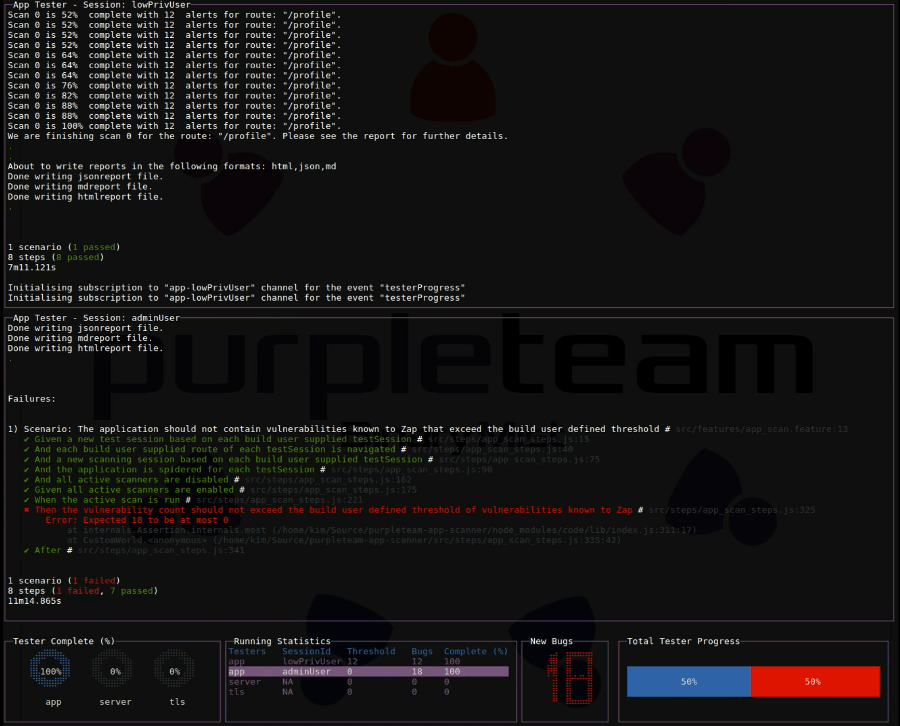 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 kovachvl/cve-2026-54356
Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…