
SnaffPoint
 nheiniger/snaffpoint
A tool for pointesters to find candies in SharePoint
cloud-securityinformation-gatheringpenetration-testing+3
2883 years ago
nheiniger/snaffpointA tool for pointesters to find candies in SharePoint
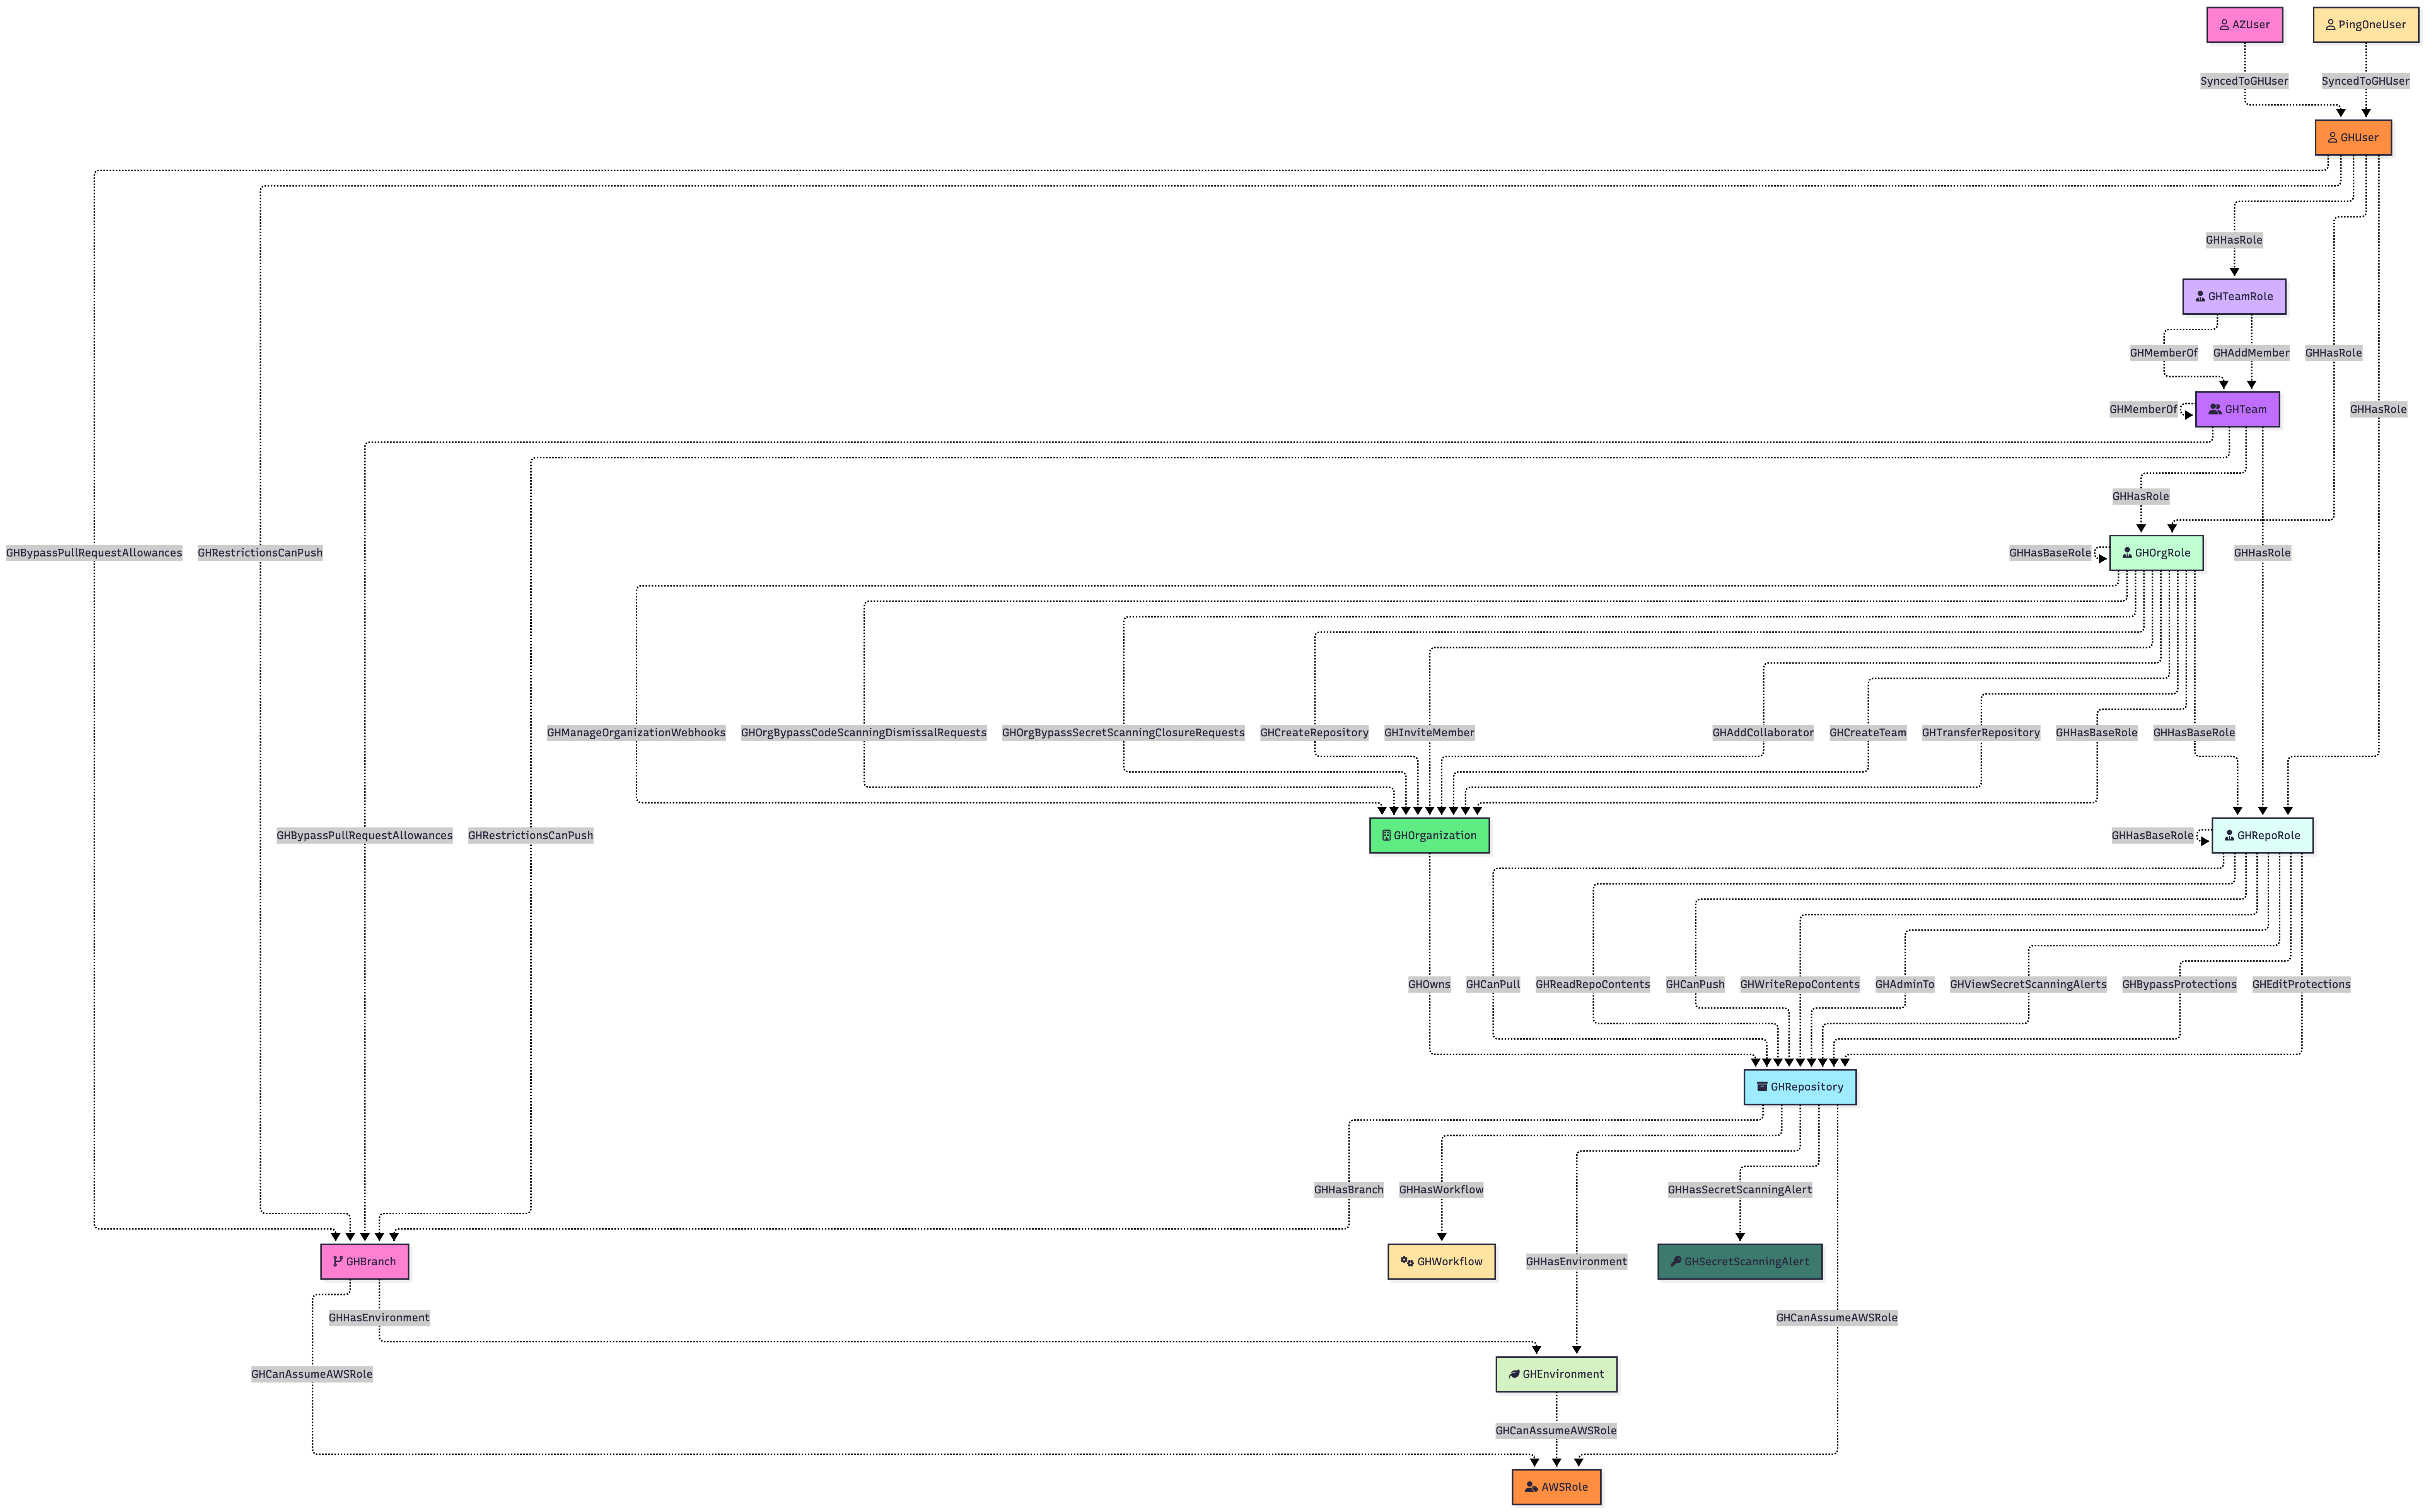 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 0xsearches/sandcastle
🏰 A Python script for AWS S3 bucket enumeration.
 synacktiv/mindmaps
Azure mindmap for penetration tests
 blacklanternsecurity/offensive-azure
Collection of offensive tools targeting Microsoft Azure
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 professionallyevil/harpoon
A collection of scripts, and tips and tricks for hacking k8s clusters and containers.
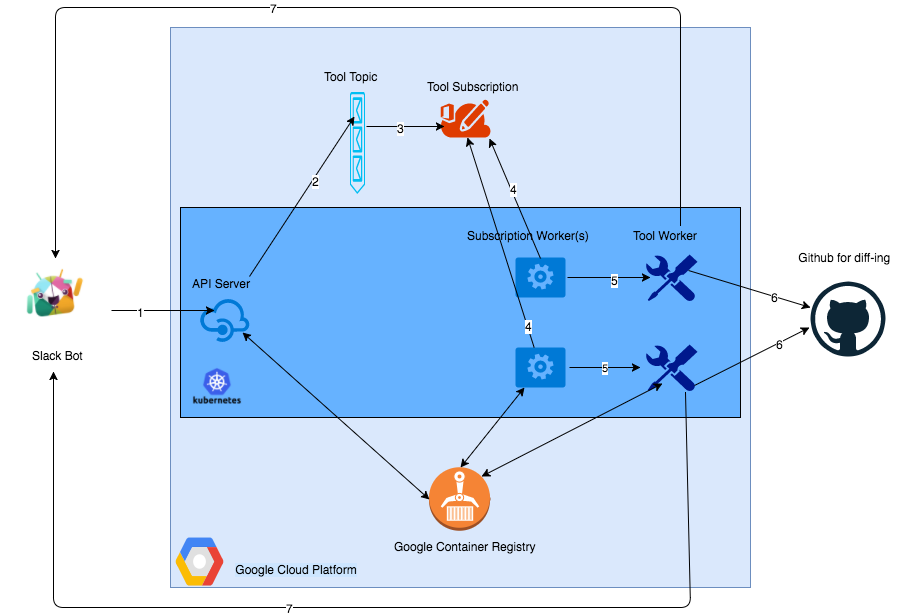 anshumanbh/kubebot
A security testing Slackbot built with a Kubernetes backend on the Google Cloud Platform
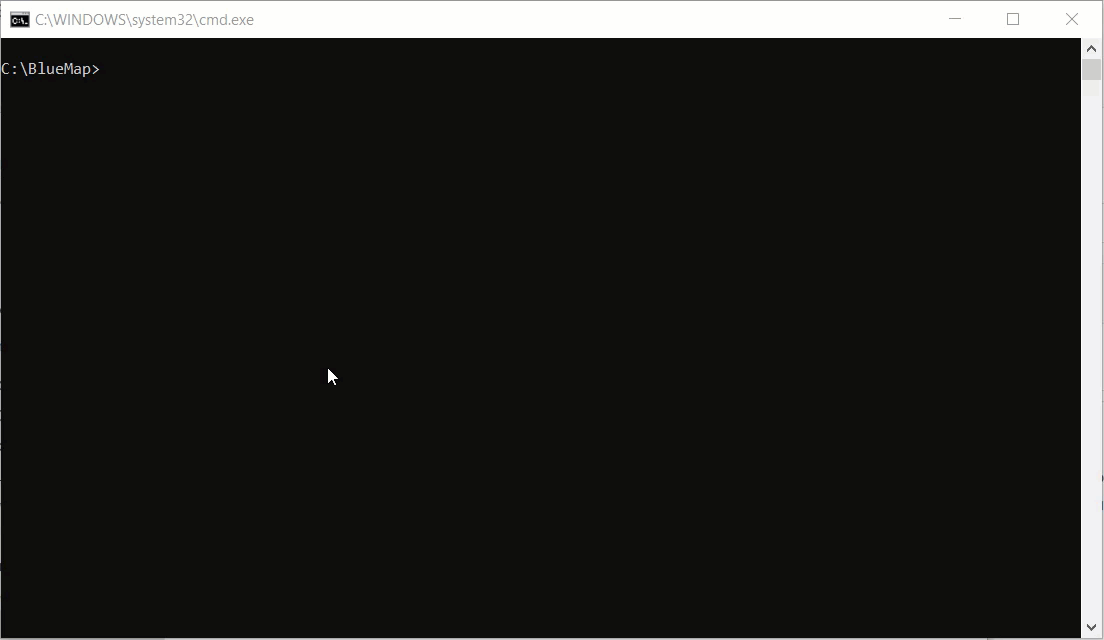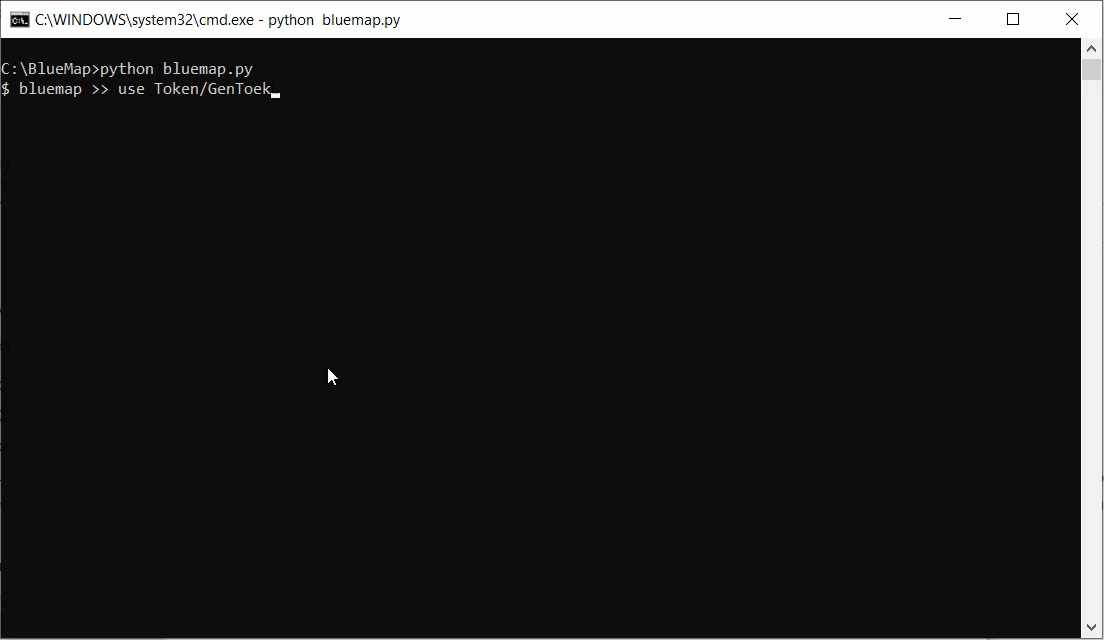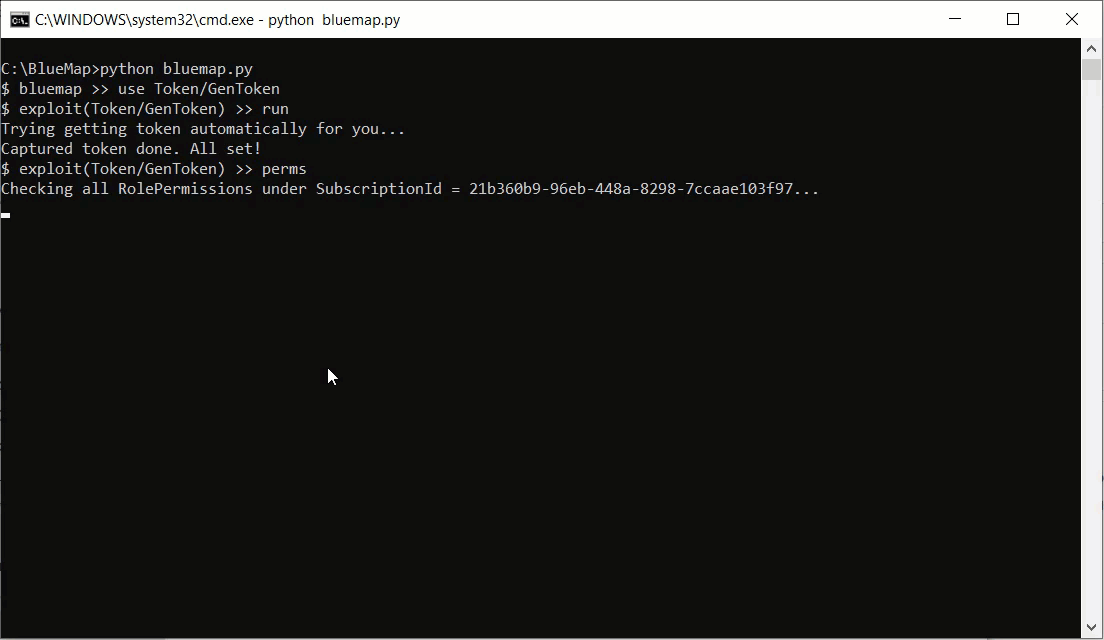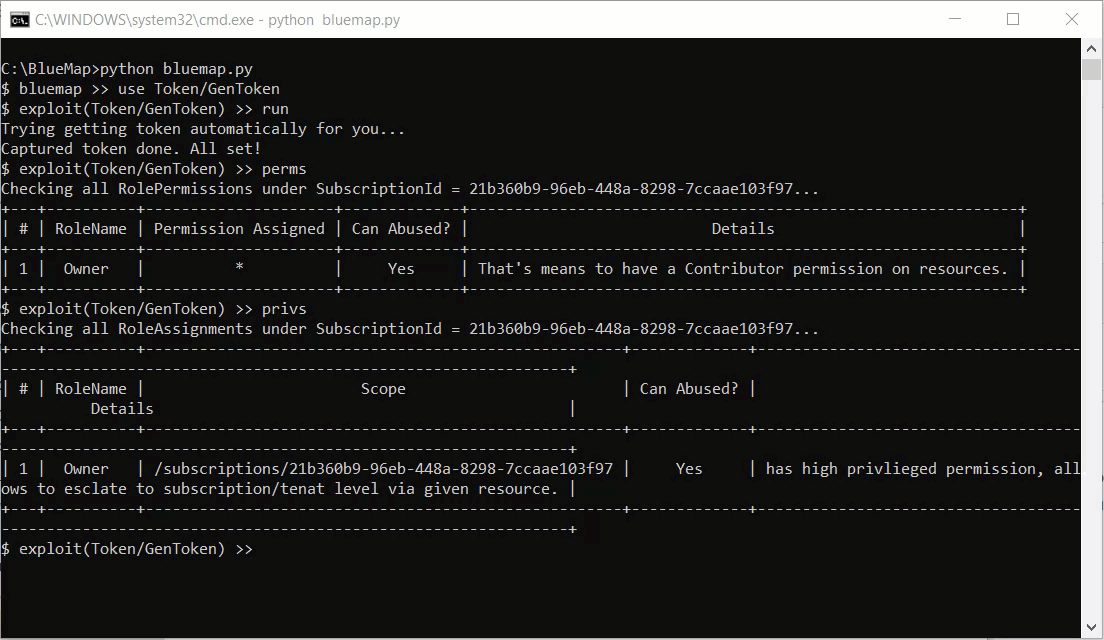 sikretalabs/bluemap
A Azure Exploitation Toolkit for Red Team & Pentesters
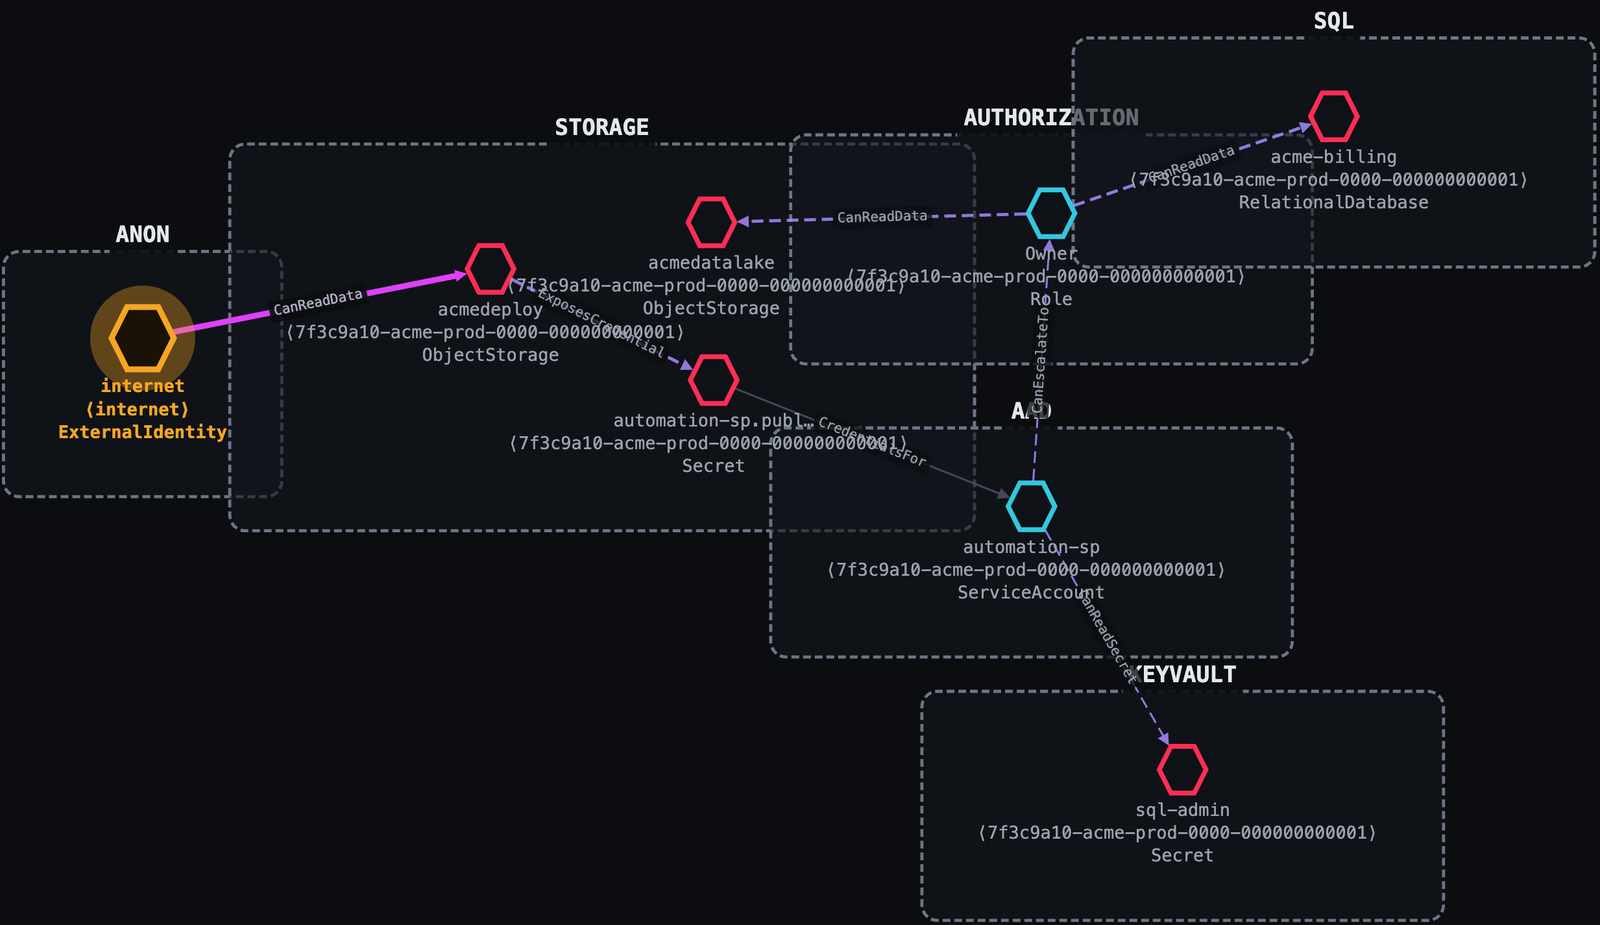 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 404tk/cloudtoolkit
Authorized cloud adversary simulation and validation toolkit
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.