

ws4-secure-design-agentic-systems
 cosai-oasis/ws4-secure-design-agentic-systems
Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
ai-securitycloud-securitycurated-resources+6
cosai-oasis/ws4-secure-design-agentic-systemsRepository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 microsoft/igvm
Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…
 mahfuzreham/litespeed-cpanel-cve-2026-54420-fix
Defensive remediation and auditing toolkit for CVE-2026-54420 in LiteSpeed cPanel Plugin. Automates patching, detects suspicious symlinks, hunts…
 george0papasotiriou/cve-2026-21008-kubernetes-service-account-token-mounted-in-hostpath
Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…
 resellnom/litespeed-cpanel-cve-2026-54420-fix
Defensive mitigation and auditing toolkit for CVE-2026-54420 in LiteSpeed cPanel plugin, providing symlink detection, IOC hunting, and remediation…
 nu11secur1ty/kali-linux-docker
kali-linux-docker
 j81blog/adc-19781
Check ADC for CVE-2019-19781
 hahwul/s3reverse
The format of various s3 buckets is convert in one format. for bugbounty and security testing.
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 rocket-panda/cve-2025-9074
Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…
 fevar54/poc_cve-2025-29943_write-what-where-condition
Proof-of-concept for CVE-2025-29943 exploiting an undocumented stack engine bit in AMD Zen CPUs to corrupt the stack pointer in SEV-SNP protected…
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
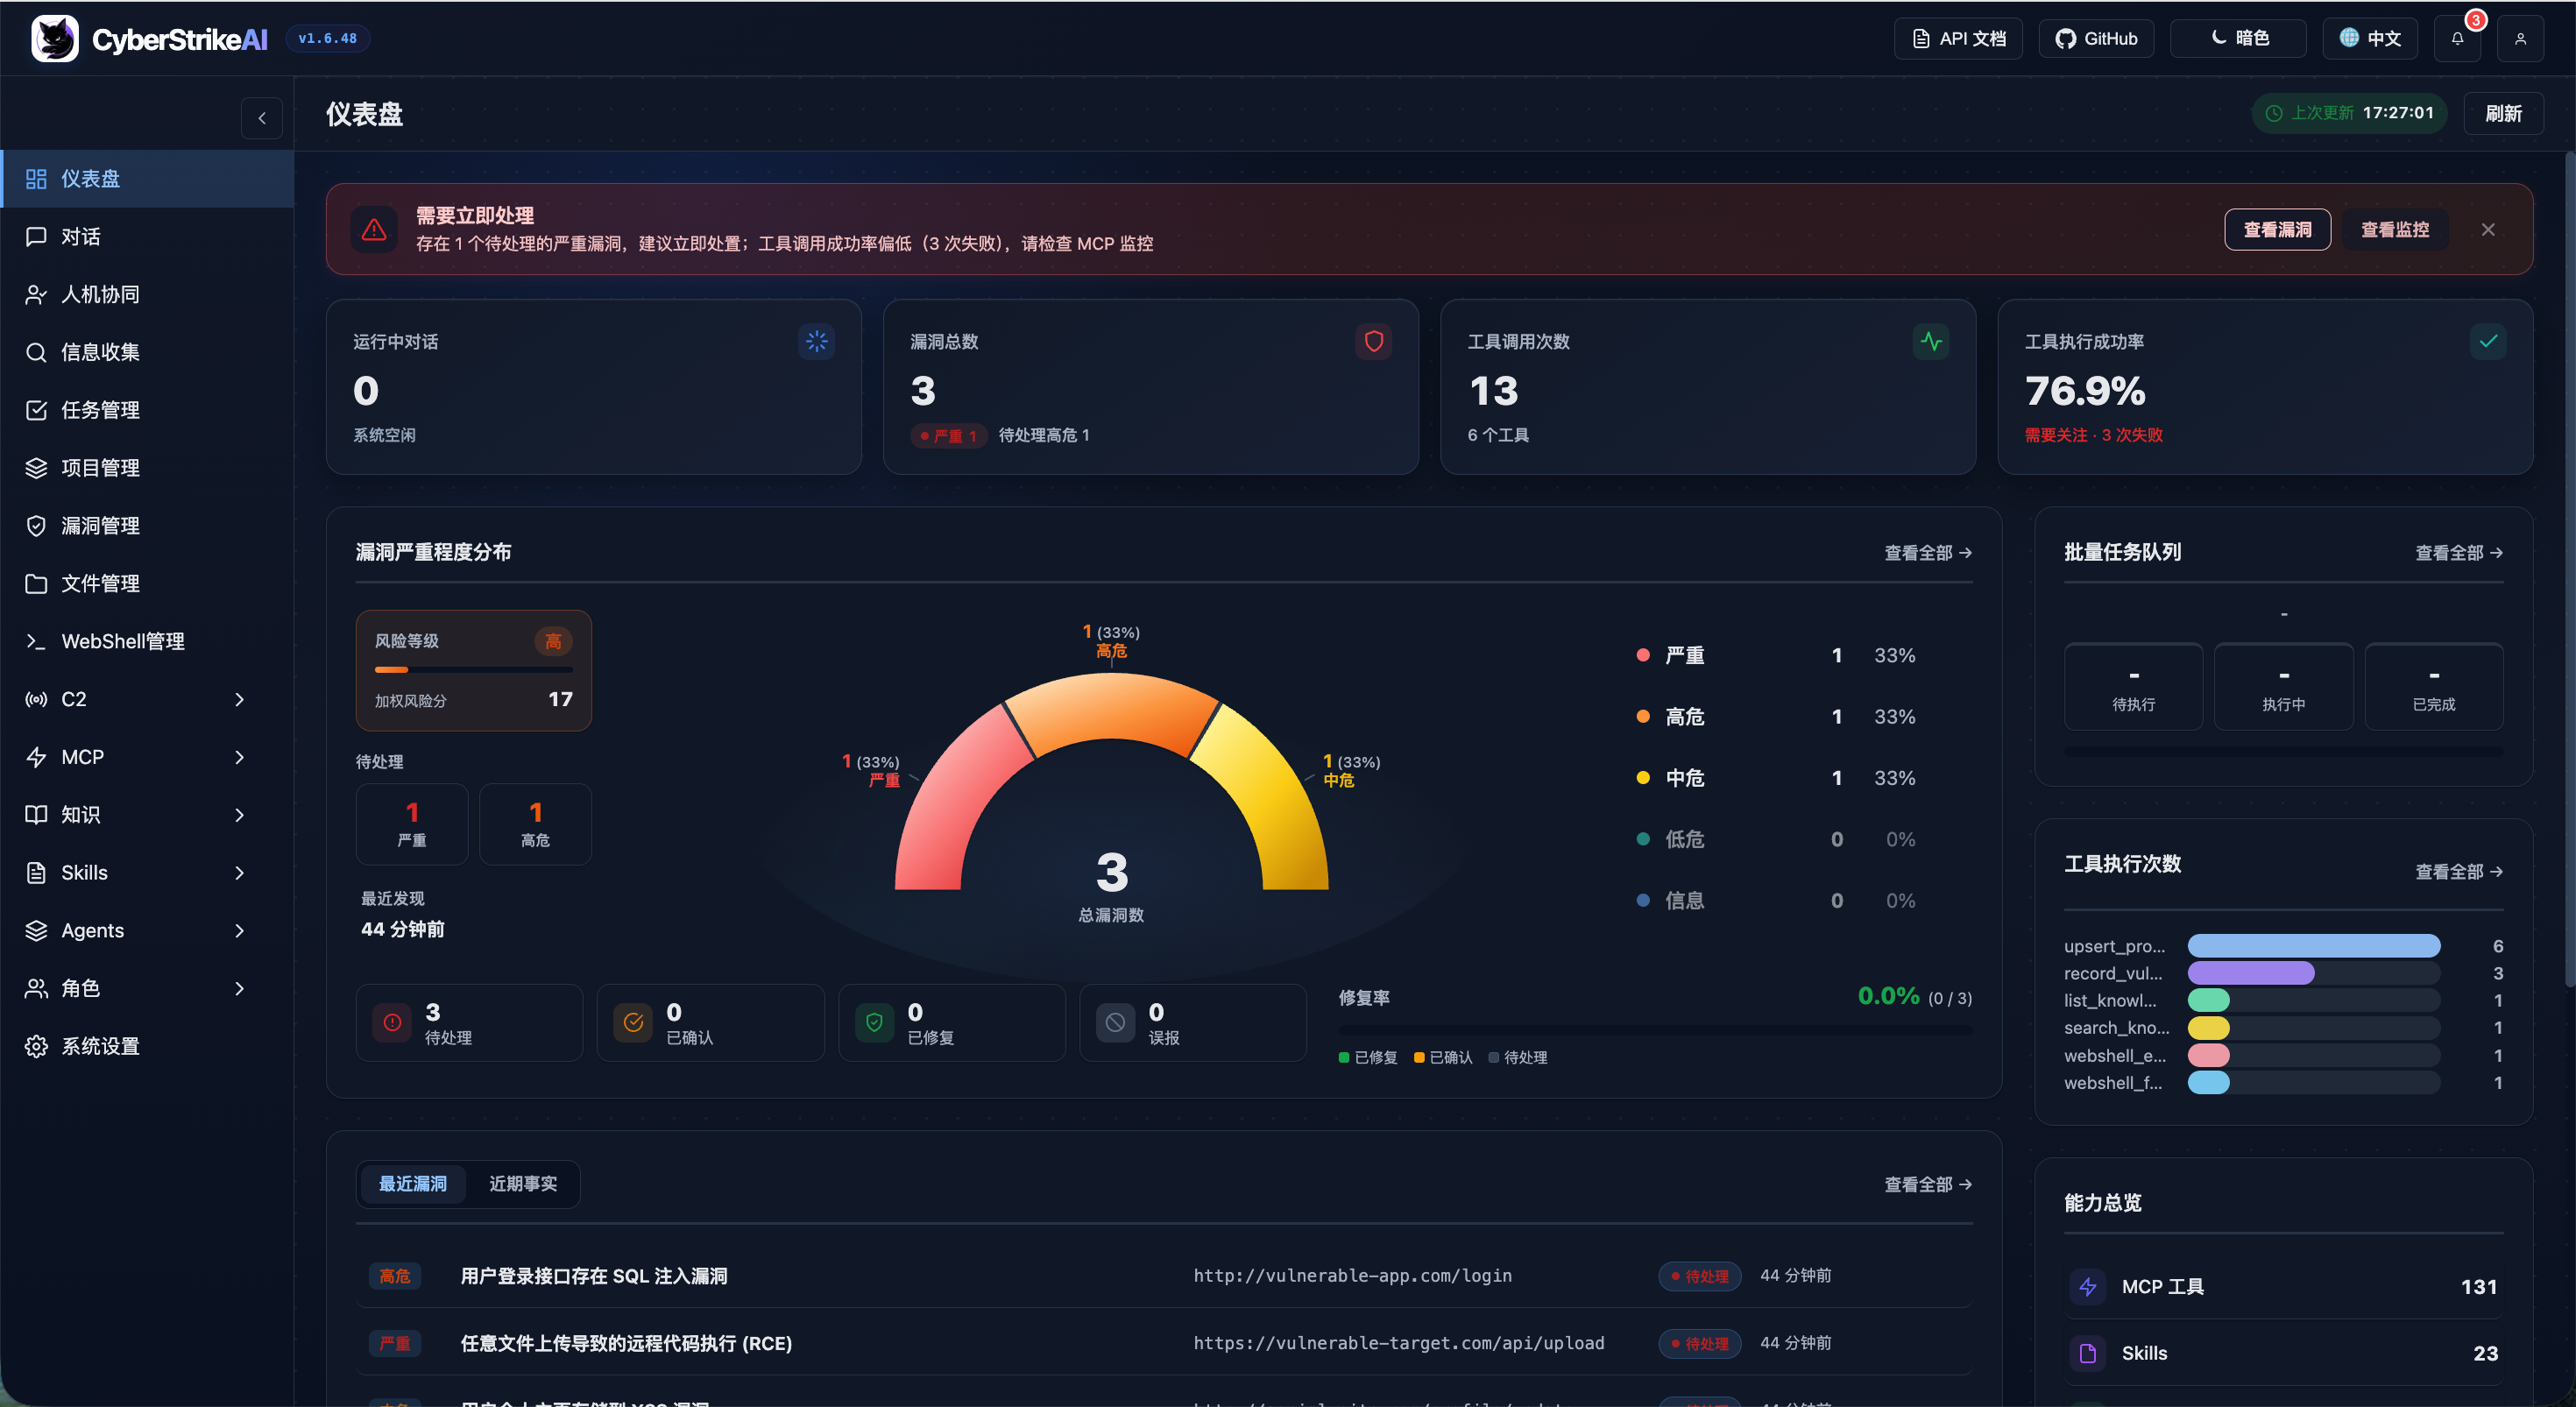 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
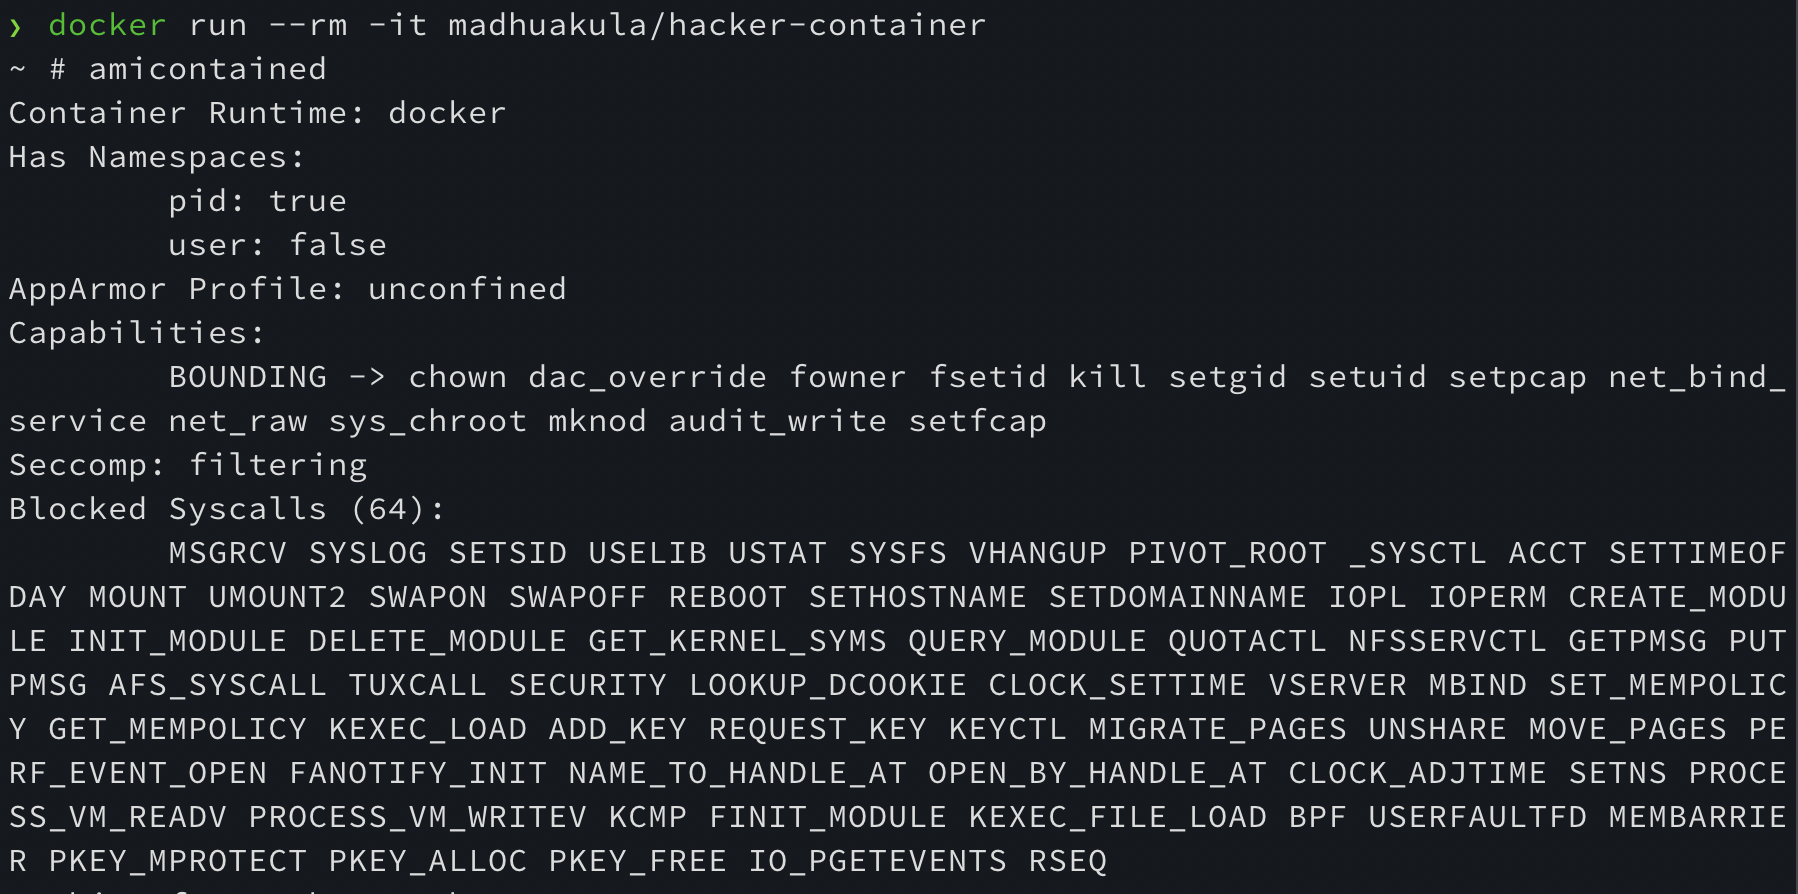 madhuakula/hacker-container
The Swiss Army Container for Cloud Native Security. Container with all the list of useful tools/commands while hacking and securing Containers,…
 hakaioffsec/ingressnightmare-poc
This is a PoC code to exploit the IngressNightmare vulnerabilities (CVE-2025-1097, CVE-2025-1098, CVE-2025-24514, and CVE-2025-1974).