
CVE-2026-7791
 benzamir/cve-2026-7791
Local Privilege Escalation in Amazon WorkSpaces via TOCTOU and Arbitrary File Write
binary-exploitationcloud-securityexploitation+2
1
benzamir/cve-2026-7791Local Privilege Escalation in Amazon WorkSpaces via TOCTOU and Arbitrary File Write
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 oscerd/cve-2026-40564
CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 i3r1h0n/ingressnightterror
My view on IngressNightmare vulnerability (CVE-2025-1974)
 imohammed28/cve-2024-10220-test
Kubernetes gitRepo volume vulnerability (CVE-2024-10220) exploit for controlled HPC security research, demonstrating arbitrary command execution on…
 istenrot/centos-dirty-cow-ansible
Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 dviejopomata/cve-2020-8554
Proof-of-concept exploit for CVE-2020-8554, demonstrating Kubernetes service externalIP manipulation to achieve man-in-the-middle attacks on cluster…
 f88/ghostbusters15
Playbooks 'Fix for CVE-2015-0235(GHOST)' running on Ansible
 peterthomasawen/opensslupgrade1.1.1q-ubuntu
A script to change OpenSSL versions on Ubuntu to 1.1.1q to protect against CVE-2022-2097.
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API
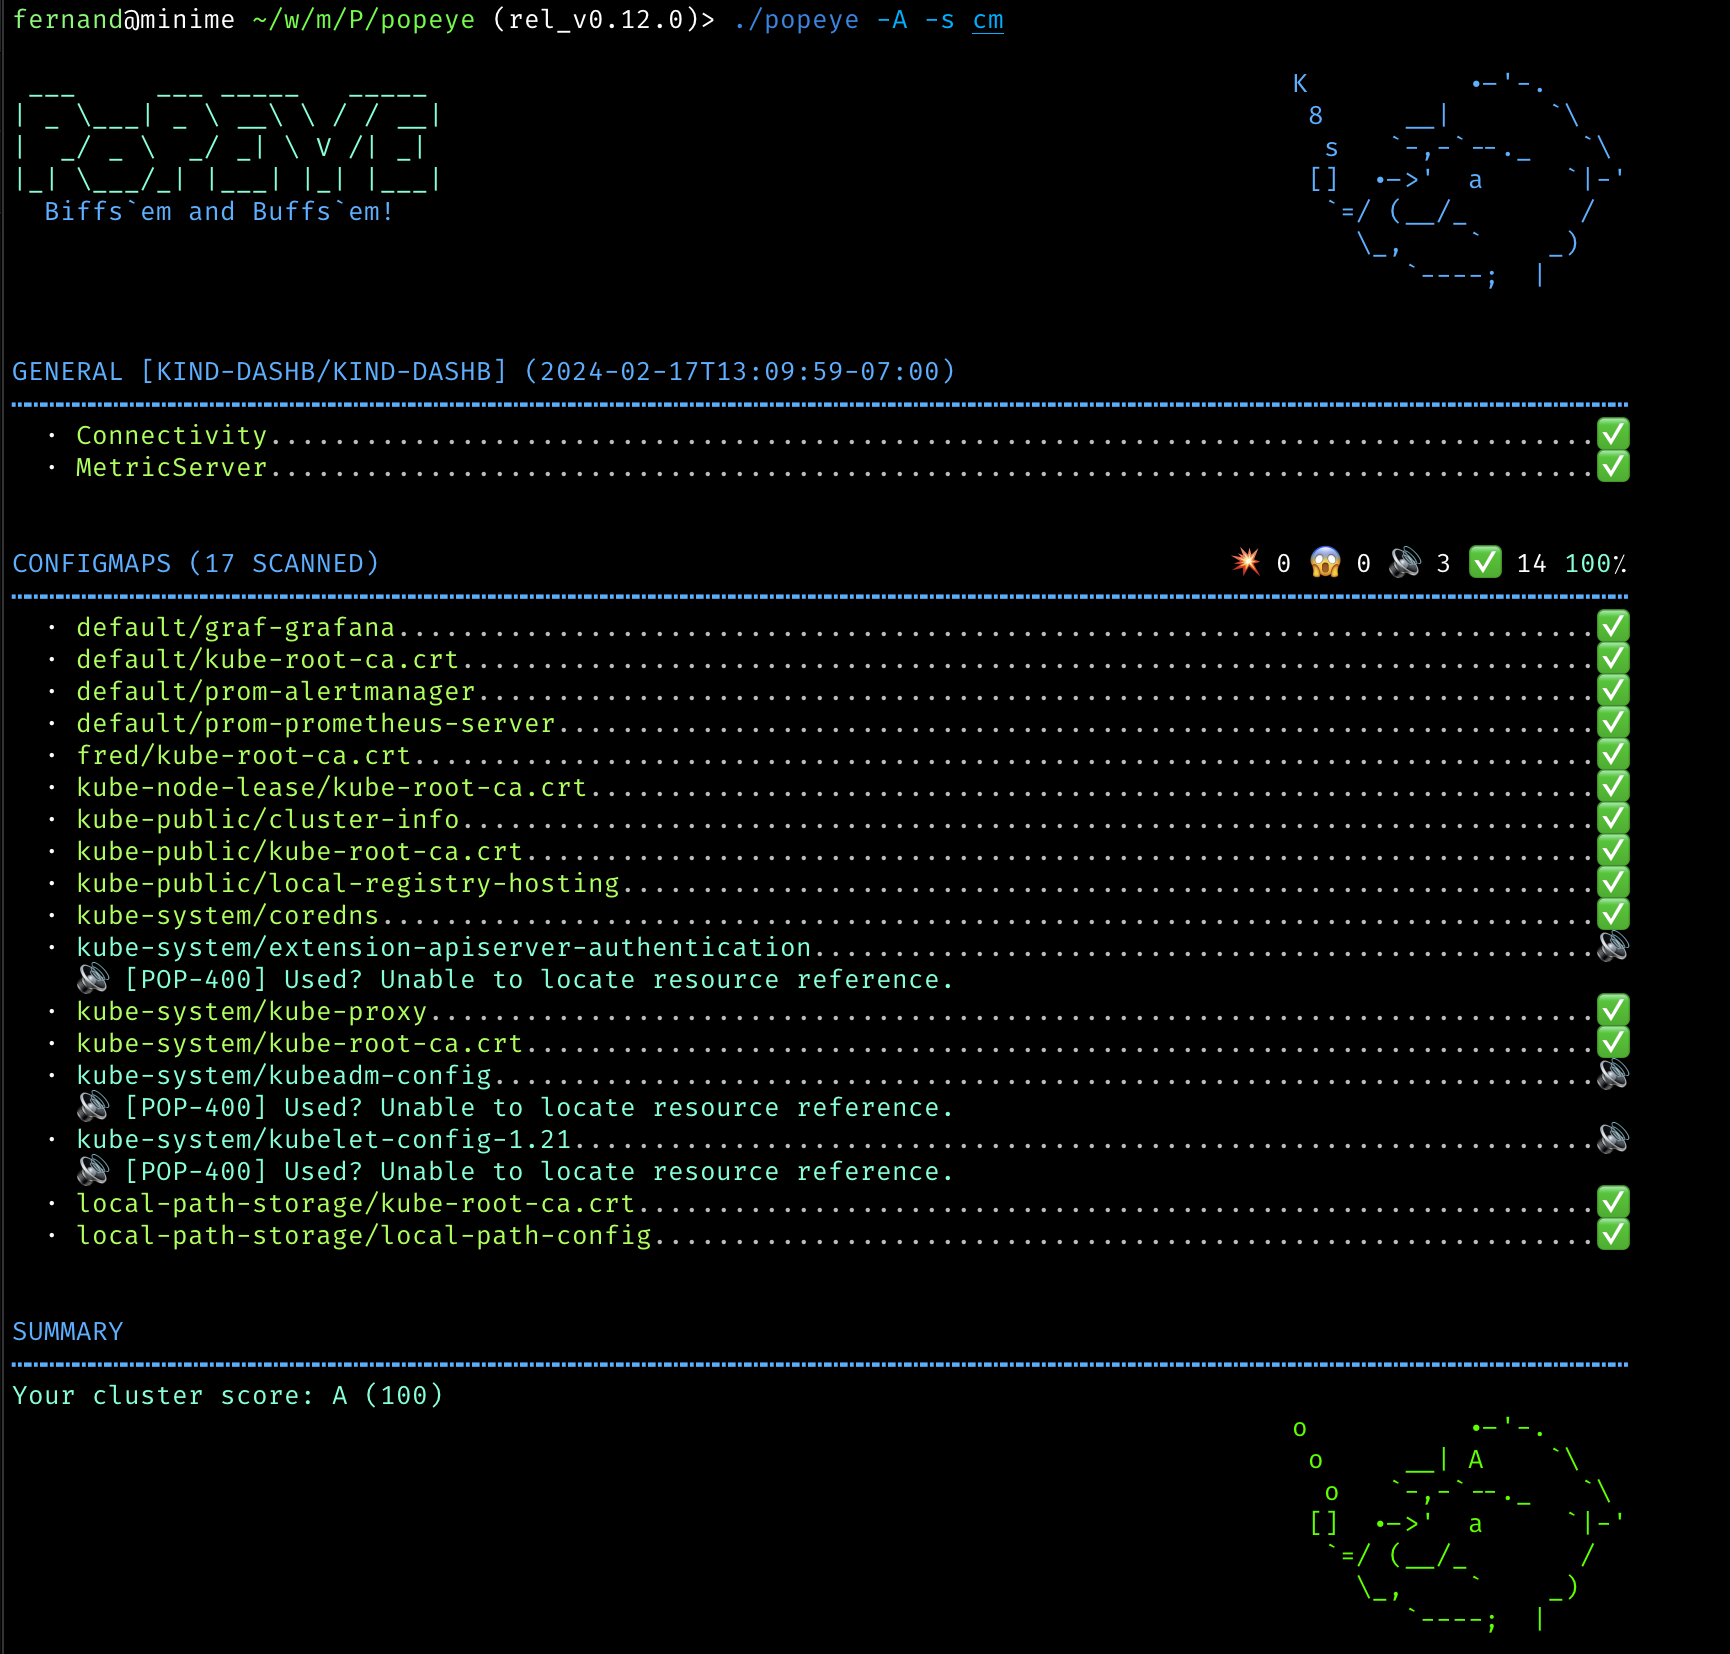 derailed/popeye
👀 A Kubernetes cluster resource sanitizer
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking
 assetnote/blind-ssrf-chains
An exhaustive list of all the possible ways you can chain your Blind SSRF vulnerability
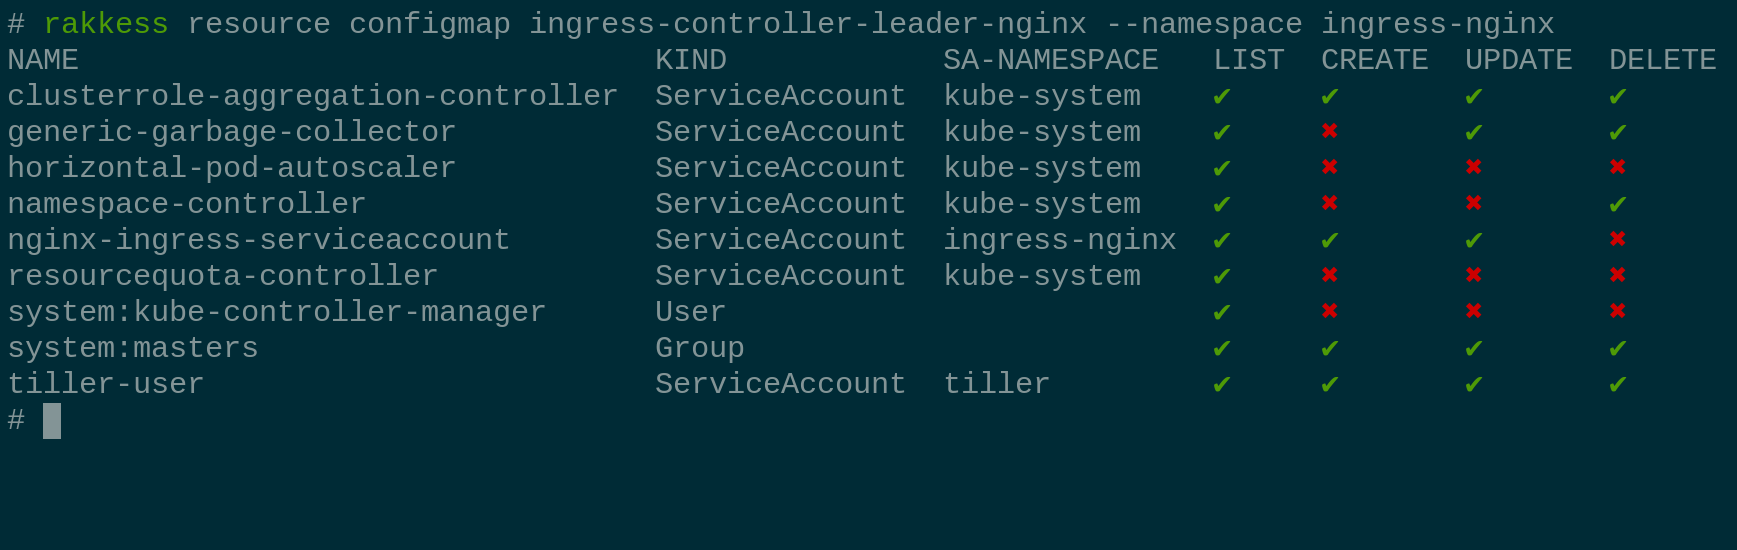 corneliusweig/rakkess
Review Access - kubectl plugin to show an access matrix for k8s server resources