gvisor
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
cloud-infrastructure-securitycloud-securitycontainer-escape+4
19.8k
google/gvisorSandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
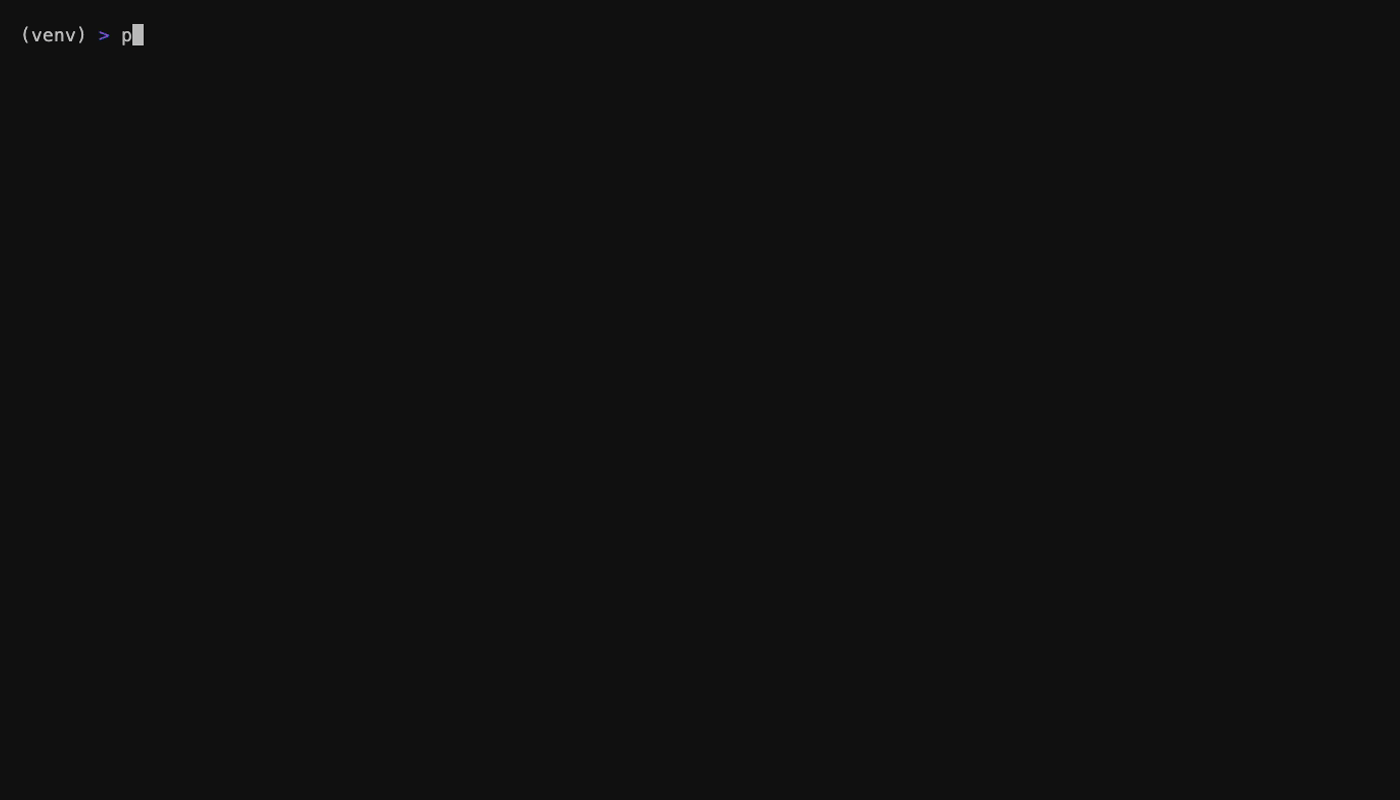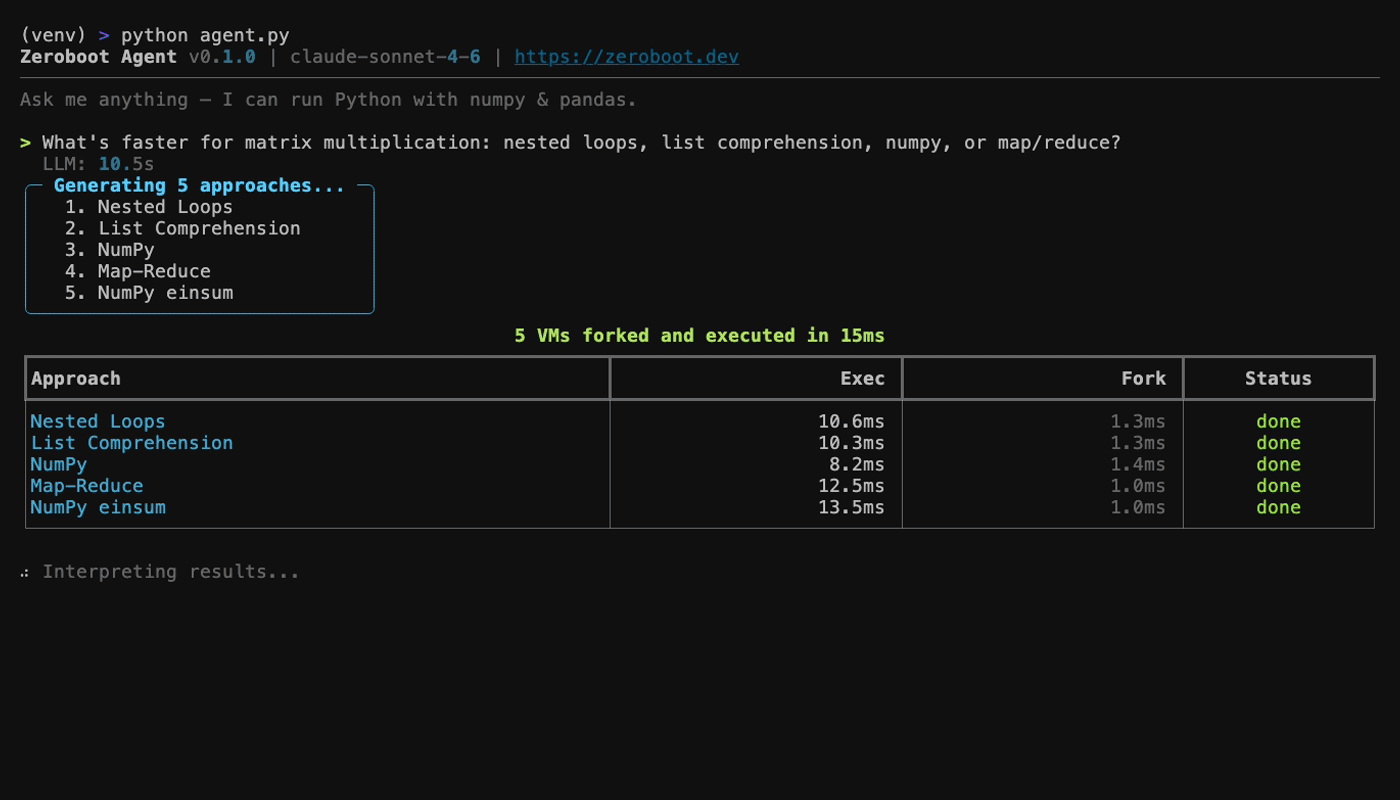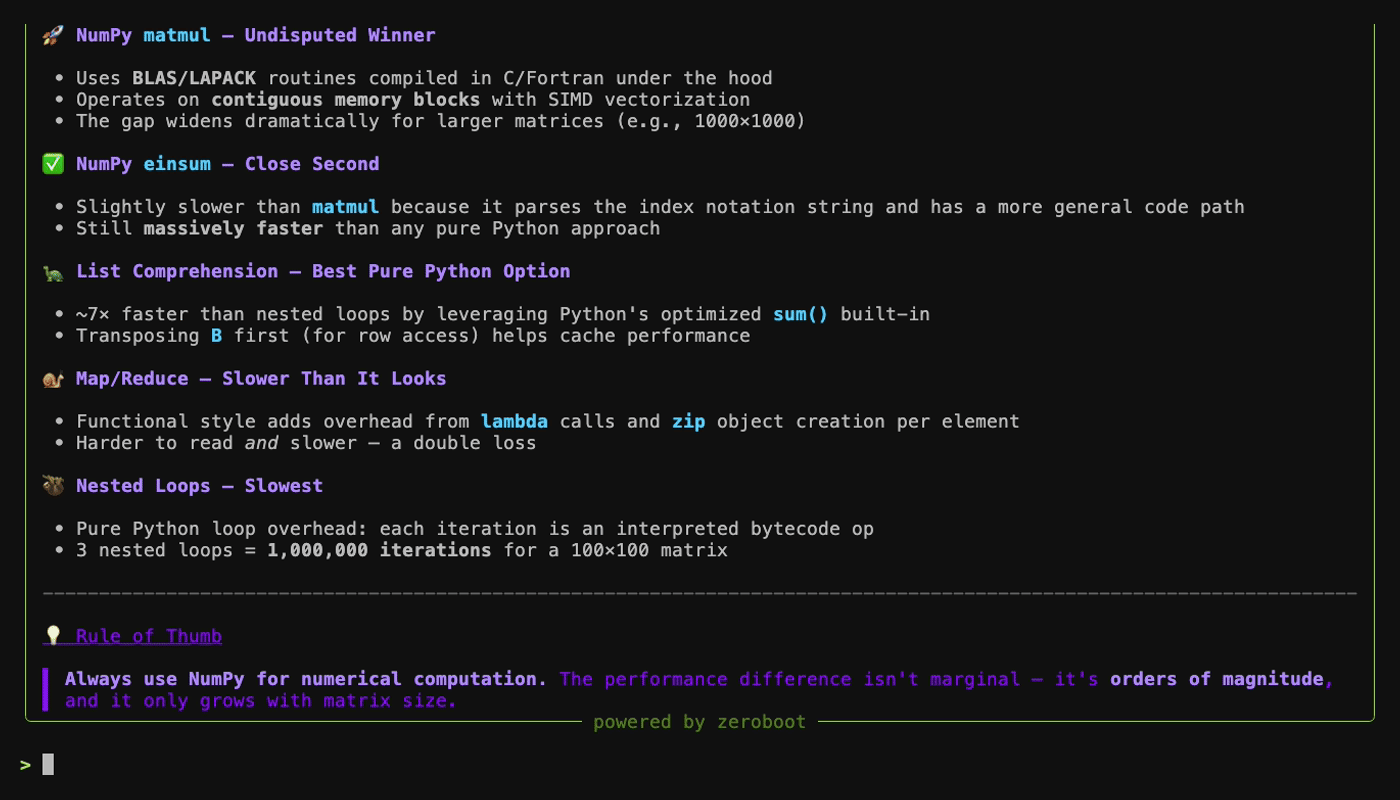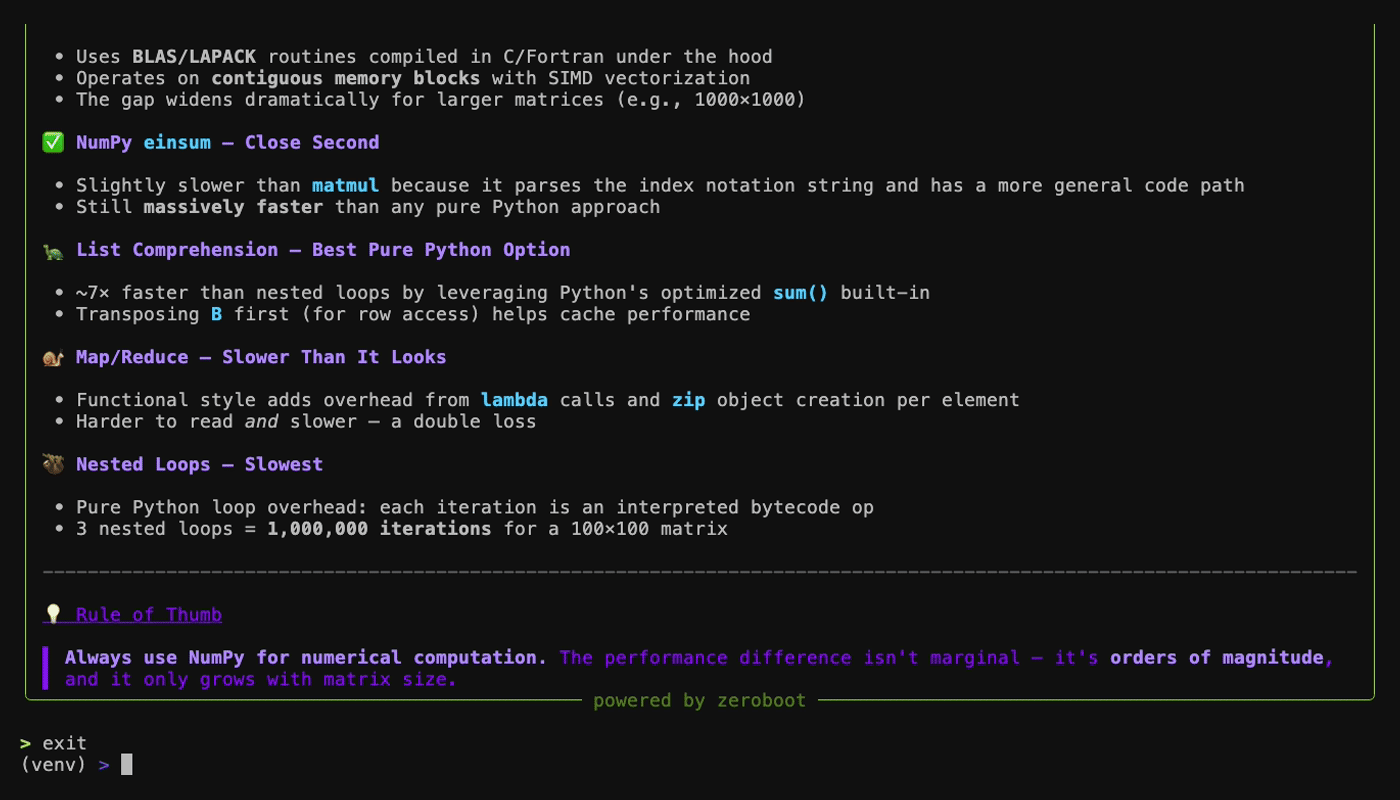 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
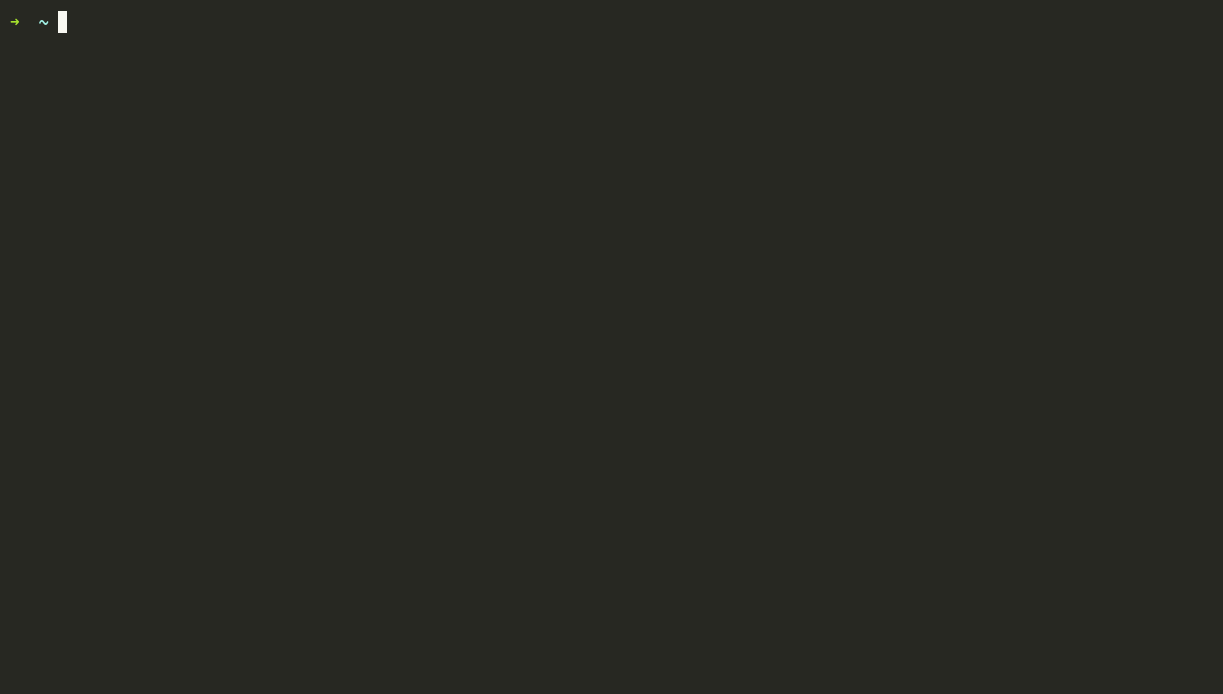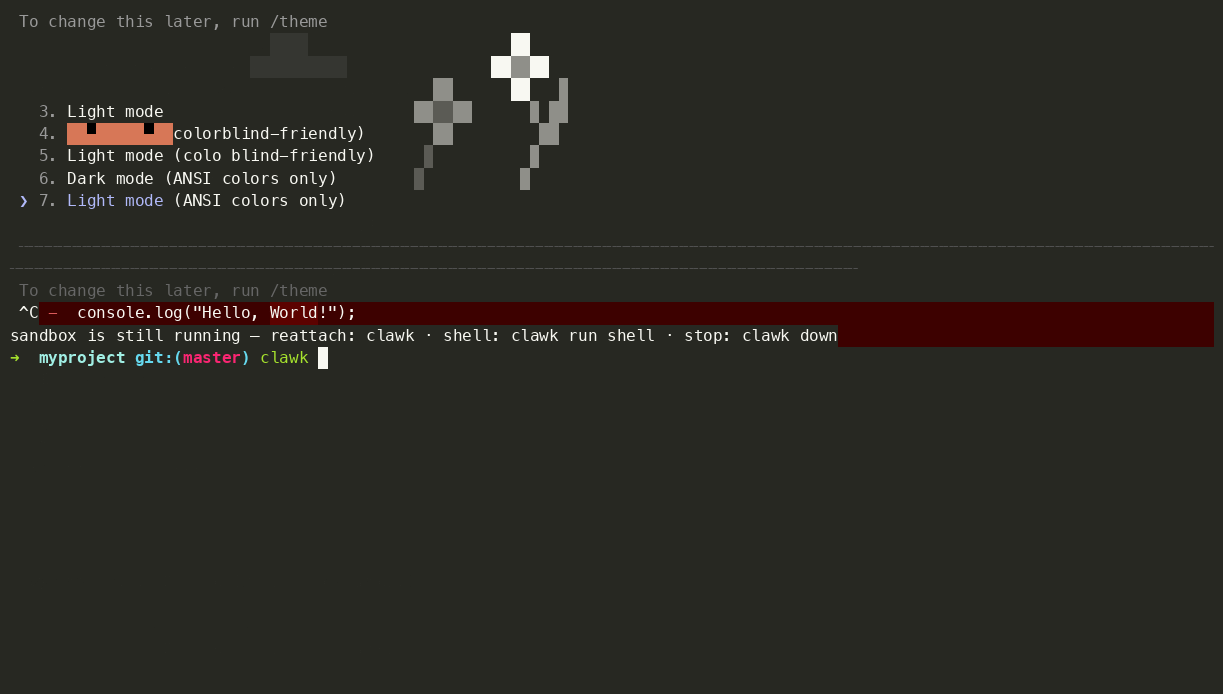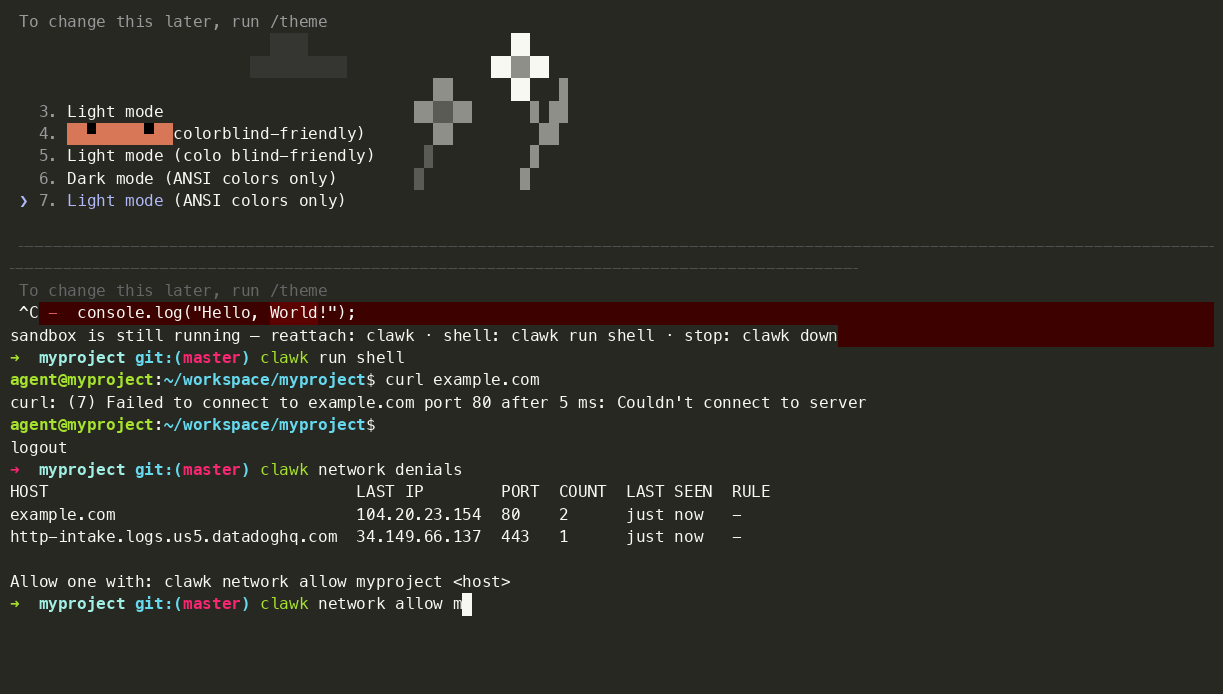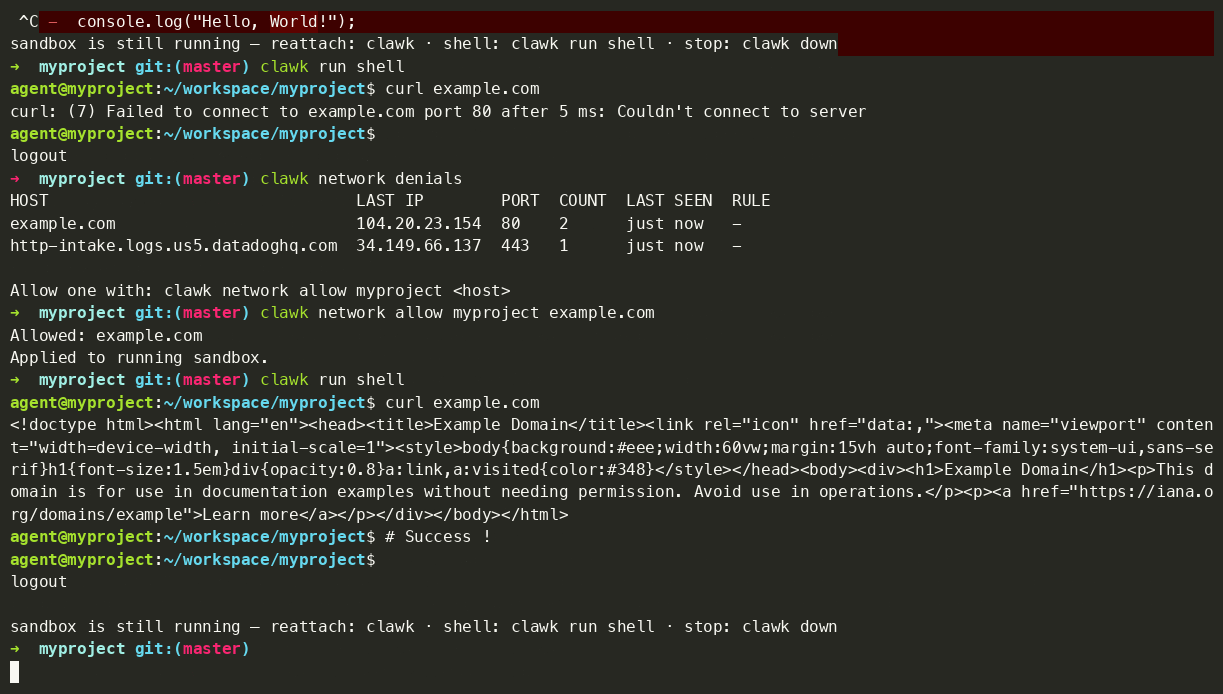 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
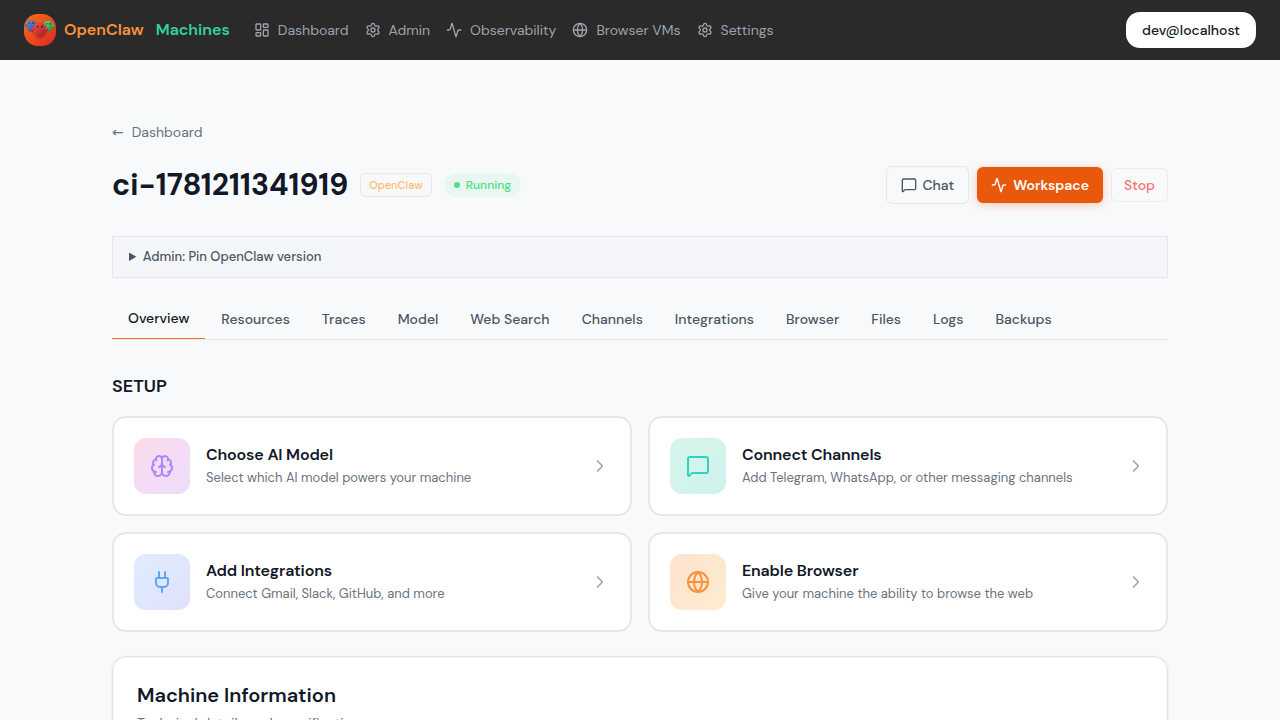 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 chaitin/veinmind-tools
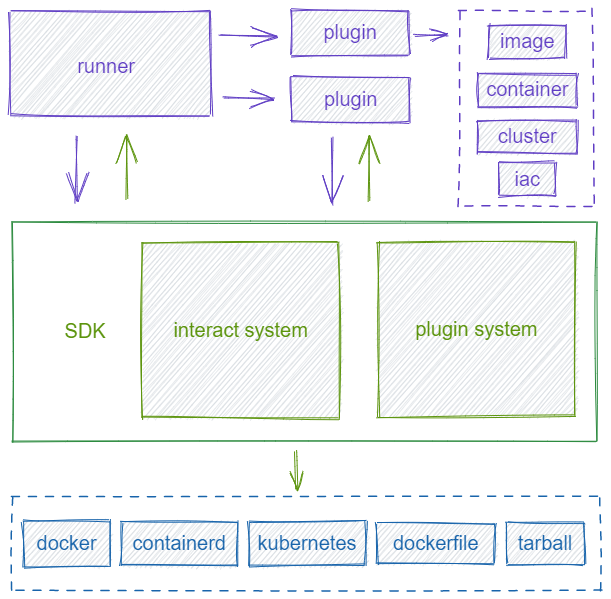
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集