
attack_range
 splunk/attack_range
A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
cloud-securityeducationlabs-practice+1
2.6k
splunk/attack_rangeA tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
 grabesec/xcp_ng_cve-2026-43284_tester
Tester for CVE-2026-43284
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 slauger/cve-2026-31431
Analysis and mitigation guide for CVE-2026-31431, a Linux kernel local privilege escalation in the crypto algif_aead subsystem, with impact…
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
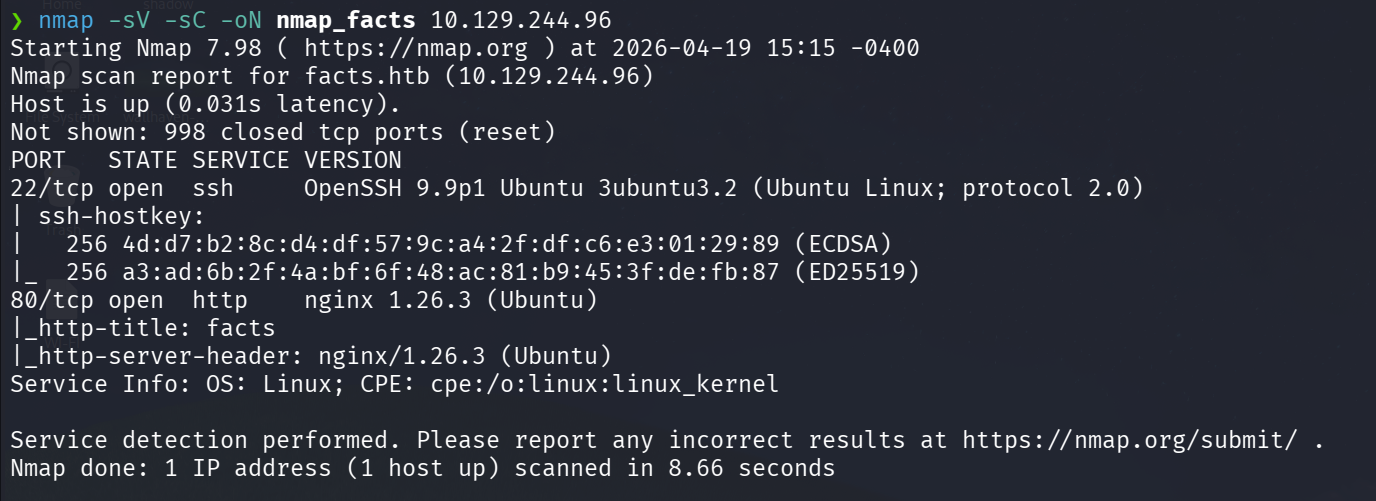 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
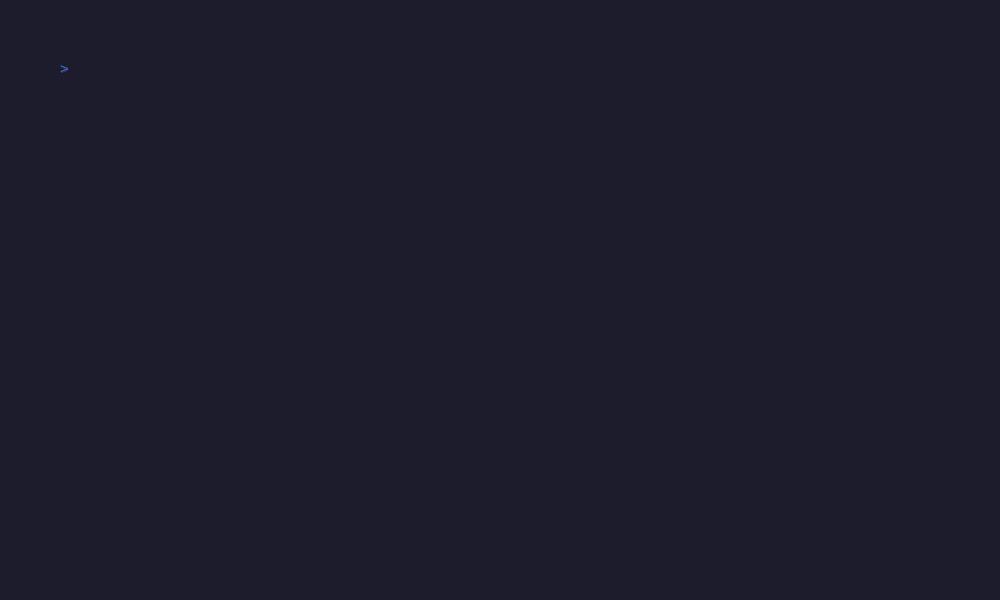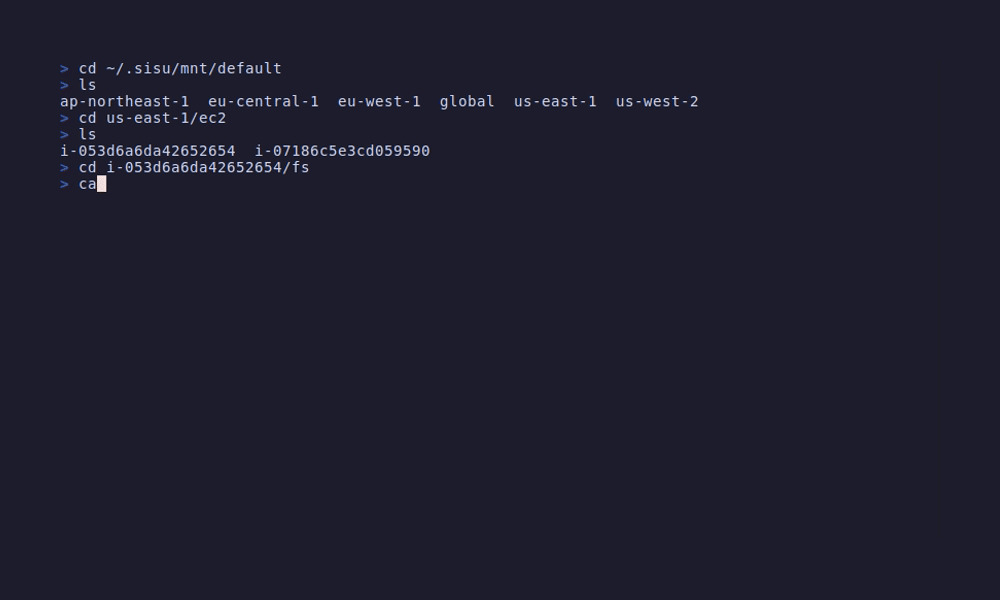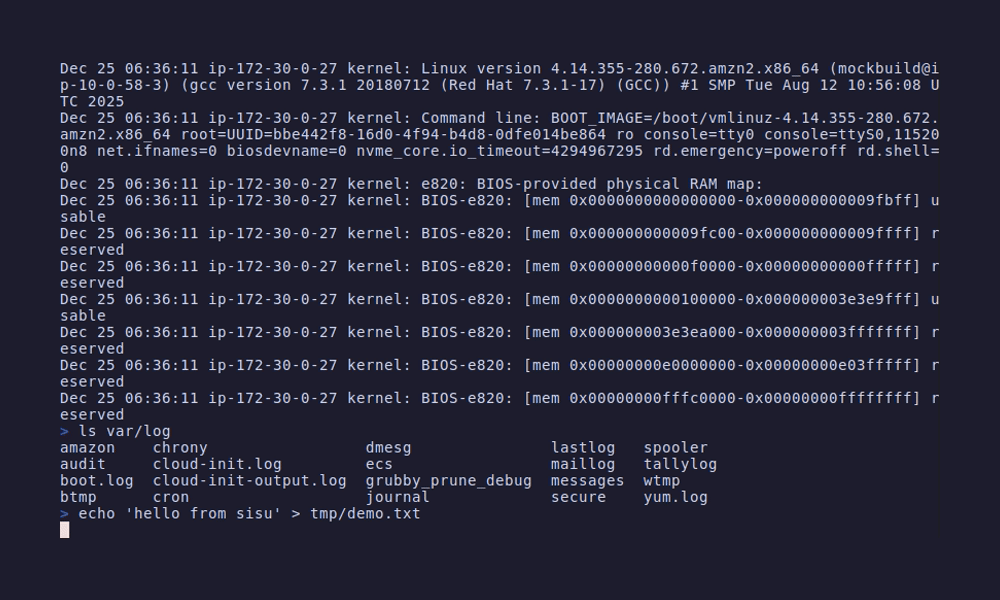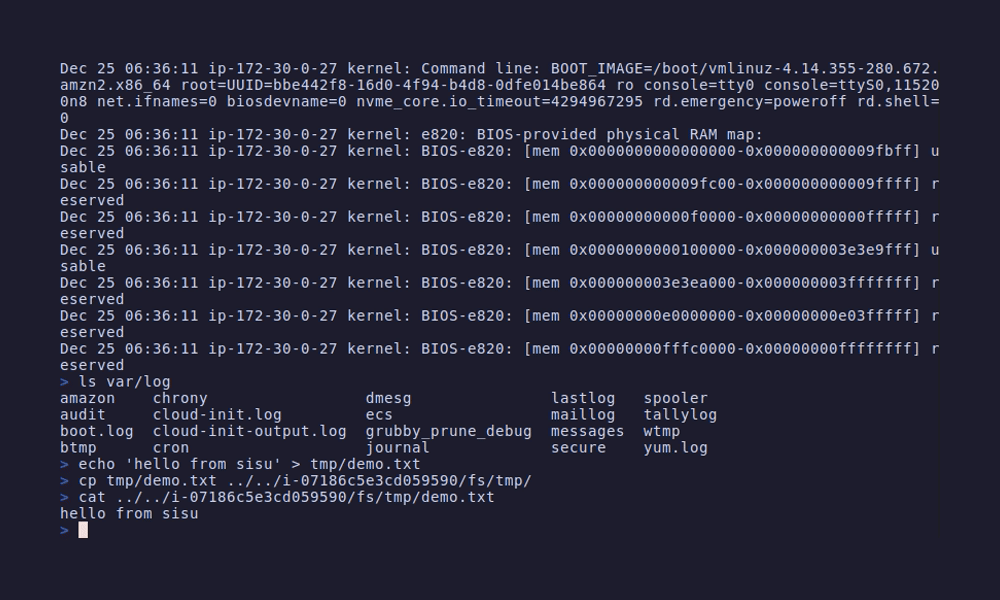 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 sh-ubh/cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105, a Kubernetes privilege escalation vulnerability allowing unauthorized command execution in pods via…