
cicd-sensor
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
cloud-securitydevsecopsforensics+3
1
cicd-sensor/cicd-sensoreBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…

 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 google/turbinia
Automation and Scaling of Digital Forensics Tools
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
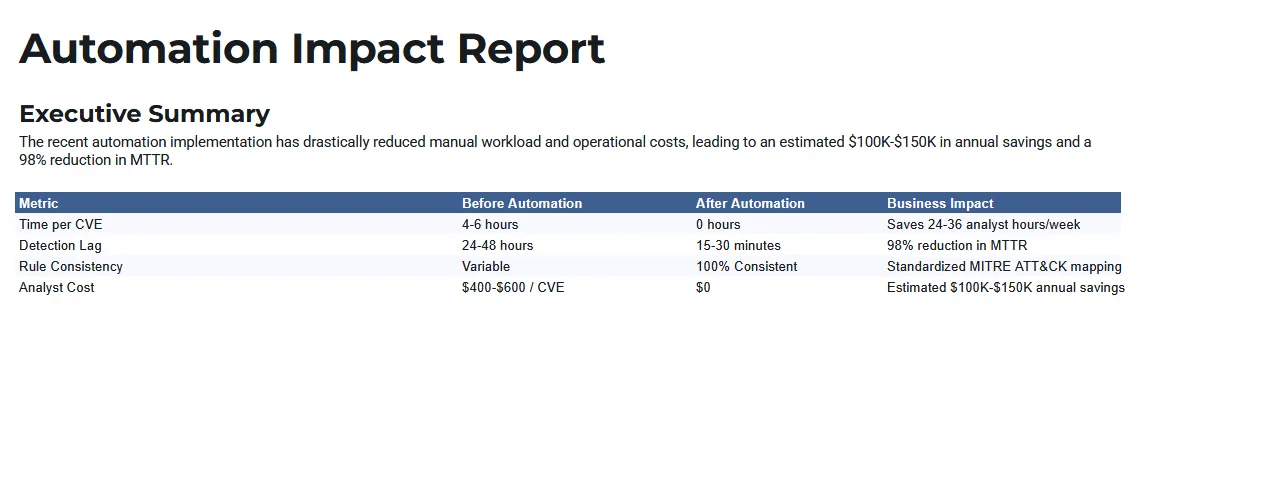 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 kreotic/sentrygrid
ML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.
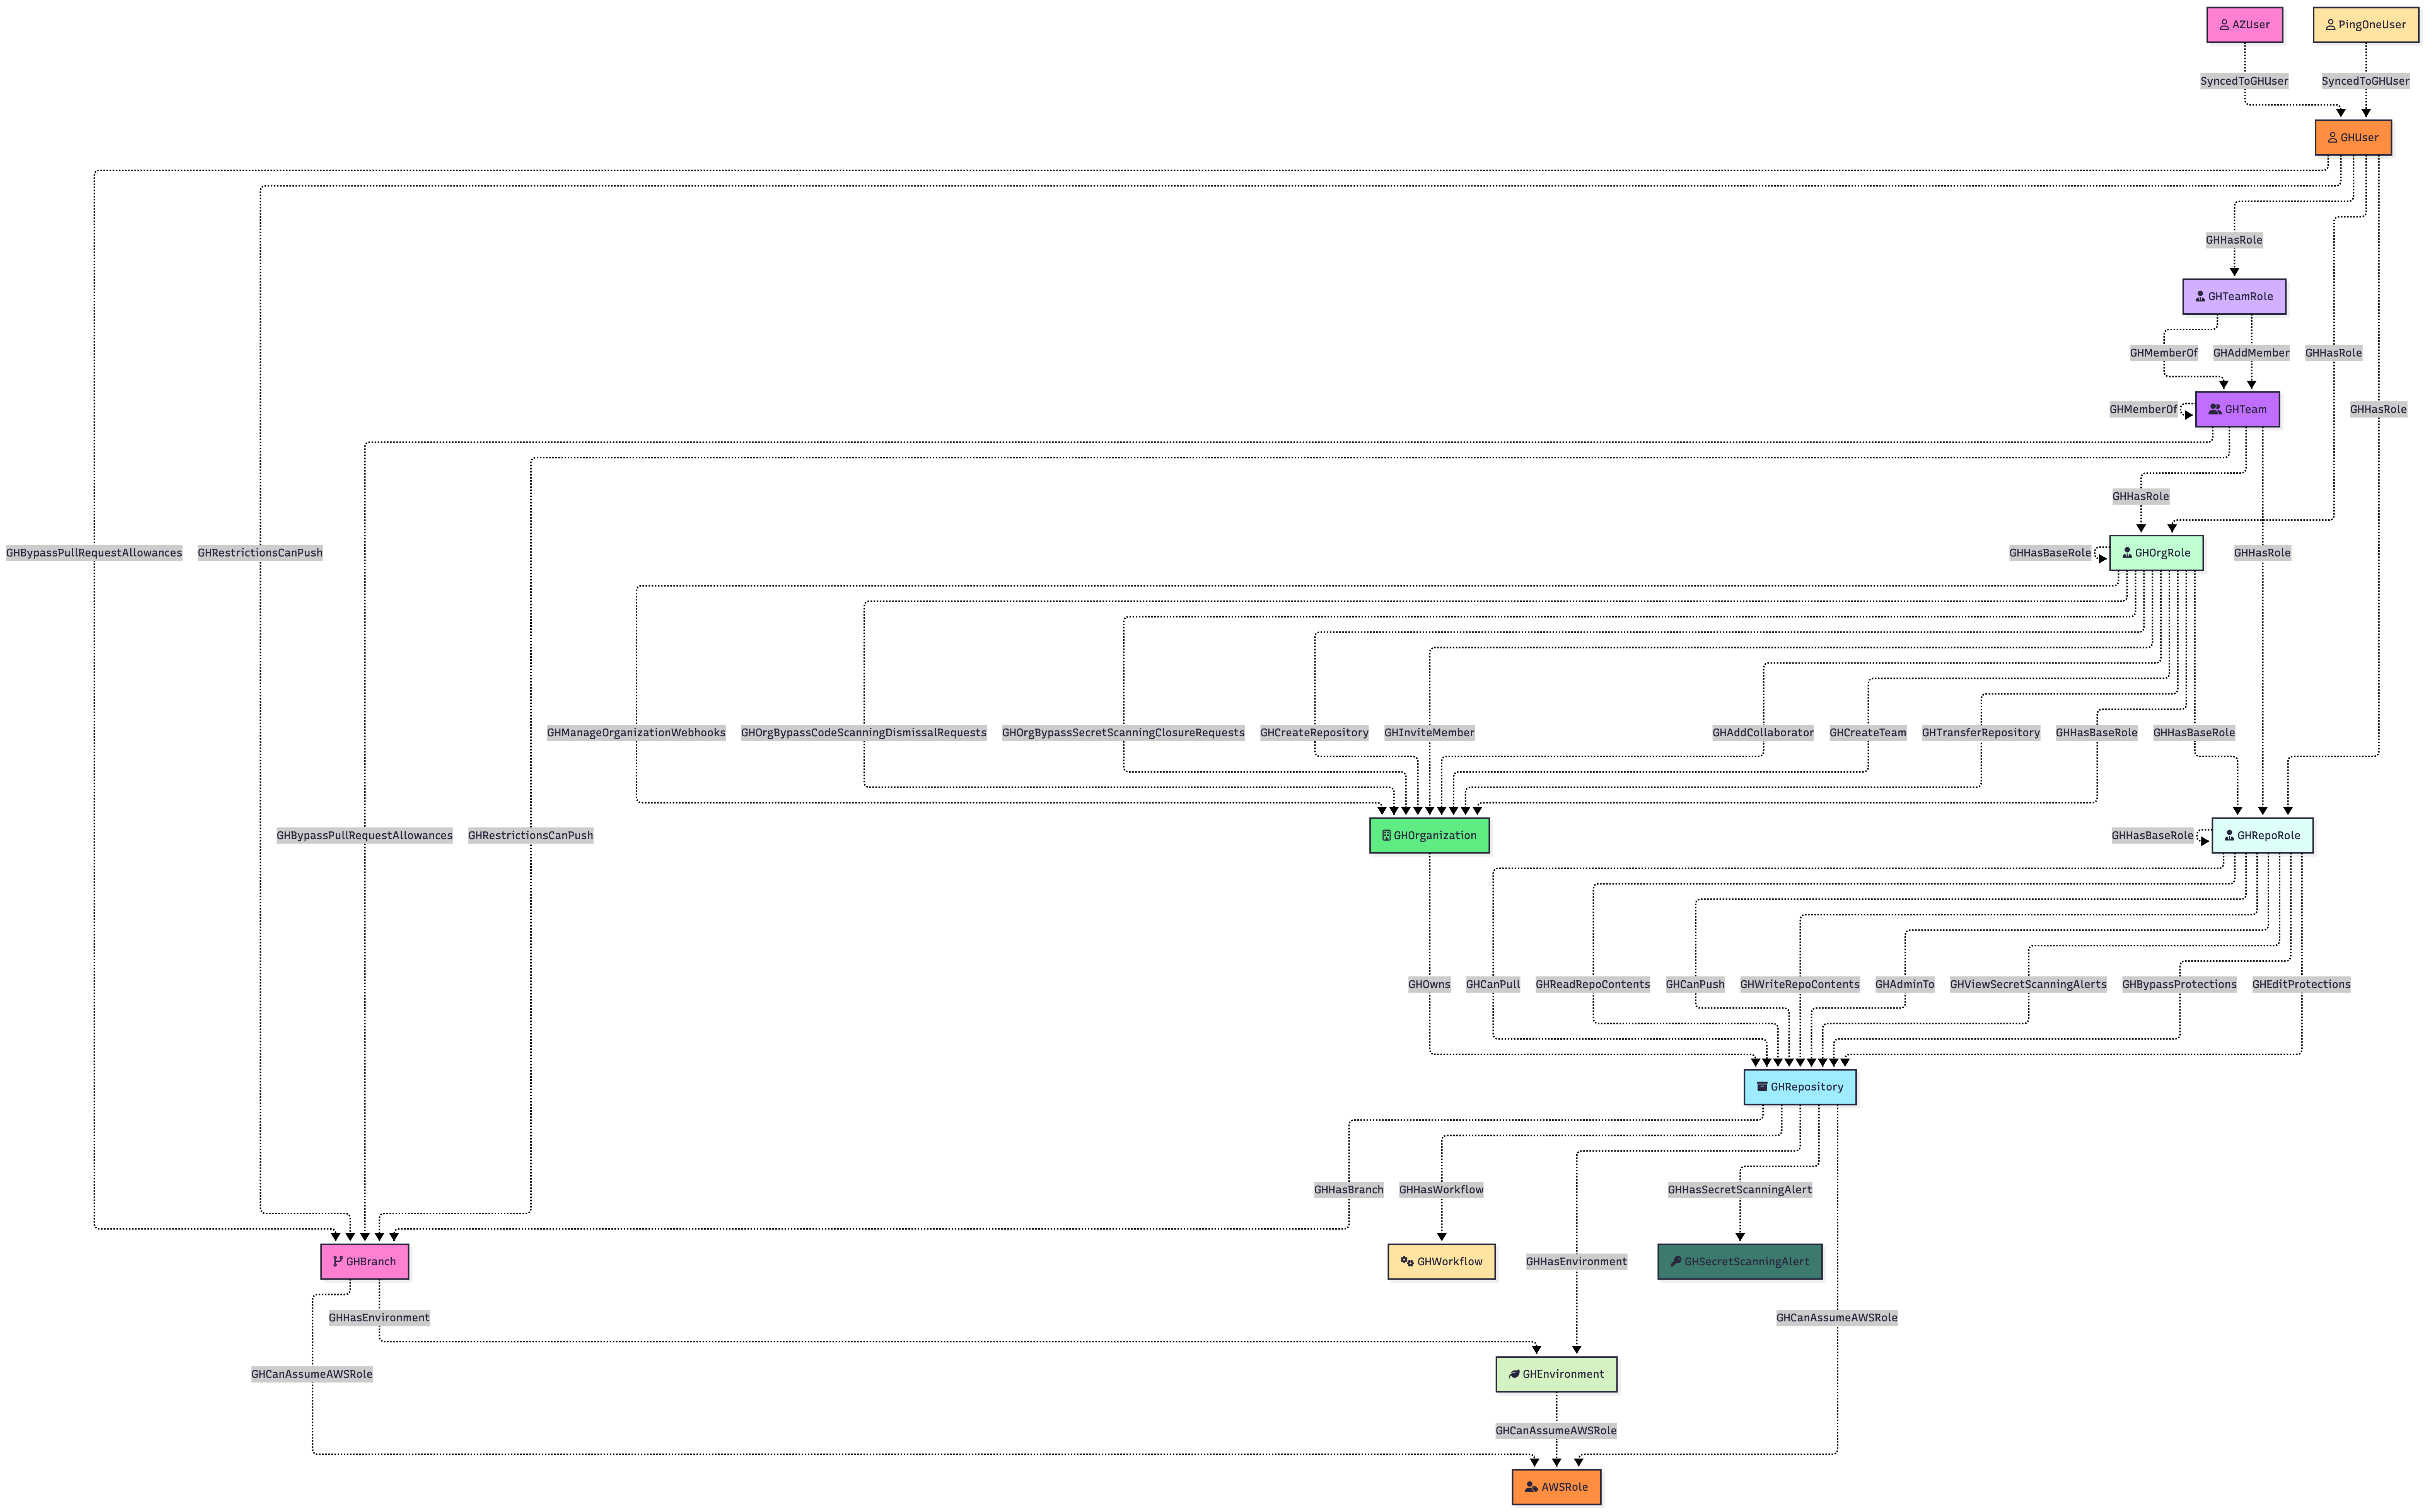 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
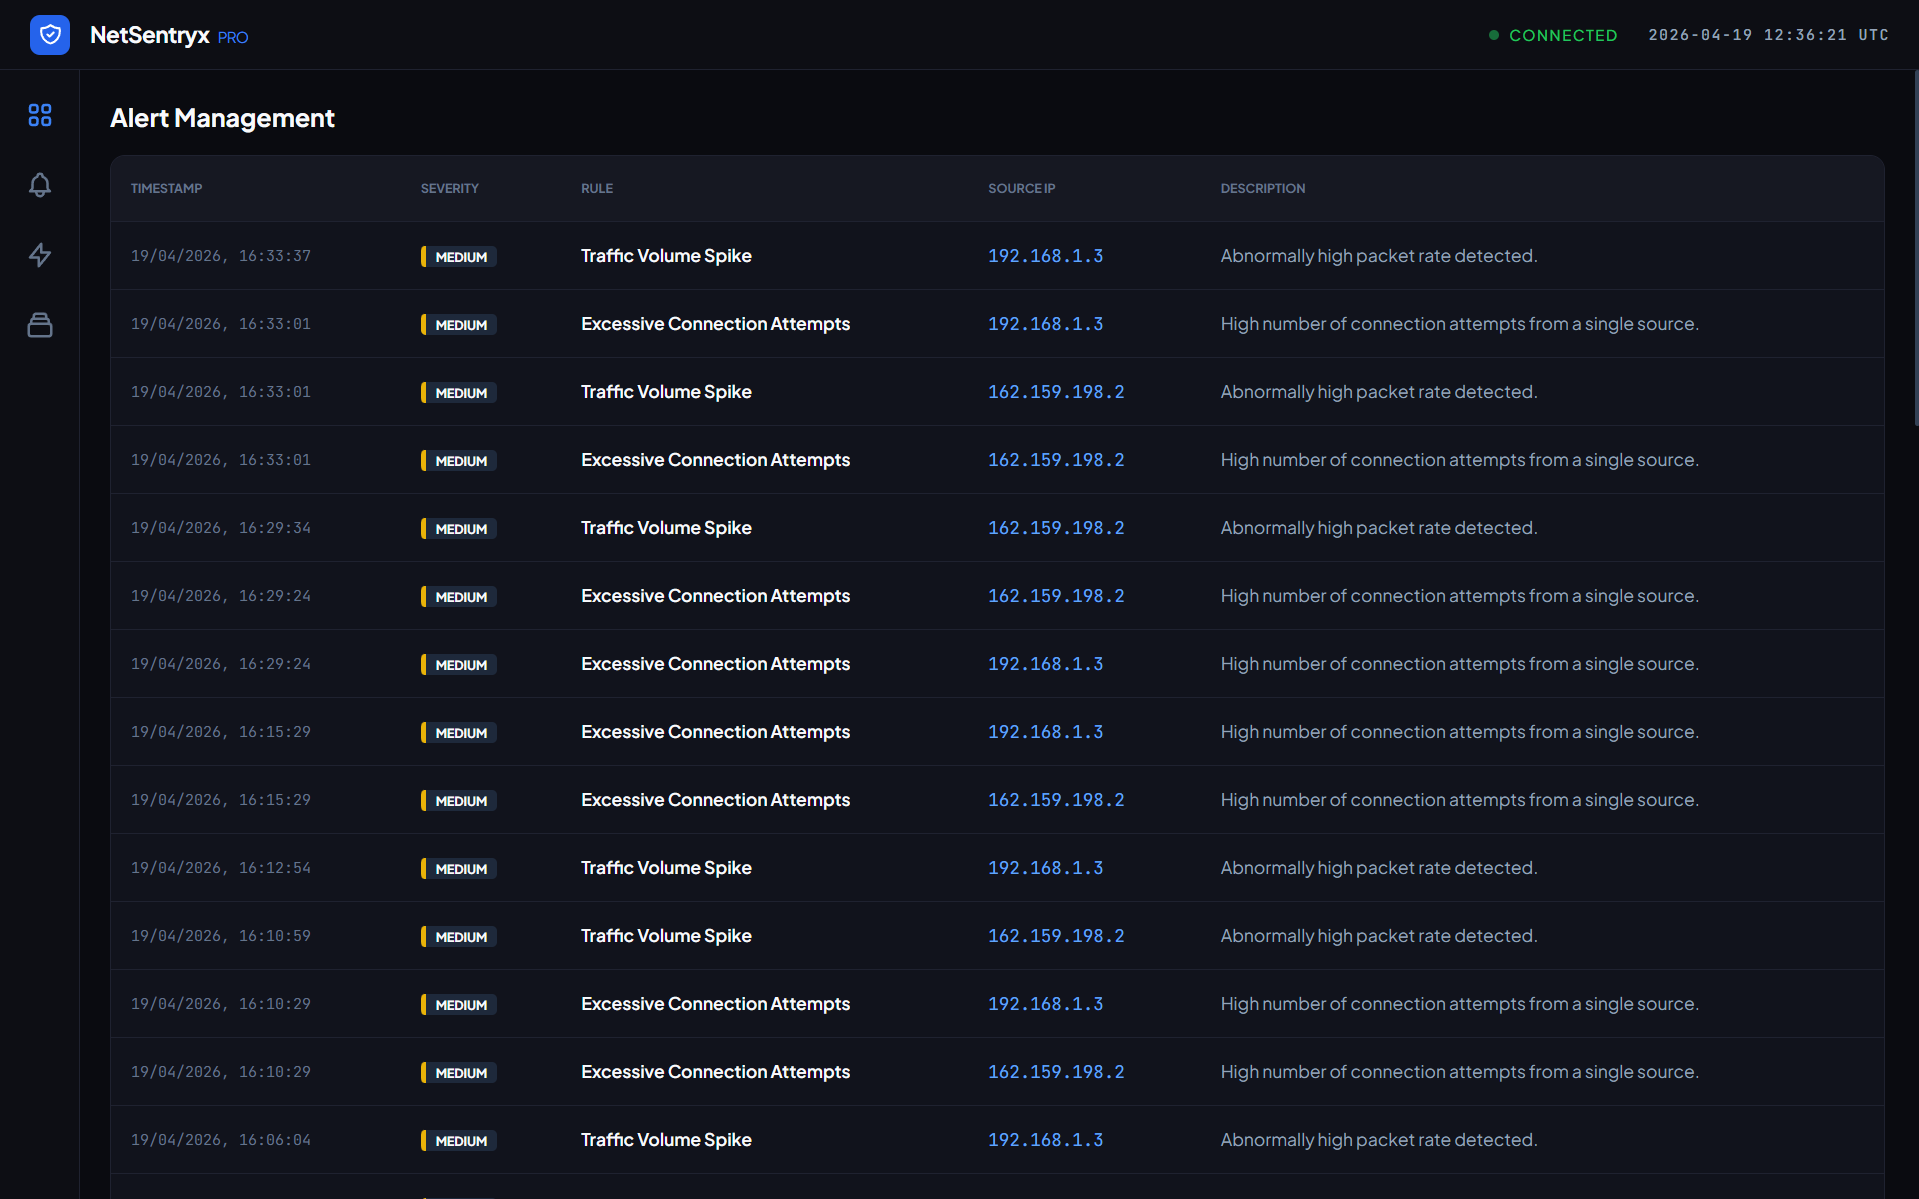 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 eshlomo1/microsoft-sentinel-secops
SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
 hybridbrothers/hunting-queries-detection-rules
The purpose of this repository is to share KQL queries to help identify security misconfigurations, hunt for specific patterns, or detect malicious…
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…